ActiveScanPlusPlus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…

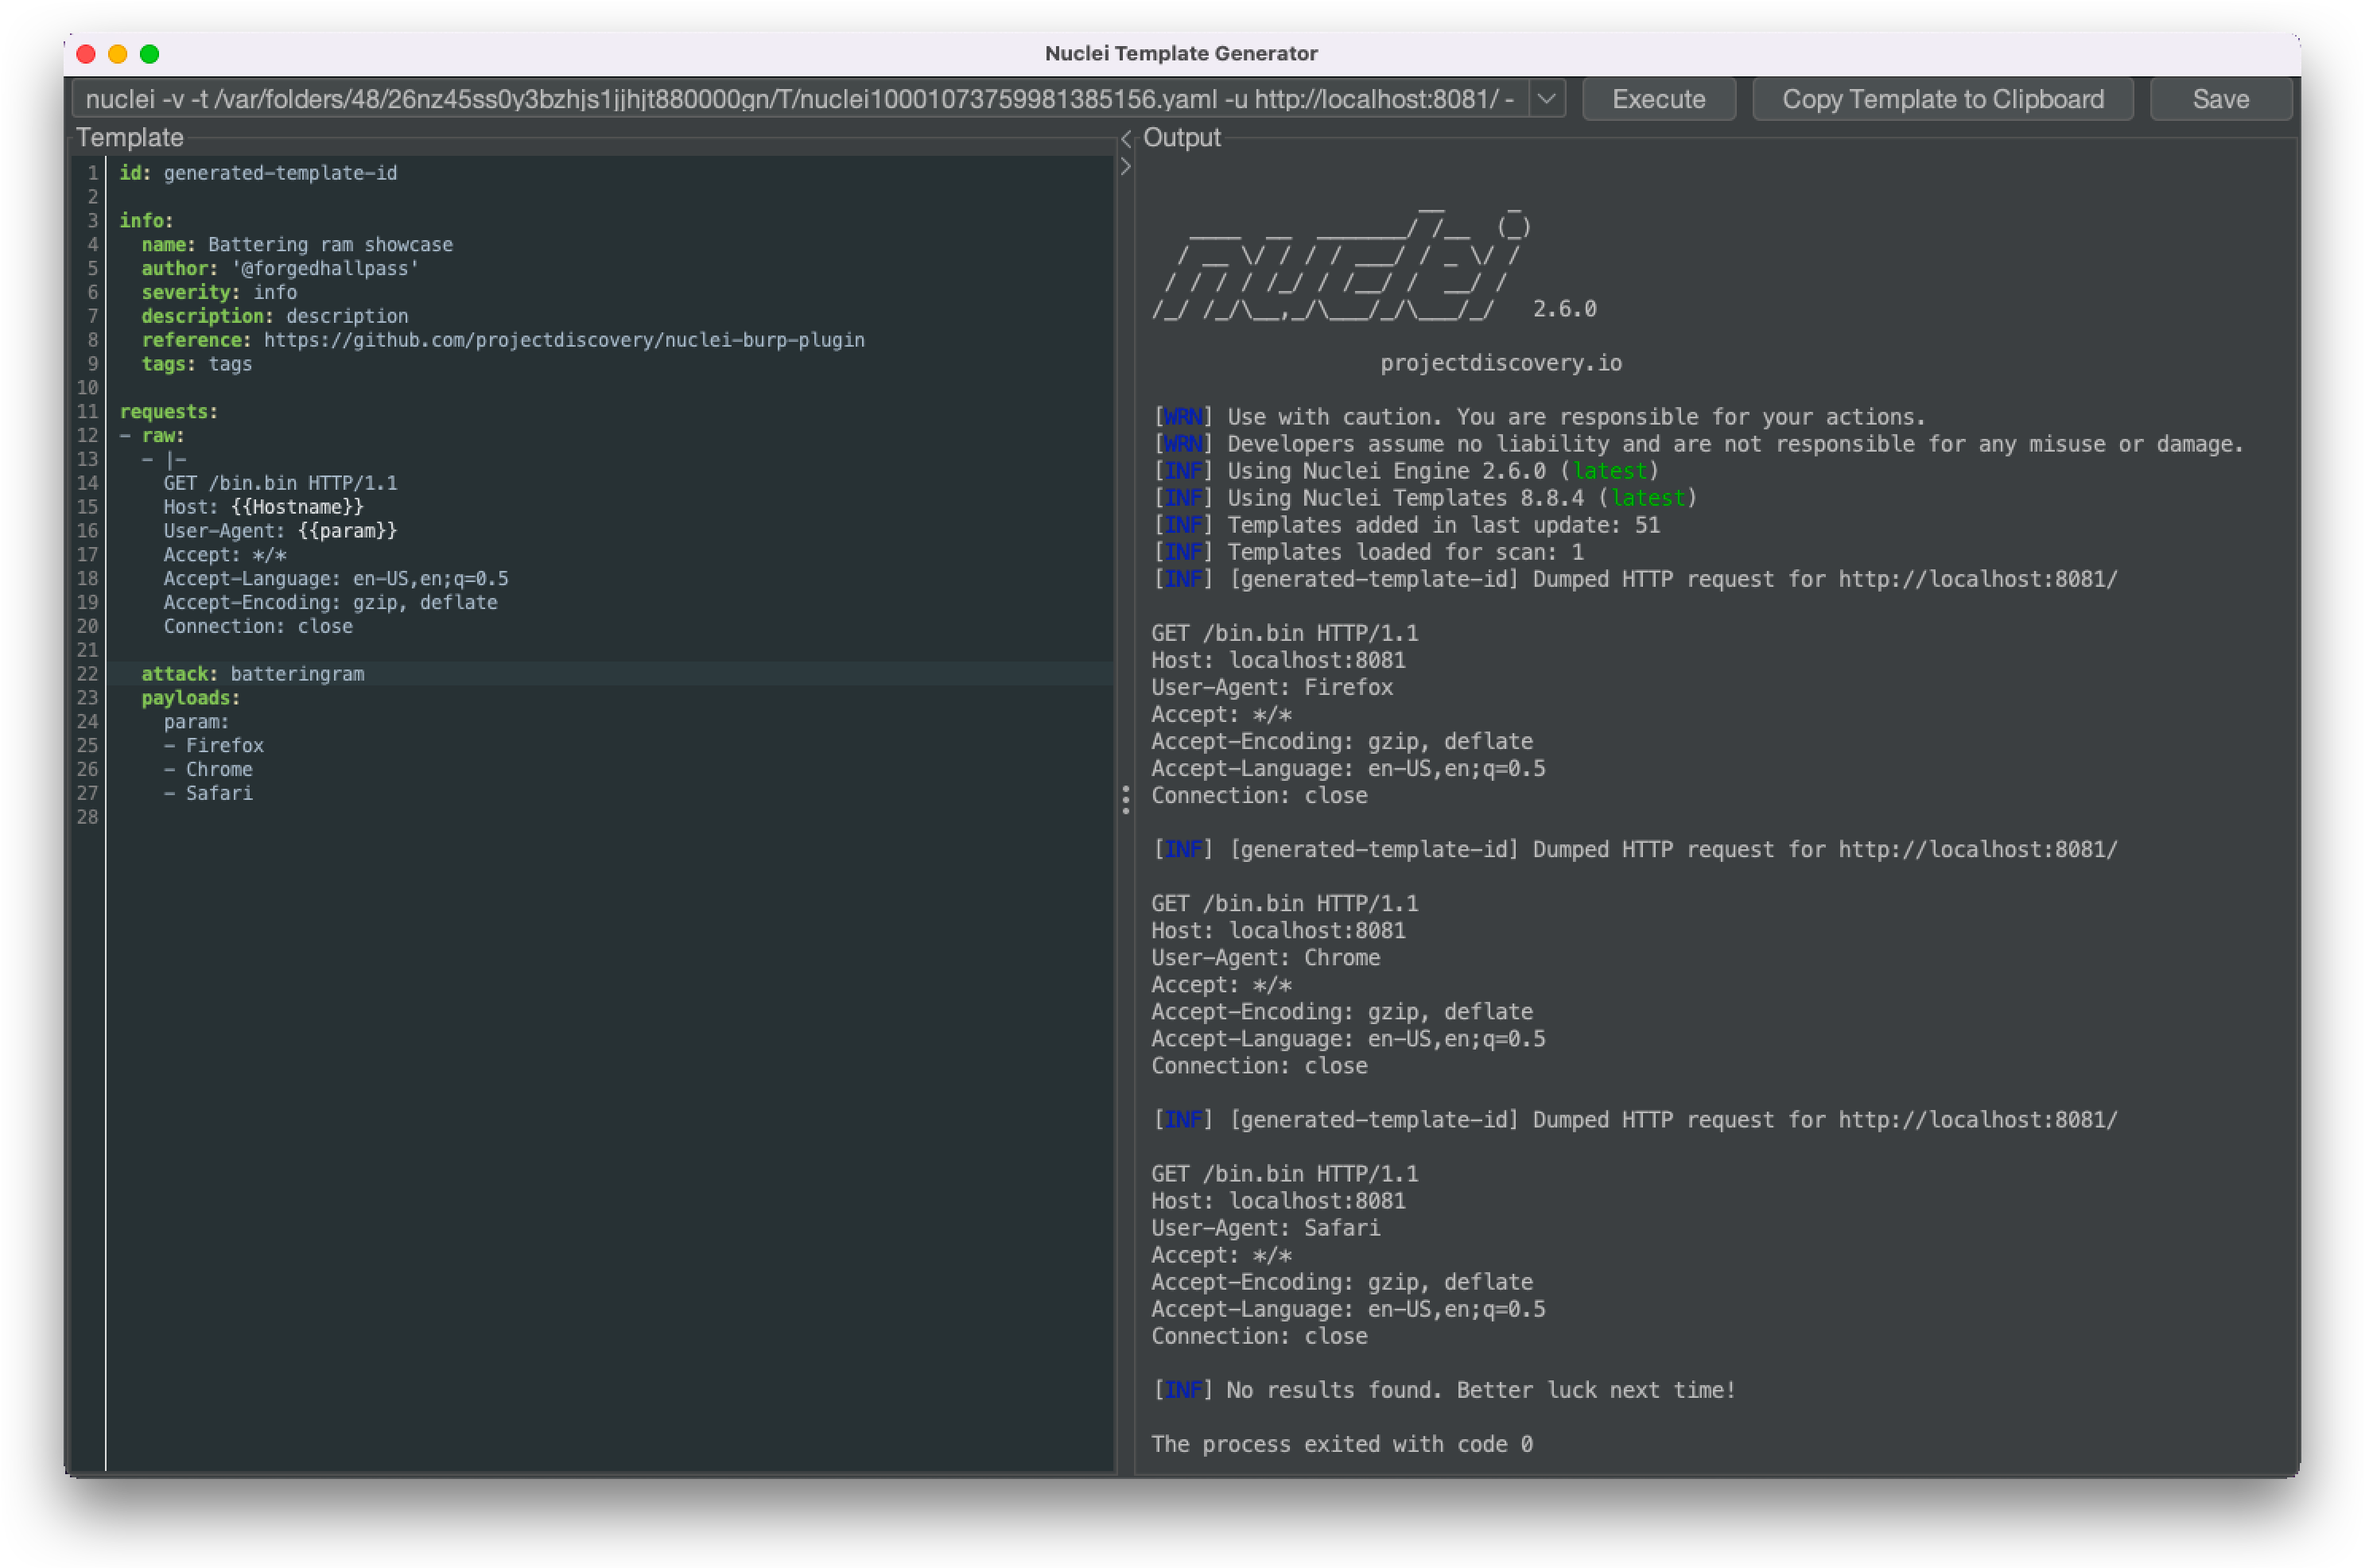
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…

Go client to communicate with Chaos DB API.

Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…

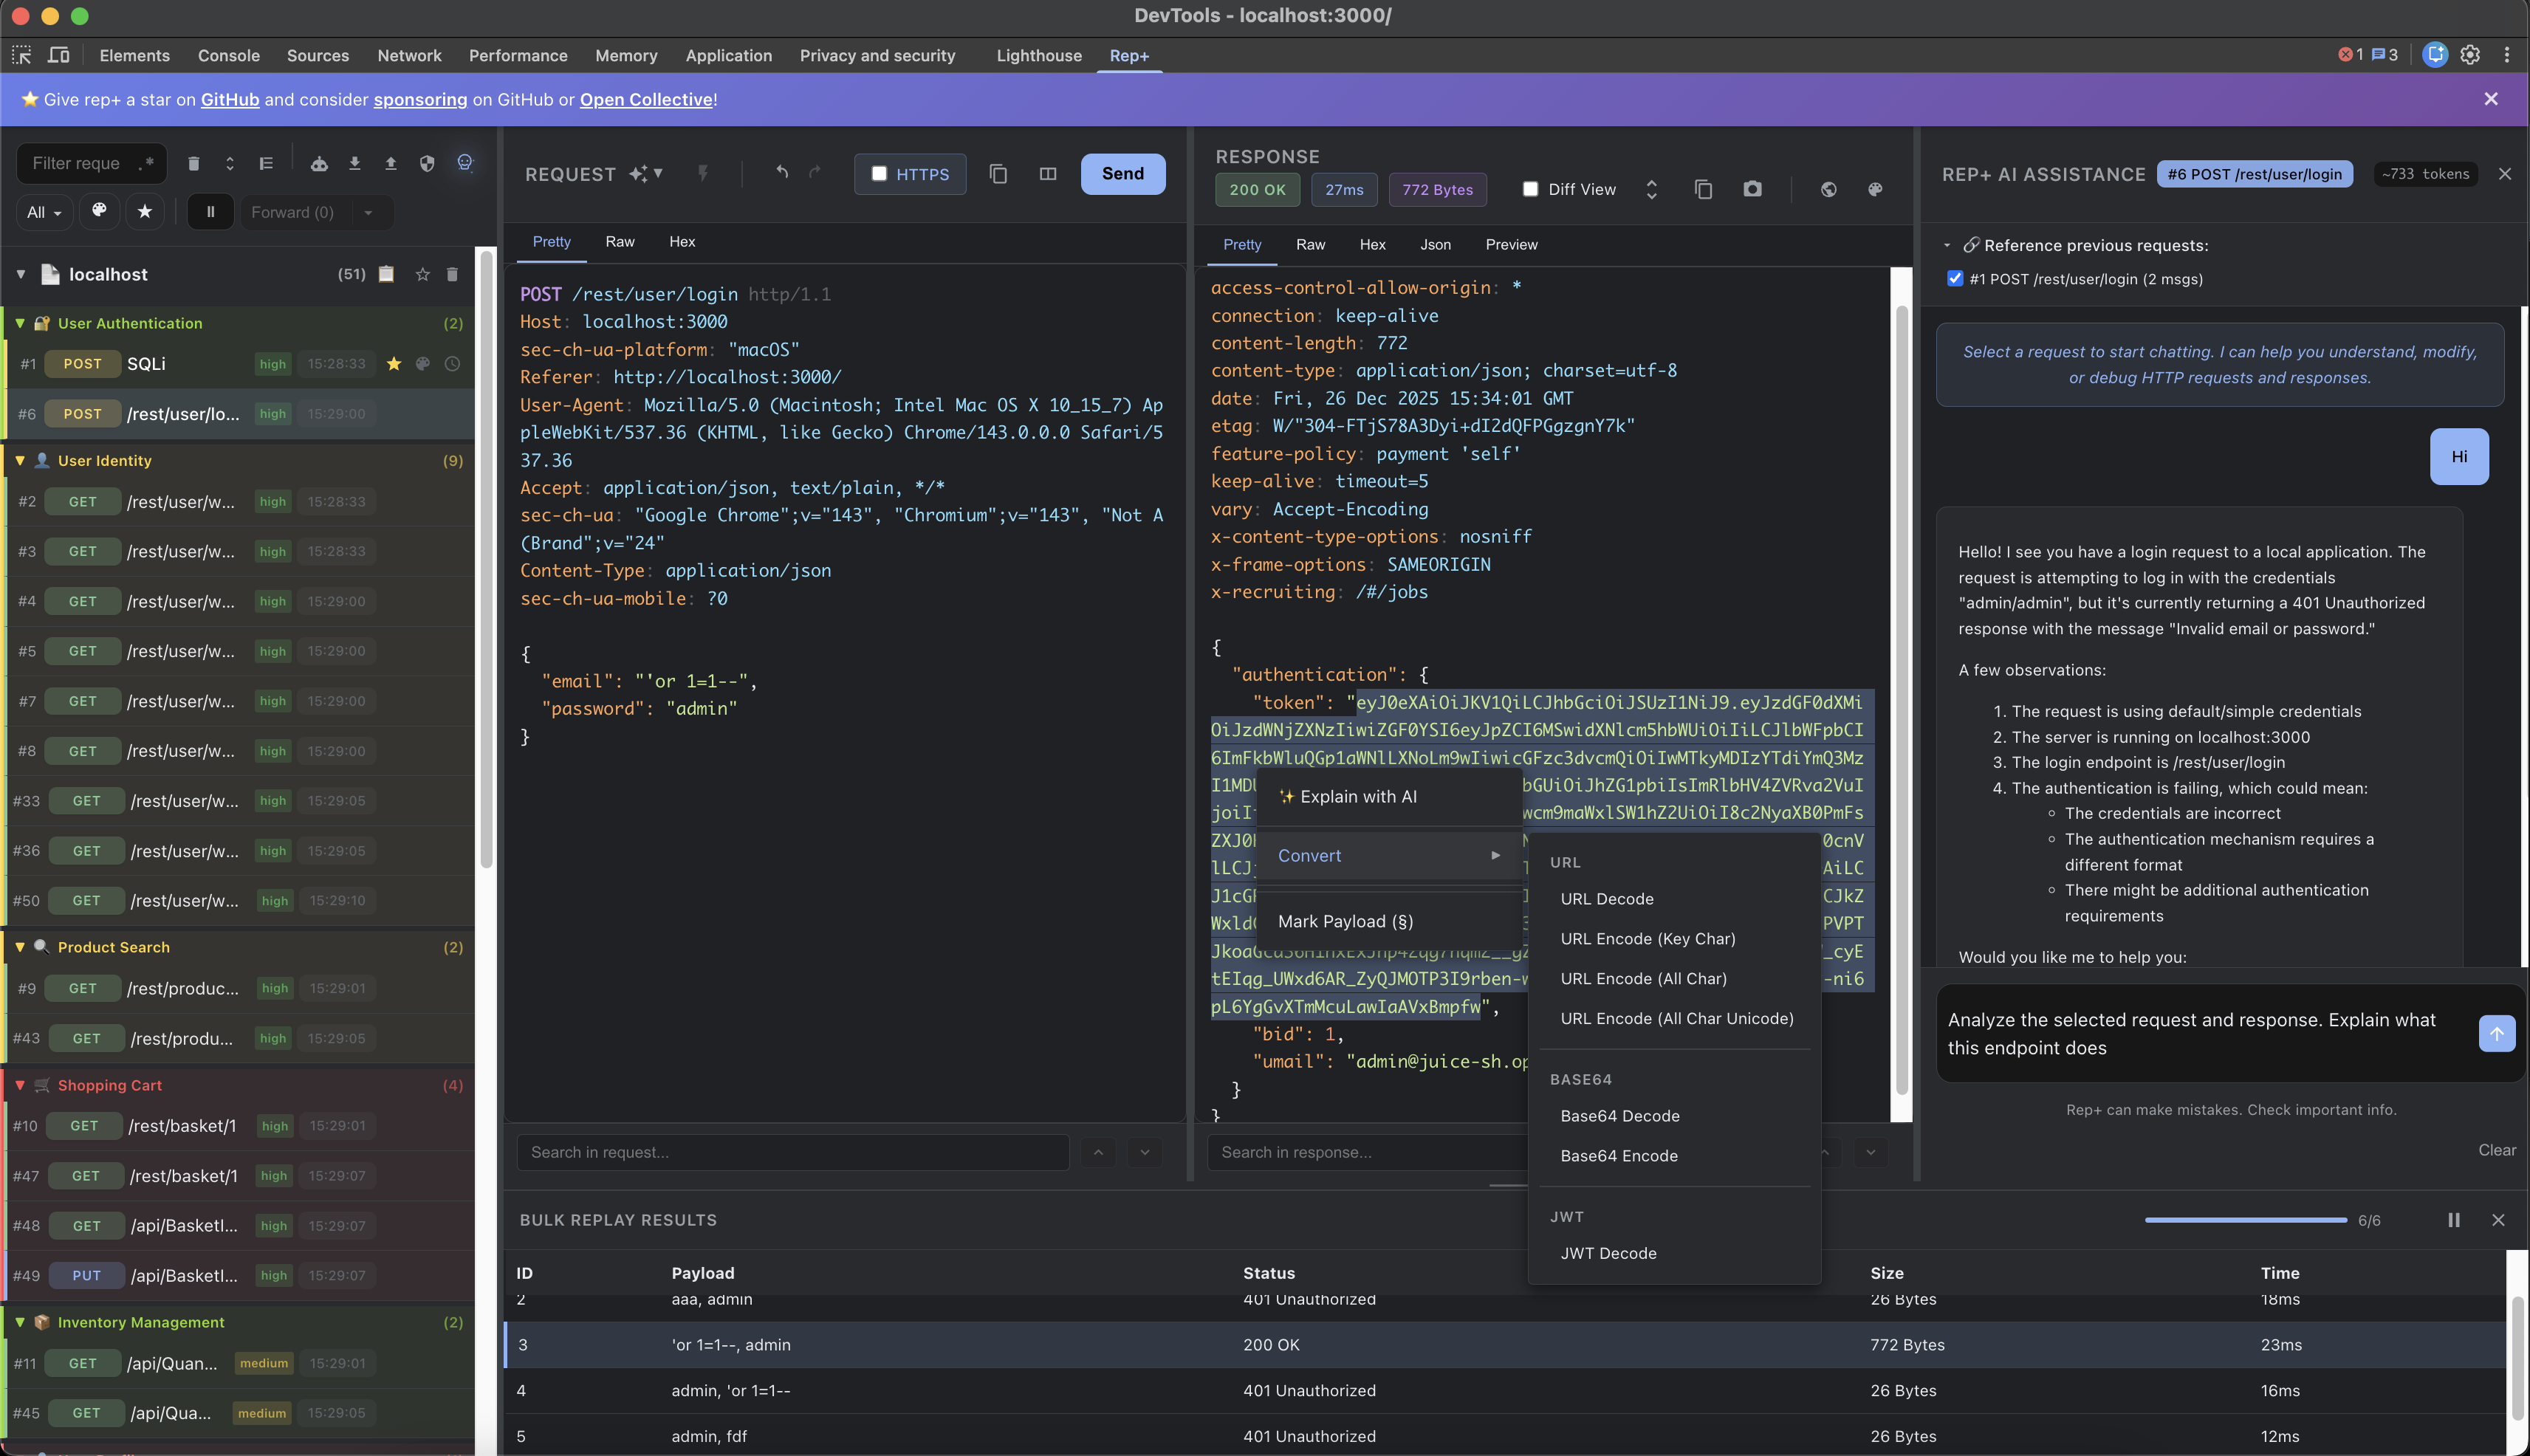
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks

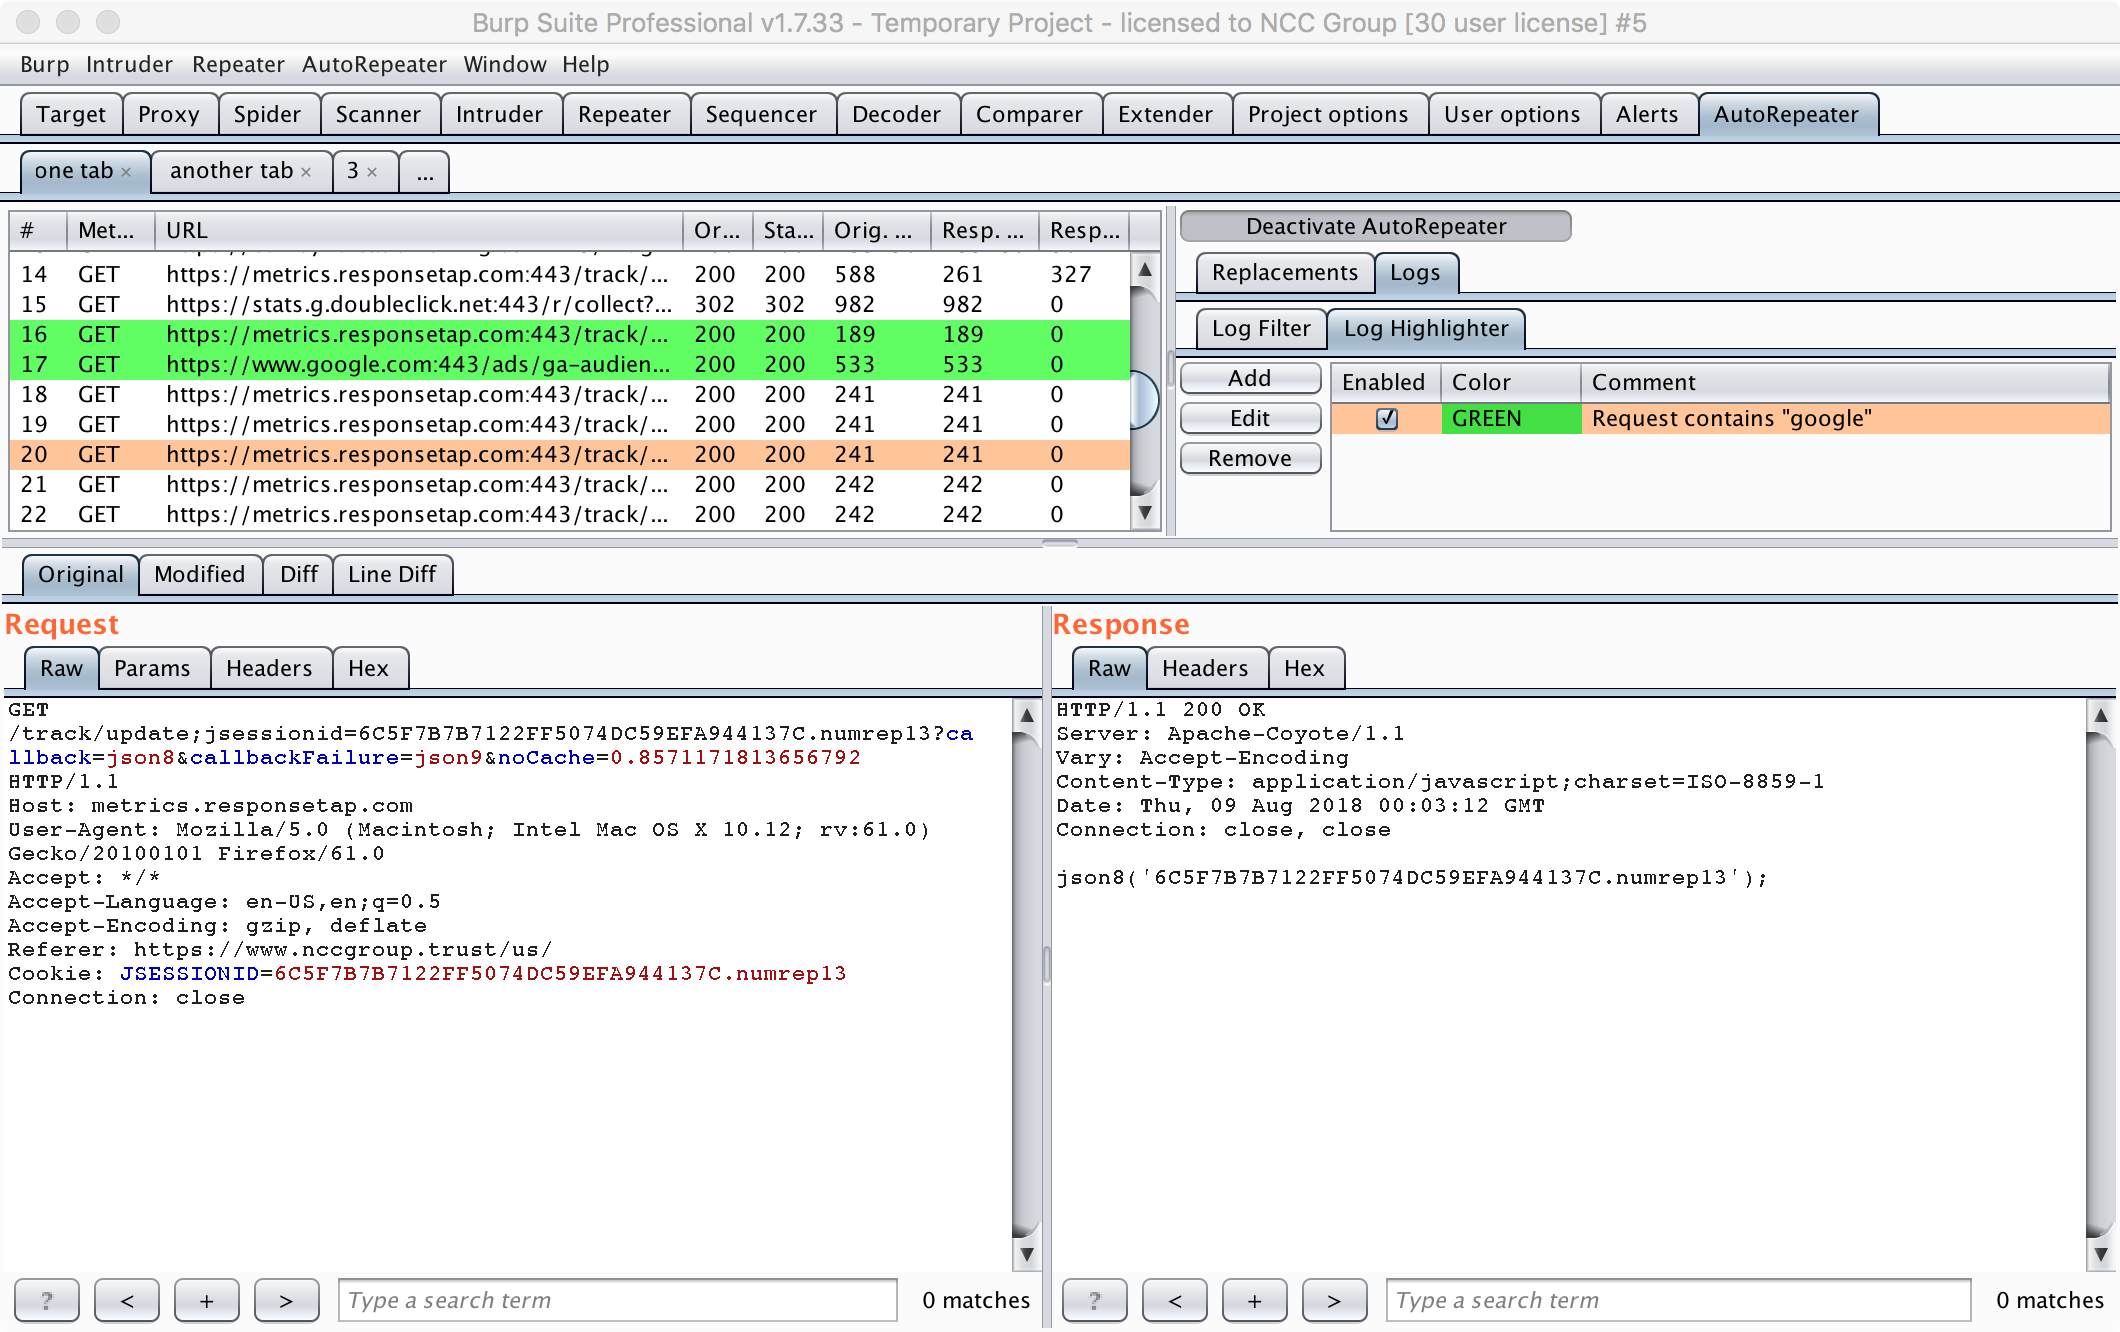
Automated HTTP Request Repeating With Burp Suite

AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)

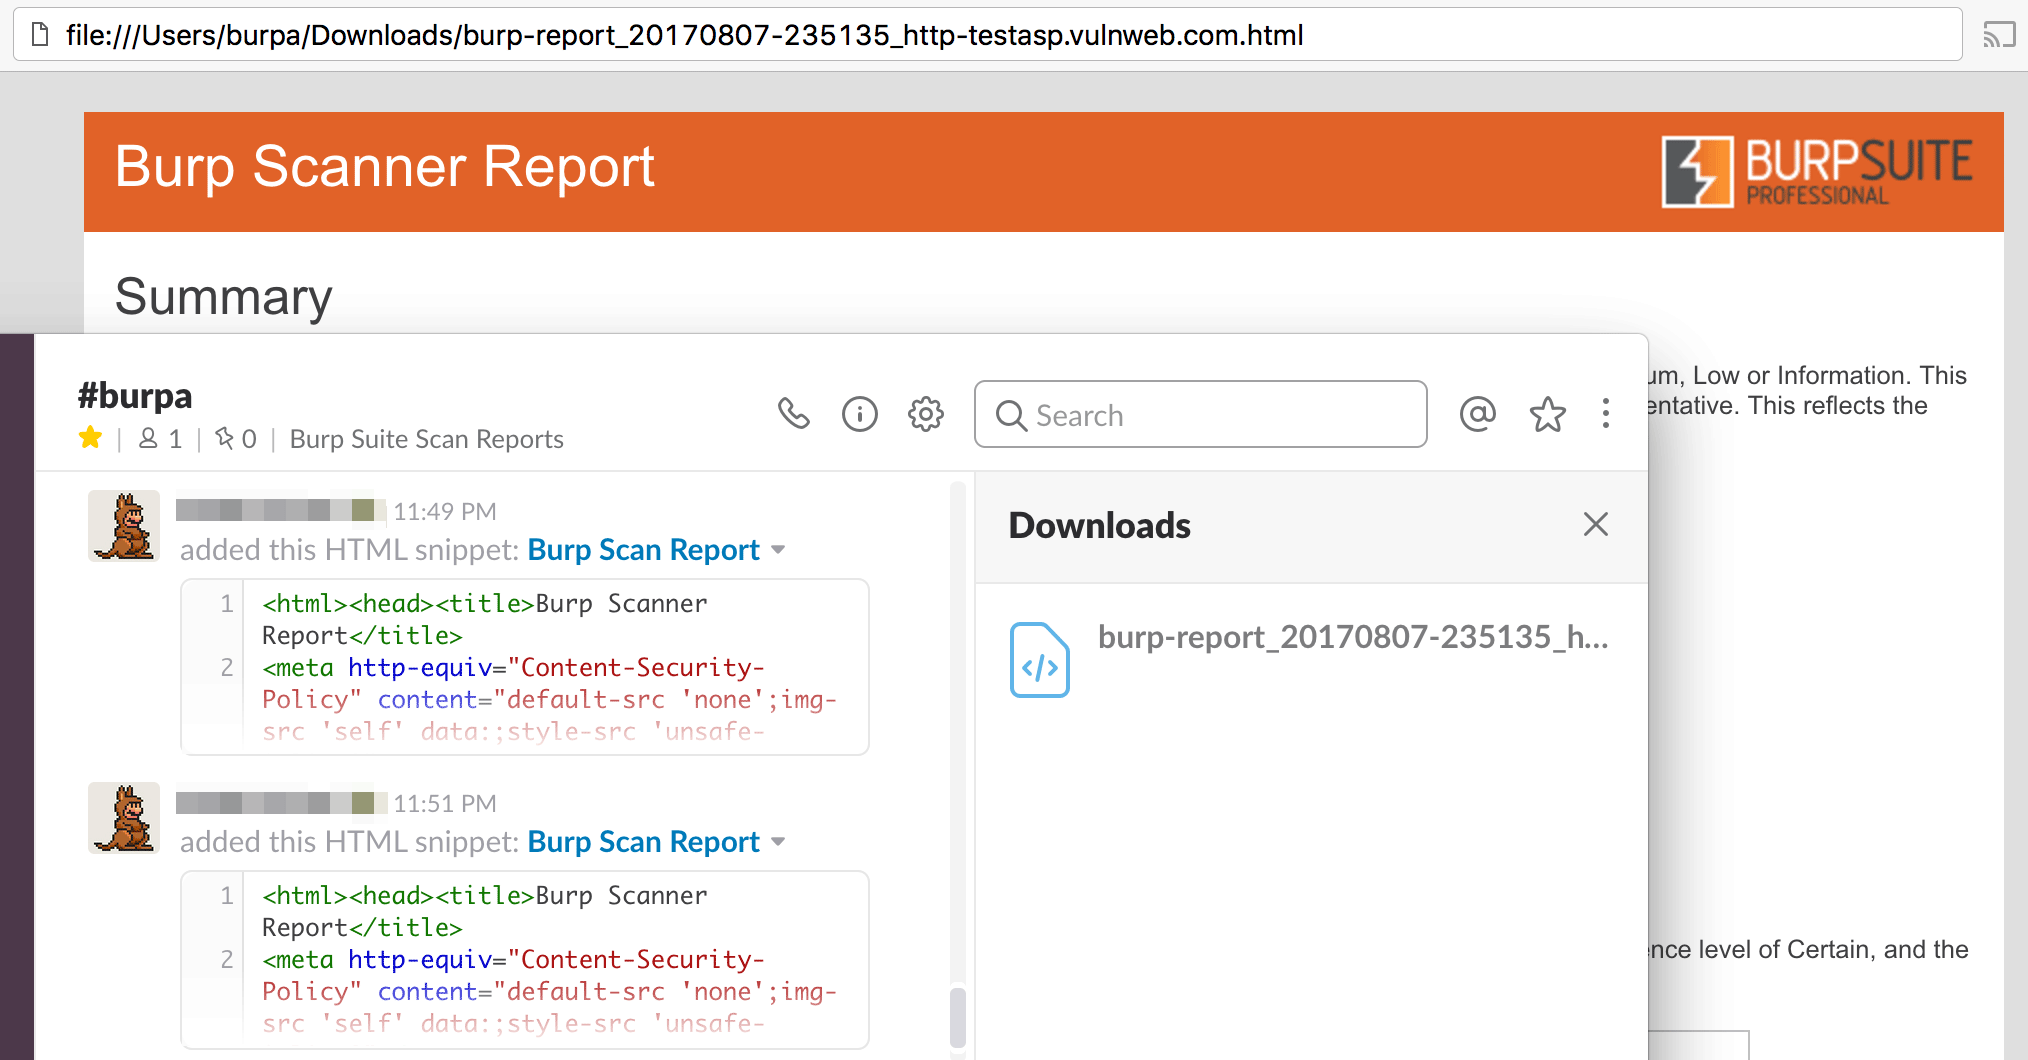
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…

Tests your WAF with +160 payloads

This script communicates with the Nessus API in an attempt to help with automating scans. Depending on the flag issued with the script, you can list…

Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

GraphQL security auditing script with a focus on performing batch GraphQL queries and mutations

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…

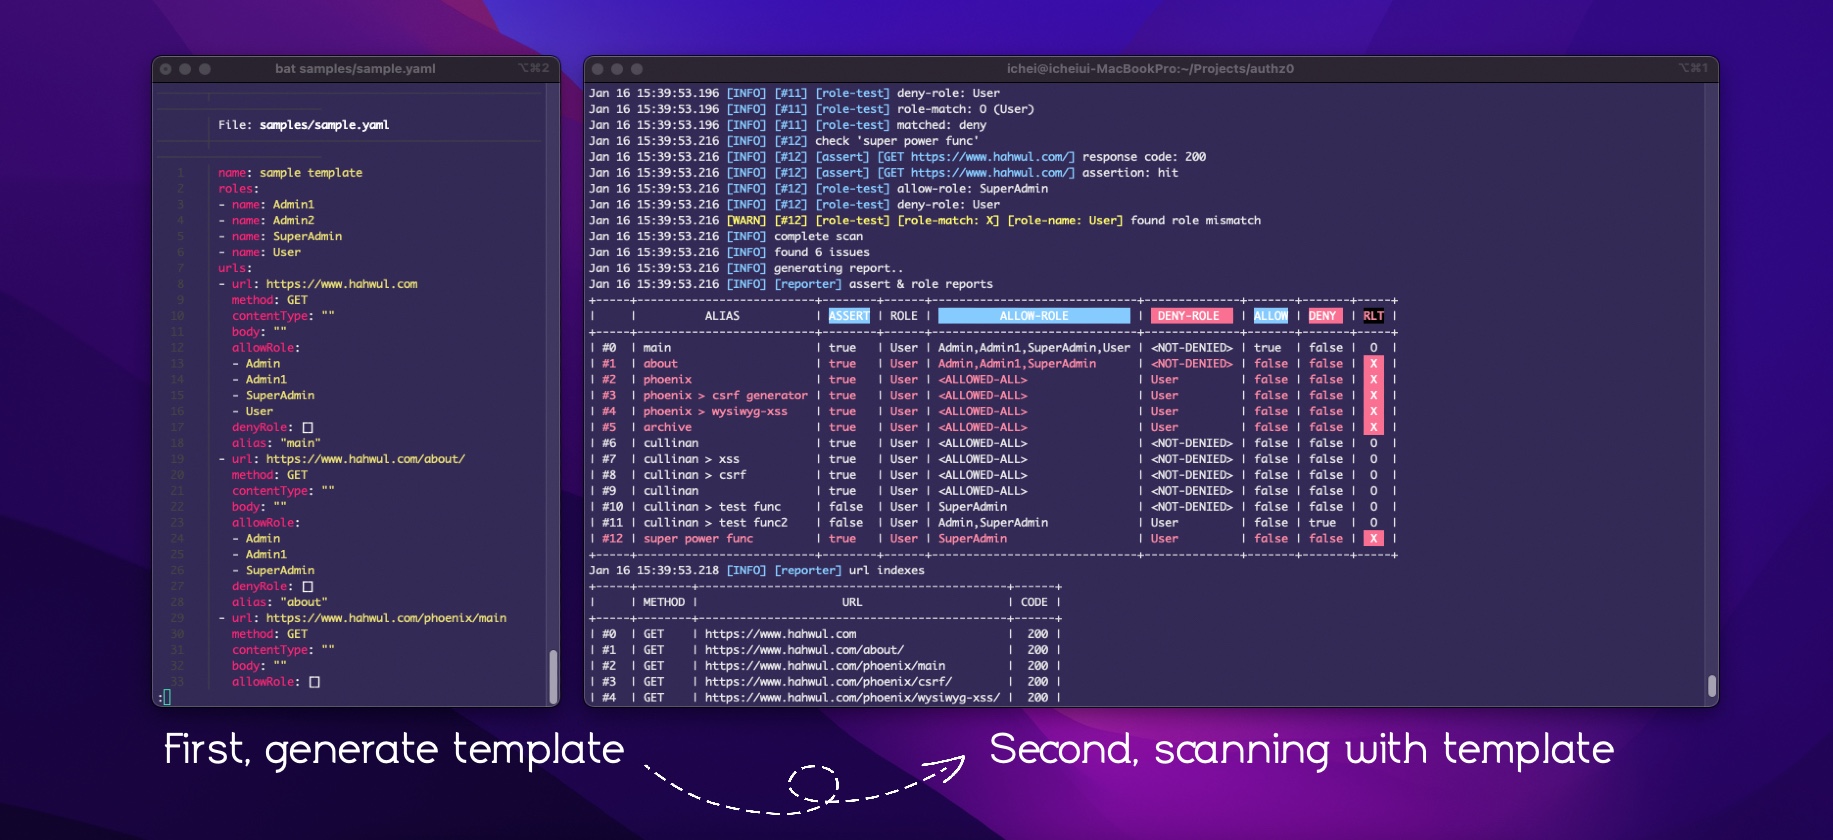
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…