

faraday_burp
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
api-security-testingdevsecopspenetration-testing+3
infobyte/faraday_burpBurp Extension for collaboration in Faraday
 b0rn2d/spring-cloud-gateway-nacos
Nacos下Spring-Cloud-Gateway CVE-2022-22947利用环境
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
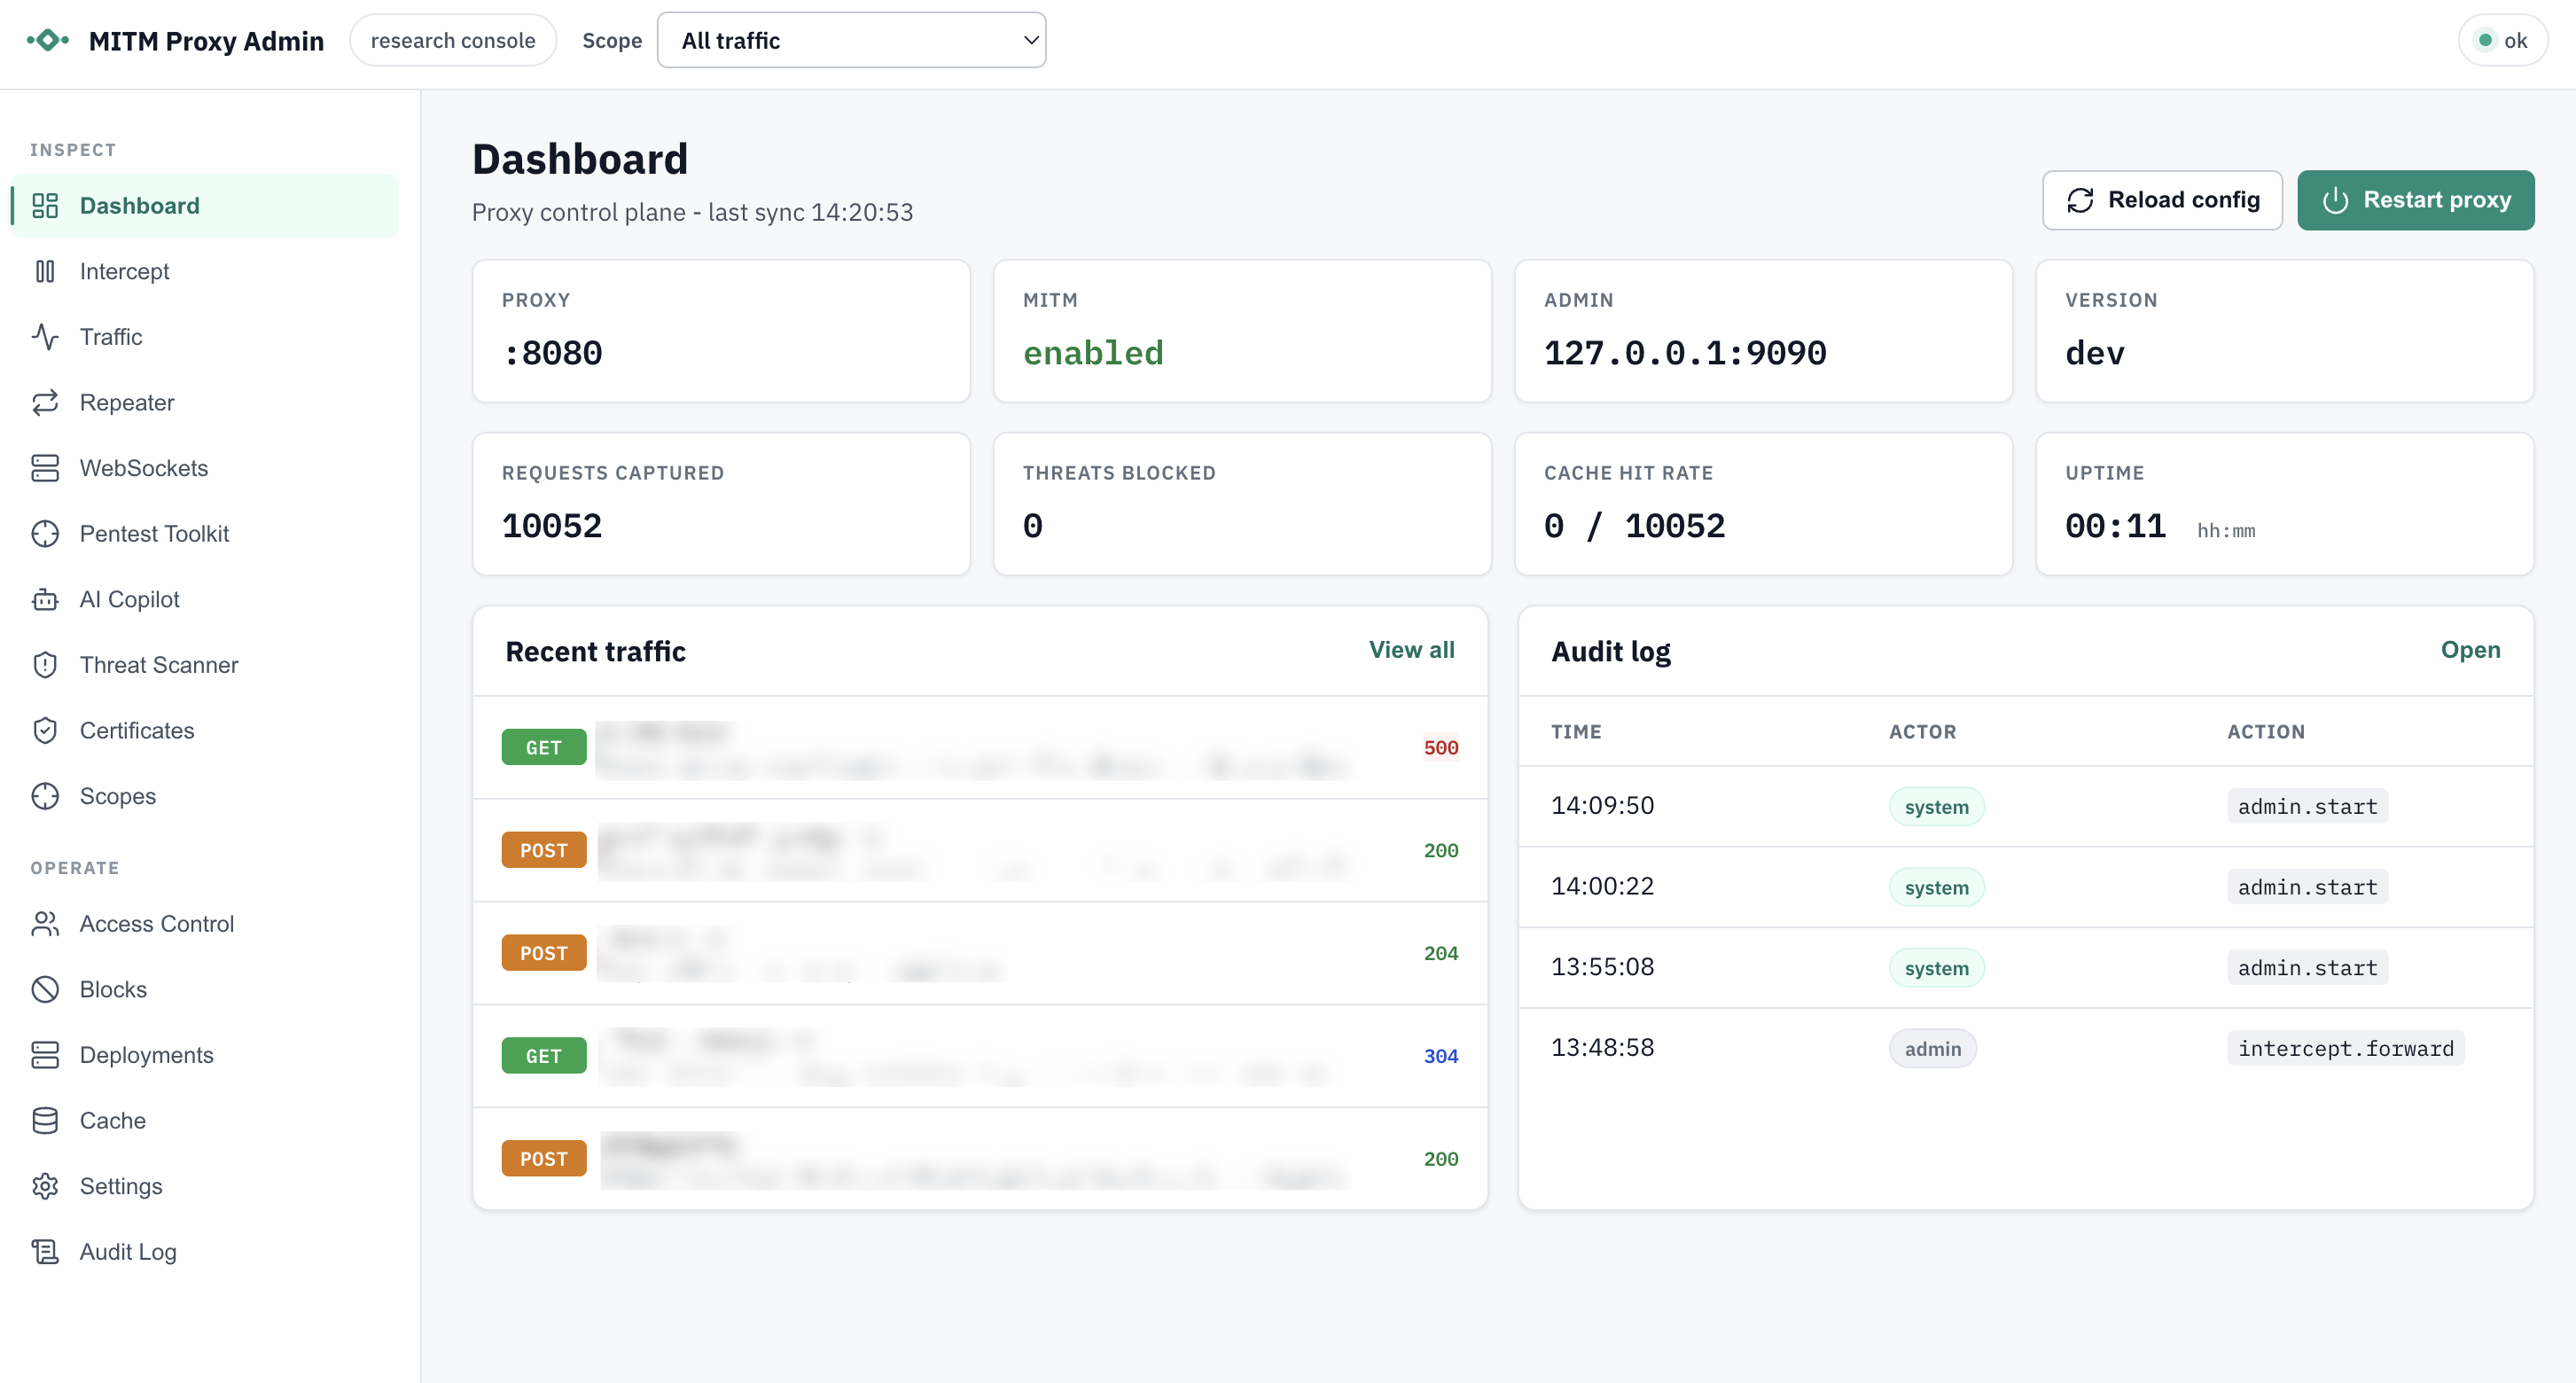 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
 vertexcover-io/strot
API Scraper Agent for Web API's
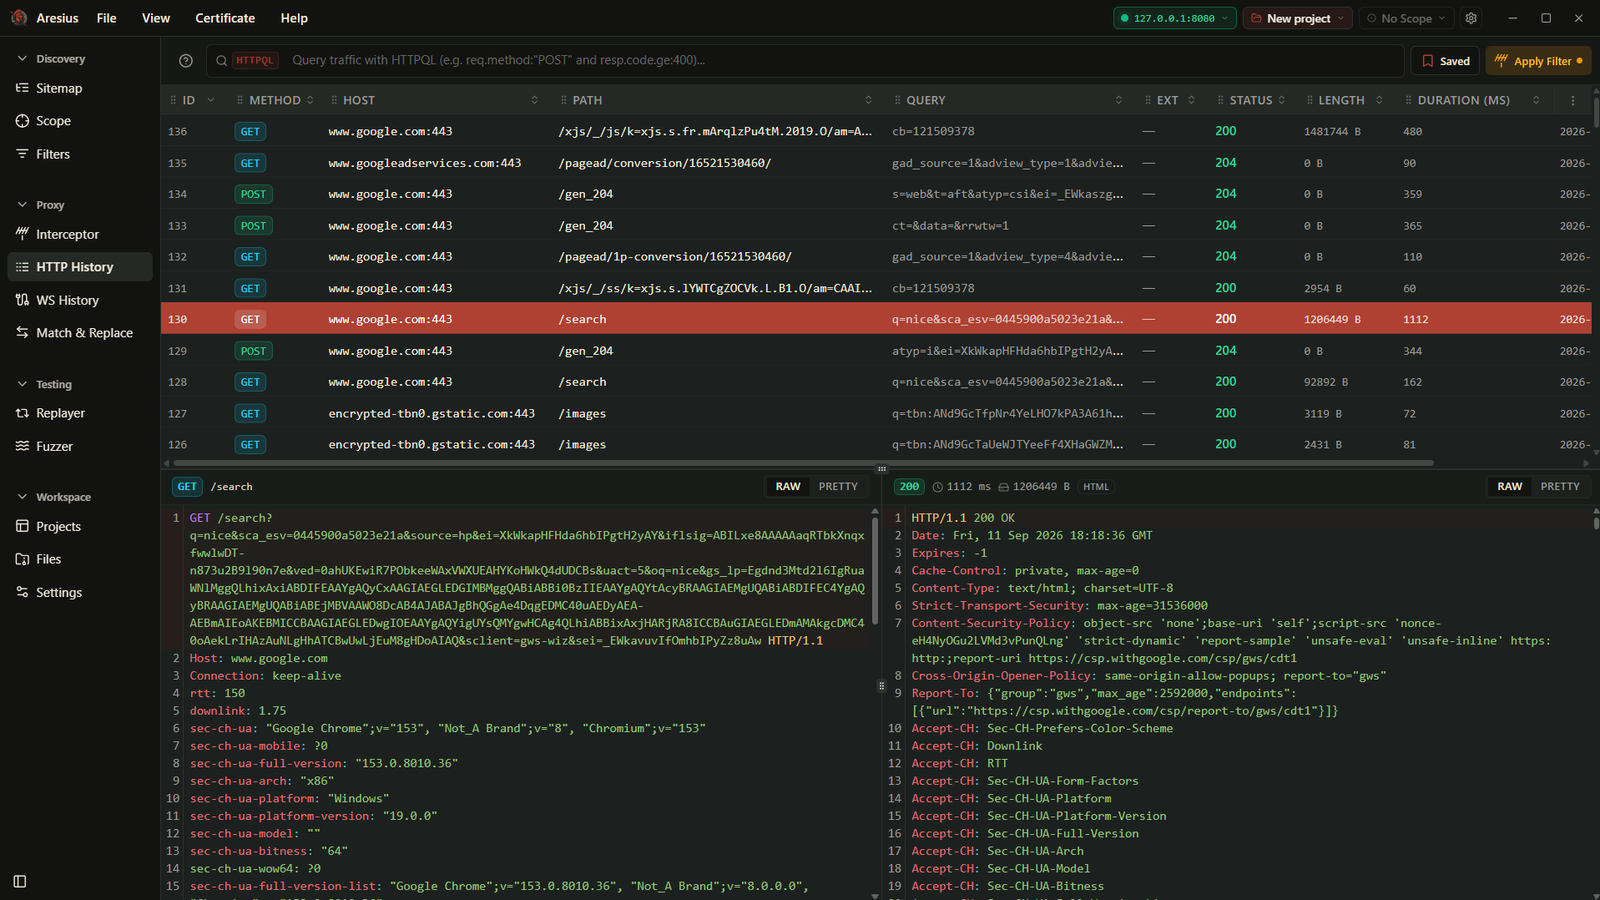 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
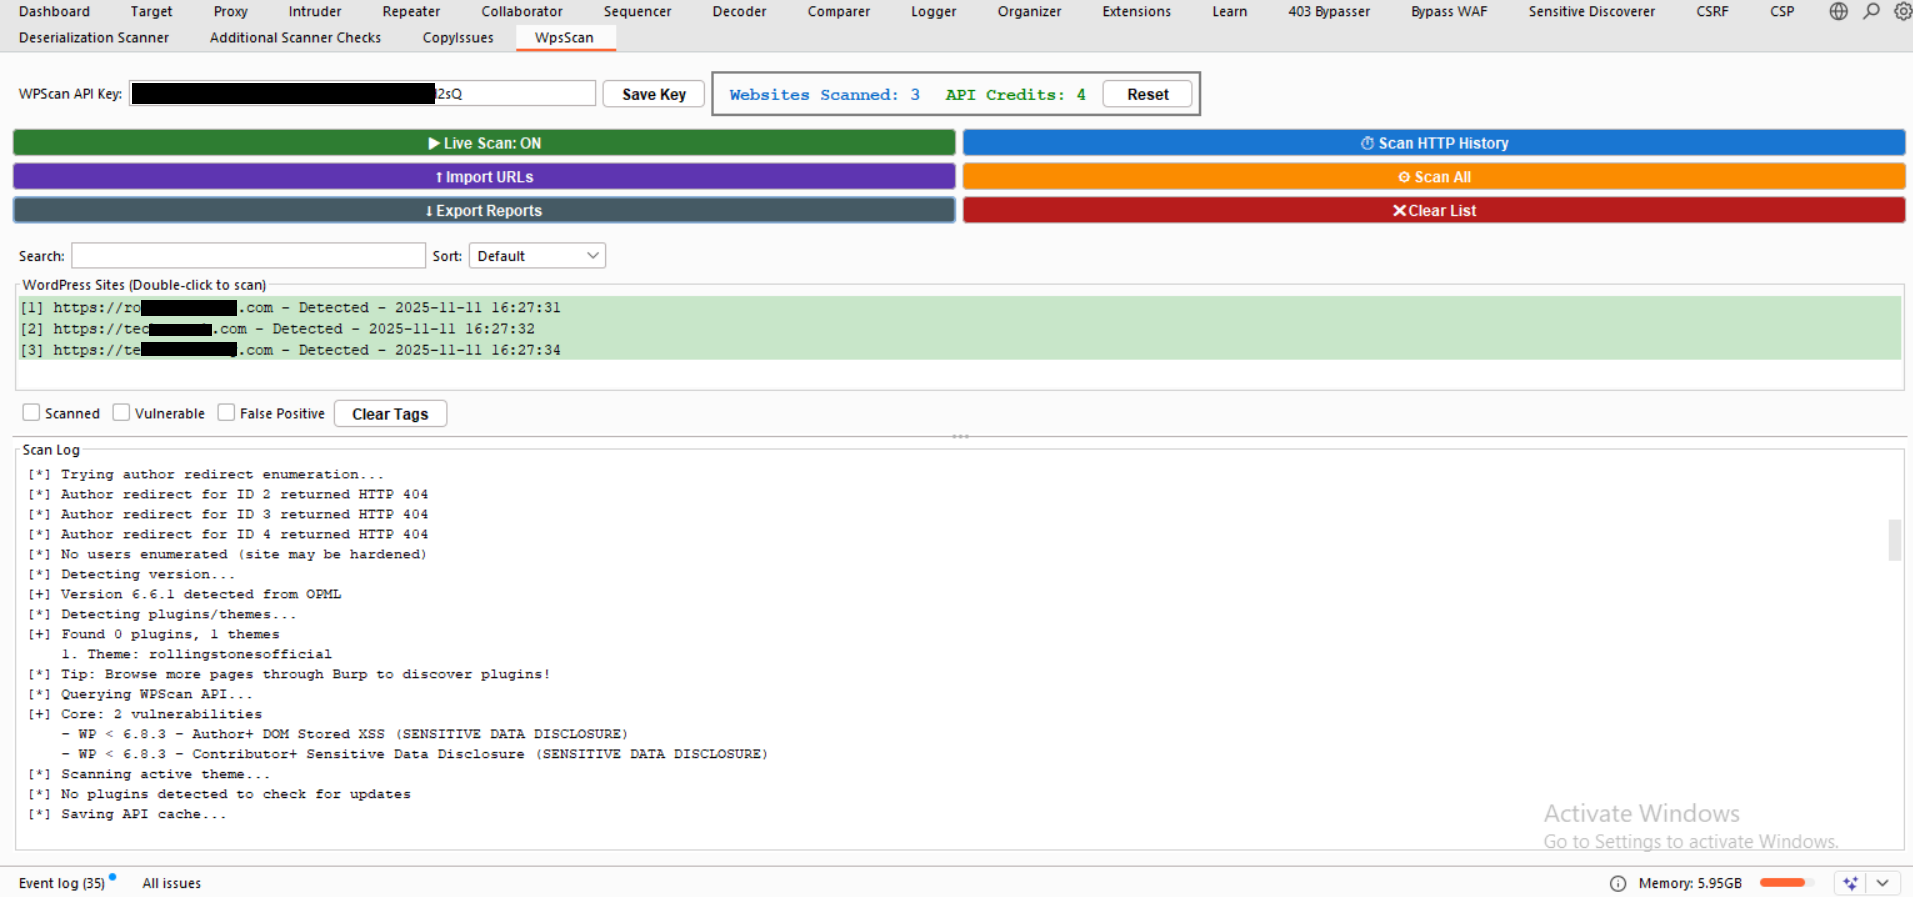 teycir/burpwpsscan
Burp extension for wordpress security scanning
 yutusec/apisix_crack
Apisix系列漏洞:未授权漏洞(CVE-2021-45232)、默认秘钥(CVE-2020-13945)批量探测。
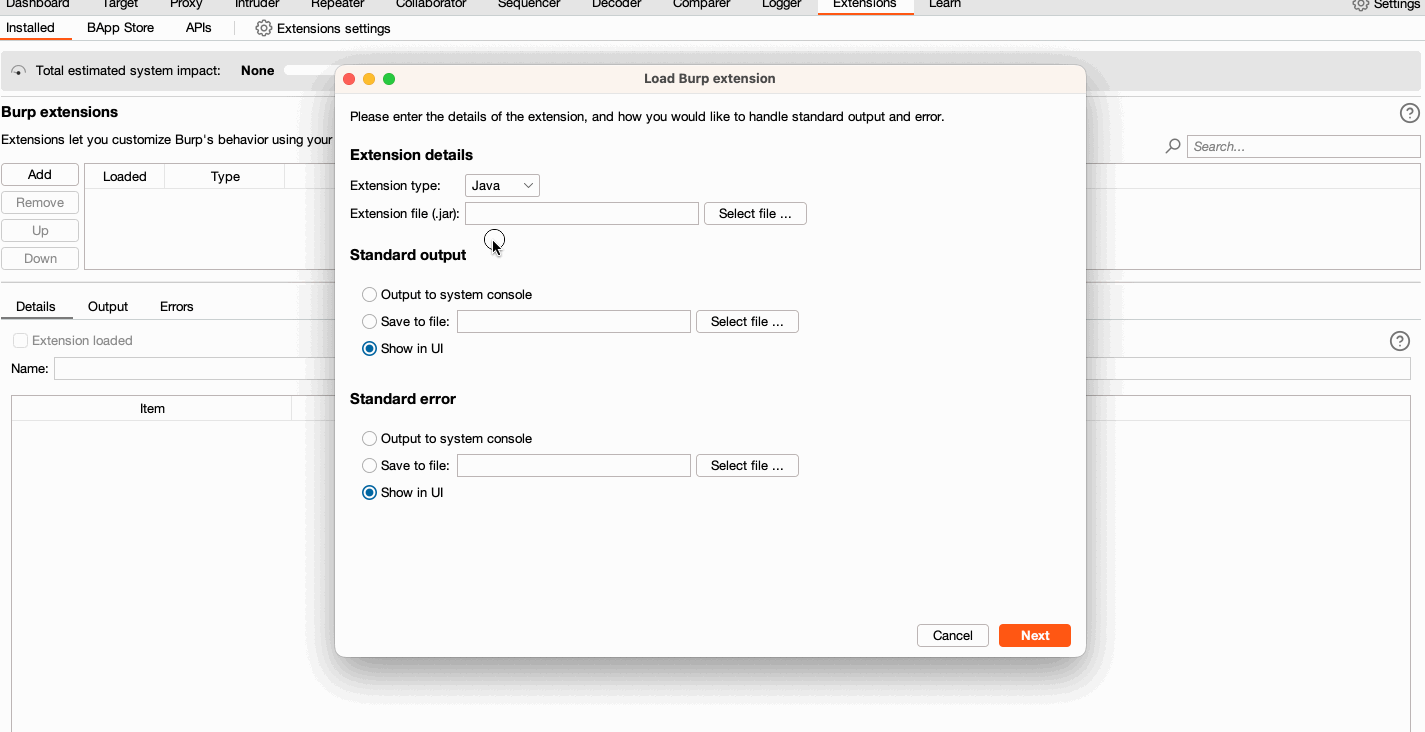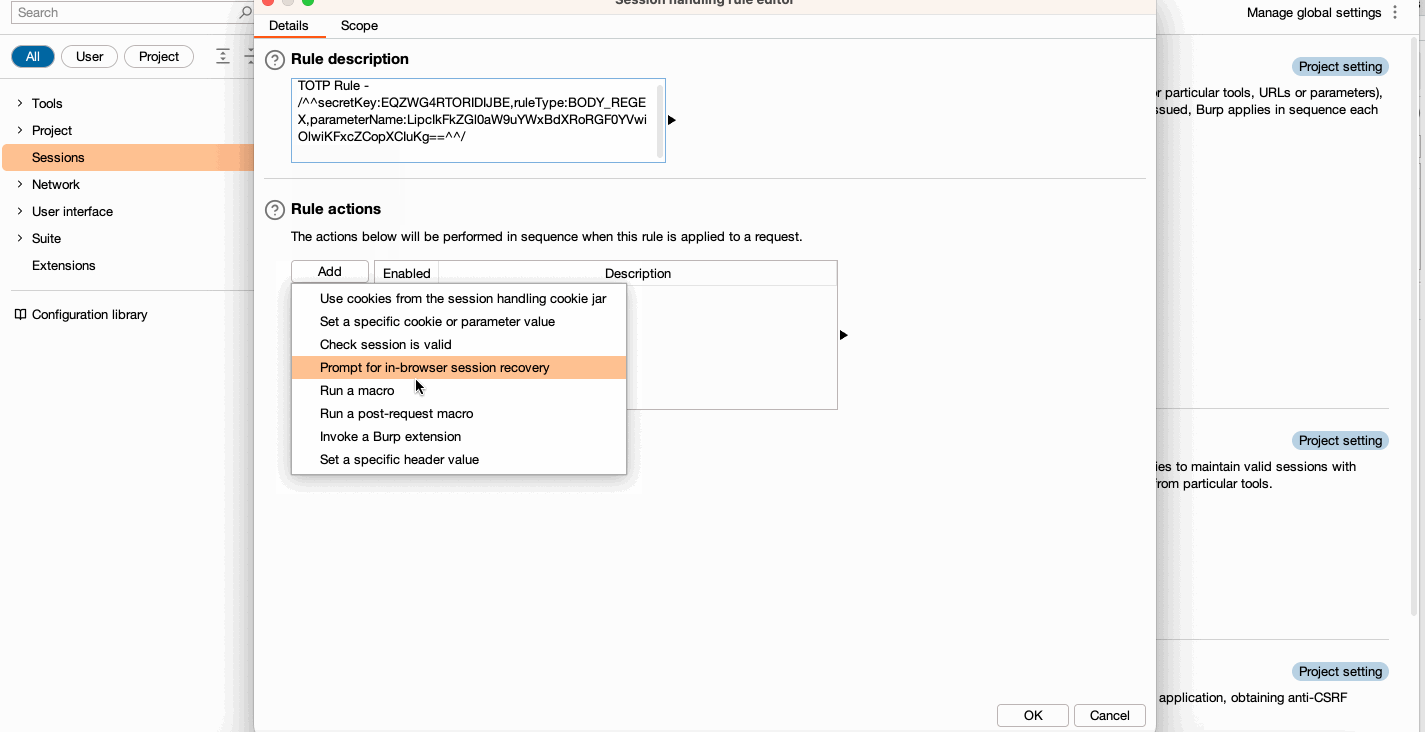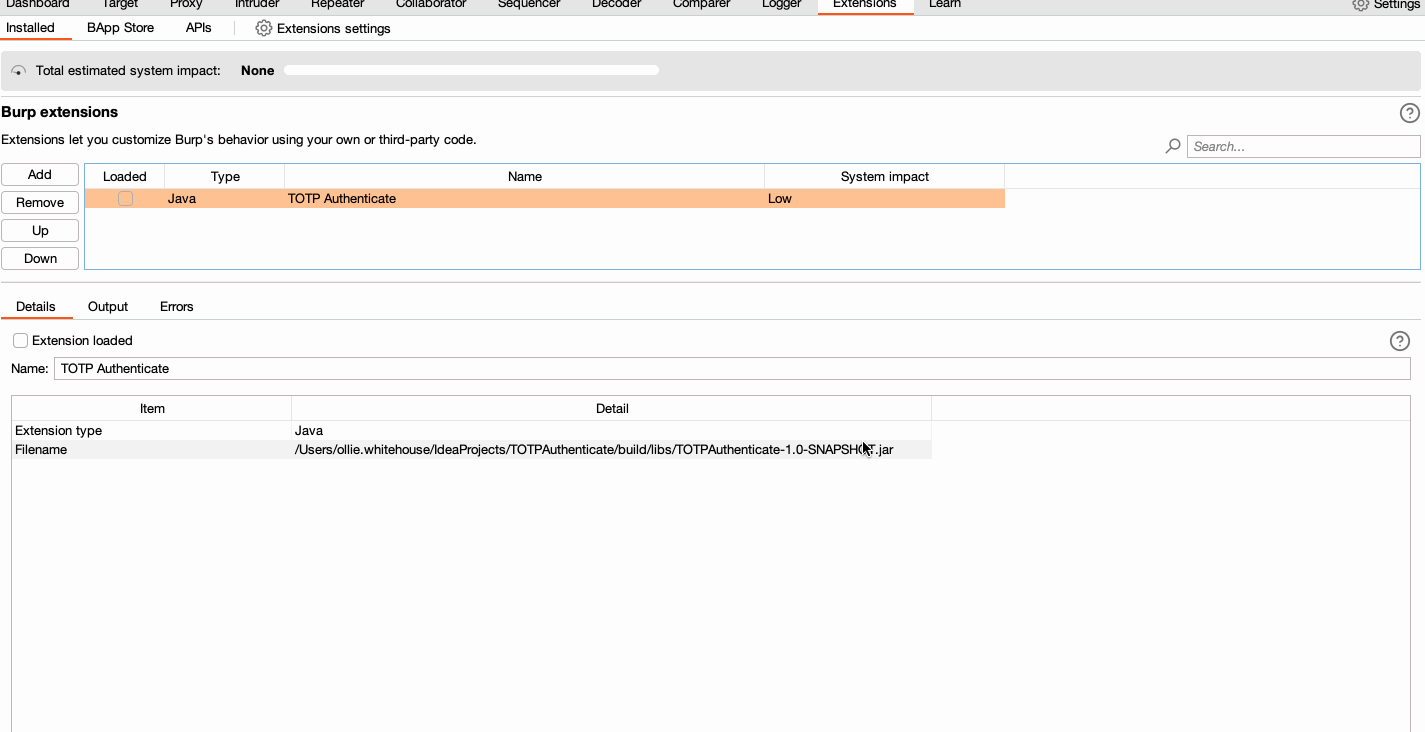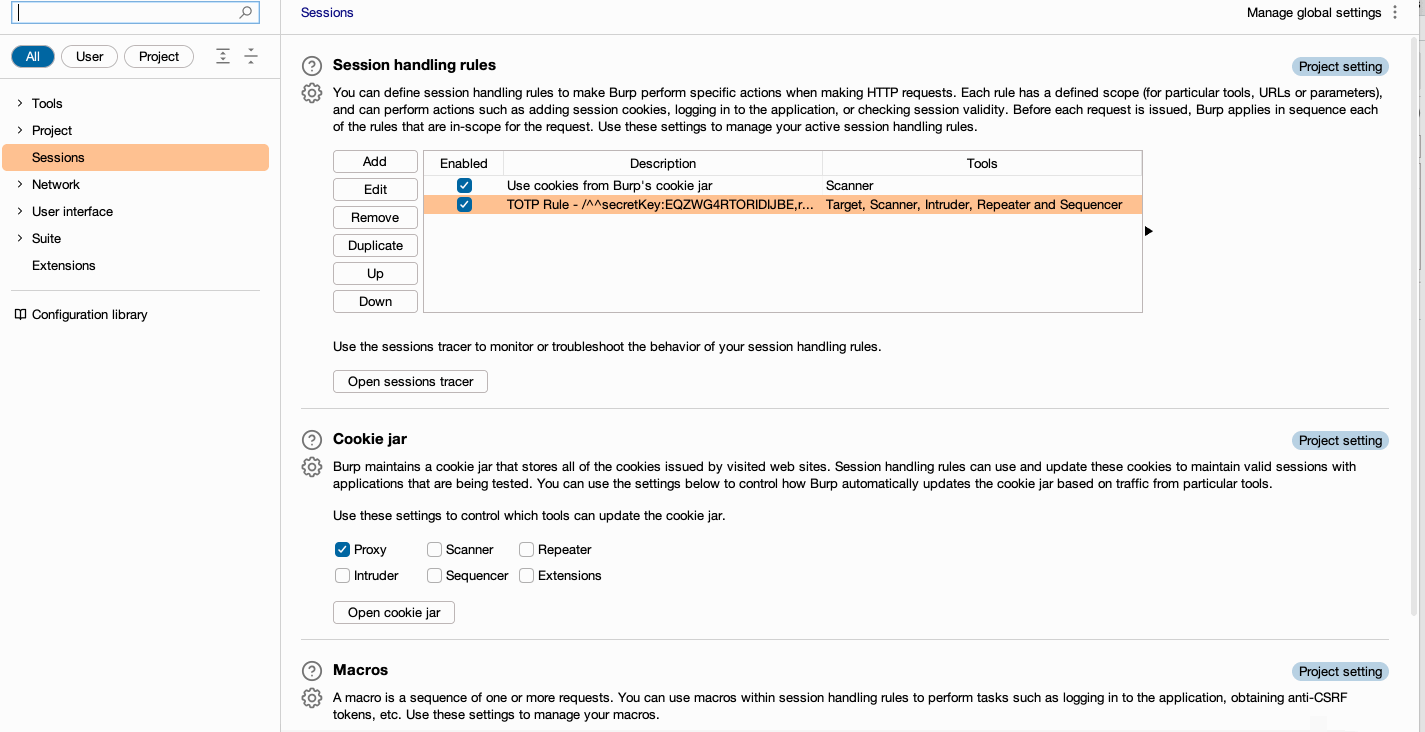 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
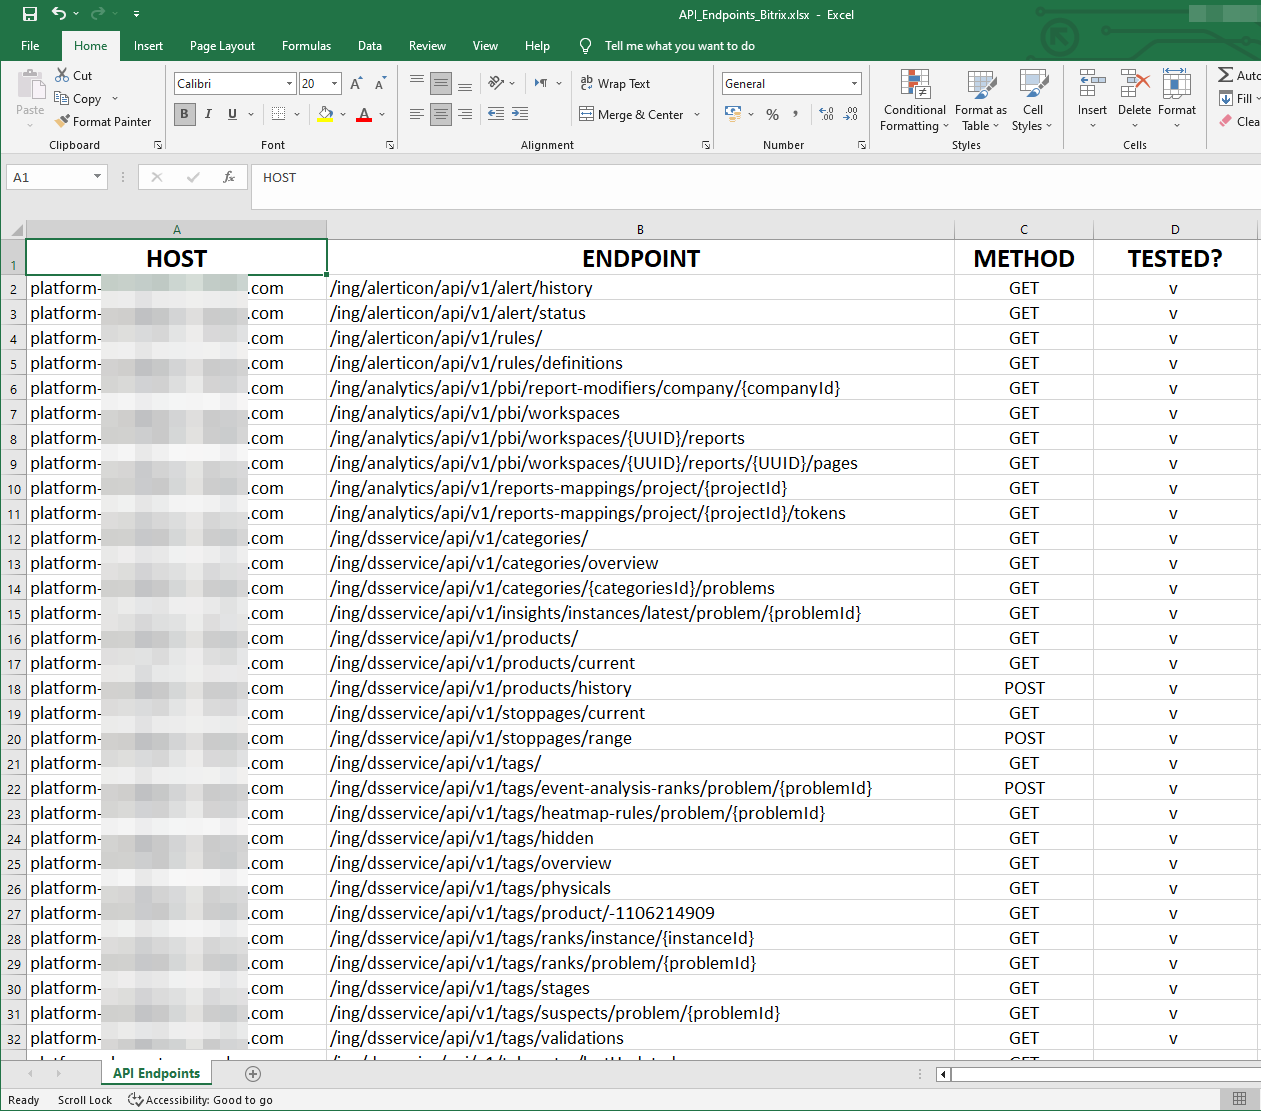 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 yutusec/spel
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947)批量检测工具
 hunzi0/cve-2022-22947-rce_poc
批量url检测Spring-Cloud-Gateway-CVE-2022-22947
 licitrasimone/cve-2026-75157-poc
Standalone authorized universal HTTP PoC for CVE-2026-75157
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…