

repeat-strike
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
ai-securityapi-security-testinginformation-gathering+6
41
hackvertor/repeat-strikeBurp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
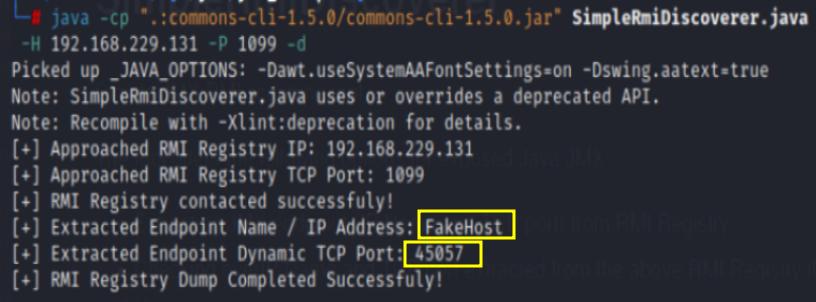 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
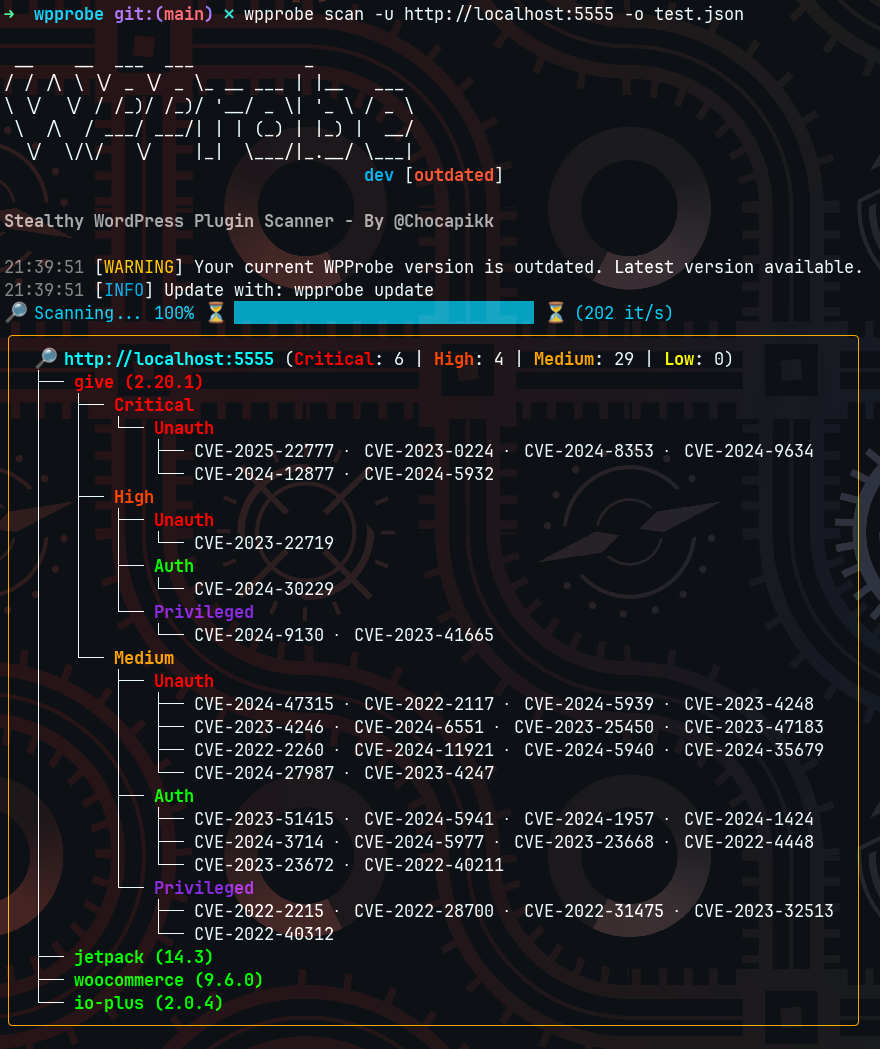 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
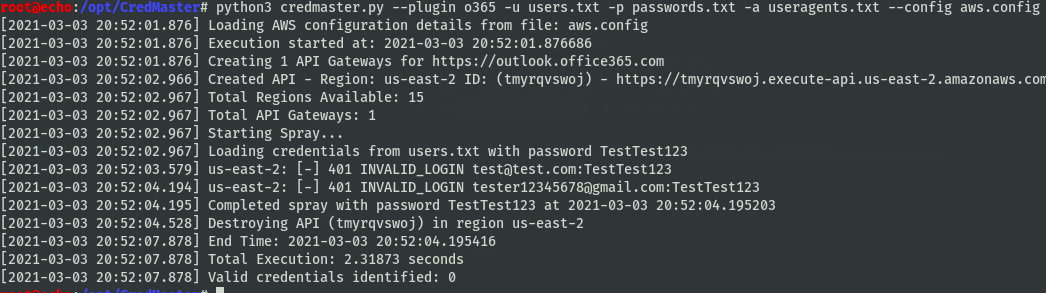 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
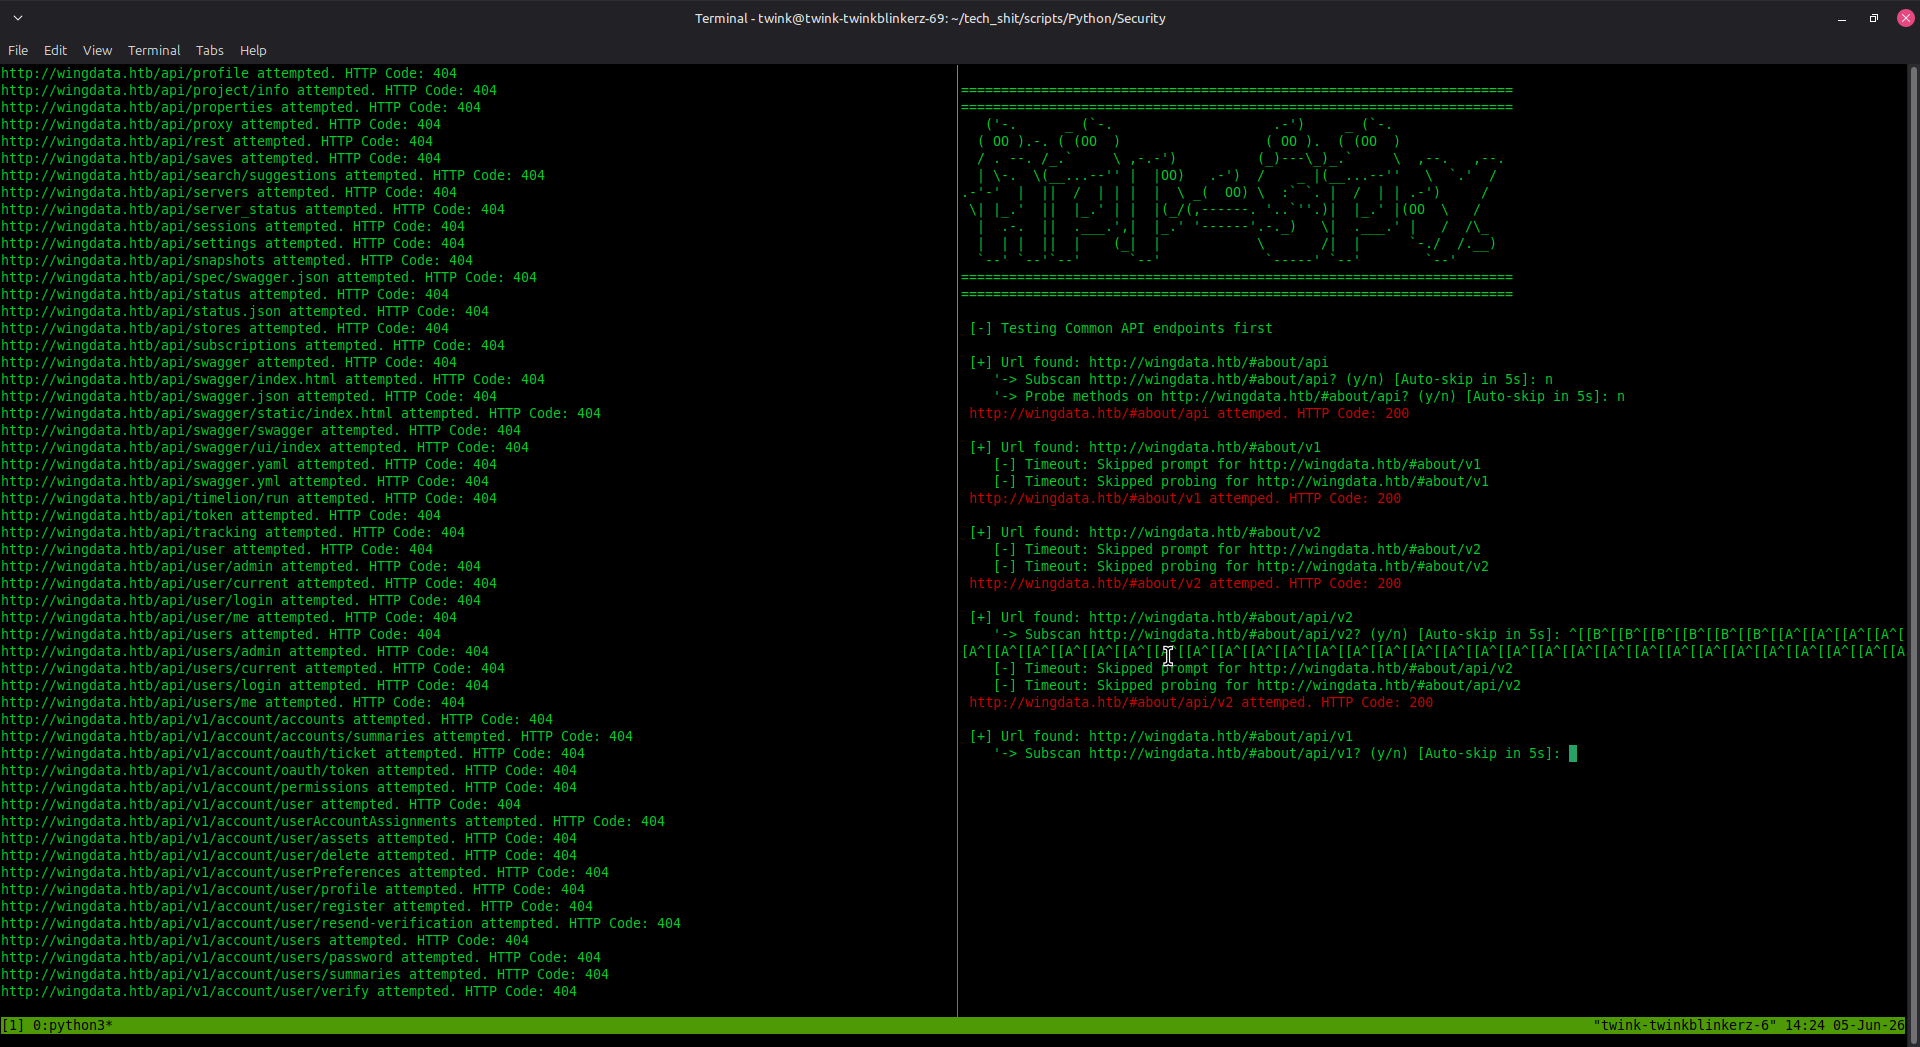 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
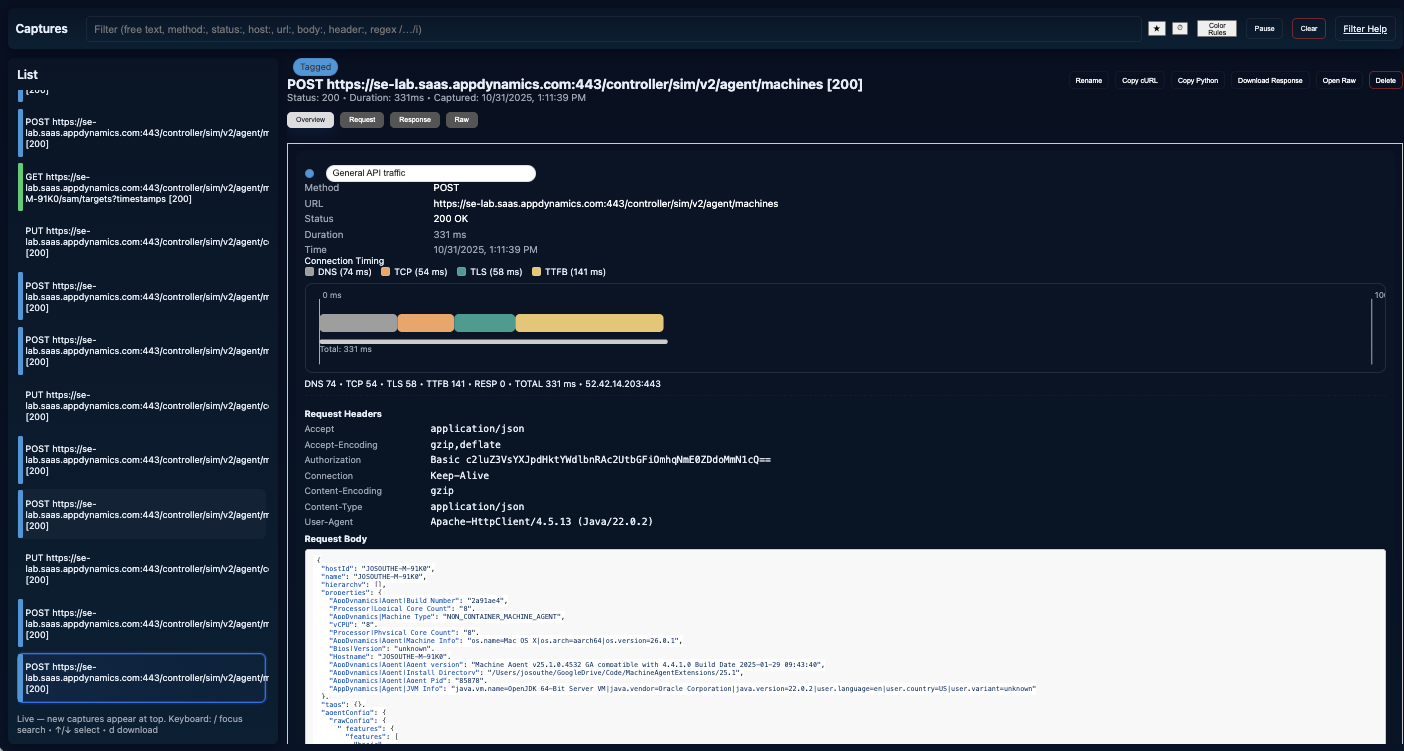 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication