
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
45 results
WindowsMemPageDelta preview

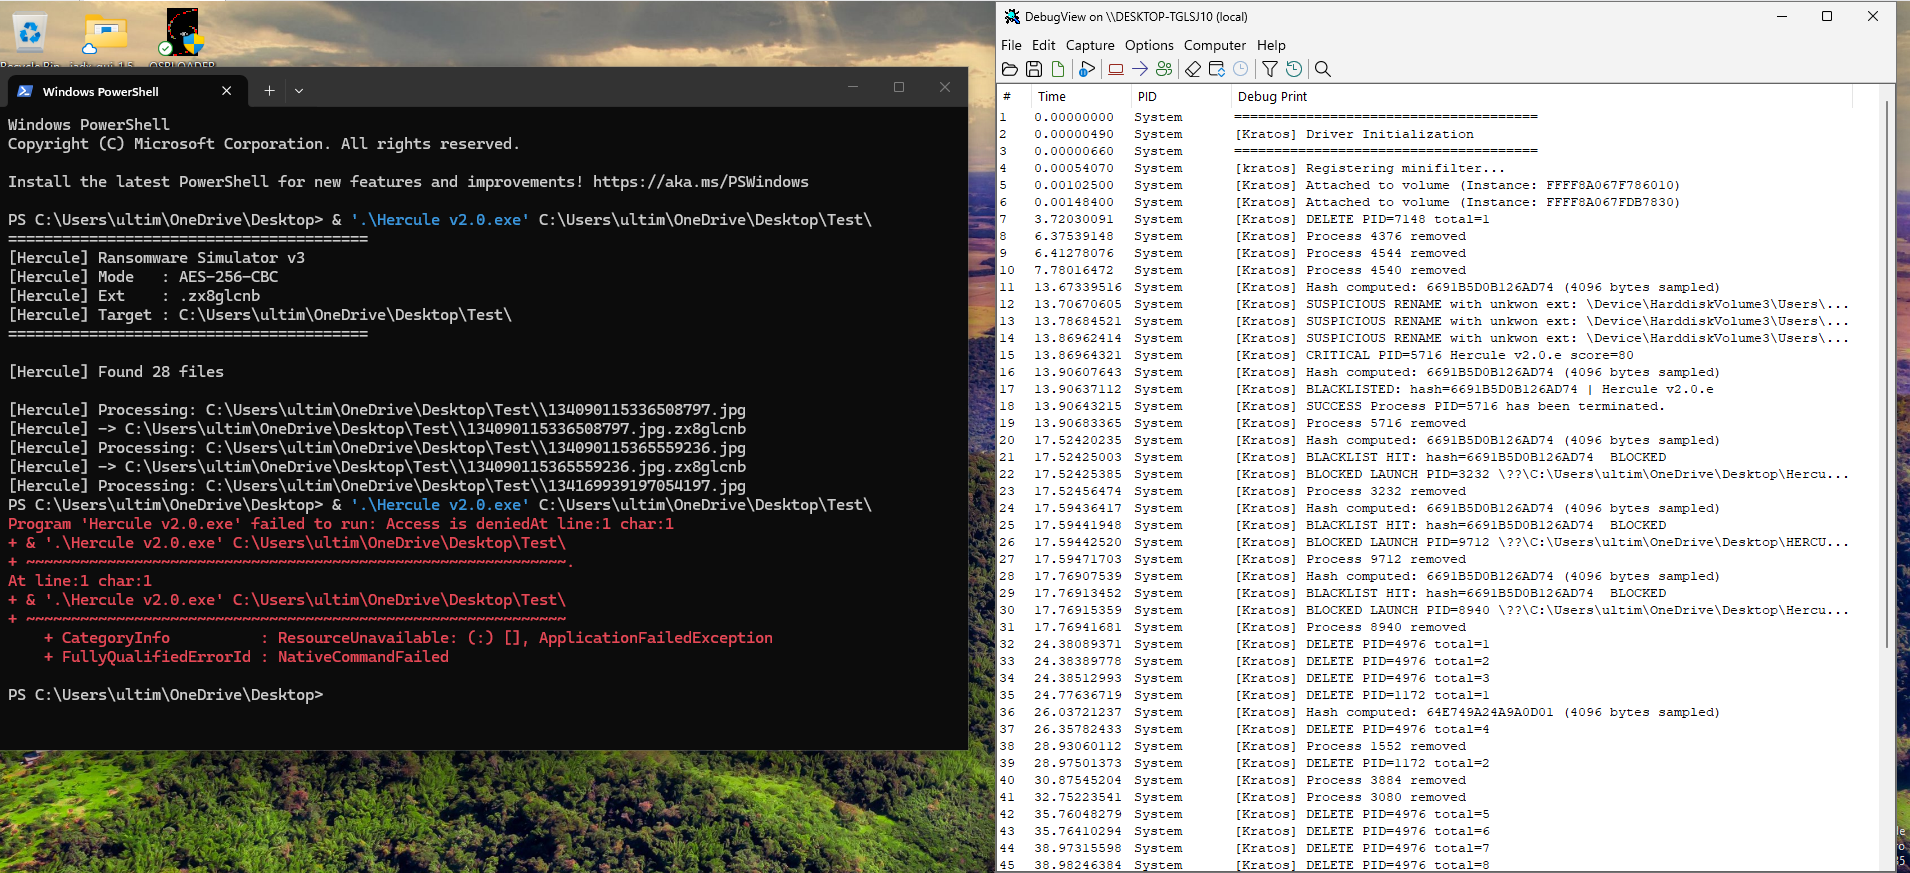
WindowsMemPageDelta

GitHubnccgroup/windowsmempagedelta

A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
anomaly-detectiondefensive-toolslog-analysis+1
33
5 years ago
kratosminifilter preview

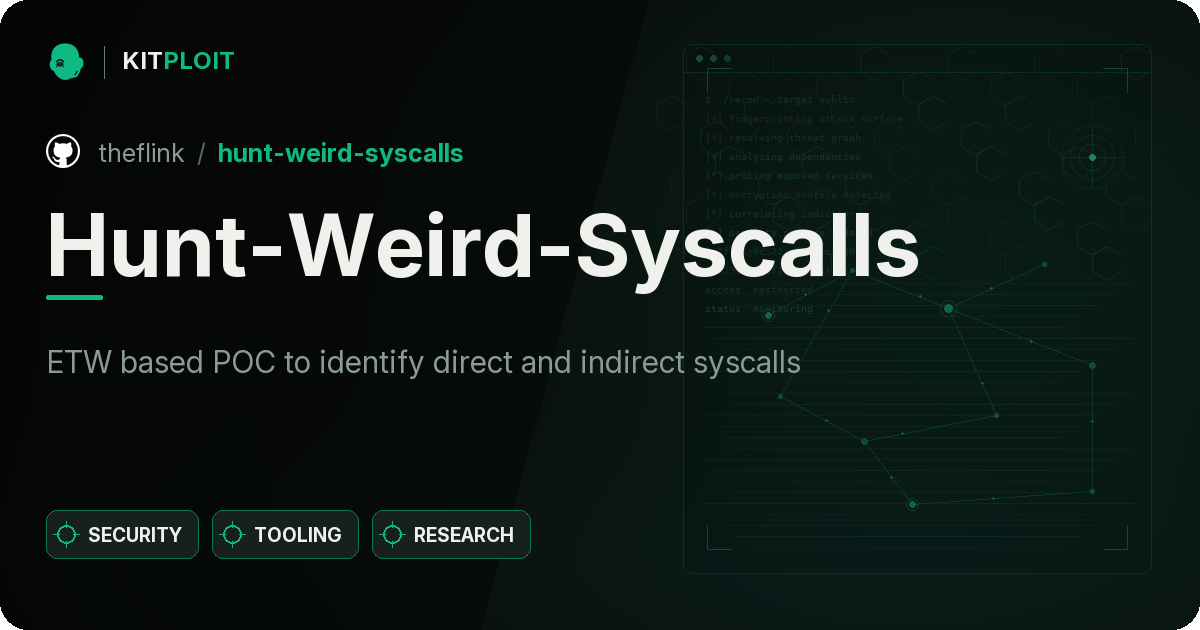
kratosminifilter

GitHubmukendi/kratosminifilter

Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize
anomaly-detectiondefensive-toolsincident-response+2
419 days ago
Hunt-Weird-Syscalls preview

Hunt-Weird-Syscalls

GitHubtheflink/hunt-weird-syscalls

ETW based POC to identify direct and indirect syscalls
anomaly-detectiondefensive-toolsintrusion-detection+1
1973 years ago
monitor preview

monitor

GitHubbetterdb-inc/monitor

Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
anomaly-detectiondatabase-securitylog-analysis
1.3k4h 36m ago
KilledProcessCanary preview

KilledProcessCanary

GitHubnccgroup/killedprocesscanary

A canary designed to minimize the impact from certain Ransomware actors
anomaly-detectiondefensive-toolsdigital-forensics+2
1015 years ago
DetectWindowsCopyOnWriteForAPI preview

DetectWindowsCopyOnWriteForAPI

GitHubnccgroup/detectwindowscopyonwriteforapi

Enumerate various traits from Windows processes as an aid to threat hunting
anomaly-detectiondefensive-toolsforensics+3
1974 years ago
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
anomaly-detectionbinary-analysisdefensive-tools+4
19 months ago
CVE-2024-38063 preview

CVE-2024-38063

GitHubskac44/cve-2024-38063

Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…
anomaly-detectioneducationexploitation+4
1 year ago
dns_watchdog_windows2 preview

dns_watchdog_windows2

GitHubmicrolaser/dns_watchdog_windows2

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

anomaly-detectiondefensive-toolsdns-analysis+5
15 days ago
zeek-xor-exe-plugin preview

zeek-xor-exe-plugin

GitHubcorelight/zeek-xor-exe-plugin

Zeek plugin to detect and decrypt XOR-encrypted EXEs
anomaly-detectionbinary-analysisdynamic-analysis-sandboxing+5
52 years ago
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

anomaly-detectionbinary-analysisdigital-forensics+3
614 years ago
defender preview

defender

GitLab0warn/defender

This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…

anomaly-detectionauthenticationconfiguration-auditing+6
6 months ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
anomaly-detectiondigital-forensicsincident-response+5
7381 month ago
PortDog preview

PortDog

GitHubpuniaze/portdog

Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
anomaly-detectiondefensive-toolsintrusion-detection+3
13411 years ago
latma preview

latma

GitHubsilverfort-open-source/latma

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…

anomaly-detectioncloud-securityincident-response+5
803 years ago
mimikatz-detector-condrv preview

mimikatz-detector-condrv

GitHubnccgroup/mimikatz-detector-condrv

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…
anomaly-detectiondefensive-toolsincident-response+3
424 years ago
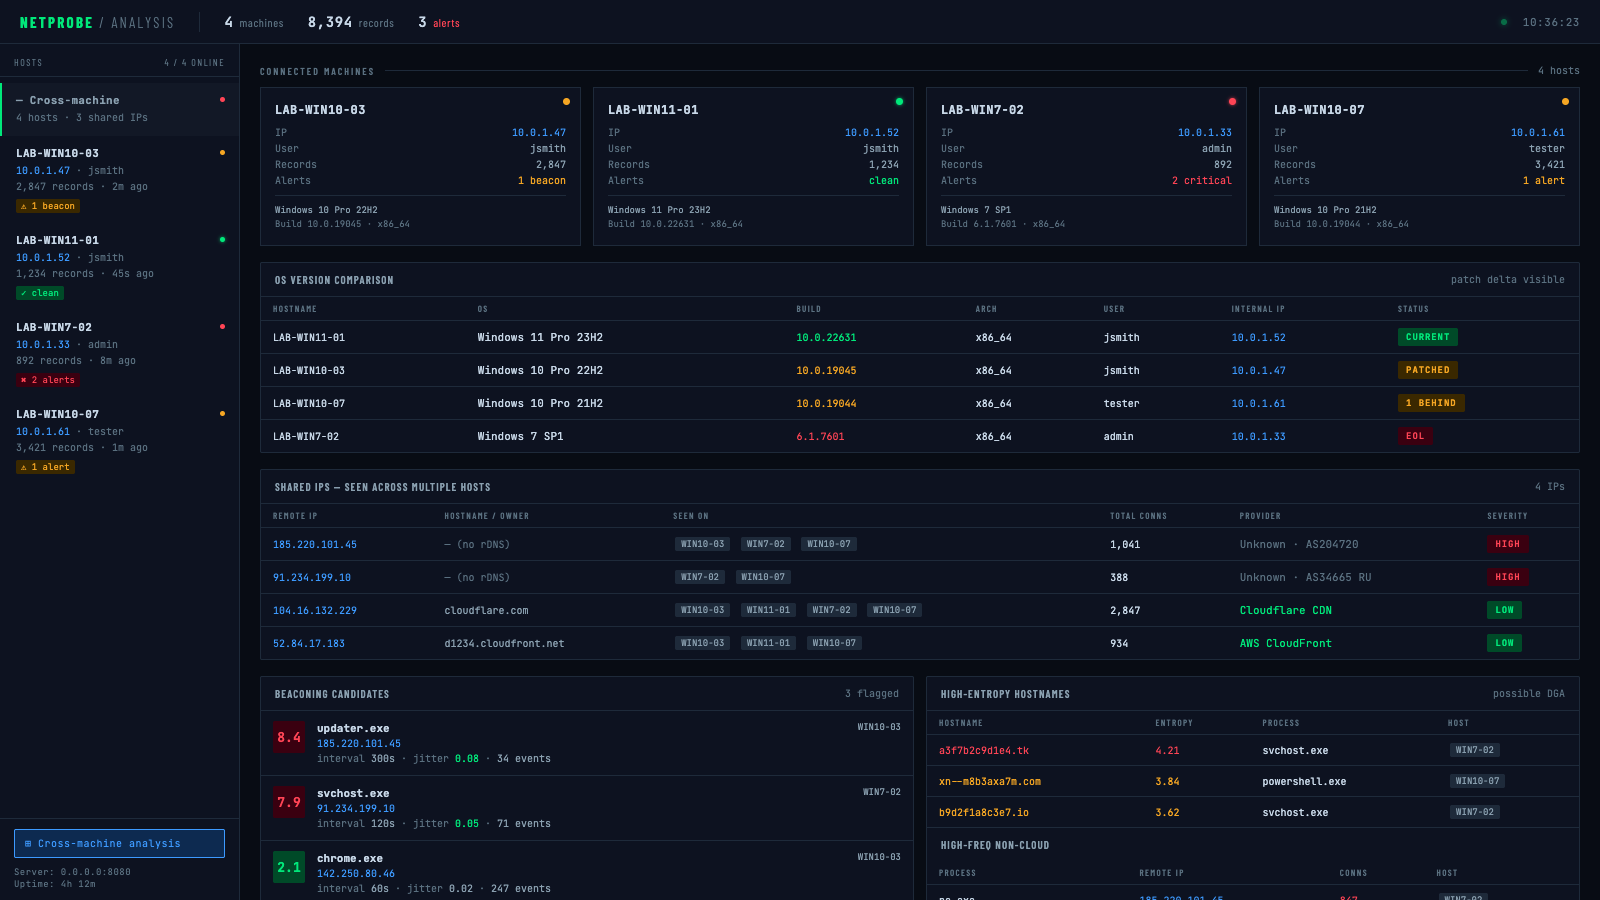
gibson preview

gibson

GitLabhackinglz/gibson

Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity
anomaly-detectioncloud-securitydefensive-tools+6
7 months ago
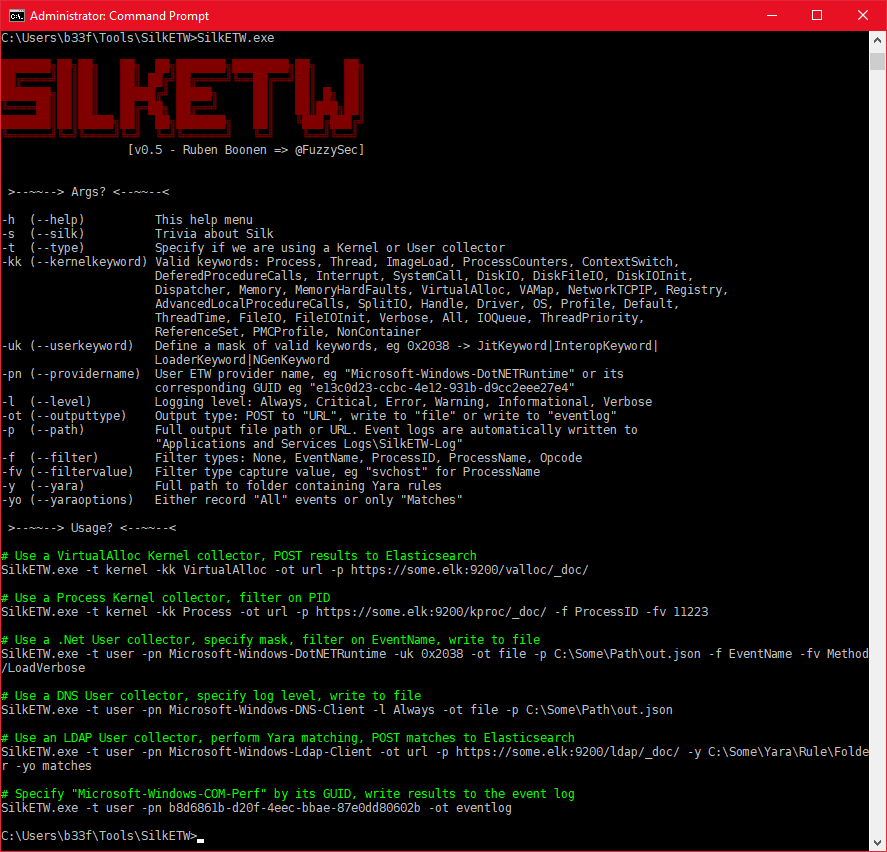
SilkETW preview
Archived

SilkETW

GitHubmandiant/silketw

C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

anomaly-detectiondefensive-toolsdigital-forensics+8
8523 years ago
Previous123Next