professional-services

Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…

Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…

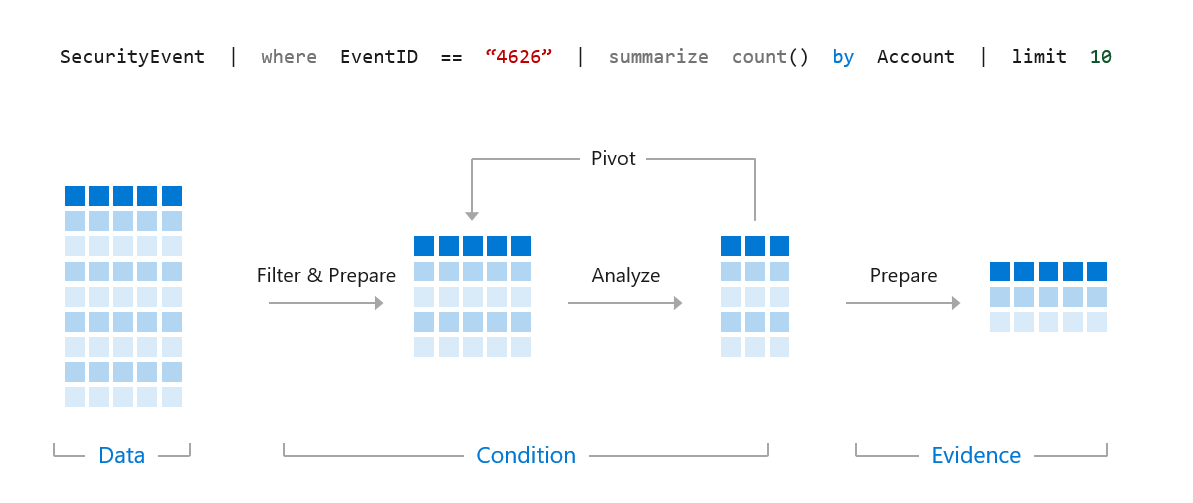
Collection of KQL queries

A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon

Open-source IoT Platform - Device management, data collection, processing and visualization.

Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…

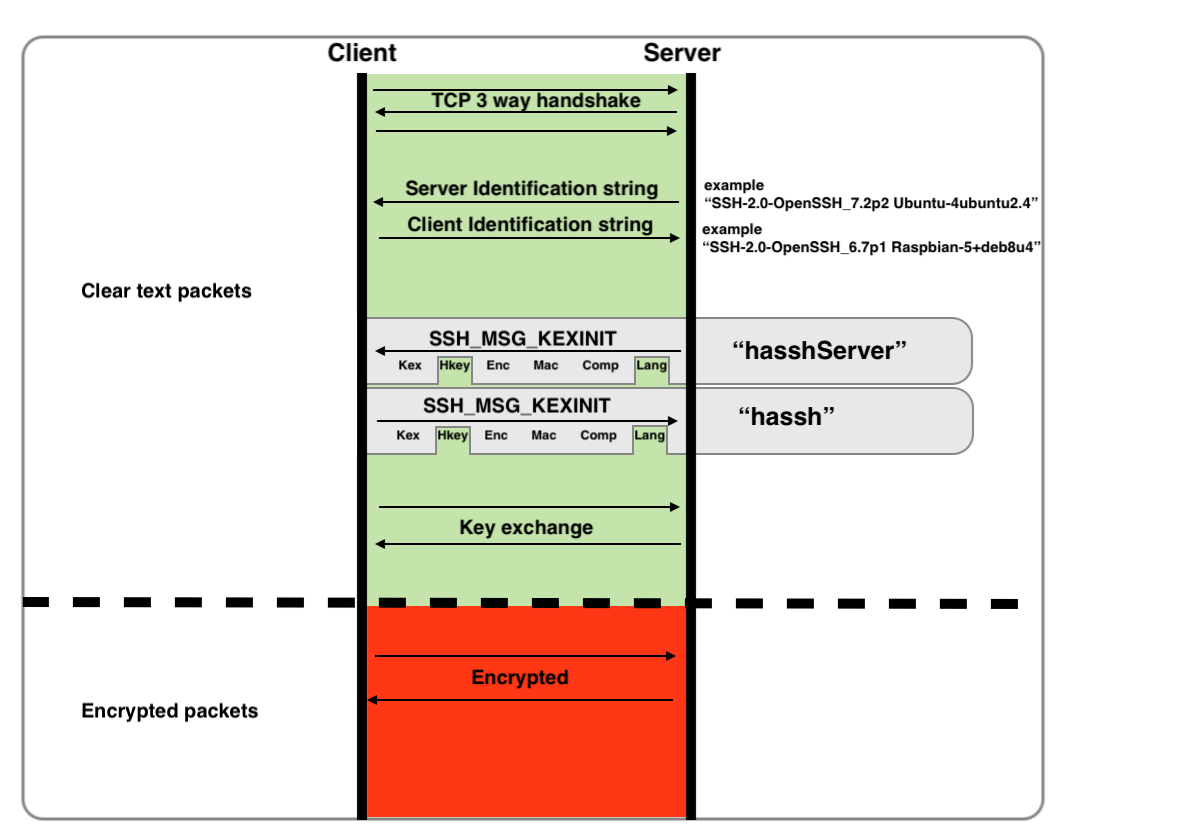
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness

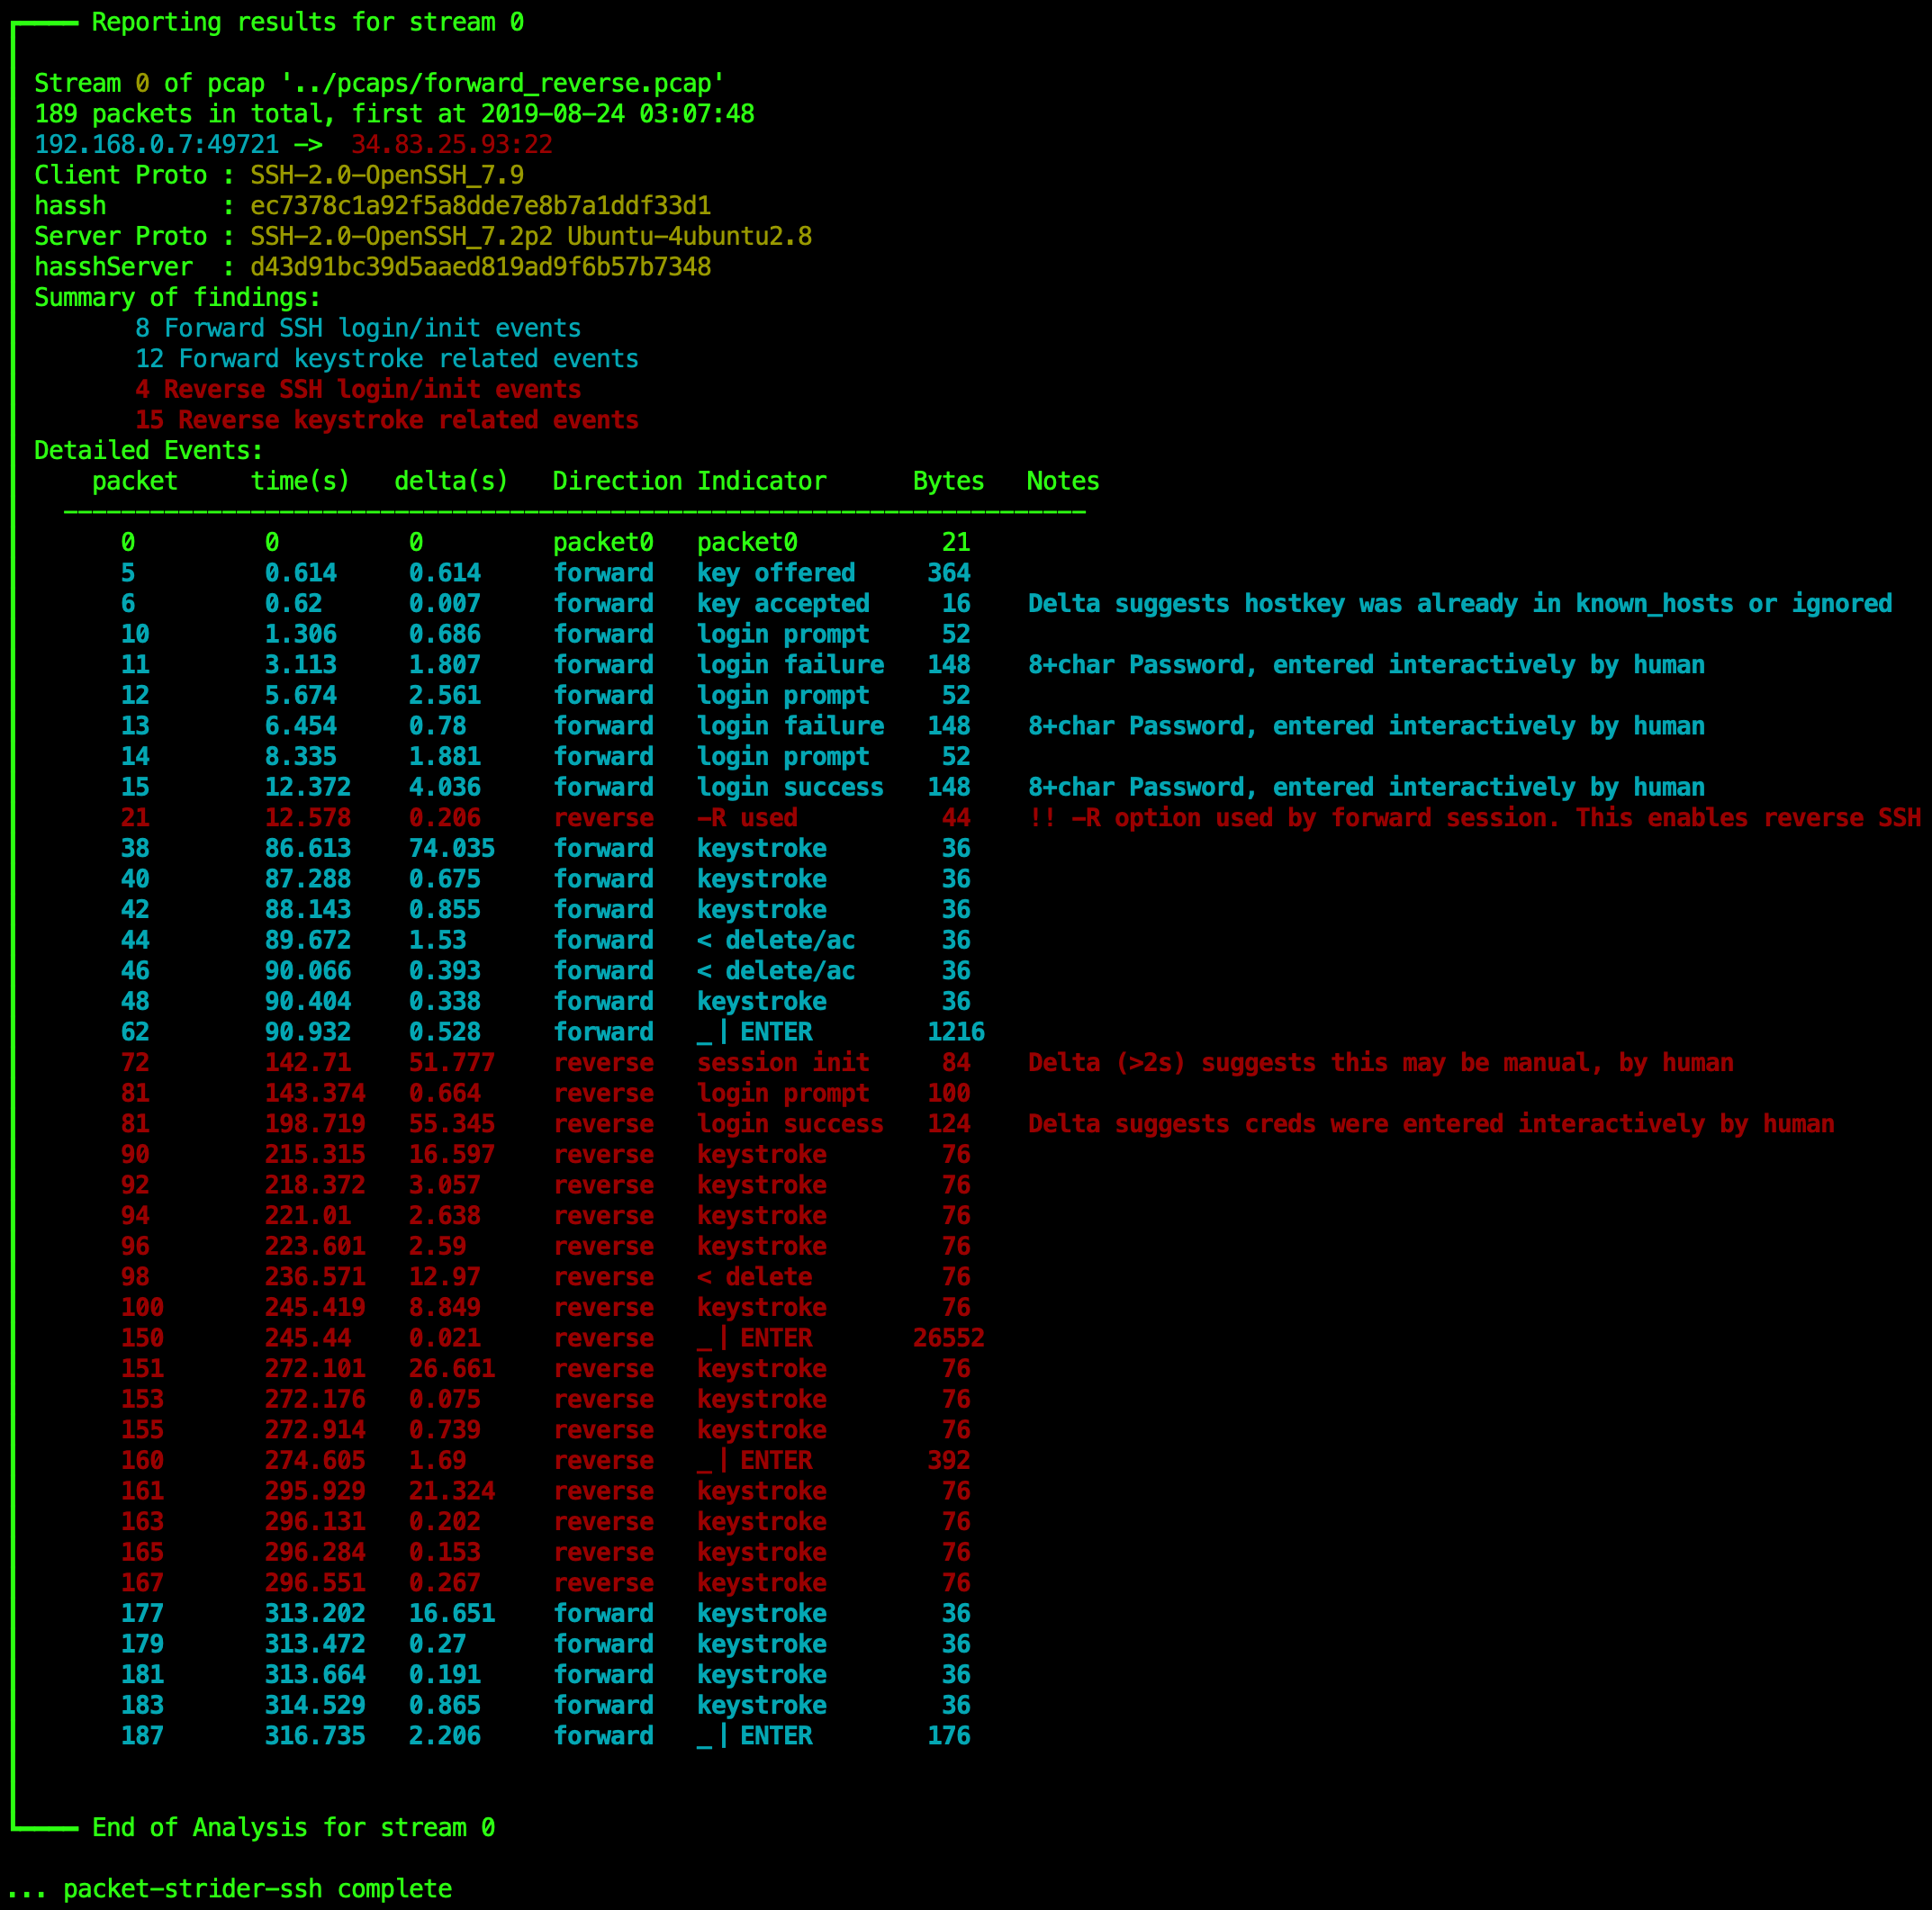
A network packet forensics tool for SSH

Enumerate various traits from Windows processes as an aid to threat hunting

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

Zeek package for tracking long connections to report them before they have completed.

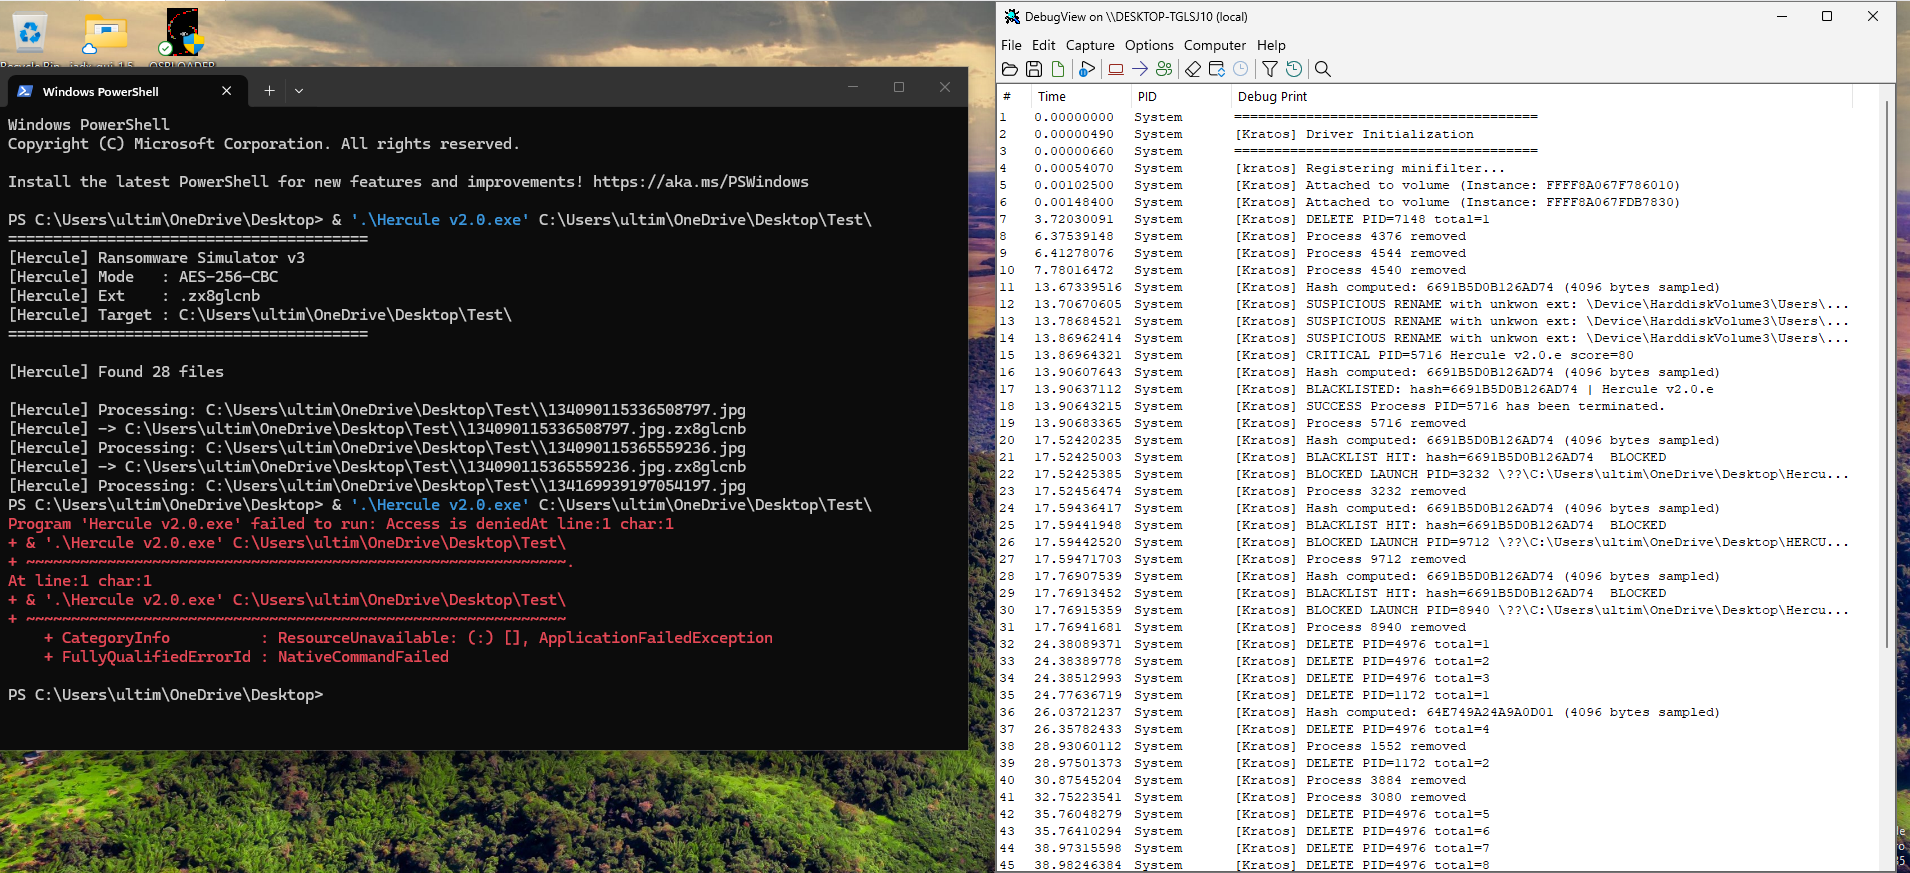
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize

Runs custom filters on Elasticsearch and alerts on matches

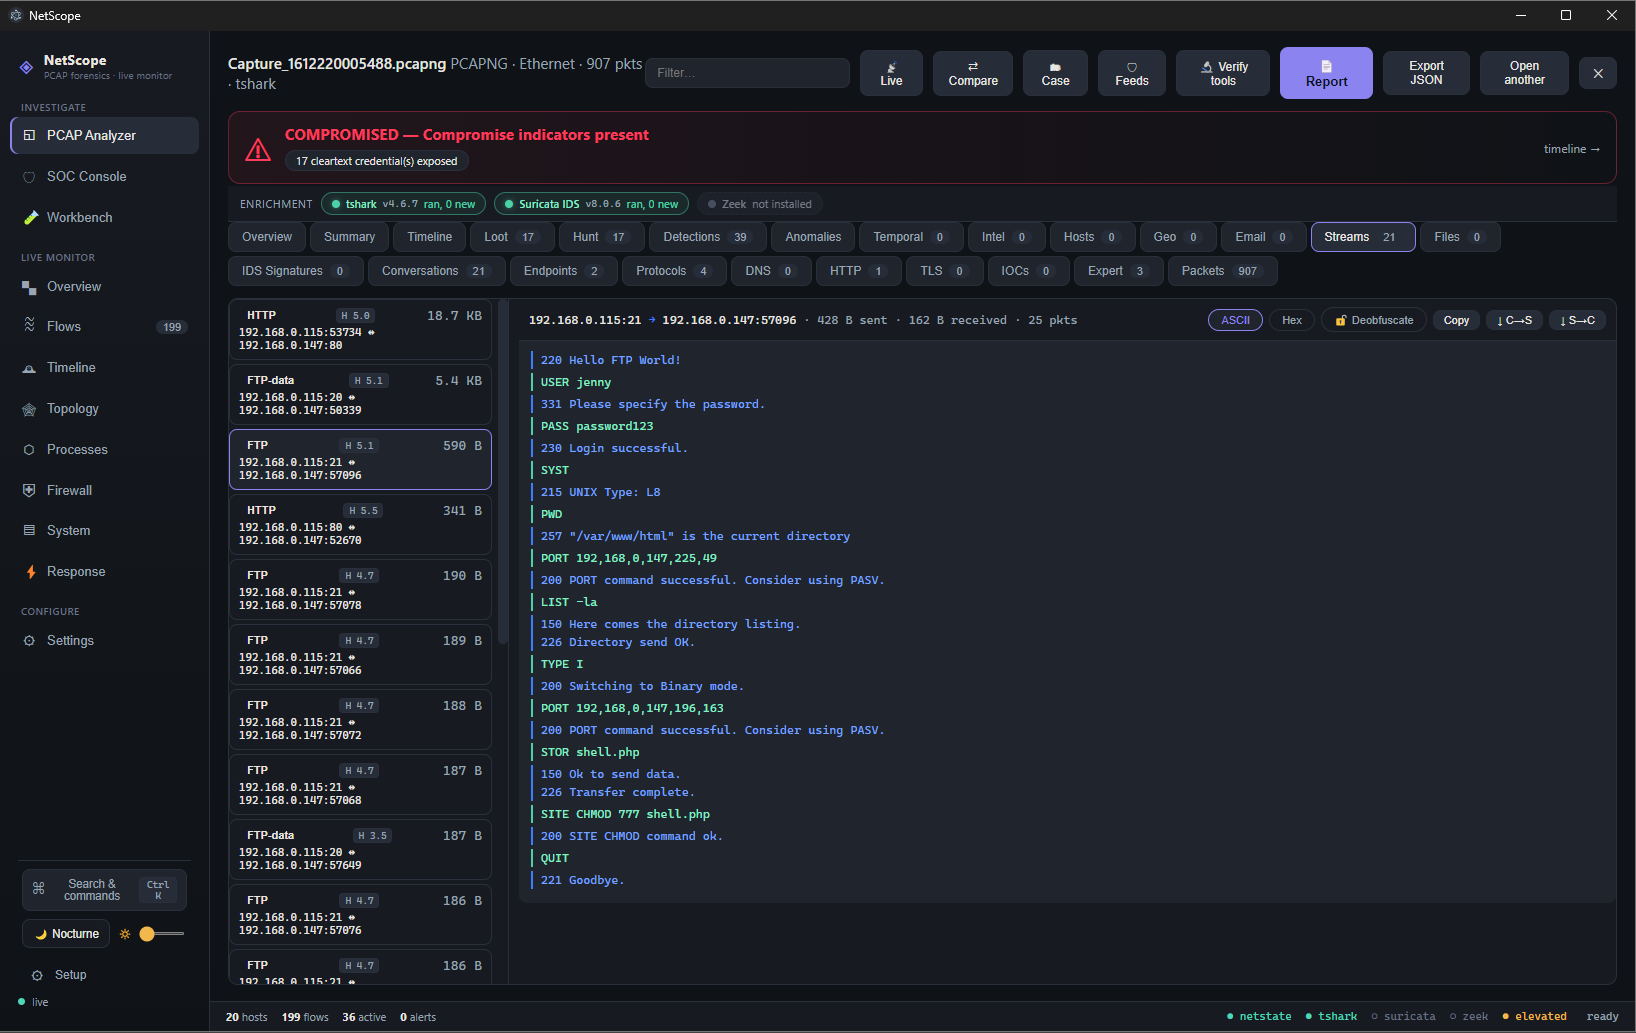
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…