MappedImagesDetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

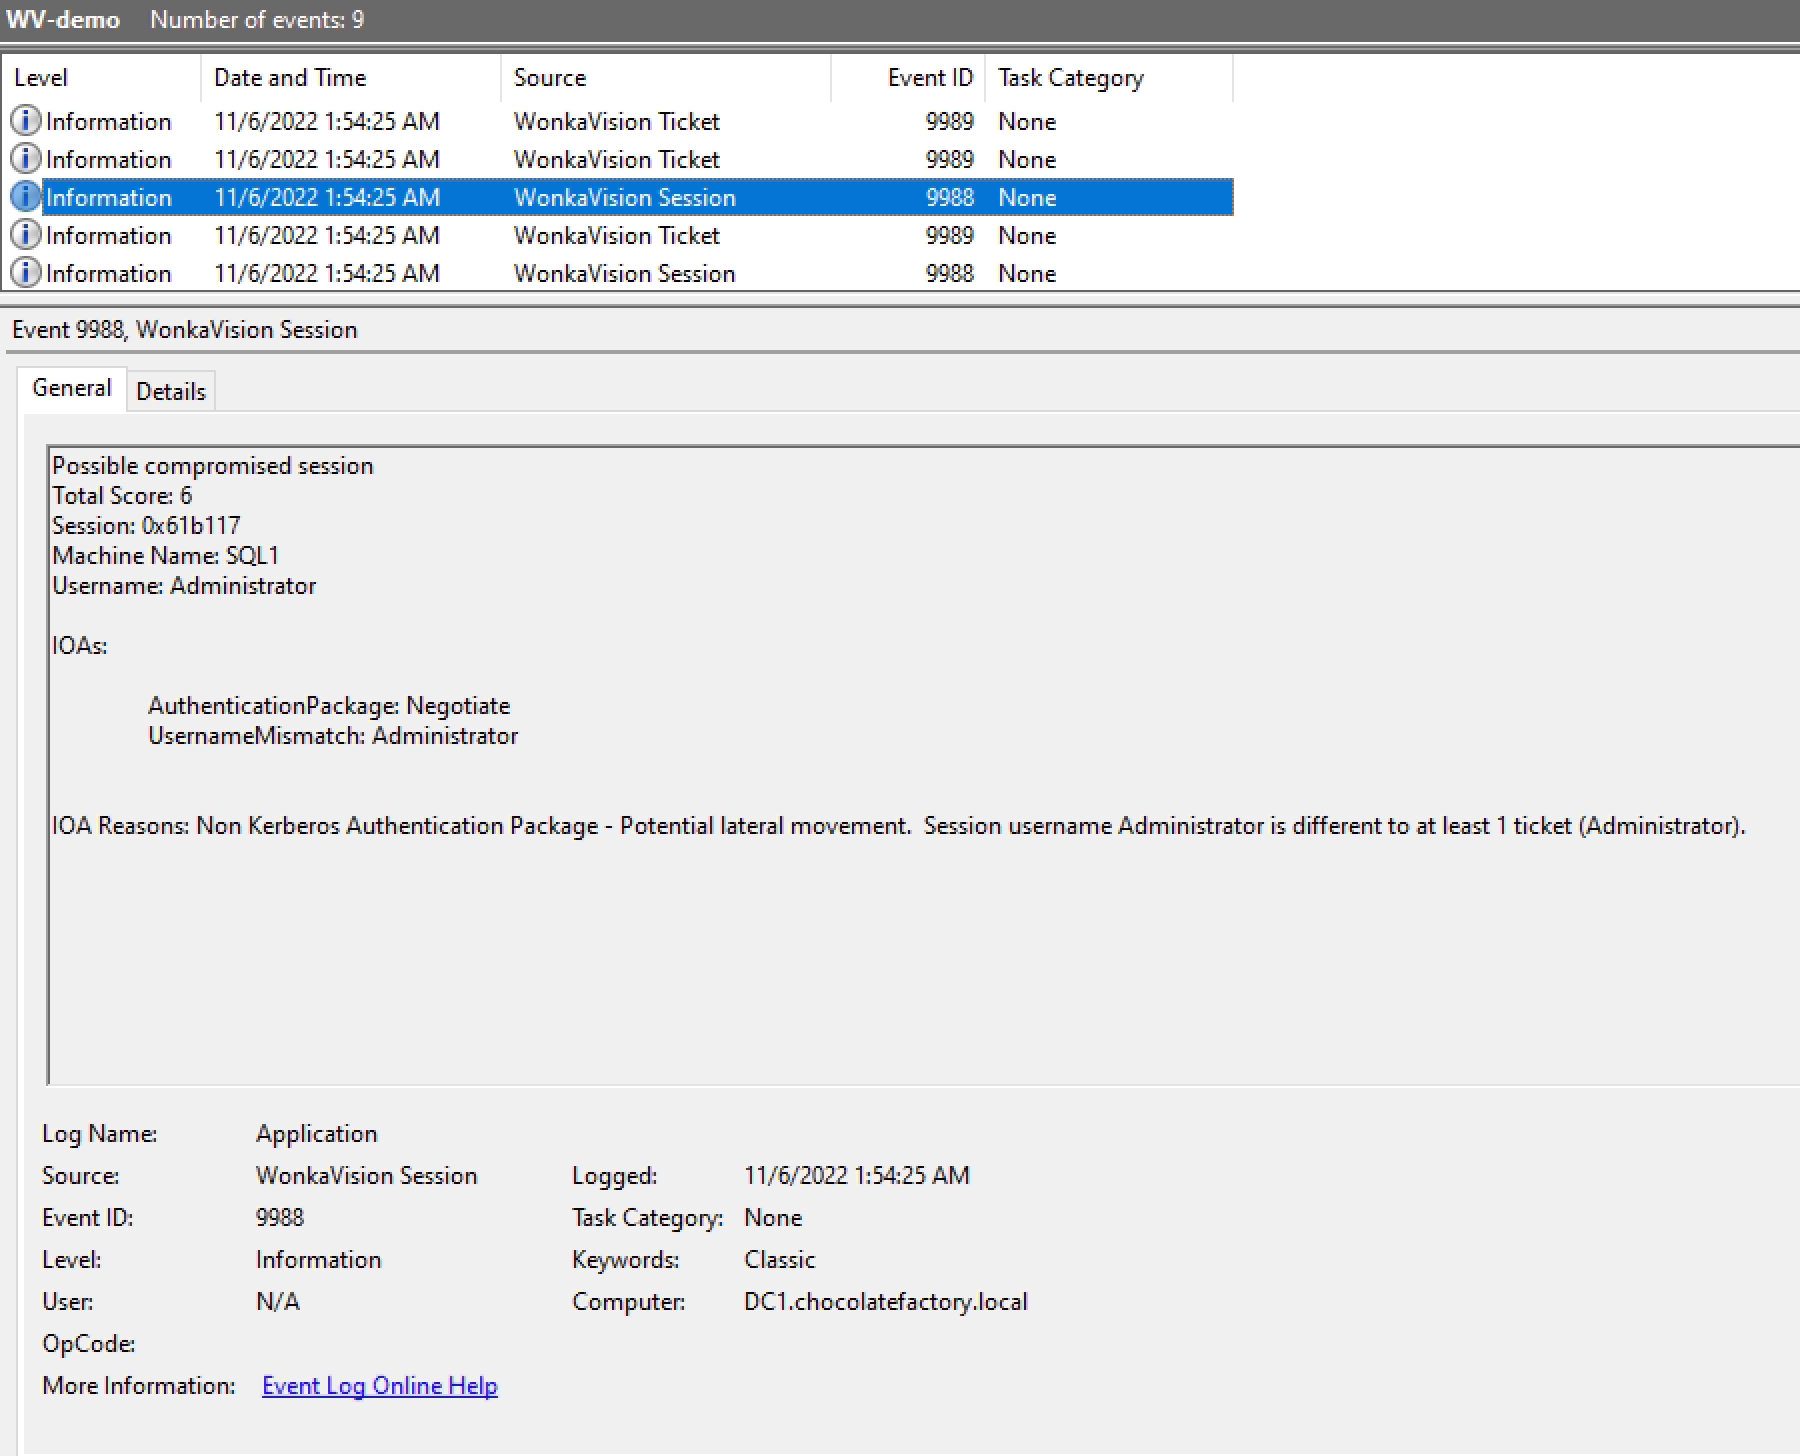
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…

Enumerate various traits from Windows processes as an aid to threat hunting

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

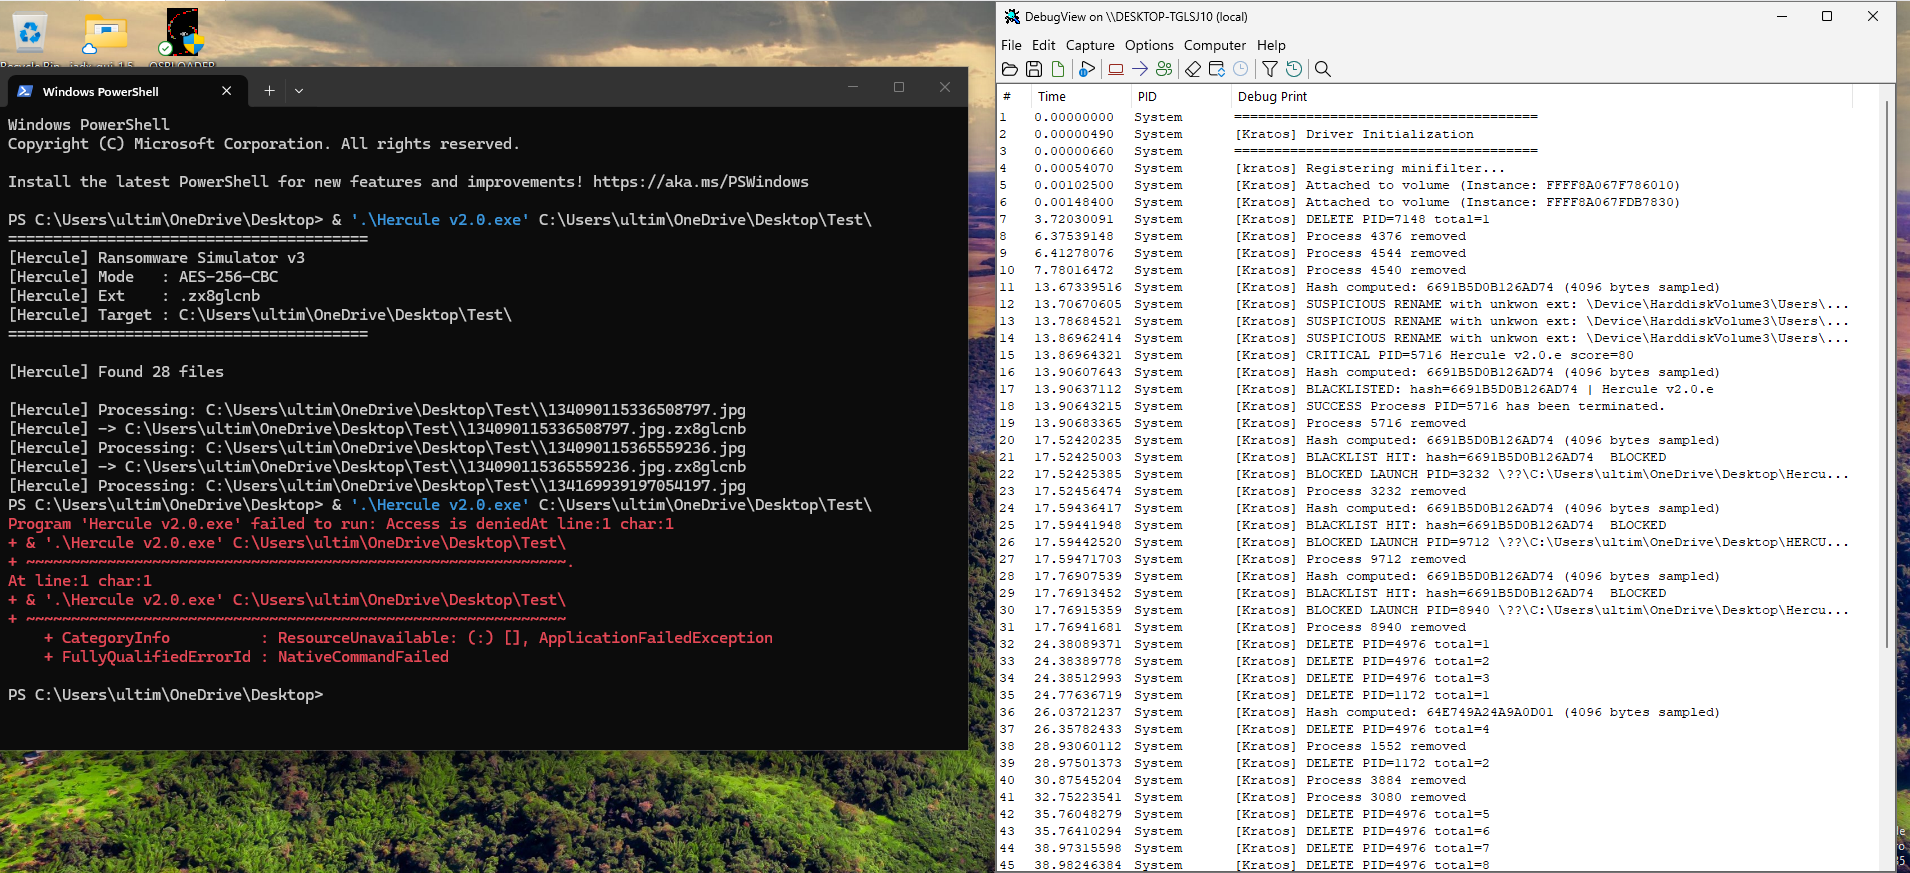
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize

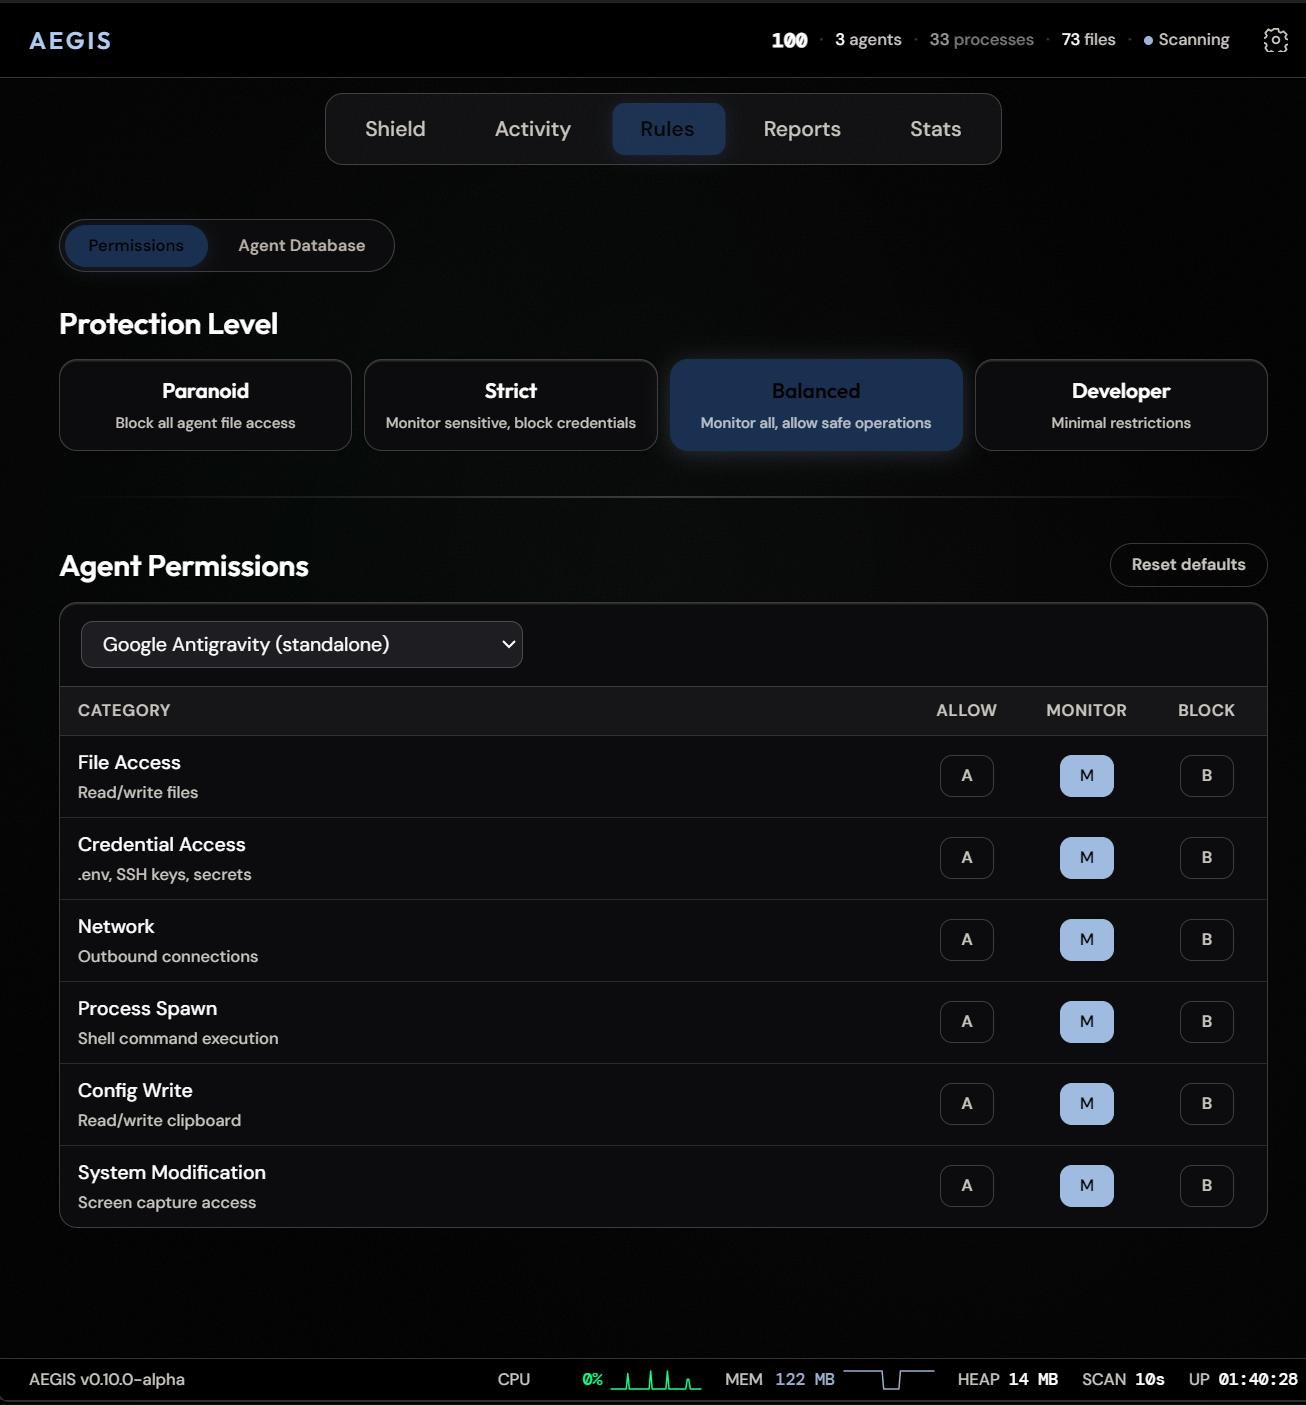
Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…

A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

Default Detections for EDR

PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.

ML-Based behavioral endpoint detection system for Linux machines

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

Zeek detector for QuasarRat