OWASP-GoatDroid-Project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…

*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…

CVE-2016-5195 (Dirty COW) PoC for Android 6.0.1 Marshmallow

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

A python based tool for exploiting and managing Android devices via ADB

Statically unpacking common android banker malware.

Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…

Universal Android root tool based on CVE-2016-5195. Watch this space.

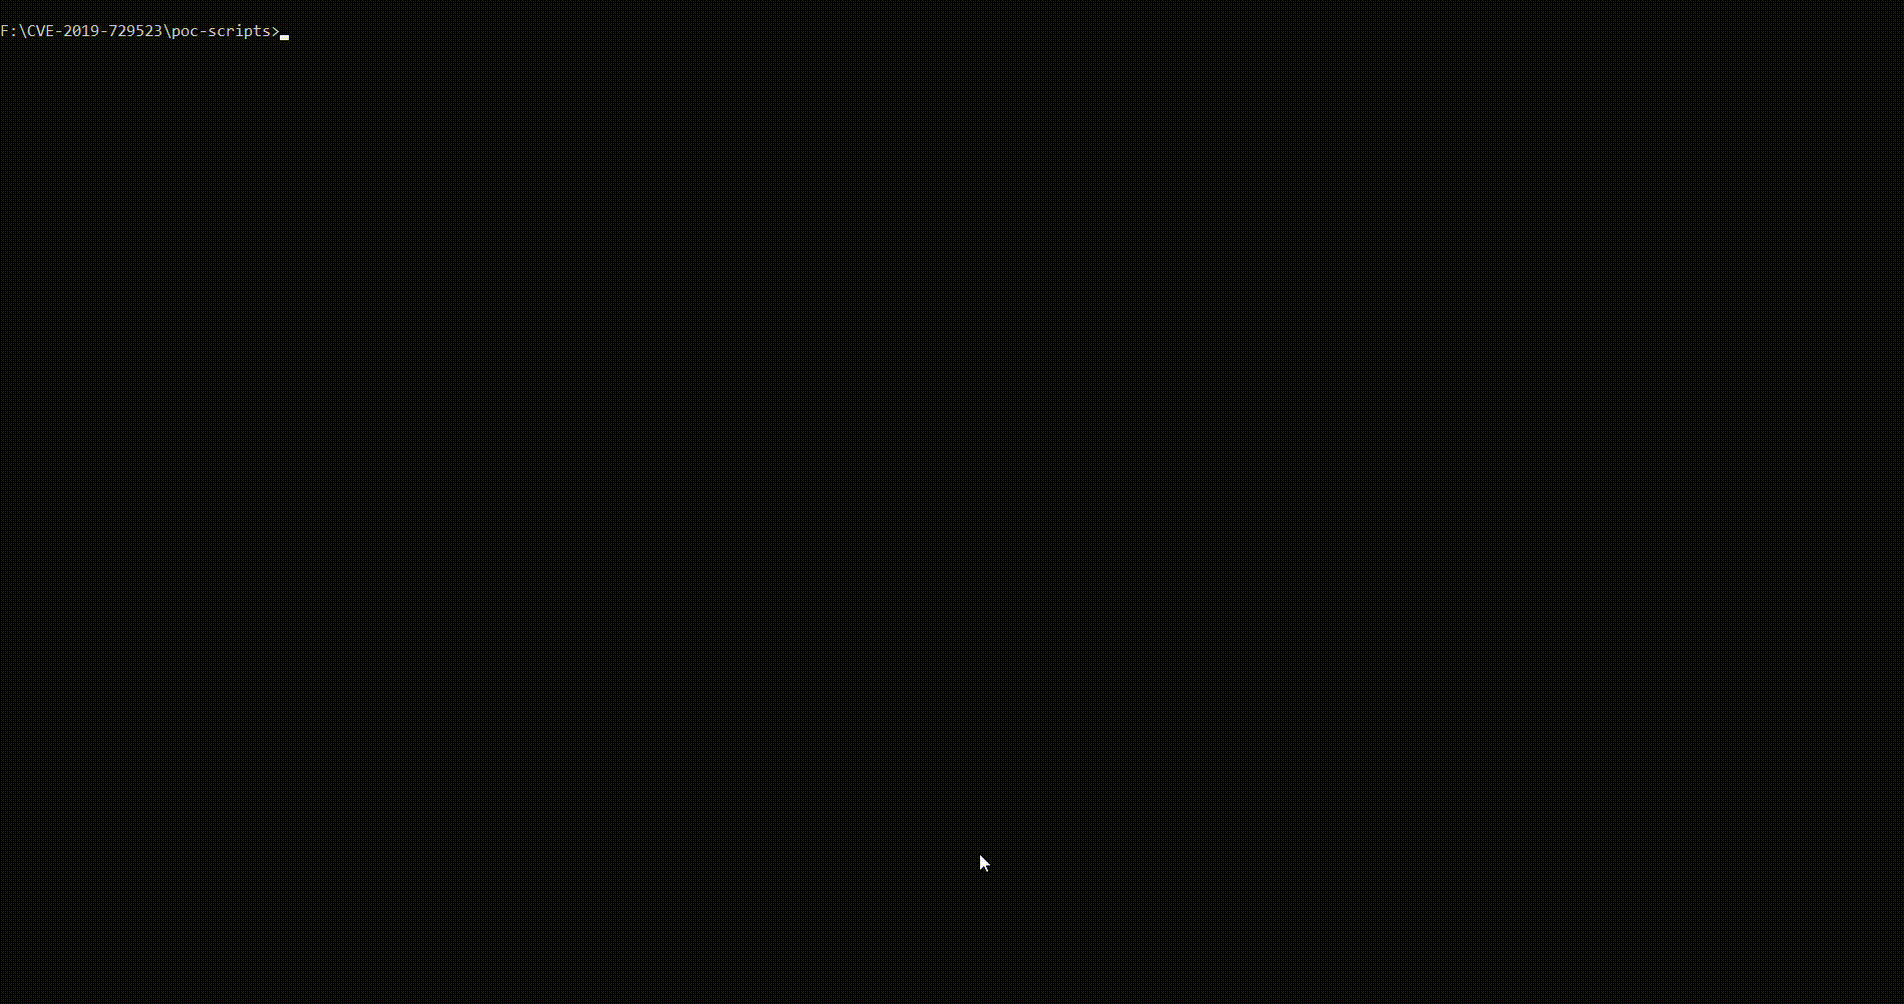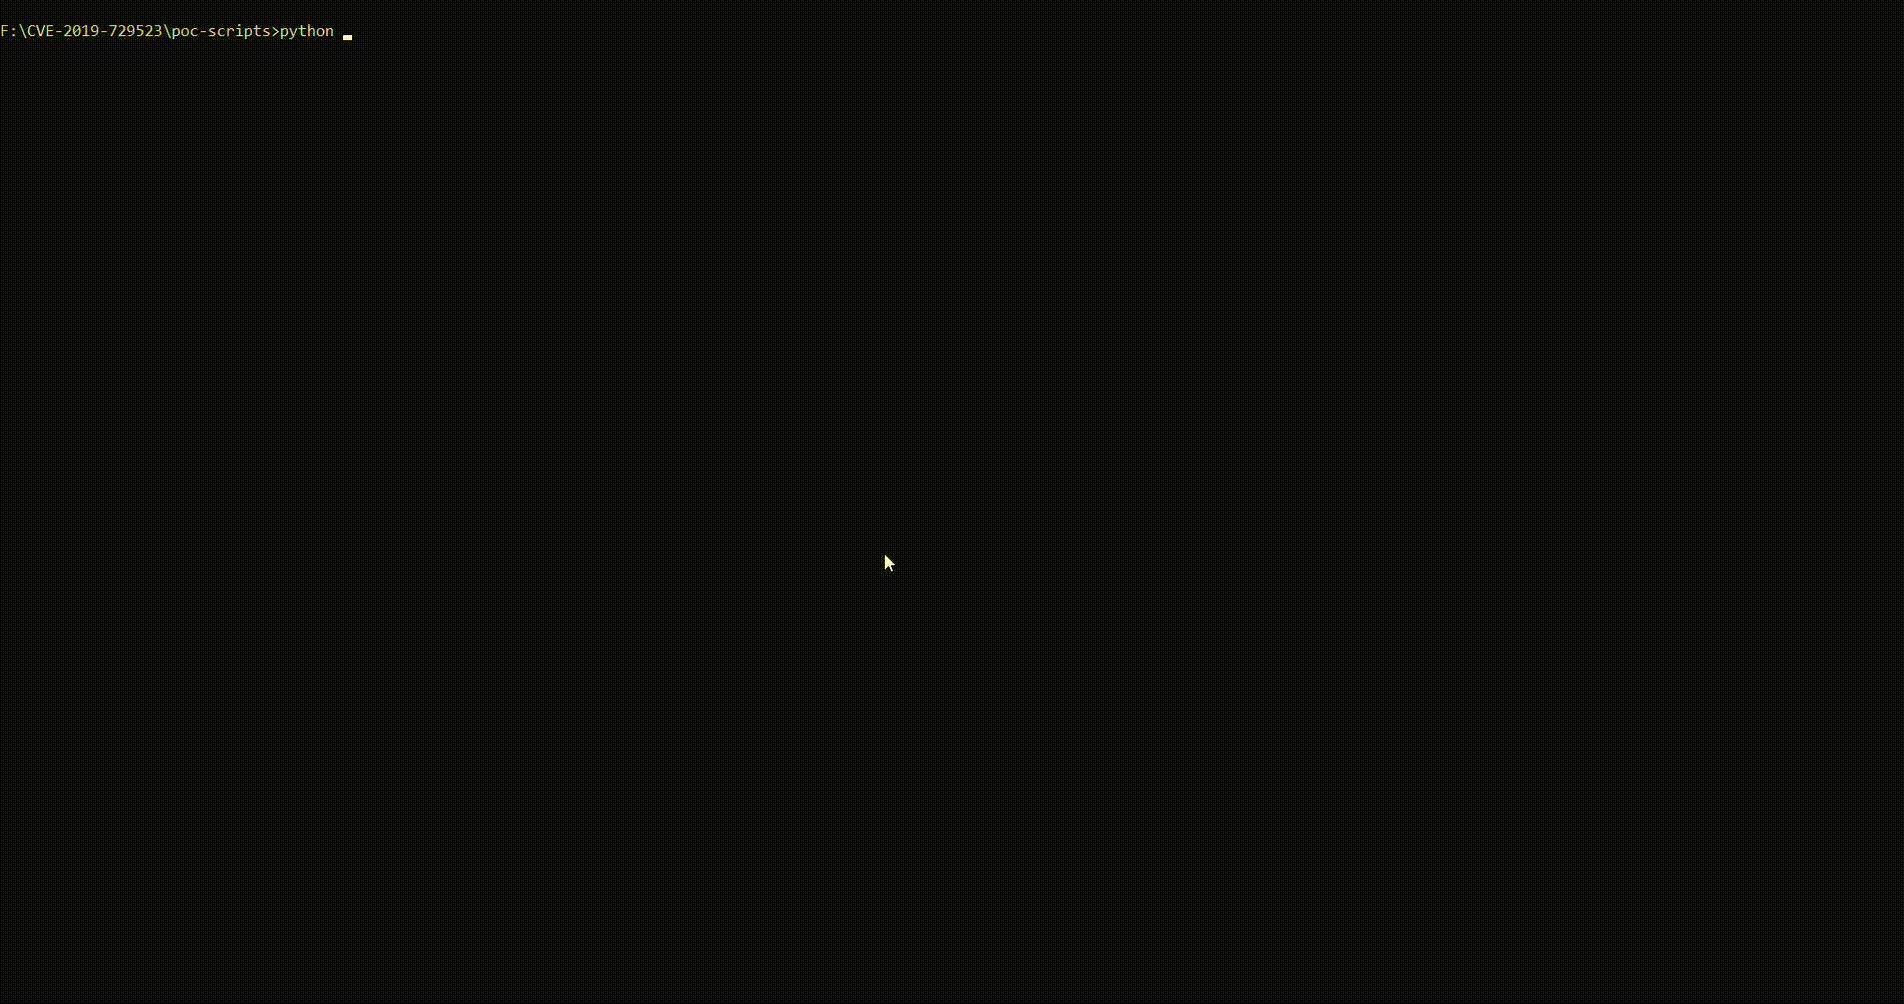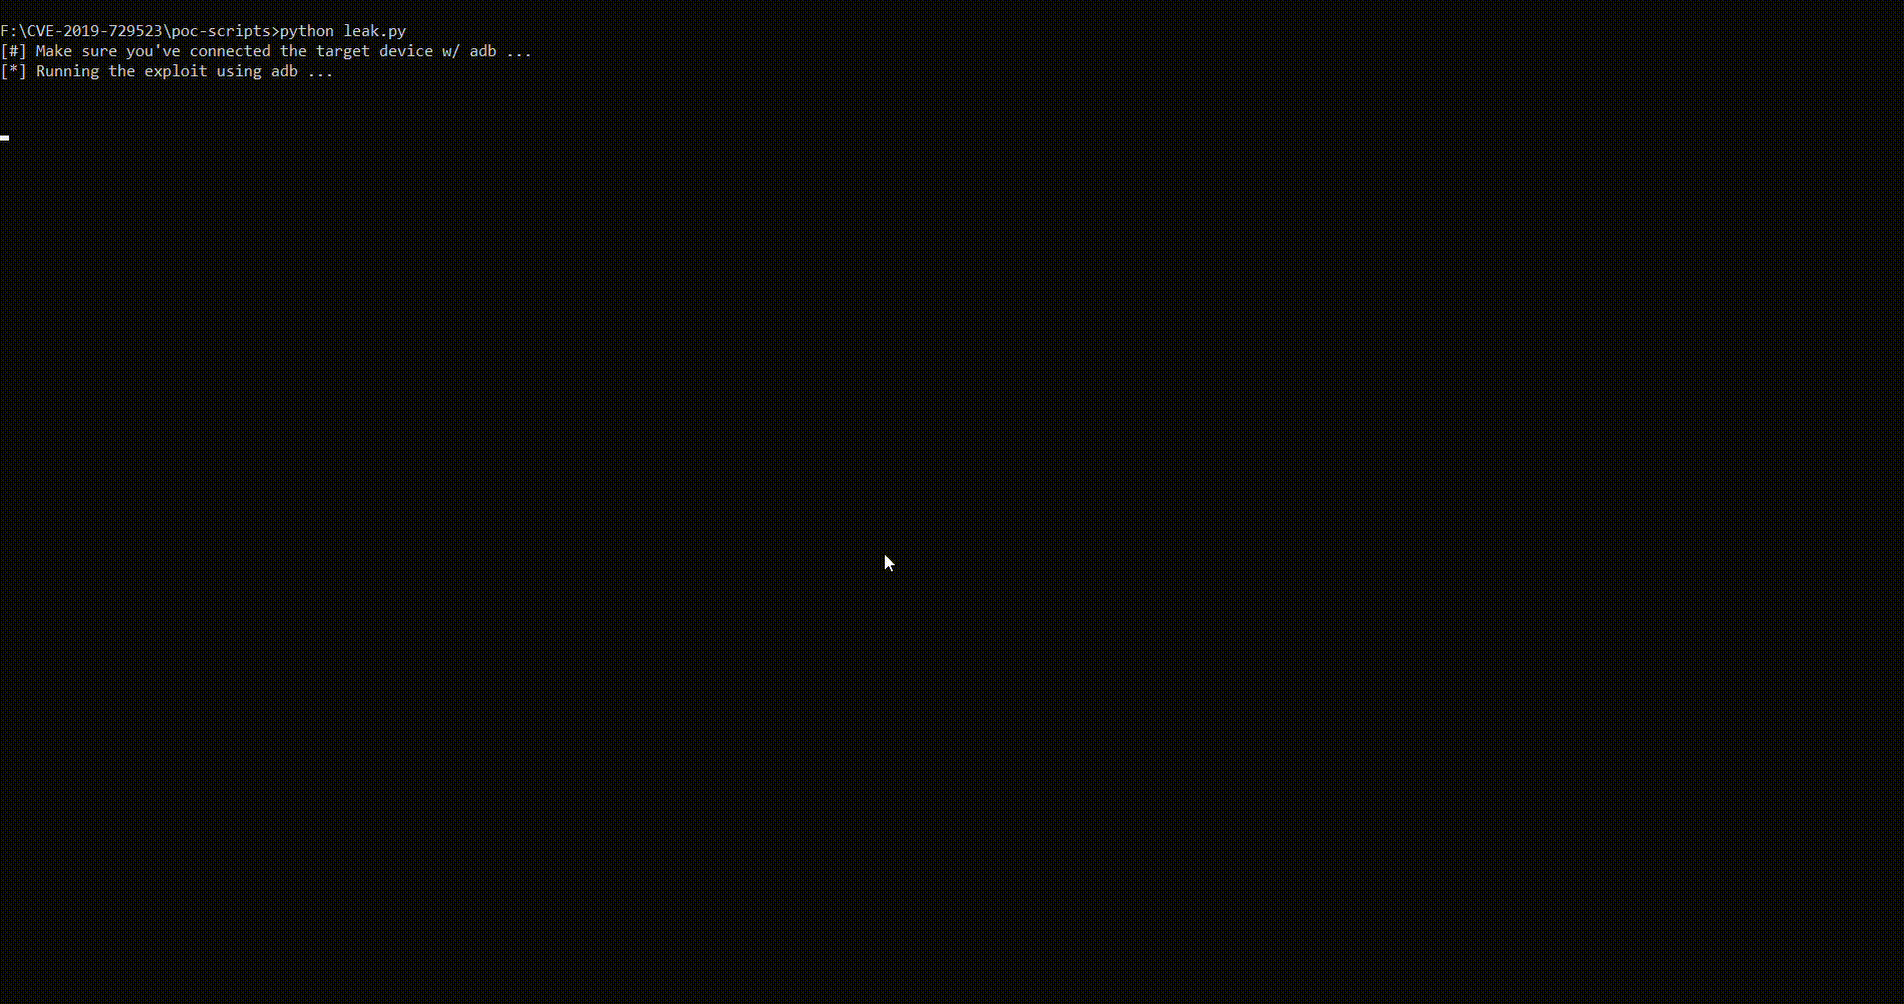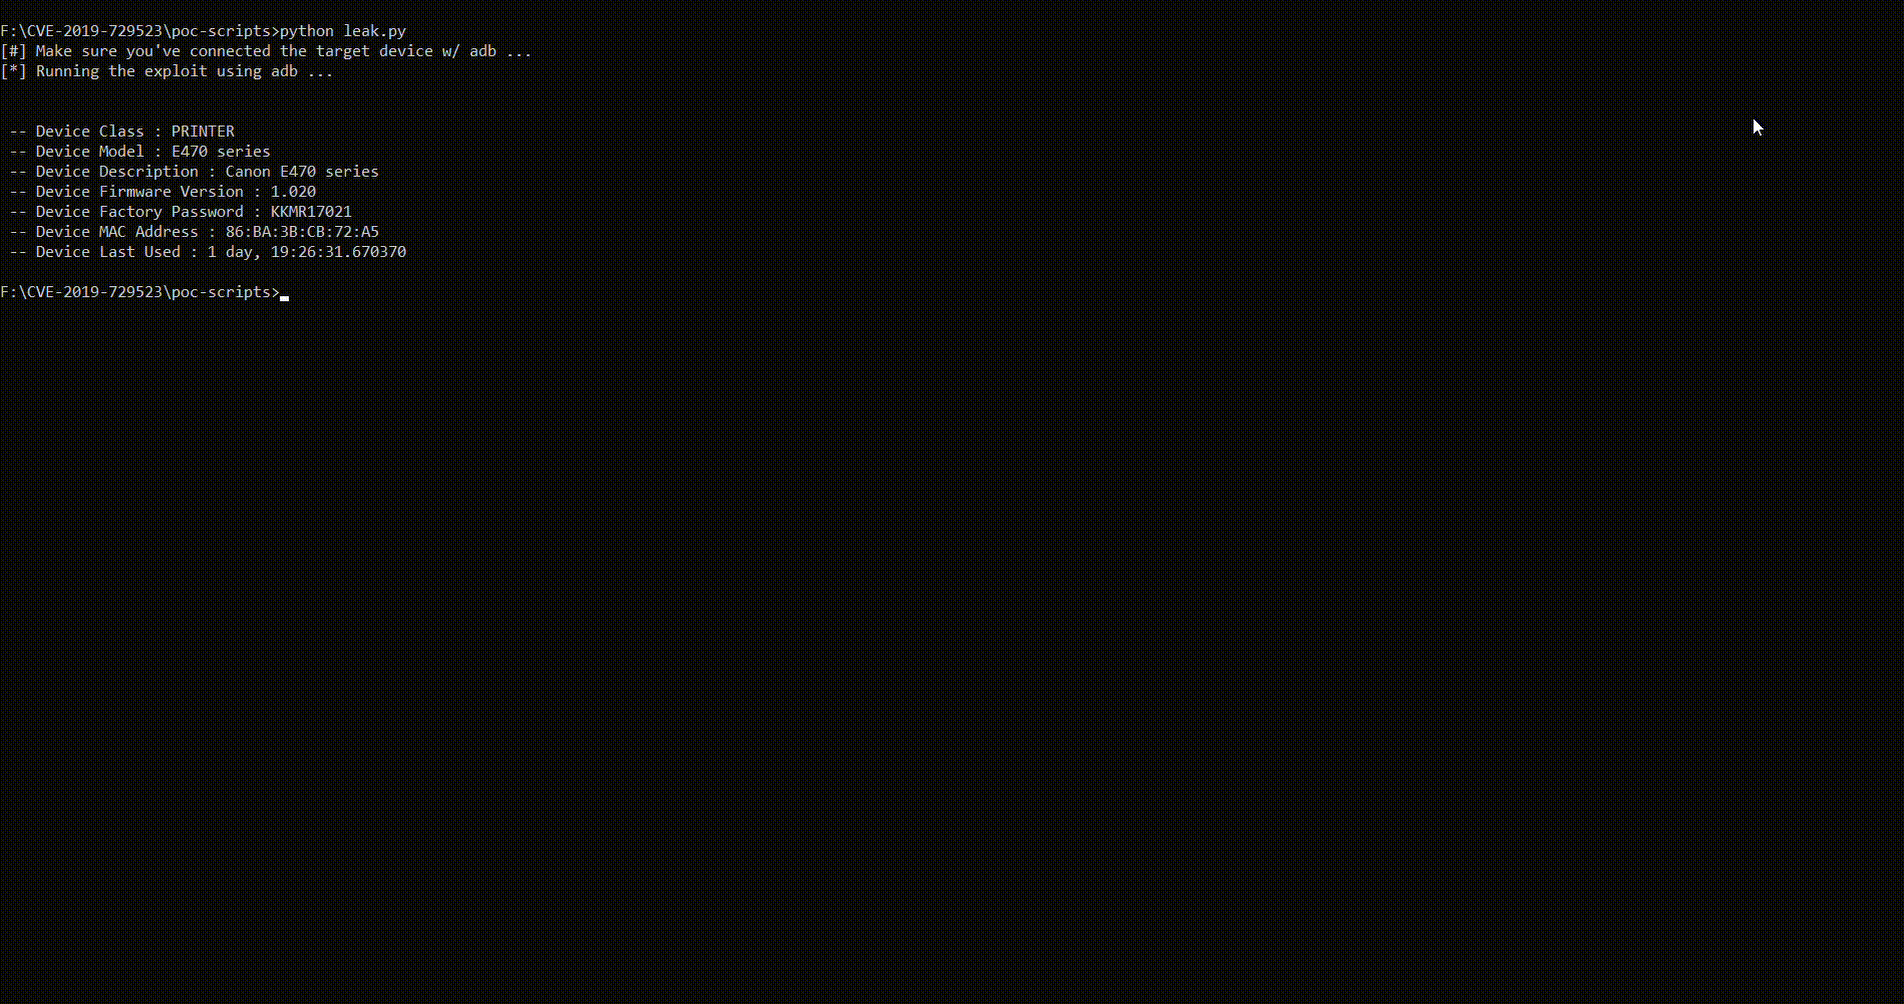
POC for CVE-2019-14339 Canon PRINT 2.5.5

Web-based Source Code Vulnerability Scanner

Root takeover via signature spoofing in KernelSU

Android Tethering Provisioning Check Bypass (CVE-2017-0554)

Use own Phone to DoS Attack without Termux! (Android 5.1+)

Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.

Audits Android TV and Google TV devices over ADB for BadBox, XCPE and Vo1d malware, with a VPN traffic sentinel, IoC blocklists and reversible…

Packs a runtime into built APK, AAB or IPA files to detect root, jailbreak, debuggers, Frida hooks, emulators, VPN/proxy interception and repackaging…

Make your own app expensive to reverse. A build-time audit, harden and verify harness for native binaries and mobile apps, built to counter…

VaultZero: offline, zero-knowledge password manager and encrypted vault for Android. AES-256-GCM, BIP-39 128-bit recovery kits, hardware biometrics,…

Per-boot KernelSU late-load via CVE-2026-64560 — OnePlus Pad 3 (OPD2415, SM8750, kernel 6.6.118-android15-8, 4K, locked bootloader): payload port,…