 chrisdcode1/vault-zero
VaultZero: offline, zero-knowledge password manager and encrypted vault for Android. AES-256-GCM, BIP-39 128-bit recovery kits, hardware biometrics, no network permission, no telemetry.


Offline, zero-knowledge password manager and encrypted vault for Android.
AES-256-GCM · PBKDF2-HMAC-SHA256 (600,000) · BIP-39 128-bit recovery kits · hardware biometrics · no network permission · no accounts · no telemetry
🌐 chrisdesarden.github.io/Vault-Zero · 📦 GitHub Releases · 📚 Documentation



VaultZero is a local-first Android vault for passwords, 2FA codes, payment cards, API keys,
crypto wallets/seed phrases, secure notes and identity documents. It is built with Kotlin and
Jetpack Compose and is deliberately incapable of connecting to the internet: the app declares
no INTERNET permission and contains no networking code.
Everything is encrypted on the device with a random 256-bit vault key, wrapped by your master password and a 12-word recovery phrase. Backups are encrypted files written through Android's system file picker — there is no account, cloud sync, analytics or remote service.
Status: production release v1.3.1 (
versionCode 5). Self-tested and pentested; an independent audit is still recommended before relying on it for high-risk secrets.
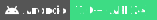
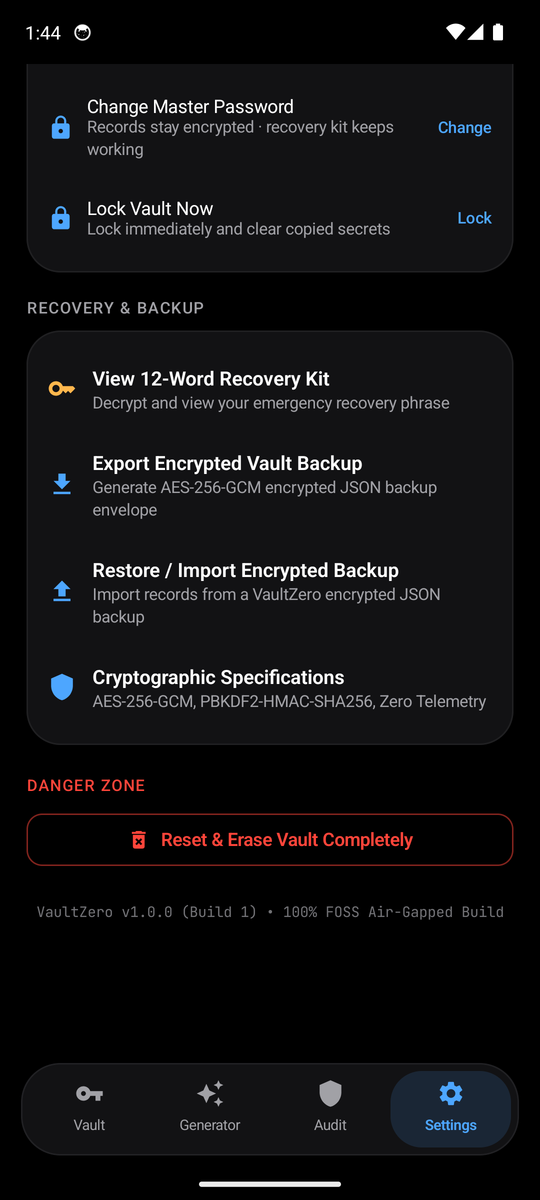
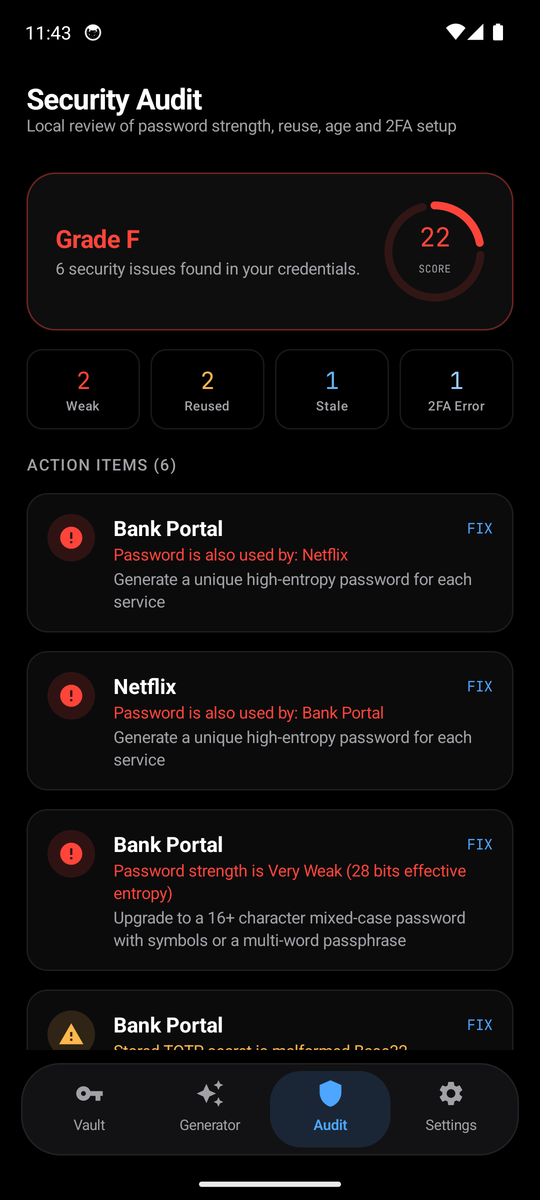
| Vault (dark) | Light theme | 2FA dashboard |
|---|---|---|
|  | 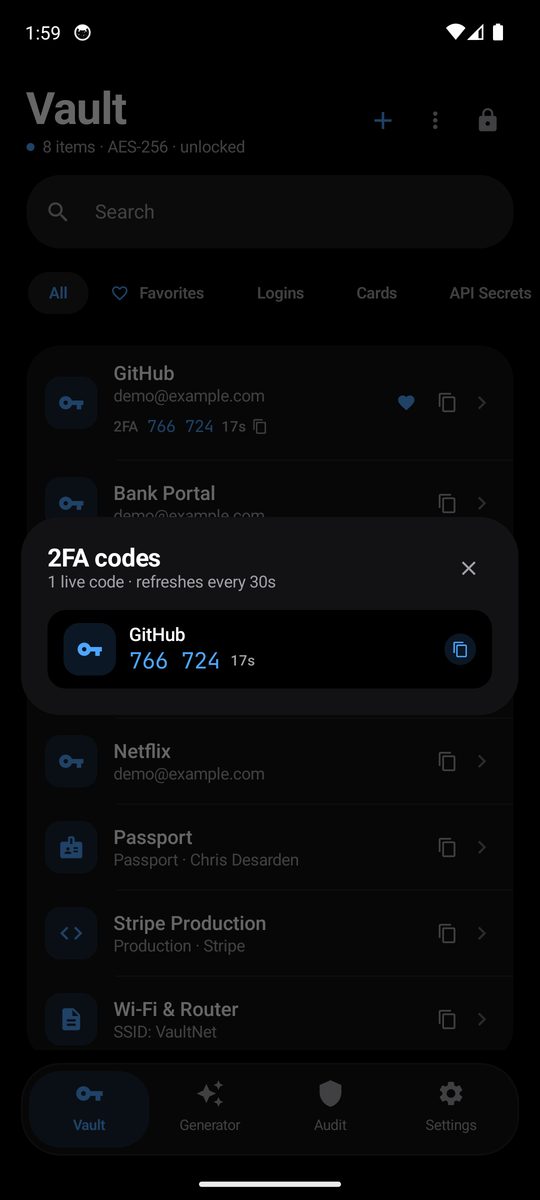 |
| Settings | Generator | Audit |
 |  |  |
More in docs/SCREENSHOTS.md.
[ENCRYPTED] placeholders.type:login, tag:work, is:fav, and audit-backed filters is:weak, is:reused, is:stale, is:no2fa, is:clean.VaultZero_Record_v2:<id>:<type> AAD.BiometricPrompt.CryptoObject — per-use authentication, invalidated when biometrics are re-enrolled. The prompt auto-appears on app open when enabled.FLAG_SECURE, Recent-Apps preview blocked.#FAFAFA grounds, single accent blue, squircle containers, floating pill navigation, large collapsing title.| Area | Implementation |
|---|---|
| Records | AES-256-GCM, random per-record IV, 128-bit tag, AAD bound to record id + type |
| Key hierarchy | Random 256-bit VMK wraps records; VMK wrapped by password KEK and recovery-phrase KEK |
| Password KDF | PBKDF2-HMAC-SHA256, 600,000 iterations, 128-bit random salt |
| Recovery | BIP-39 12-word phrase (128-bit entropy) with unique words; legacy v1.x phrases still accepted; encrypted under the VMK at rest; rotatable in Settings |
| Biometrics | AES-256-GCM Keystore key, AUTH_BIOMETRIC_STRONG, per-use auth (CryptoObject), StrongBox→TEE, invalidated by biometric enrolment changes |
| Backups | AES-256-GCM envelope, redacted metadata, 8 MiB import cap, phrase/password restore |
| Network | No INTERNET/ACCESS_NETWORK_STATE permission, no networking libraries |
| Screen capture | FLAG_SECURE, recents screenshot disabled on API 33+ |
| At rest | SQLite titles/categories/tags redacted; prefs contain only wrapped keys, salts, verifiers |
| Offline | No accounts, cloud, analytics, crash reporting, ads or trackers |