
IATelligence
 fr0gger/iatelligence
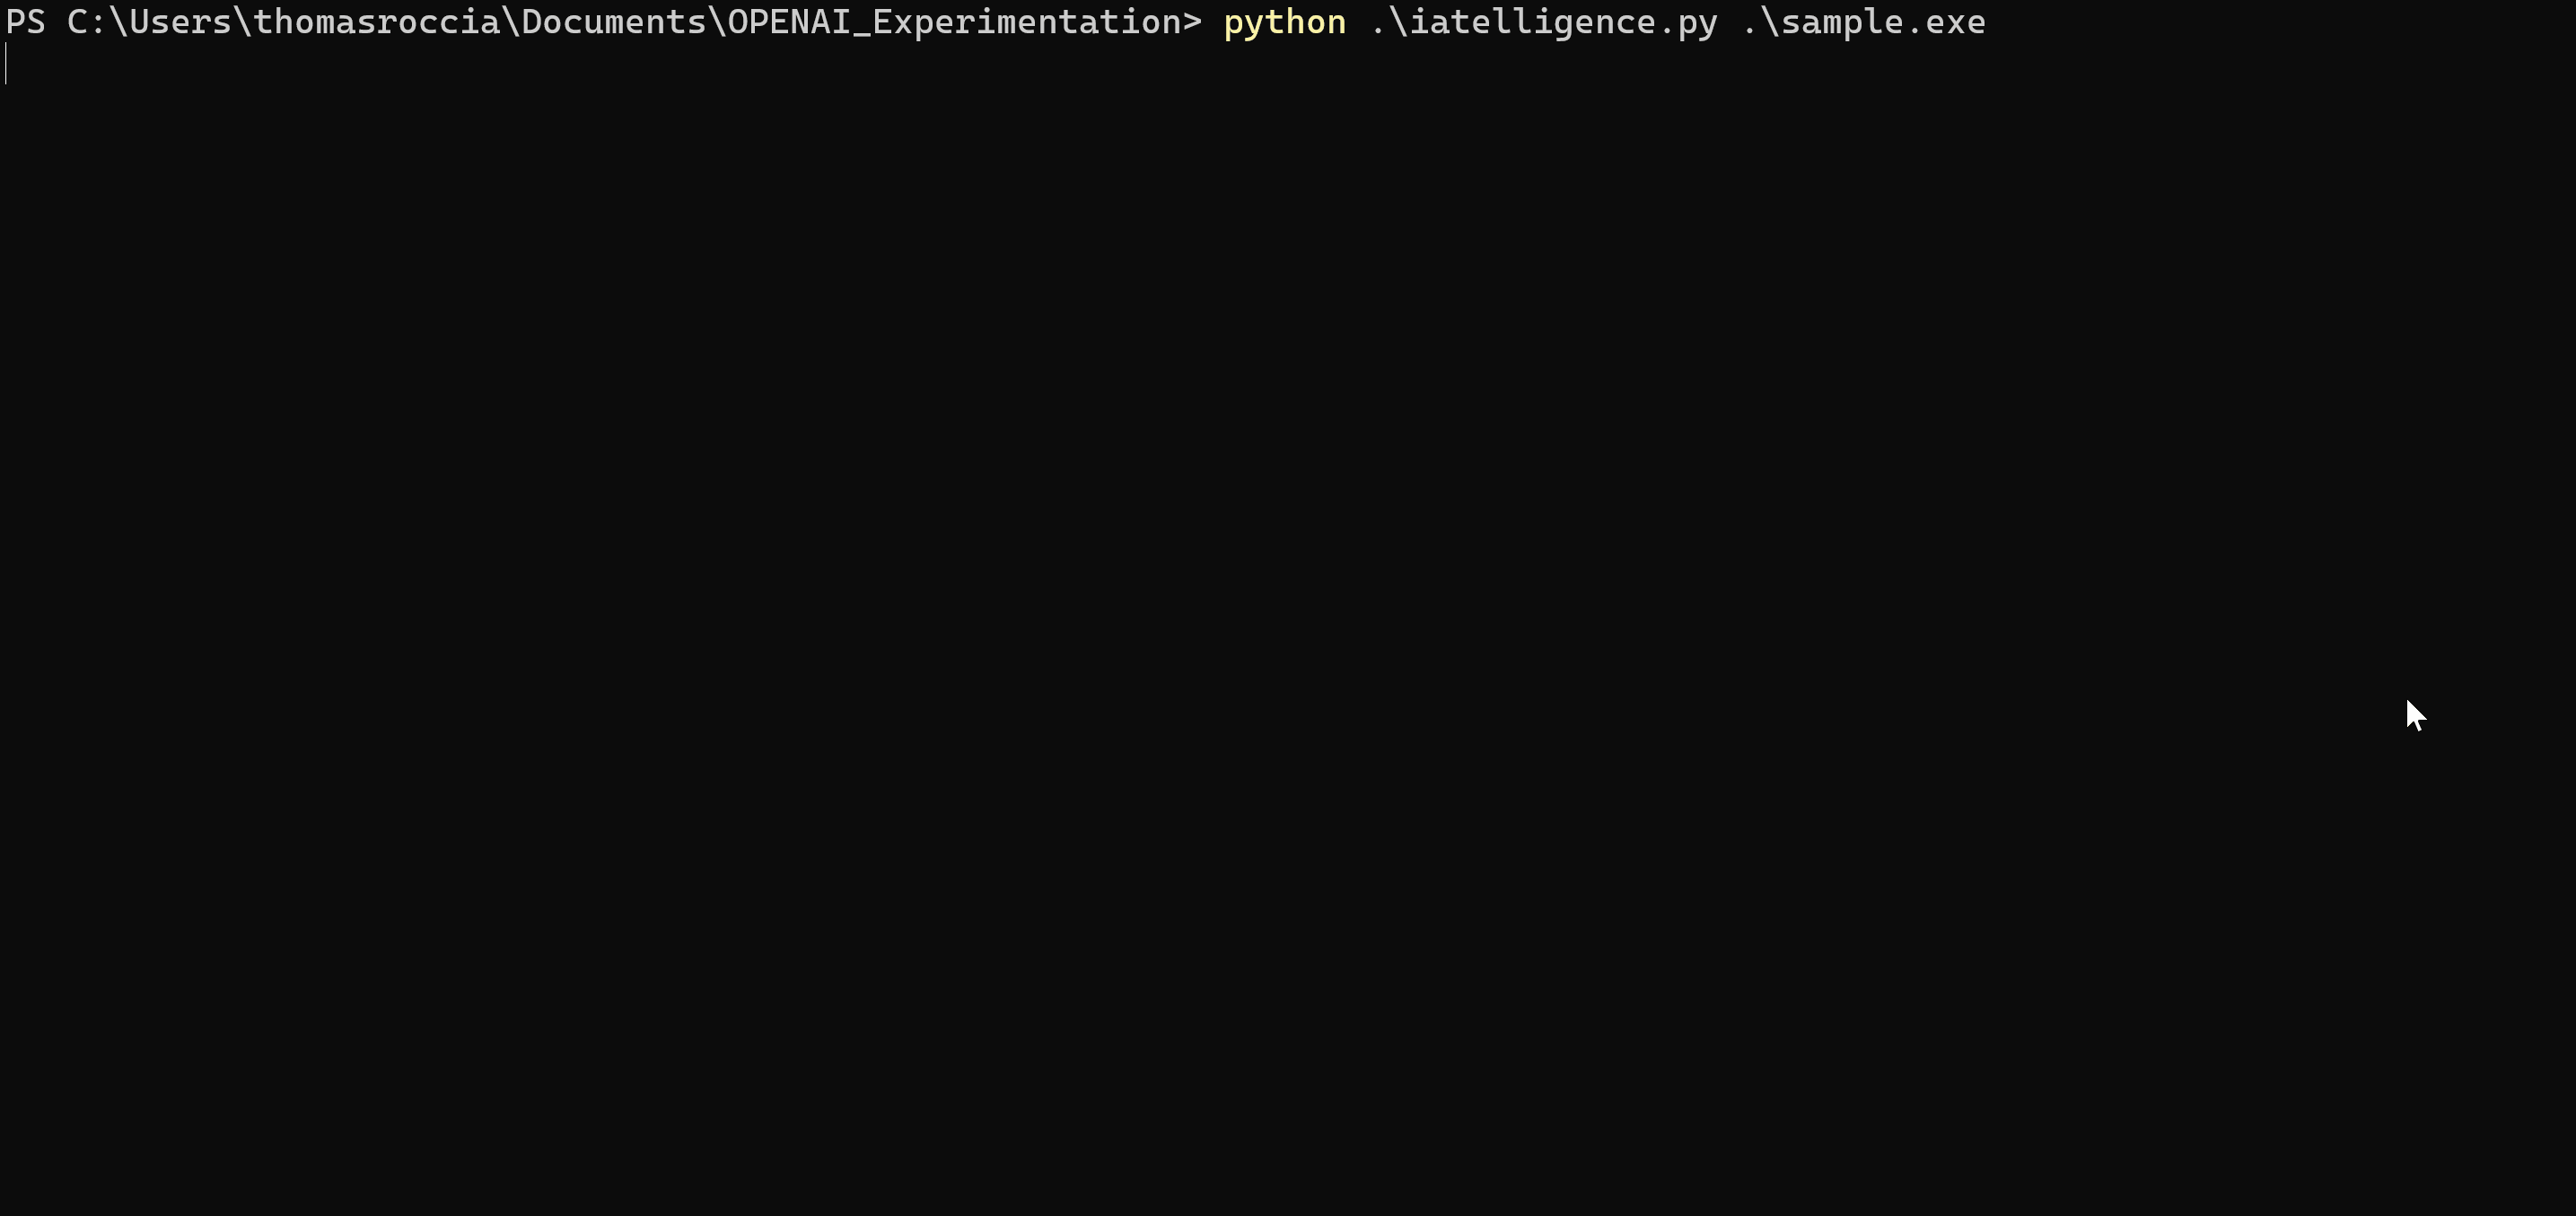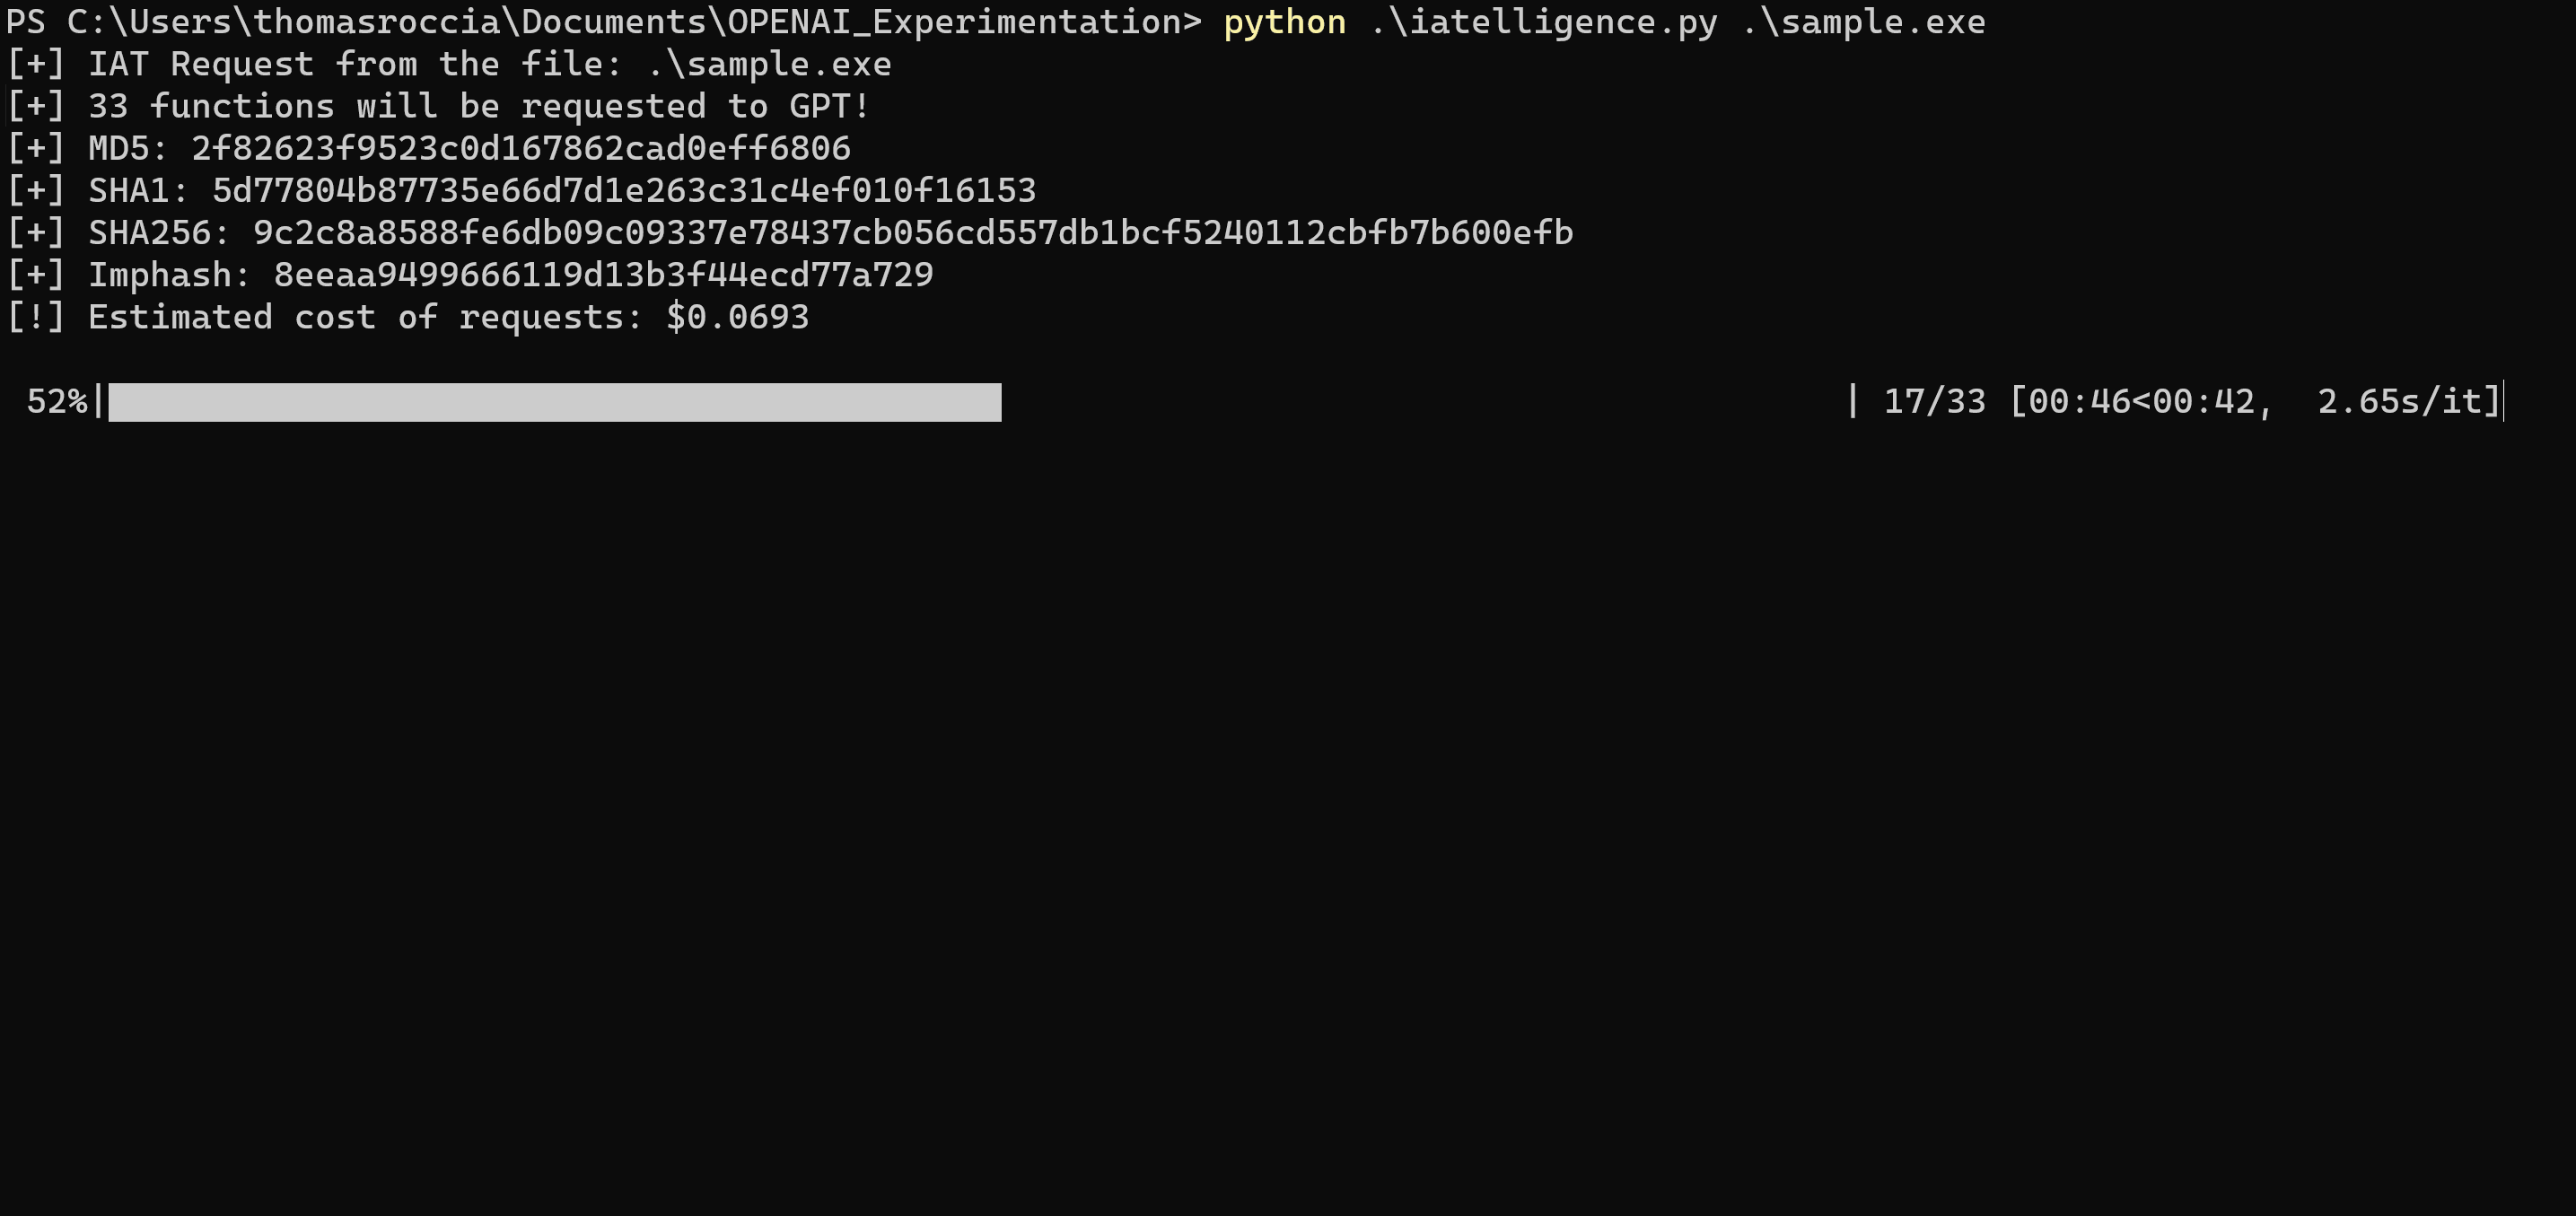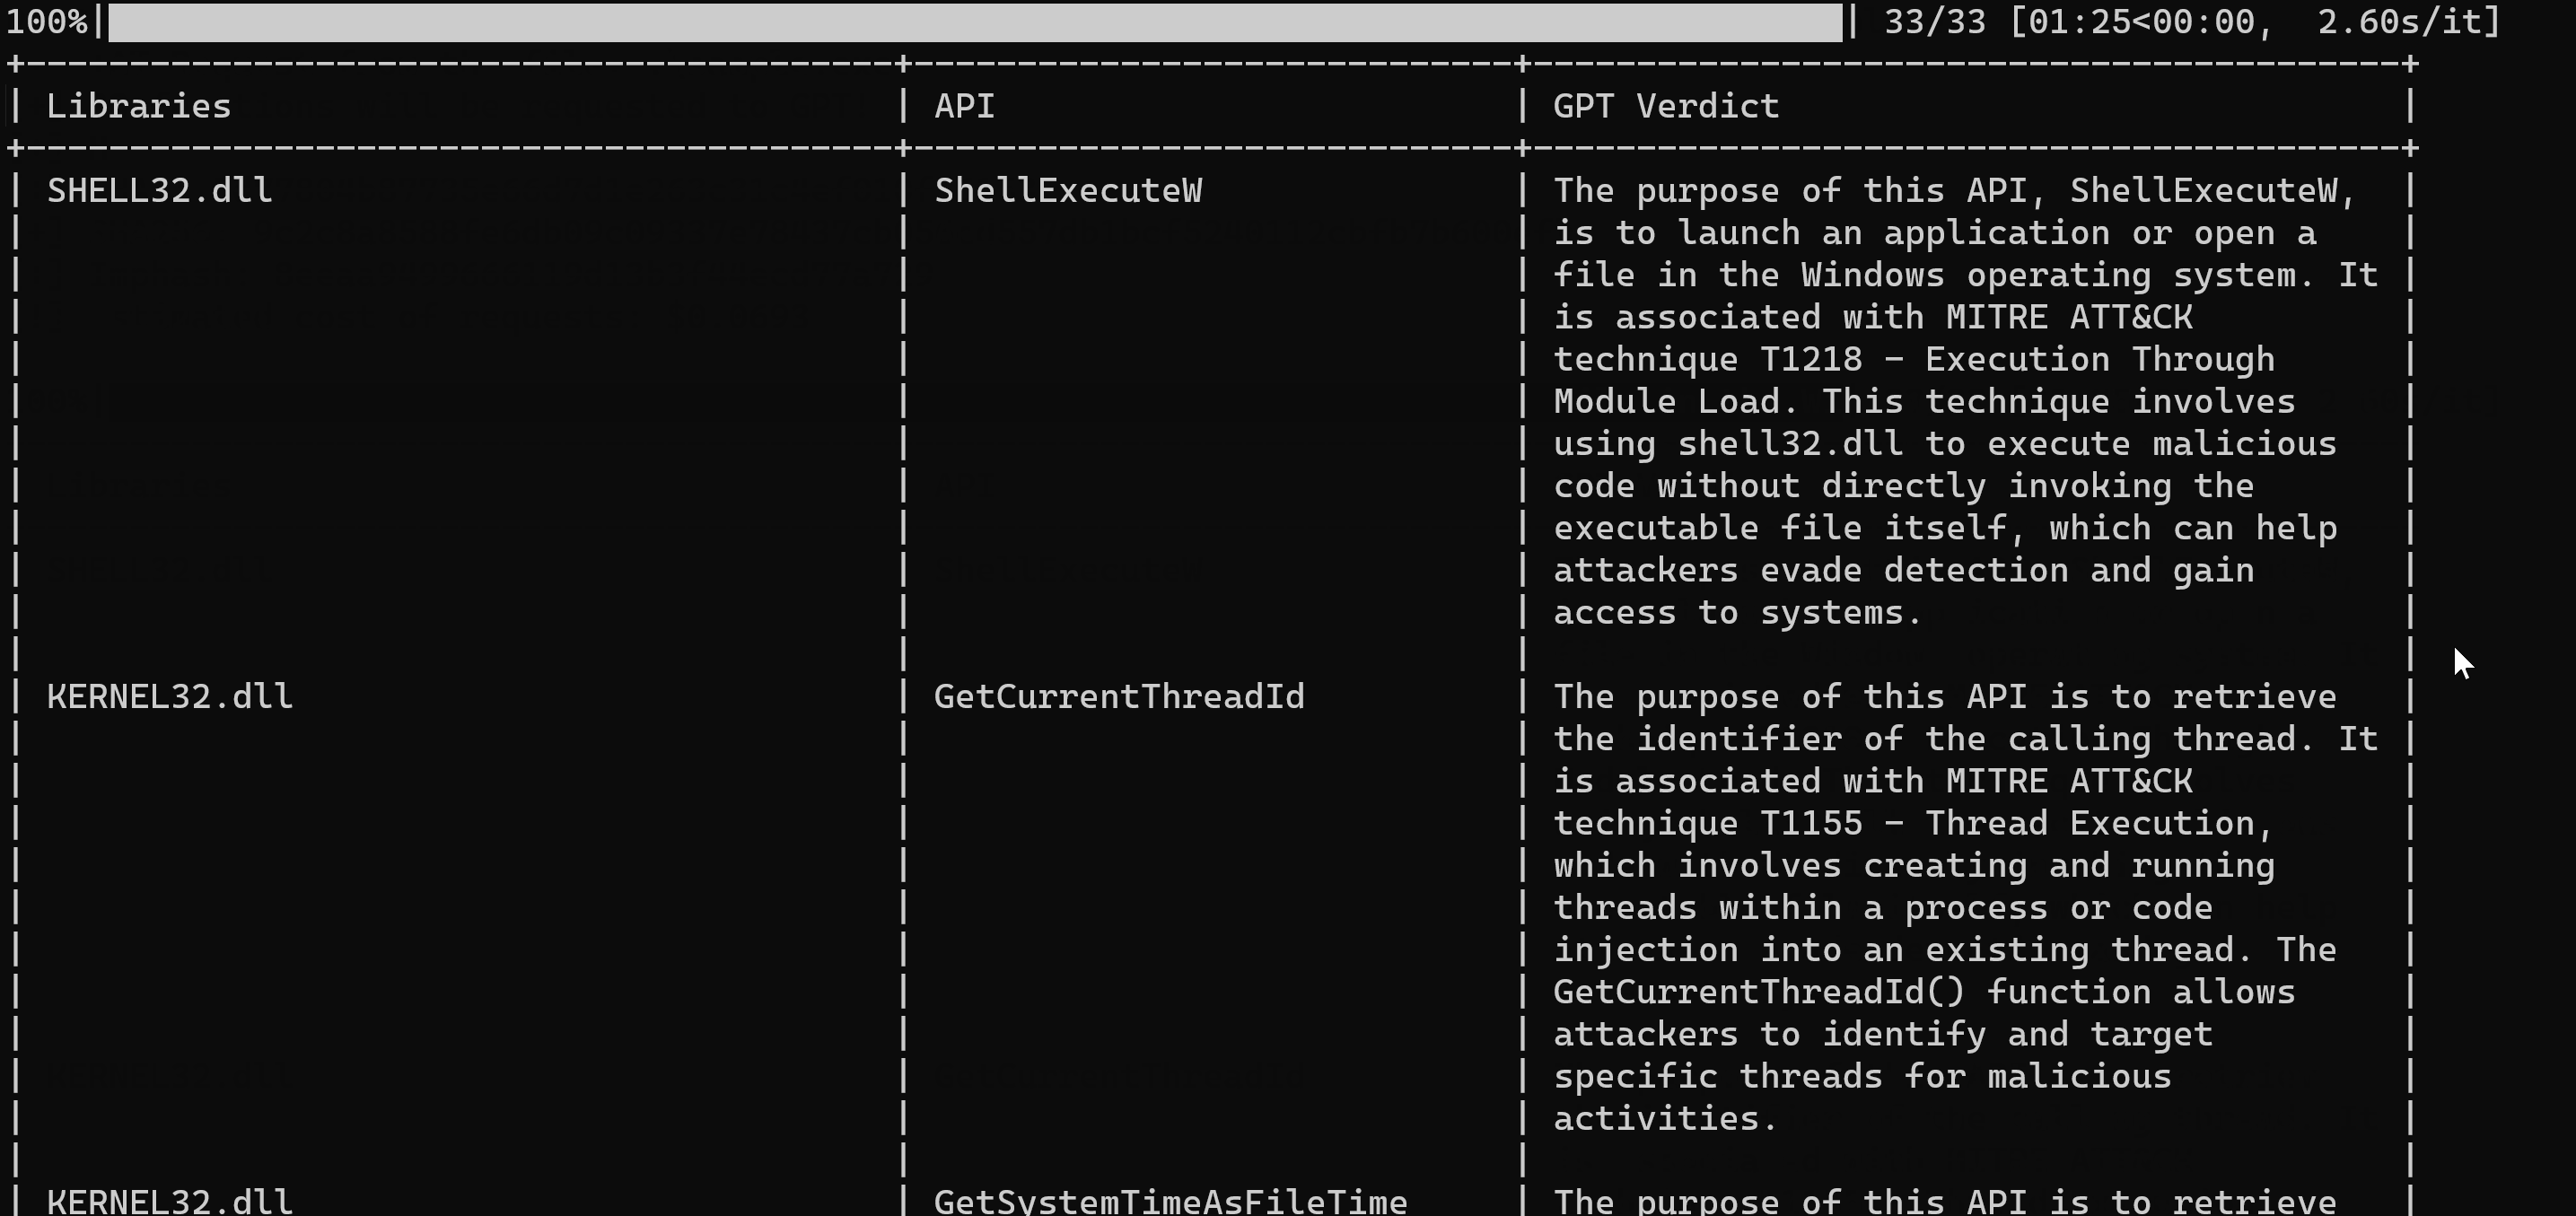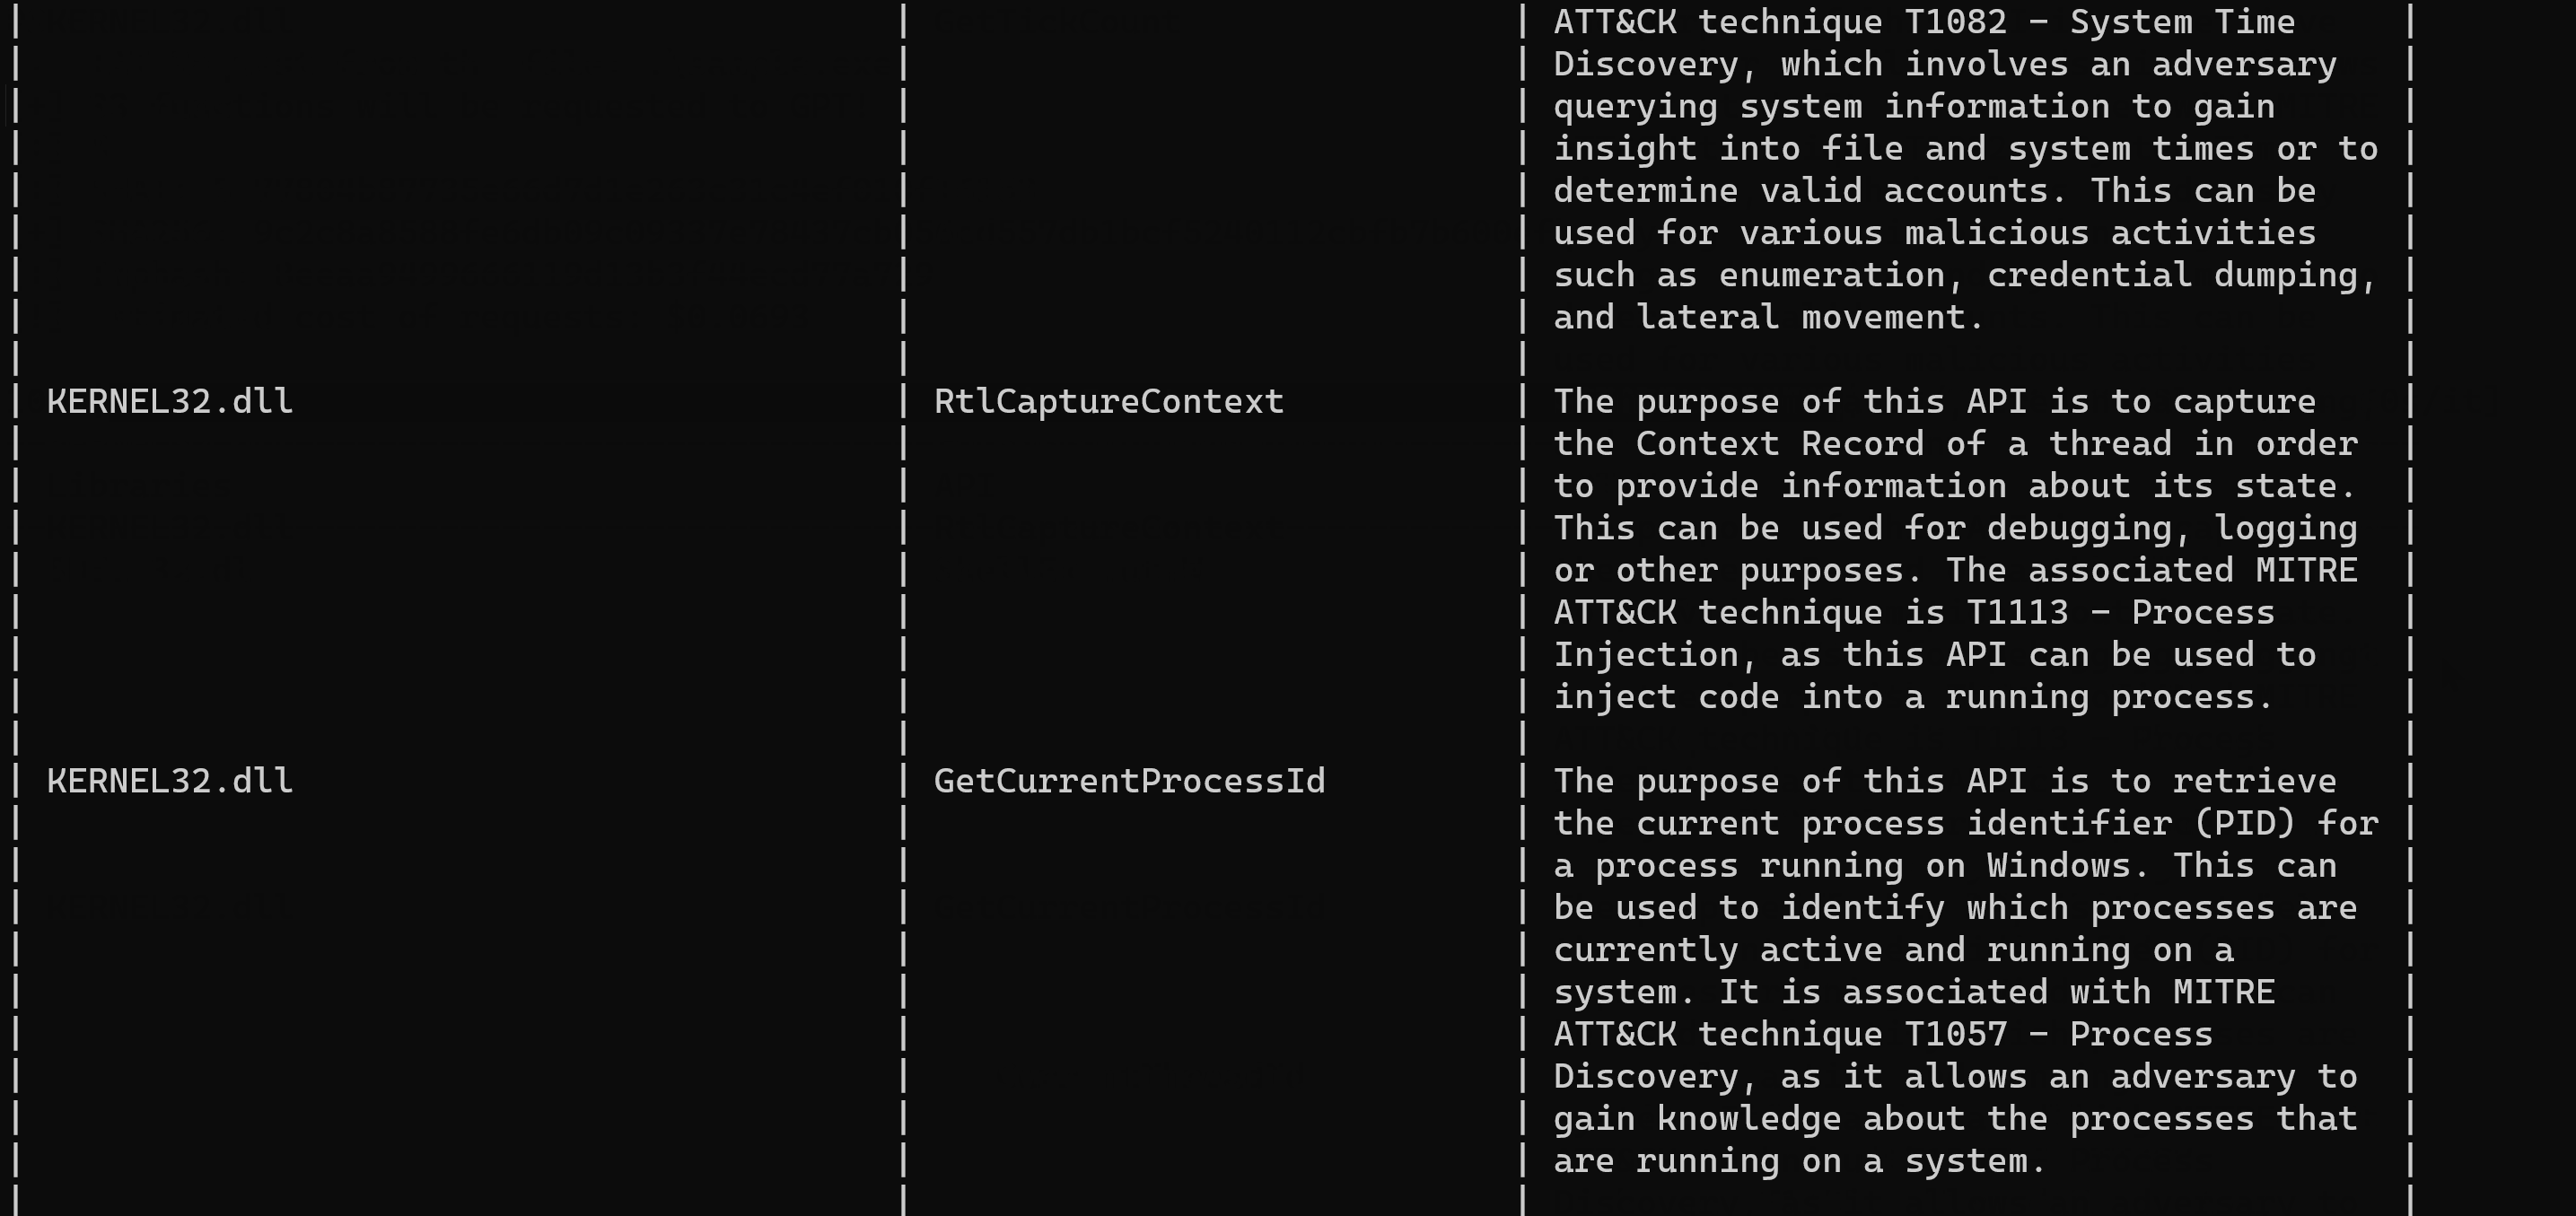
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
386
fr0gger/iatelligenceIATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 akamai/cve-2025-60719-afd.sys
Proof-of-concept and root-cause analysis of CVE-2025-60719, a use-after-free vulnerability in Windows afd.sys leading to local privilege escalation,…
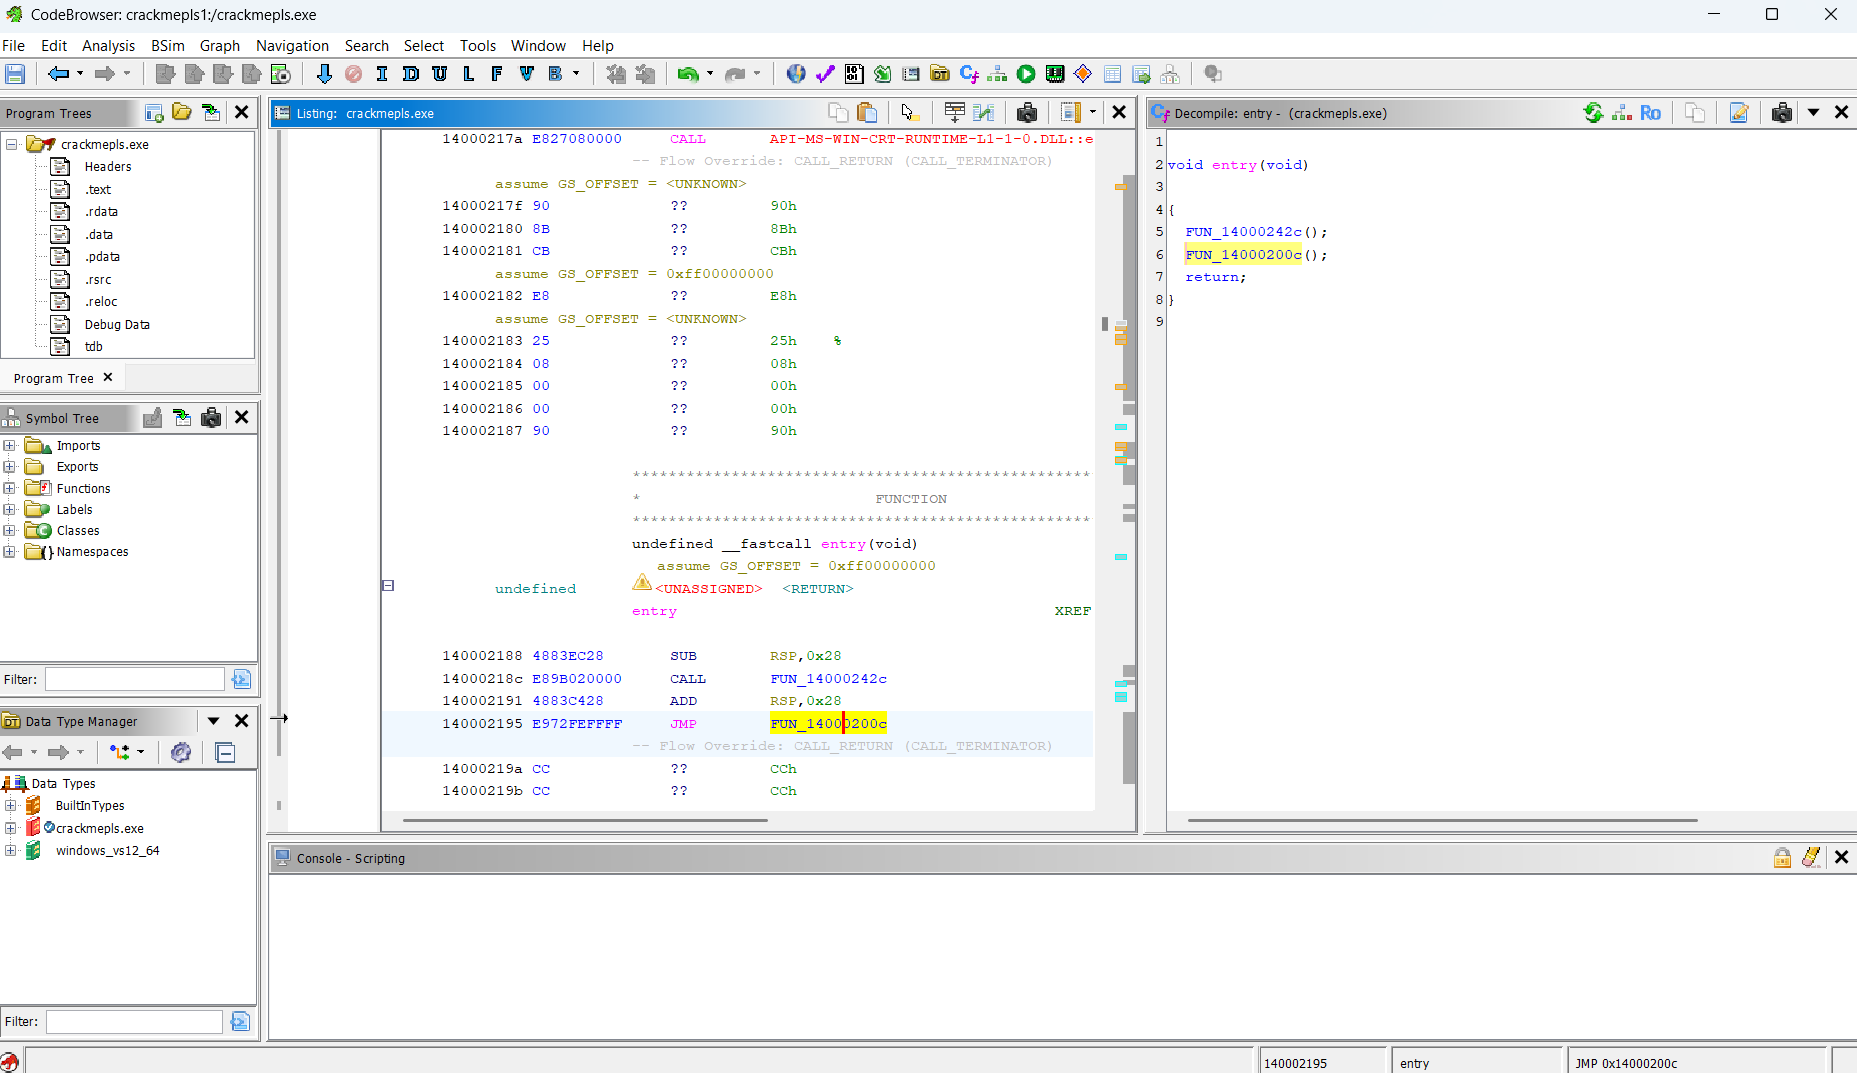 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
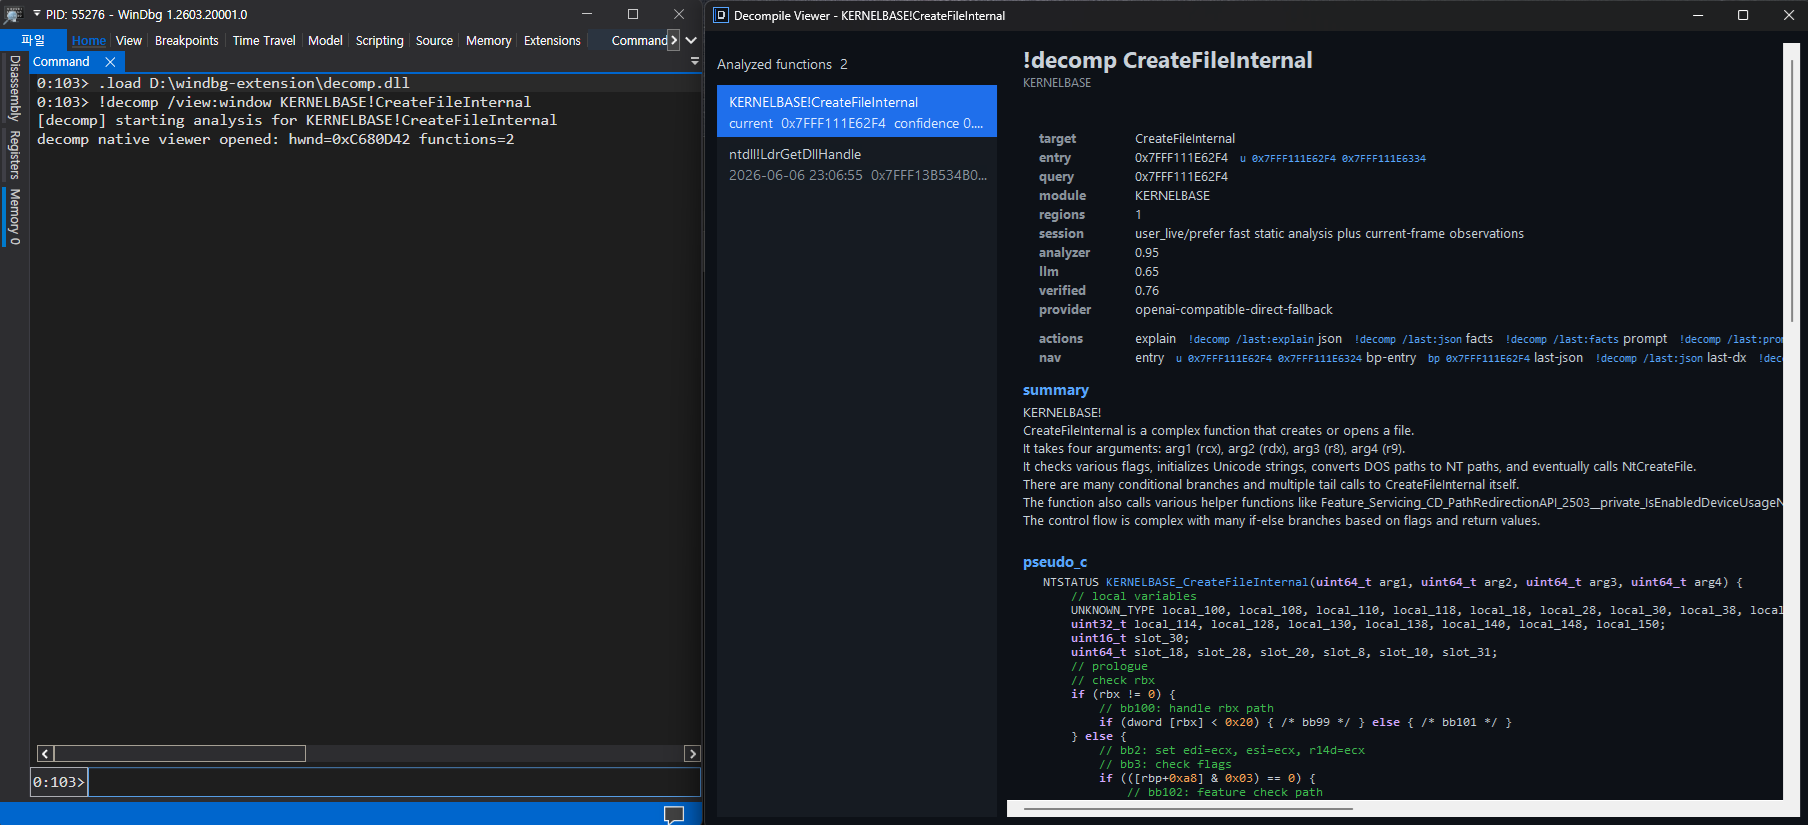 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 lauriewired/malimite
iOS and macOS Decompiler
 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT-4, Claude, and local models supported!
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 karib0u/kernagent
Headless AI agent for deterministic reverse engineering.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
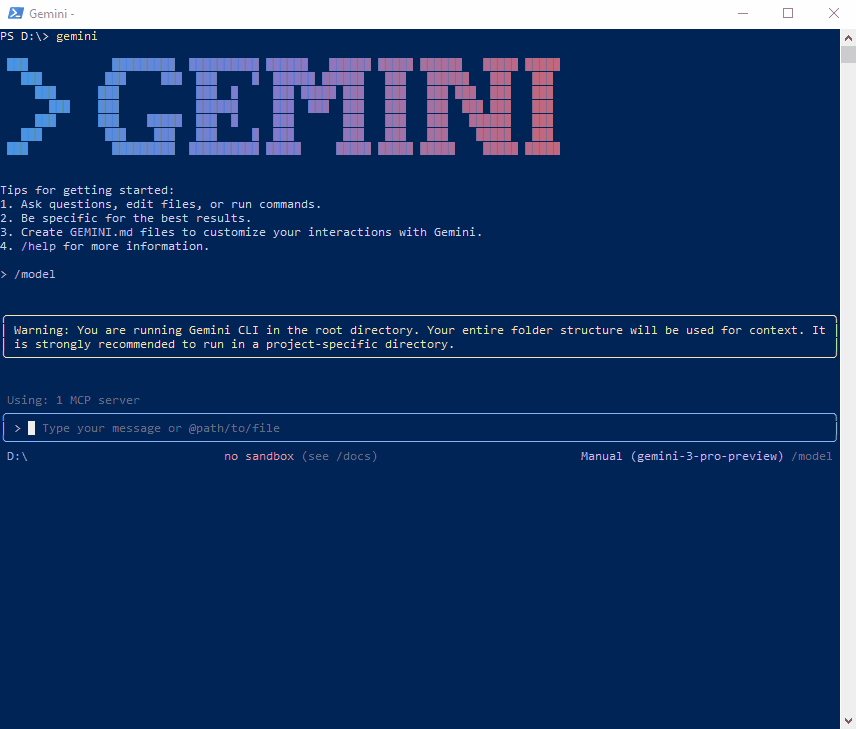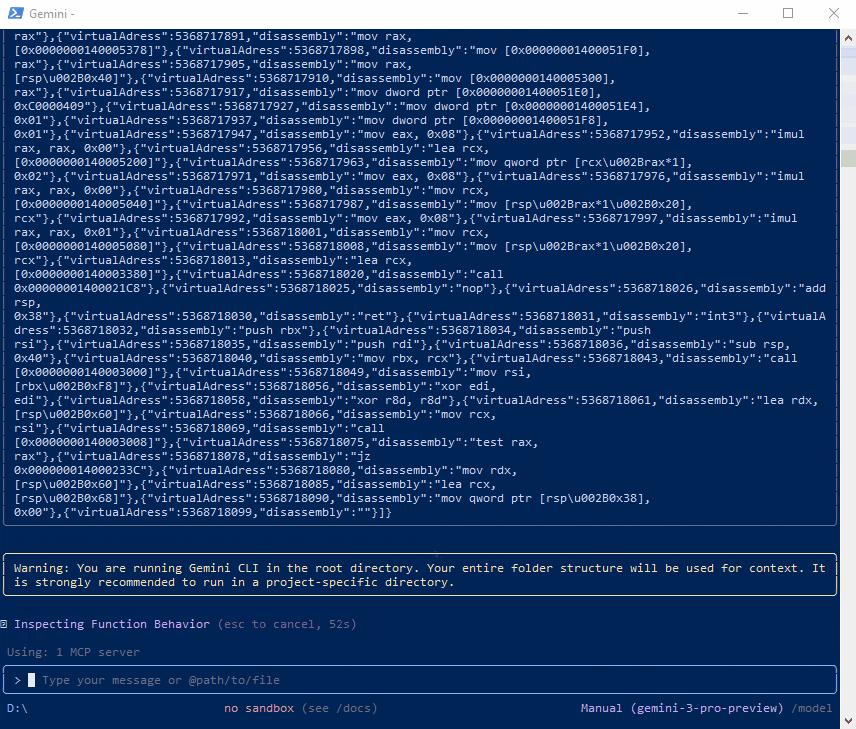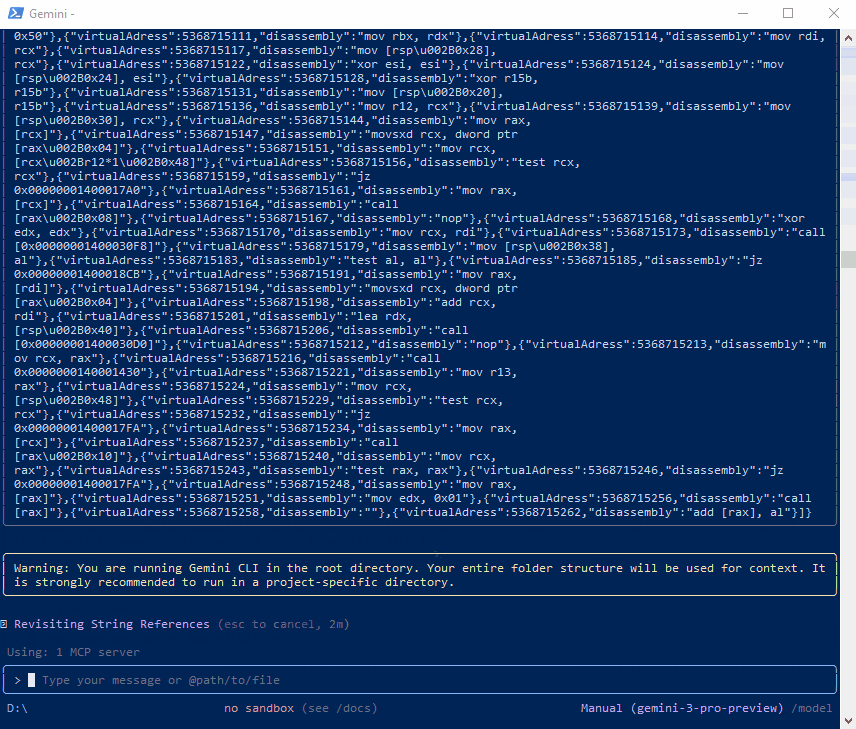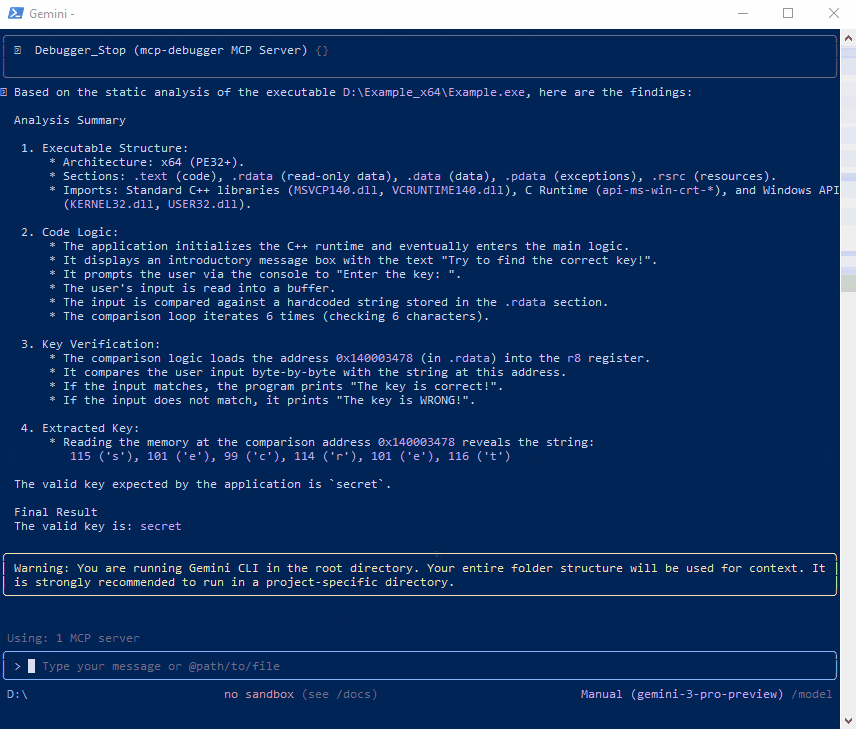 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…