

rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
rizinorg/rizinUNIX-like reverse engineering framework and command-line toolset.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 angr/angr
A powerful and user-friendly binary analysis platform!
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
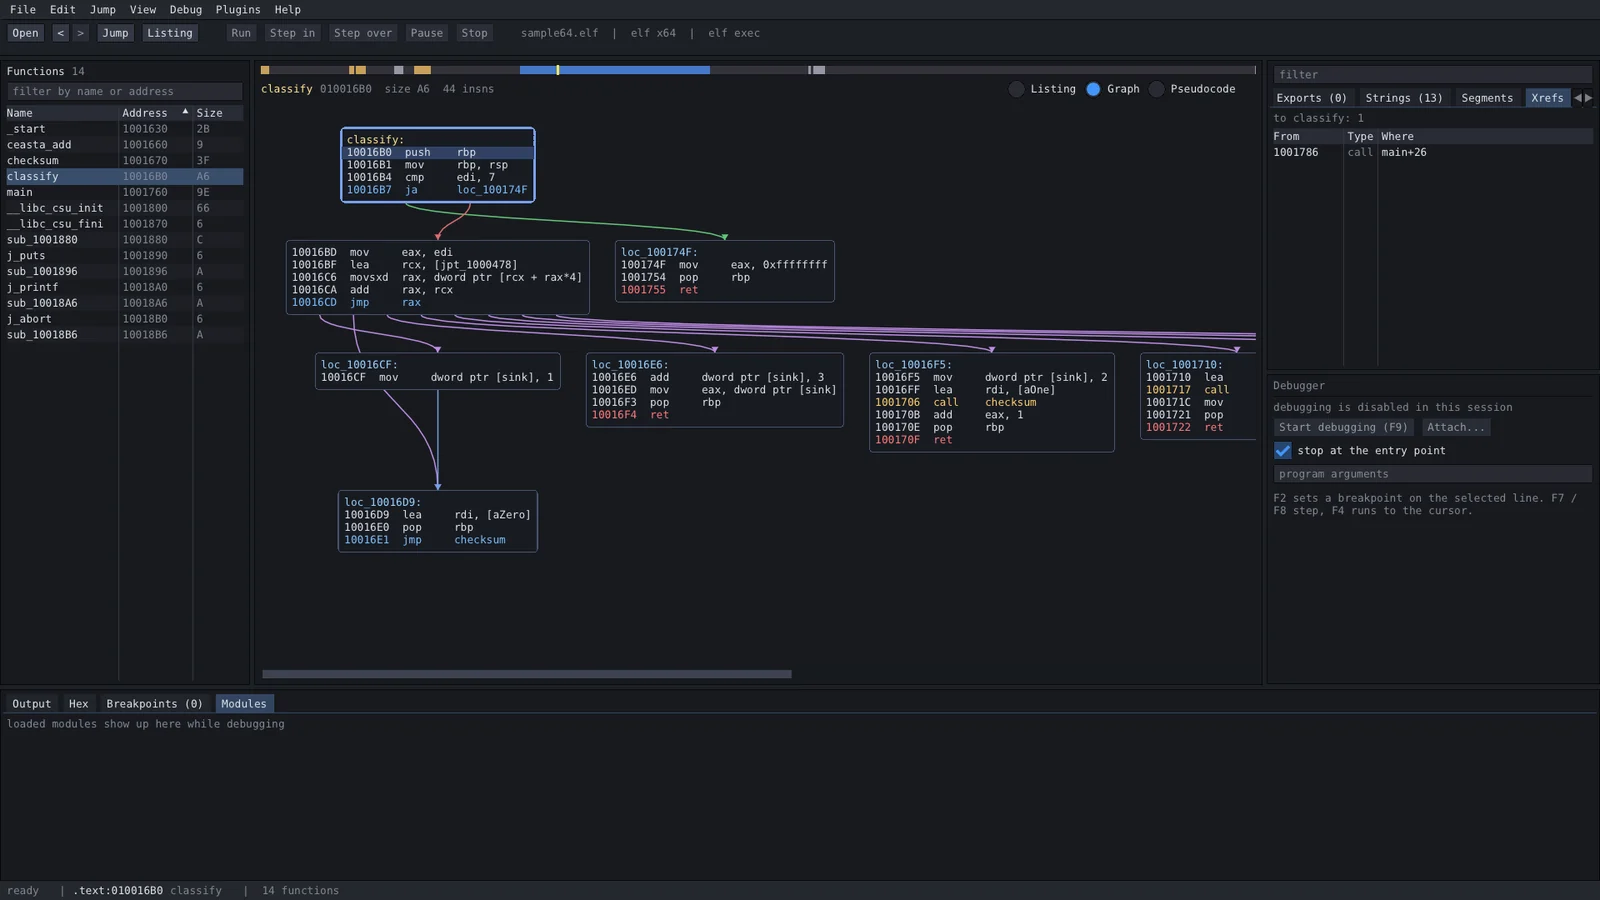 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
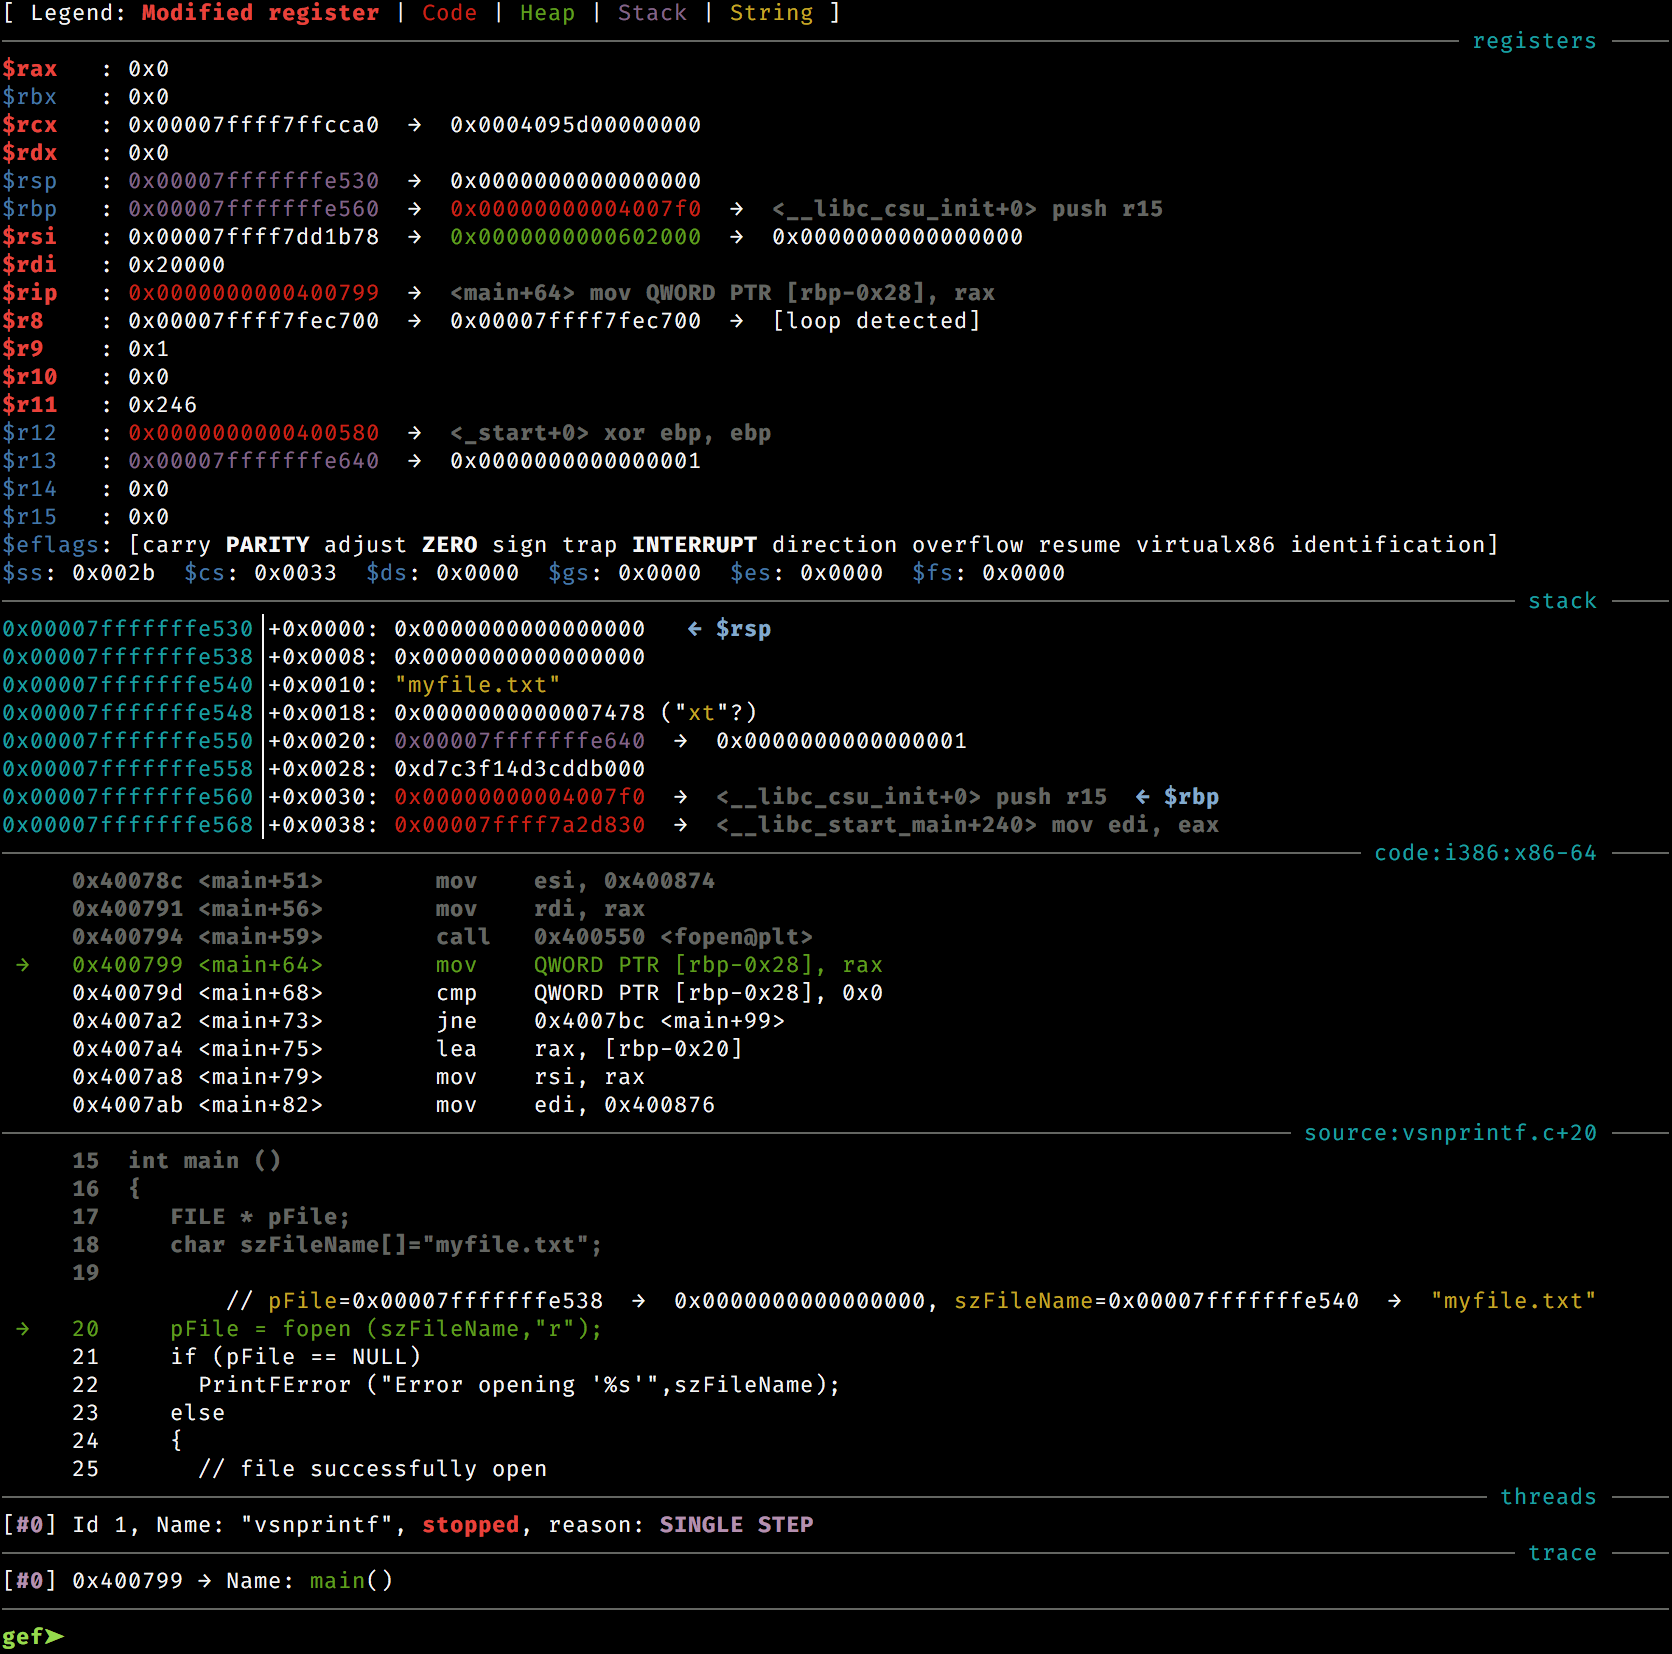 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
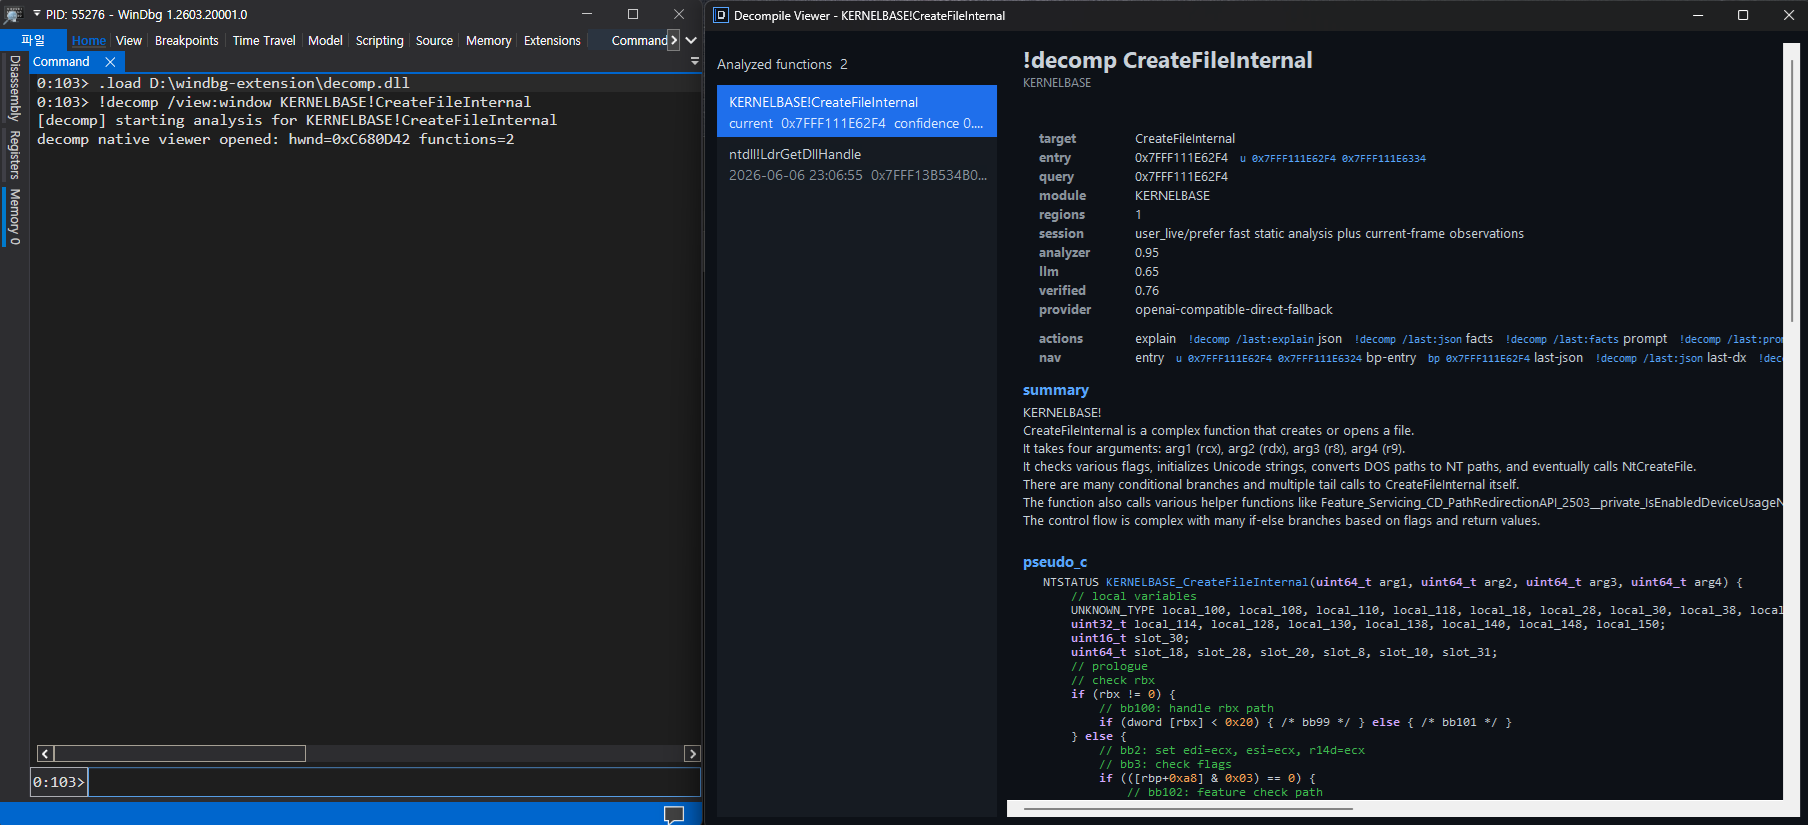 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
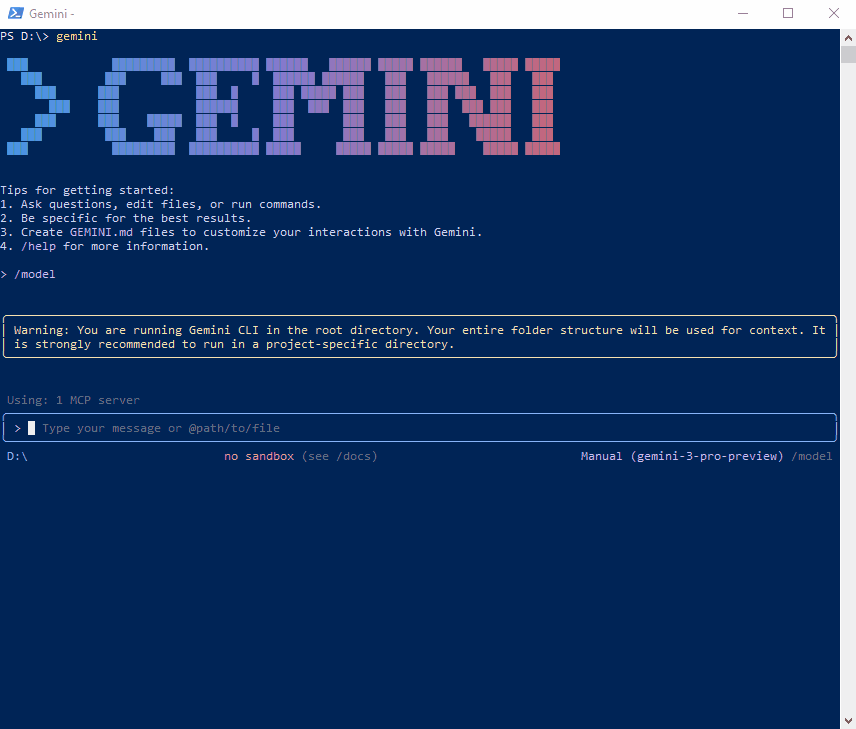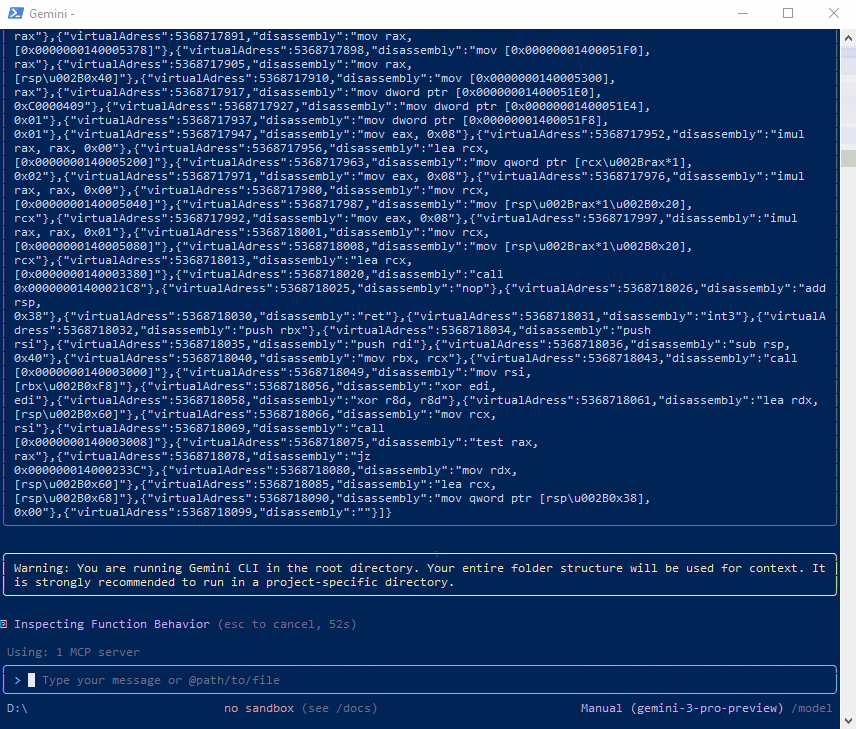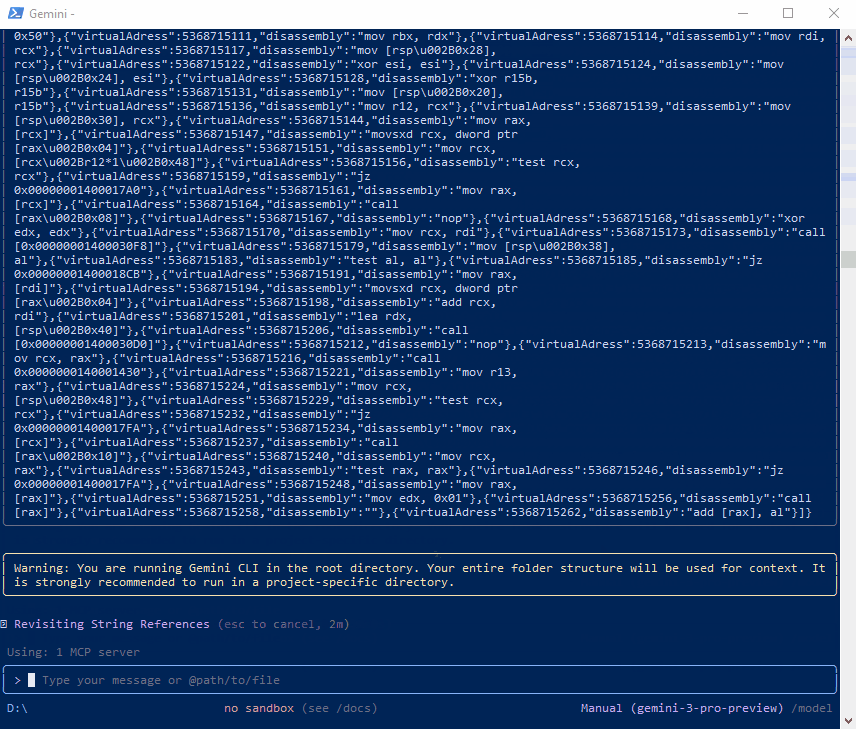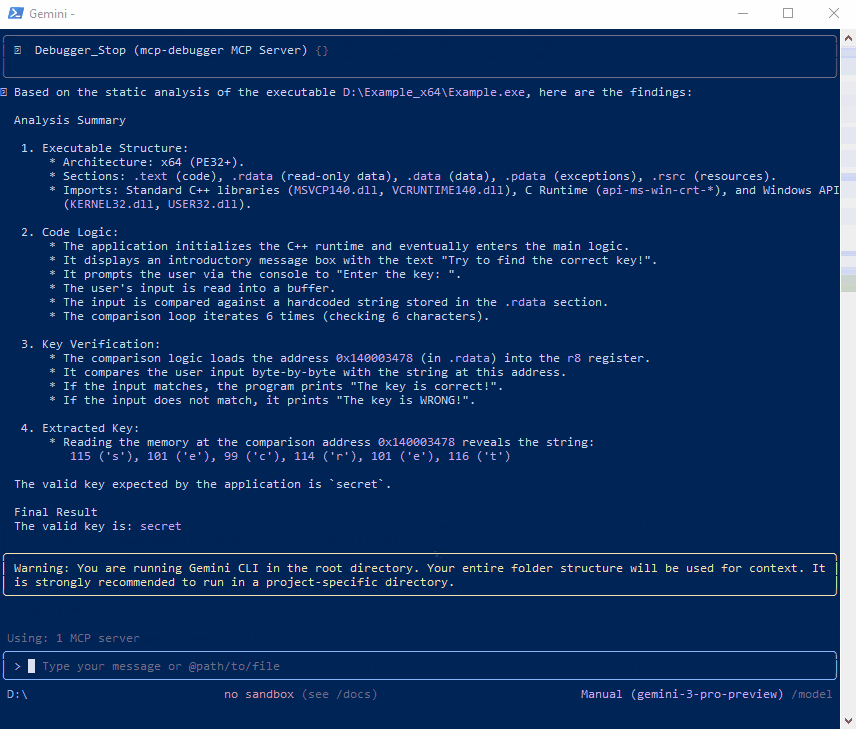 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…