
raptor
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+7
3.8k
gadievron/raptorAutonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
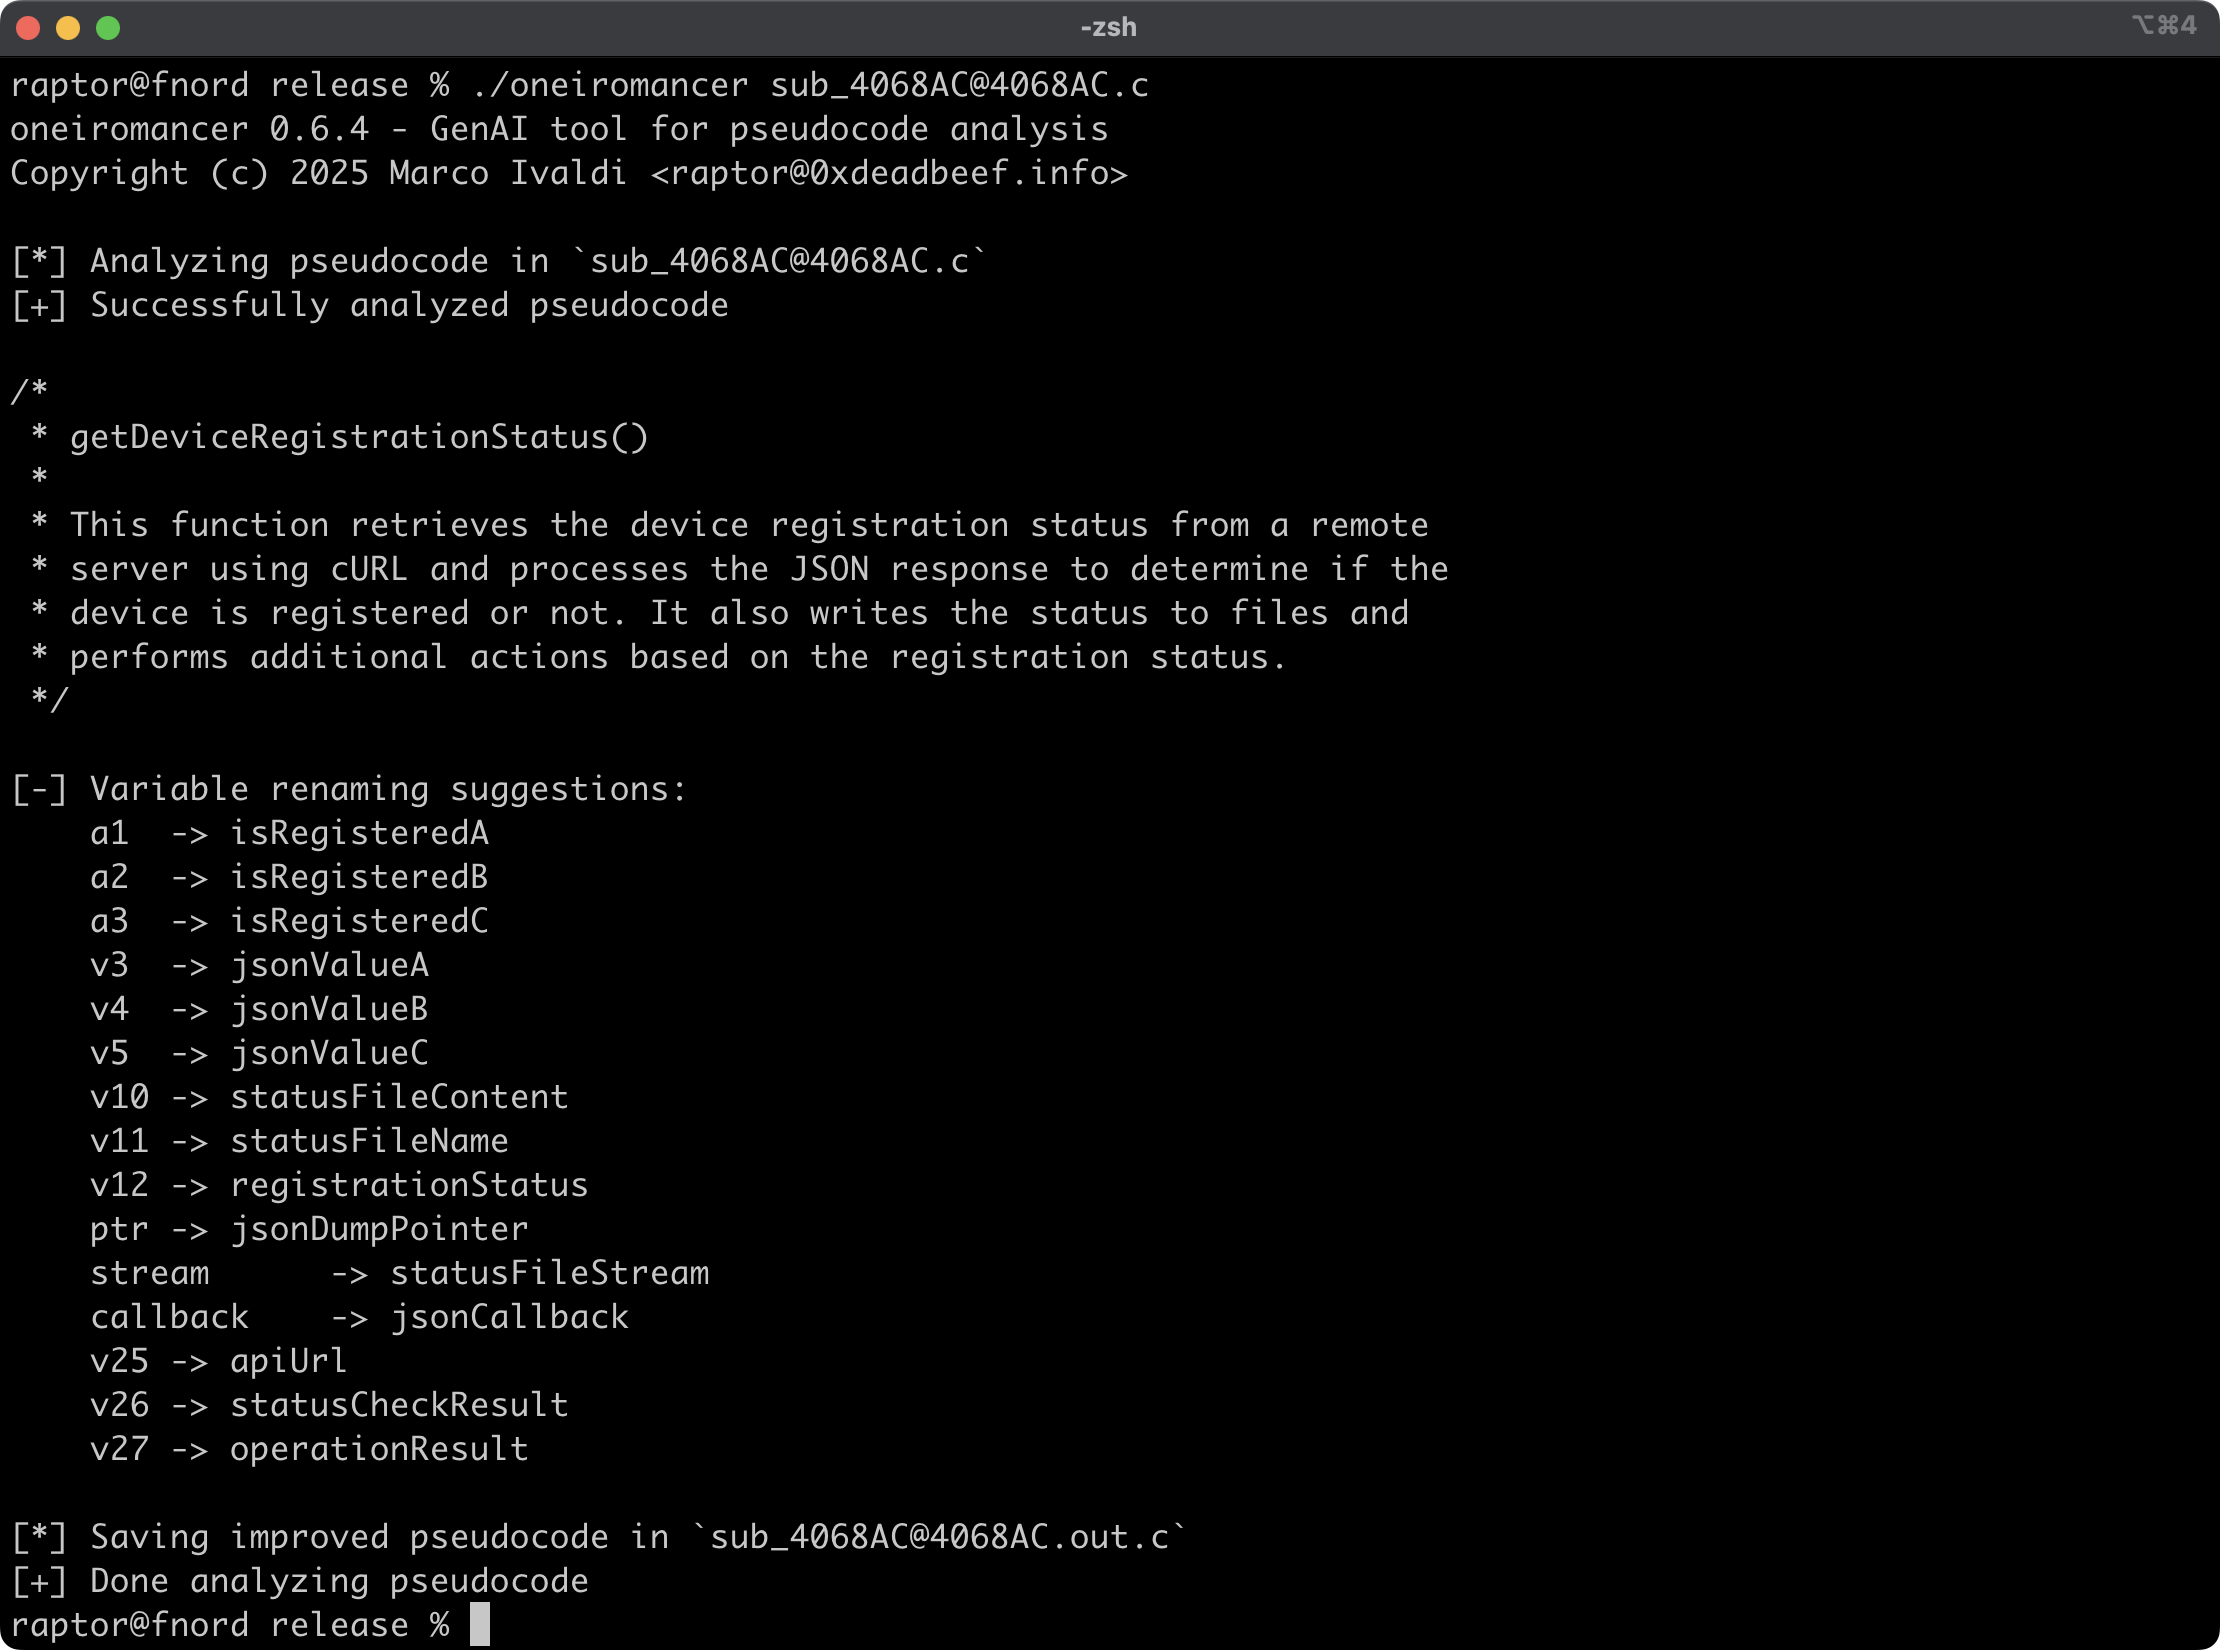 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 angr/angr
A powerful and user-friendly binary analysis platform!
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
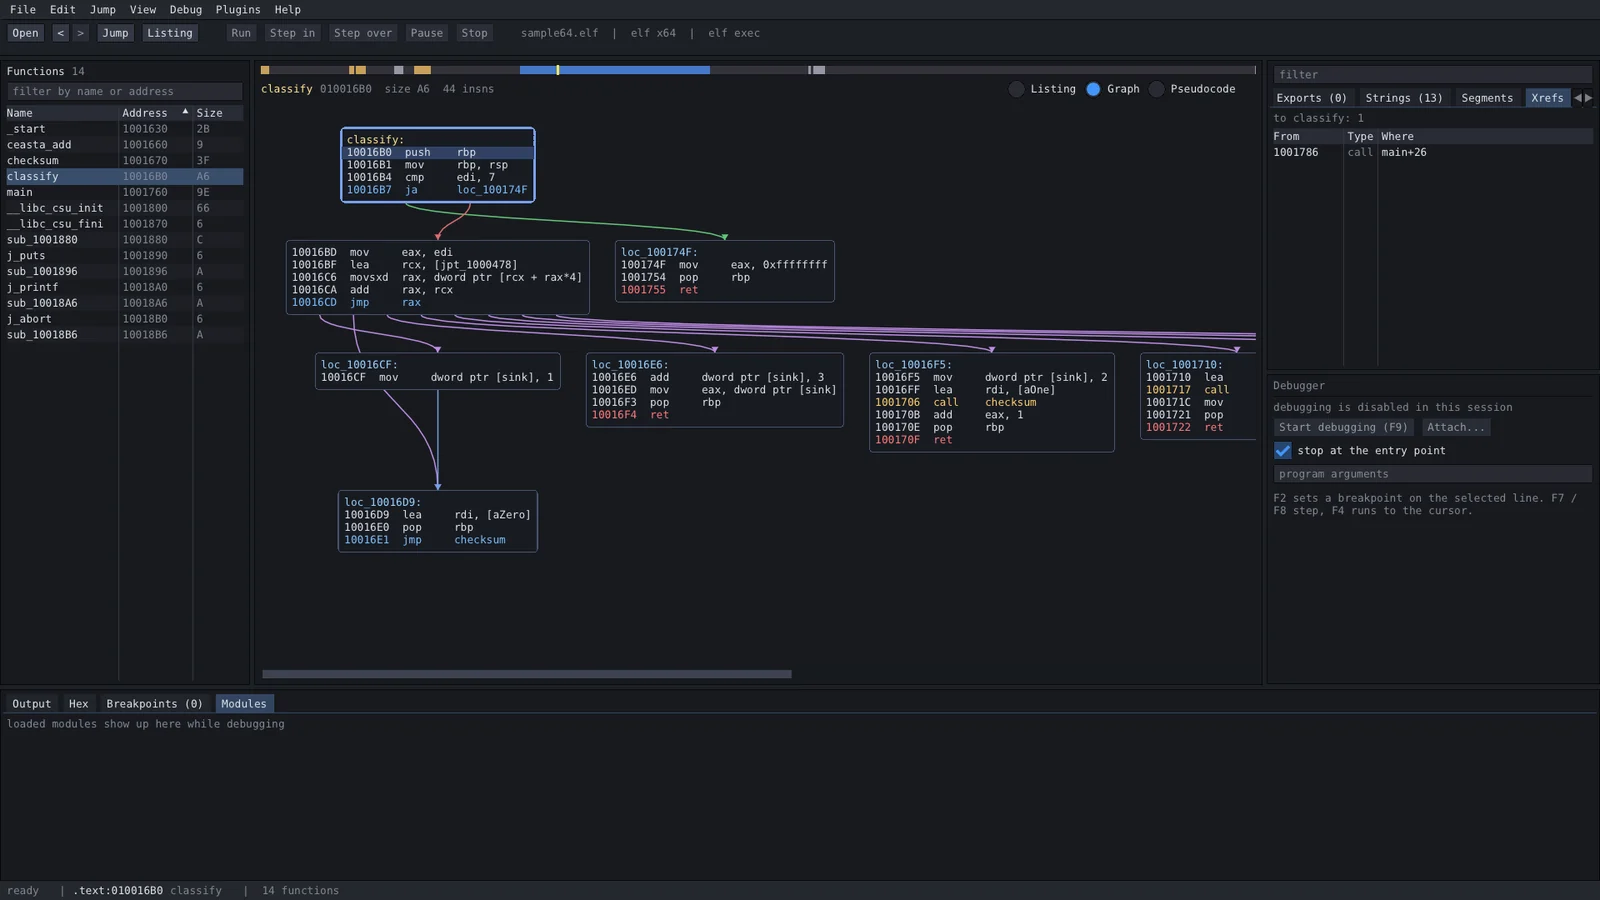 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
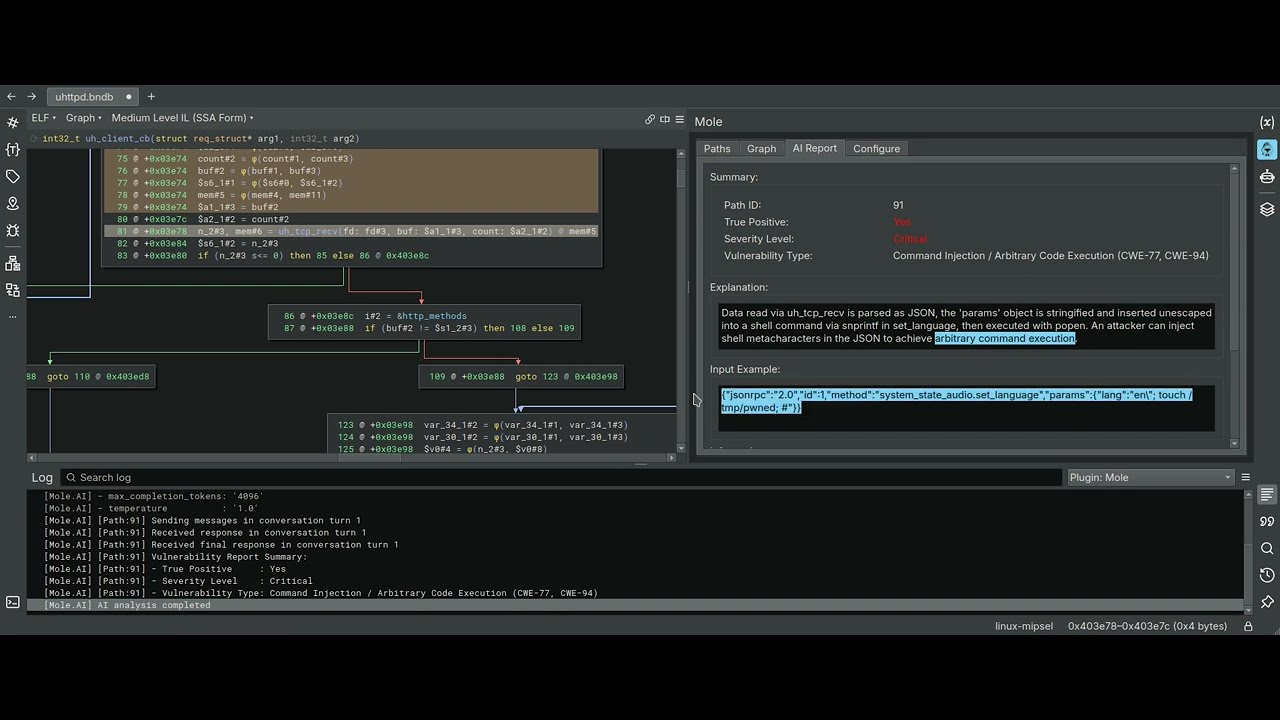 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…