Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/zux0x3a/tchopper
Lateral MovementPenetration TestingRed Teaming
GitHubzux0x3a/tchopper

TChopper

conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine

View RepositoryWebsite
567355 years agoReviewed by Kitploit
Share

TChopper

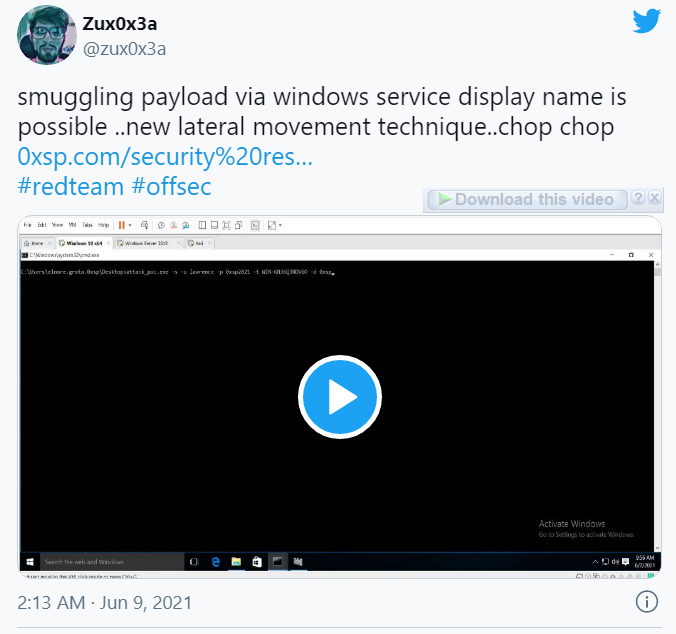
New technique I have discovered recently and give it a nickname (Chop chop) to perform lateral movement using windows services display name and WMI by smuggling the malicious binary as base64 chunks and automate the process using the TChopper tool.
image

image

How it works

  • the tool will get the file you willing to smuggle and encode the file as base64 into memory stream
  • divide the length of each line to fit 150-250 character length (250 is maximum allowed space for service lpDisplayname parameter https://docs.microsoft.com/en-us/windows/win32/api/winsvc/nf-winsvc-createservicea).
  • for chop chop attack it will create a unique service for each segmented chunk => start the service => then delete it to avoid duplicates or you can choose to only modify the service attack mode to be more faster and stable by choosing attack mode option (-m)
  • later on, it will modify service lpbinarypath parameter with required command line to grab service display name and pip out the results into tmp_payload.txt
  • finally, after finishing delivering all chuncks of the file as base64, the tool will create another service to decode the content into valid executbale and run it

while if you are conducting lateral movment using WMI technique you can also use Chopper to do that

  • Tchopper will authenticate you session using WMI
  • creation of multiple process and use powershell unique command to pip out each segment to c:\users\public\chop.enc
  • create final process to use certutil to decode the content into binary and execute it

image

Usage

#chop chop mode 
chopper.exe -s -u USERNAME -p PASSWORD -d DOMAIN -f BINARYLOCAL PATH 


# chop chop done 
chopper.exe -m -u USERNAME -p PASSWORD -d DOMAIN -f BINARYLOCAL PATH 

# use WMI to smuggle 
chopper.exe -w -u DOMAIN\USERNAME -p PASSWORD -t MACHINE -f LOCALBINARYPATH

https://youtu.be/xbvhzHul7w0

Detailed research

http://0xsp.com/security%20research%20&%20development%20(SRD)/smuggling-via-windows-services-display-name-lateral-movement

Show support

i create offsec tools for open-source community, show your support https://paypal.me/0xsp

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    938
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    352
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    291

Explore all tools

Browse our collection of tools

View all tools →








