
 you-ssef9/cve-2025-52691
This repository contains a safe Proof of Concept (PoC) to detect vulnerable SmarterMail versions affected by CVE‑2025‑52691. The script performs version detection only and does not exploit the vulnerability.

This repository contains a safe Proof of Concept (PoC) to detect vulnerable SmarterMail versions affected by CVE‑2025‑52691. The script performs version detection only and does not exploit the vulnerability.
CVE-2025-52691 – SmarterMail Version Detection PoC 📌 Description
This repository contains a Python Detection Proof‑of‑Concept (PoC) for CVE‑2025‑52691, a critical vulnerability affecting SmarterMail Build 9406 and earlier.
⚠️ This PoC performs detection only It does NOT upload files, NOT exploit, and NOT execute code.
🛑 Vulnerability Summary
CVE ID: CVE‑2025‑52691
Product: SmarterMail
Affected Versions: Build 9406 and earlier
Impact: Arbitrary file upload → Potential Remote Code Execution
Authentication: Not required
An unauthenticated attacker could upload arbitrary files to any location on the mail server if the target is vulnerable.
🔍 How does this PoC work?
This script detects vulnerable SmarterMail instances by identifying the application and extracting its version/build number.
Detection Logic
Send HTTP GET requests to common SmarterMail endpoints:
/ /interface/ /interface/login /interface/root
Detect SmarterMail presence by:
Searching for the string SmarterMail in the response body
Or detecting version patterns in HTTP headers or HTML content
Extract the version/build number
Uses regular expressions to identify version strings
Extracts the build number from the last version segment
Vulnerability Check
If build number ≤ 9406 → VULNERABLE
If build number > 9406 → NOT VULNERABLE
No payloads, uploads, or malicious actions are performed.
🧪 Example Detection Logic (Simplified) Version detected: 17.6.9406 Build number: 9406 Result: VULNERABLE
Version detected: 17.7.9412 Build number: 9412 Result: NOT VULNERABLE
🚀 How to Run Requirements
Python 3.x
requests library
Install dependencies:
pip install requests
Single Target python3 CVE-2025-52691POC.py -u http://target.com
Multiple Targets python3 CVE-2025-52691POC.py -l targets.txt
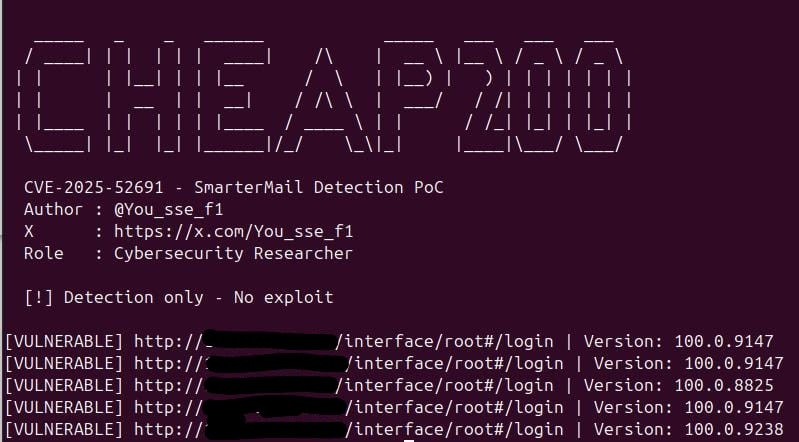
🖥 Example Output [VULNERABLE] http://example.com | Version: 17.6.9406
[NOT VULNERABLE] http://example.com | Version: 17.7.9412
[UNKNOWN] http://target.com | SmarterMail not detected
📎 References
CSA Singapore Advisory: https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2025-124
SmarterMail Official Site: https://www.smartertools.com/smartermail
⚠️ Disclaimer
This script is provided for educational and defensive security purposes only.
Scan only systems you own or have explicit authorization to test.
The author is not responsible for any misuse or illegal activity.
📜 License
MIT License
👤 Author
Researcher: @You_sse_f1
X (Twitter): https://x.com/You_sse_f1
Role: Cybersecurity Researcher
ℹ️ About
Python Detection PoC for CVE‑2025‑52691 Tags:
cve · detection · smartermail · cybersecurity · poc






