
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-22978-demo — CVE-2022-22978漏洞实例代码 | Kitploit
Tools/GitHubGitHub/wan9xx/cve-2022-22978-demo
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHubwan9xx/cve-2022-22978-demo

CVE-2022-22978-demo

CVE-2022-22978漏洞实例代码

View Repository
232 years agoNot yet reviewed
Share

CVE-2022-22978-demo

CVE-2022-22978 vulnerability demo code

Exploitation Conditions

Although rated as high severity, the exploitation conditions are quite stringent. Personally, I find this vulnerability rather underwhelming.

  1. First, spring-security must be within the affected scope.
  2. Second, it requires the use of spring-security's regex matcher regexMatchers or directly using RegexRequestMatcher, and must employ . to match paths, for example:
    • regexMatcher("/api/.*") // allow all subpaths under /api
    • regexMatcher("/files/.*\\.jpg") // match all file requests ending with .jpg
    • regexMatcher("/user/.*/profile") // allow profile paths for any username under /user
  3. In practice, such scenarios are rare. For example, with regexMatcher("/api/.*"), there must also be a controller annotated with @RequestMapping("/api/*") to handle all requests under /api. Otherwise, even if %0a%0d is used to bypass spring-security's path matching rules, a 404 error will be returned.

Exploitation Demo

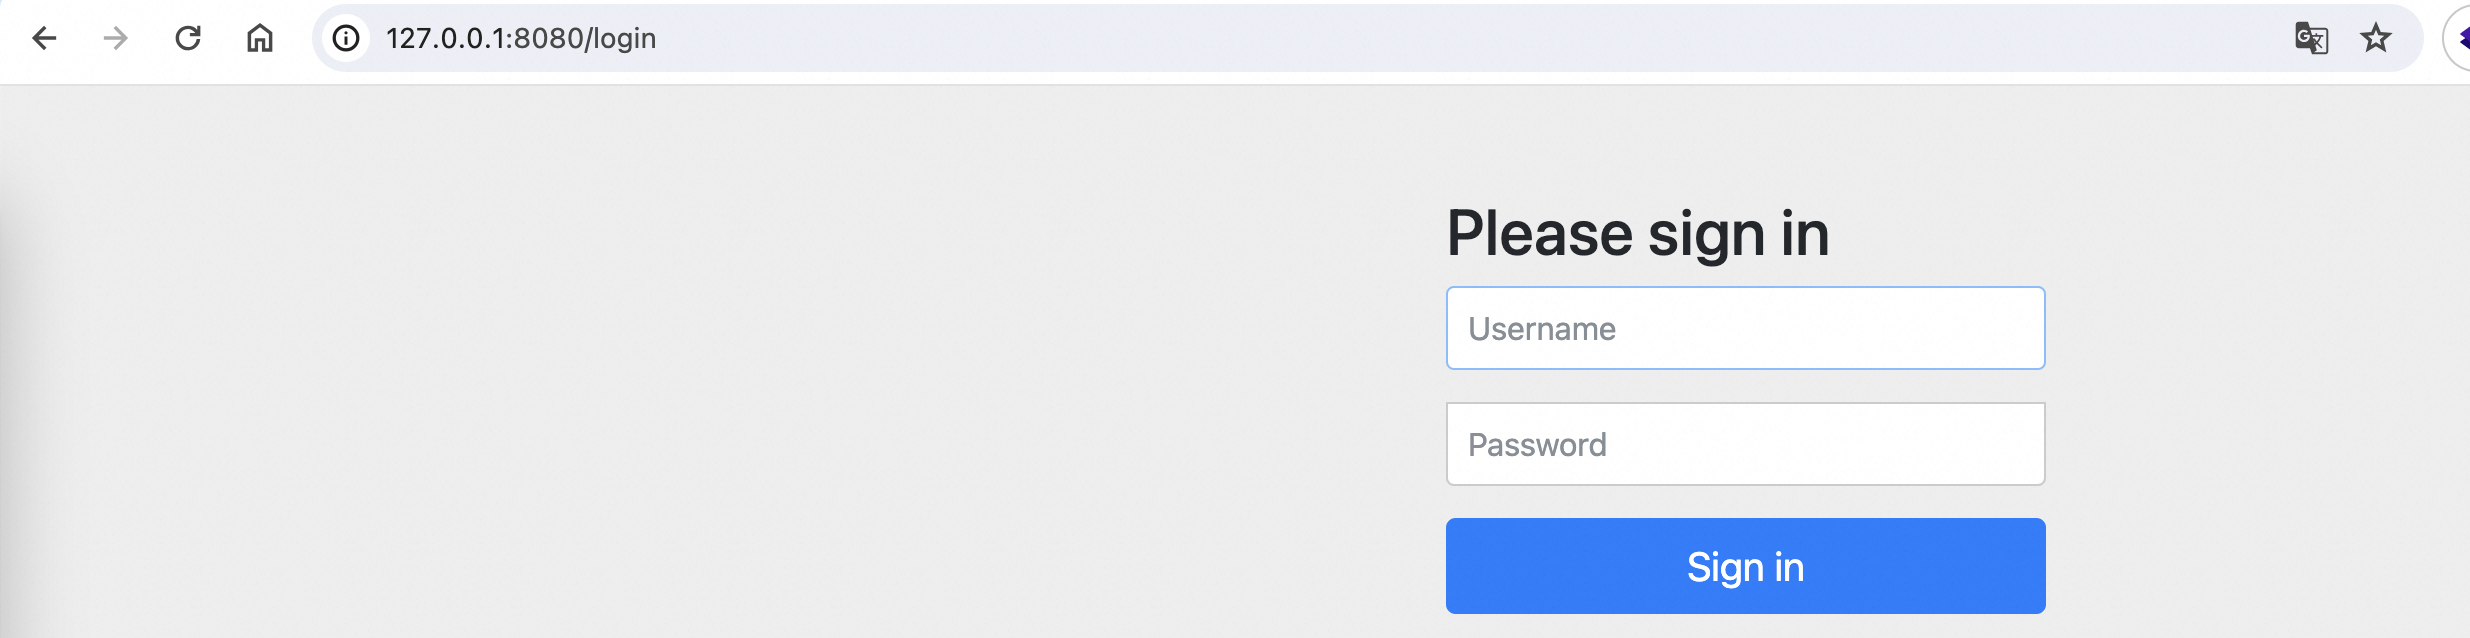
Normal access to any path redirects to the default login page provided by spring-security. image
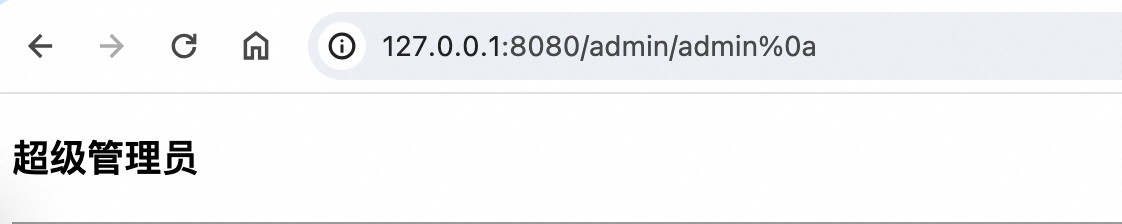
Visit: http://127.0.0.1:8080/admin/admin%0a, successfully bypasses login. image
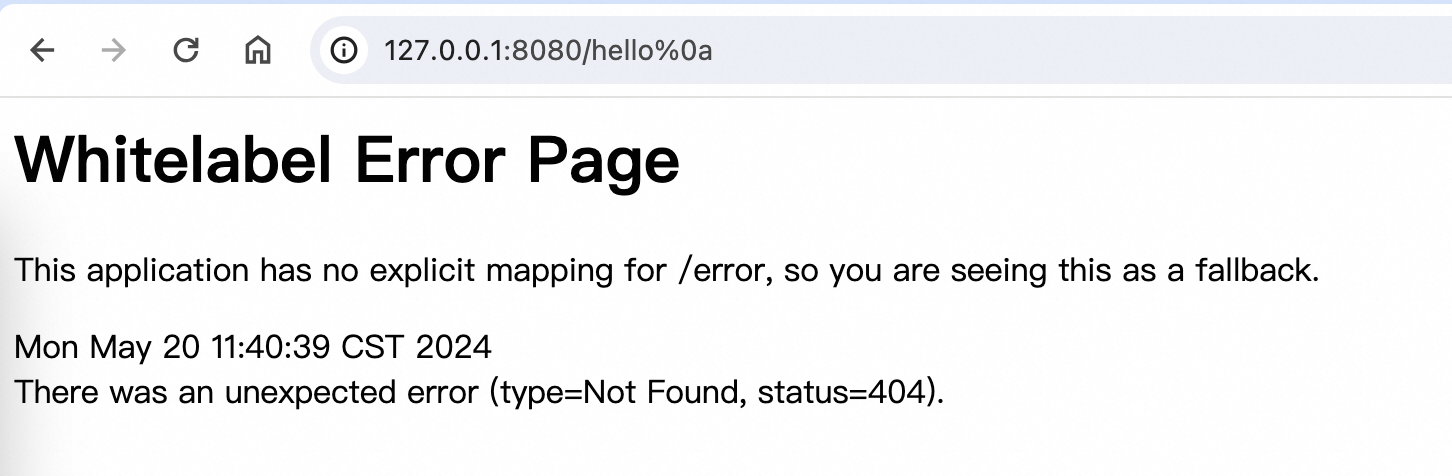
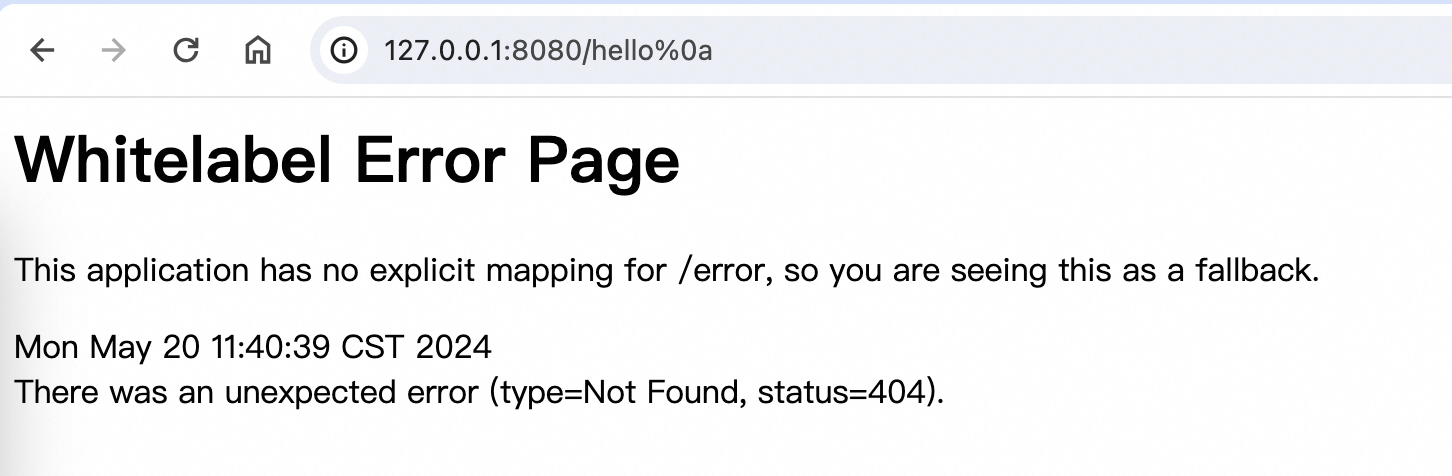
Visit: http://127.0.0.1:8080/hello%0a Bypasses security checks that require login for all paths, but because there is no controller annotated with @RequestMapping("/hello/*"), mapping fails, resulting in a 404 error. image
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →







