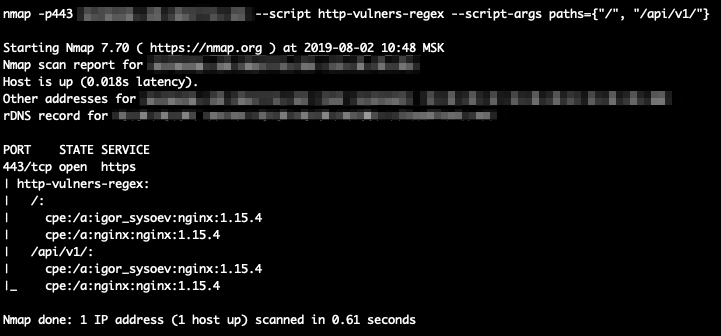
 vulnerscom/nmap-vulners
Nmap NSE script that queries the Vulners API to identify known vulnerabilities (CVEs) for detected network services, enhancing standard port scanning with automated CVE lookup and CVSS scoring.

Turn an nmap service scan into a ranked list of CVEs, exploits and what is being attacked in the wild.
One NSE script that takes the software nmap already identified, asks the Vulners database what is known about it, and prints the answer inside the scan report - worst first, by what is actually exploitable.


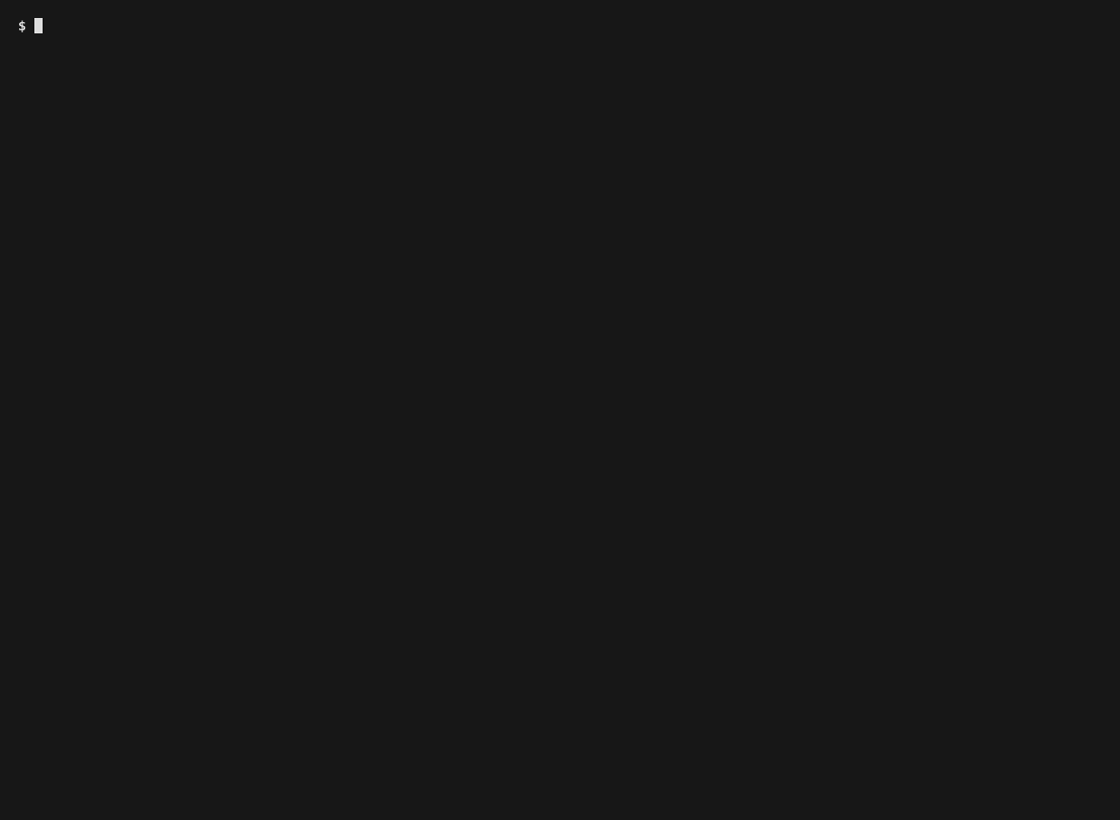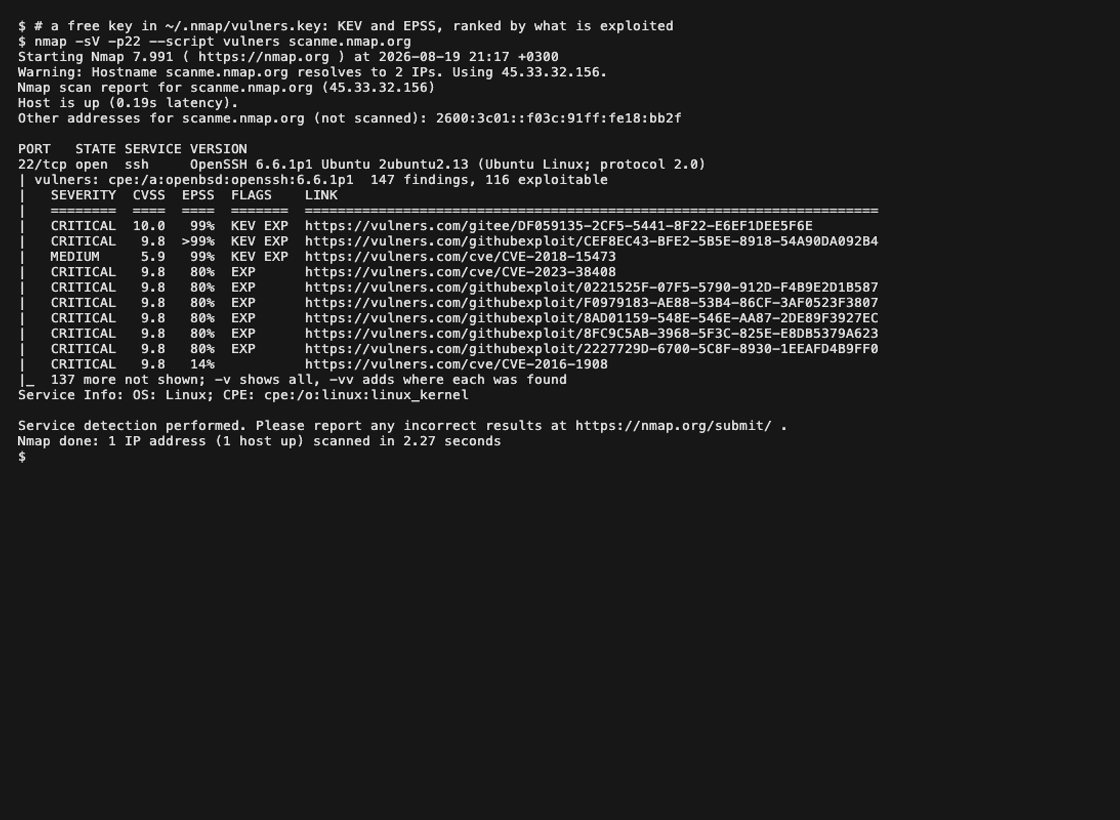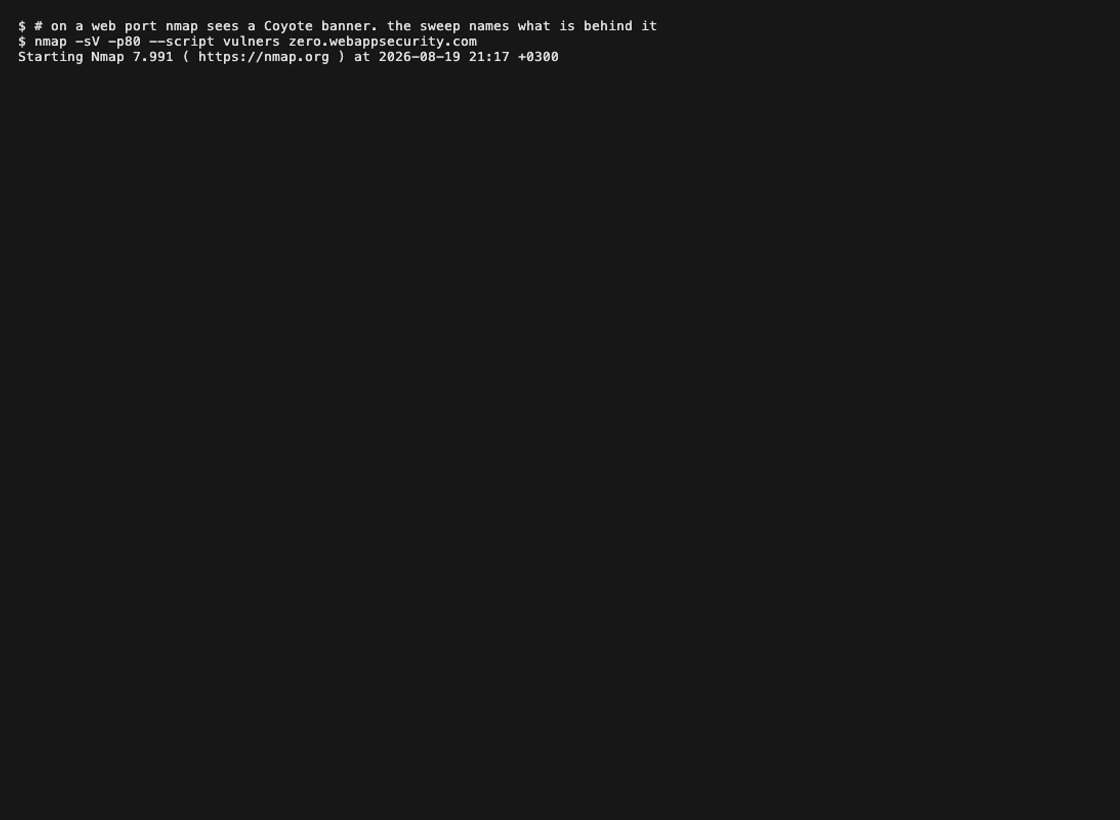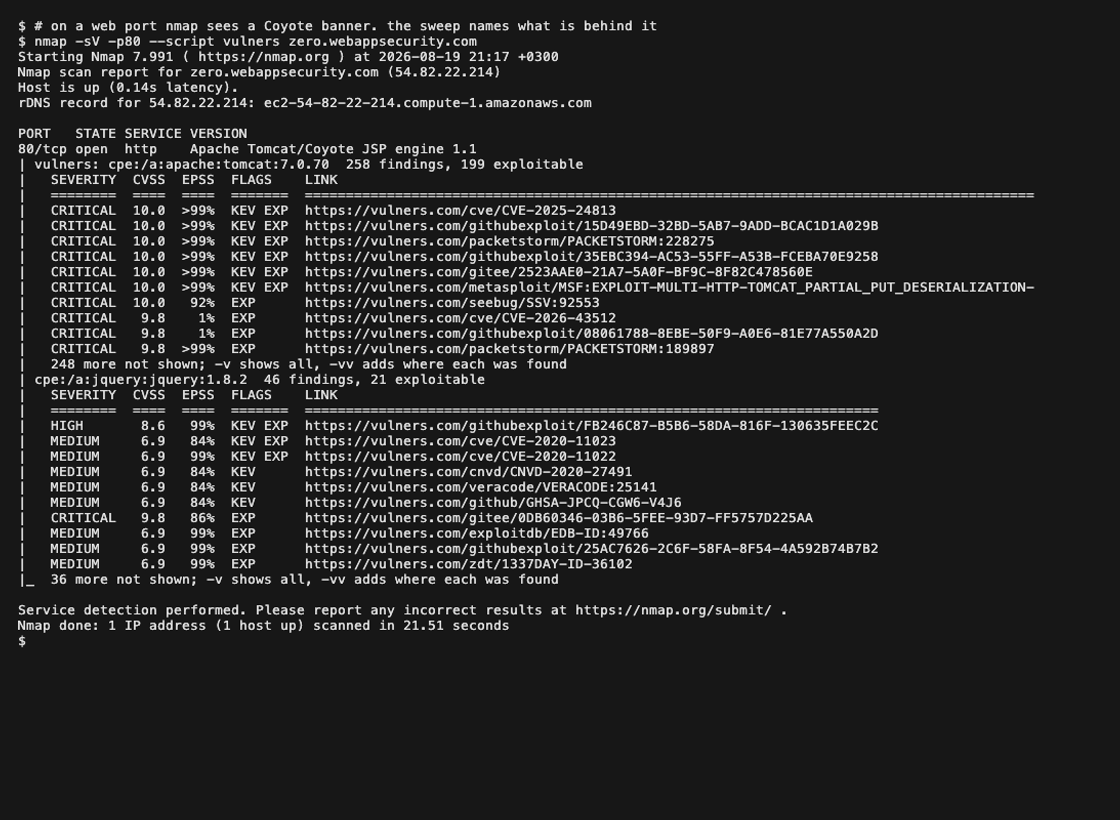
Real scans of hosts published for scanning. No key, then a key, then a web
port: nmap's -sV reports a Coyote banner and the sweep names the
Tomcat and the jQuery behind it.
For every open port it looks up the software nmap identified - the CPEs that
-sV produced - and prints what Vulners knows about it: worst first by what is
being exploited rather than by score alone, and each row a link to the page
behind it.
On an HTTP port it also fingerprints the web stack itself, which names software
-sV cannot see - an application framework, a CMS, the PHP version behind a
reverse proxy. 721 rules read the parts of a response that carry a version: the
Server header, X-Powered-By, cookies, the page title, <meta> tags,
<script src> filenames and the body. Those identities are looked up too, and
published onto the port so the rest of the scan can use them.
Two things it does beyond the sweep:
-sV could not name a service,
the raw banner is matched against rules for FTP, SMTP, SSH, MySQL, DNS, NTP,
LDAP and more. That costs no extra request, and it is the case where a port
would otherwise report nothing at all./CHANGELOG.txt for Drupal,
/administrator/manifests/files/joomla.xml for Joomla. A host running none of
the six probed products is sent nothing extra.nmap -sV --script vulners <target>
That is the whole interface. It works without an API key; with one it tells you more. There is no mode switch.
PORT      STATE SERVICE VERSION
80/tcp    open  http    Apache httpd 2.4.7 ((Ubuntu))
| vulners: cpe:/a:apache:http_server:2.4.7  272 findings, 56 exploitable
|   SEVERITY  CVSS    AI  FLAGS    LINK
|   ========  ====  ====  =======  ==============================================================
|   CRITICAL  10.0   8.8  EXP      https://vulners.com/gitee/3E6BA608-776F-5B1F-9BA5-589CD2A5A351
|   CRITICAL   9.8   9.9  EXP      https://vulners.com/zdt/1337DAY-ID-39214
|   CRITICAL   9.8   9.6  EXP      https://vulners.com/packetstorm/PACKETSTORM:171631
|   CRITICAL   9.8   9.9           https://vulners.com/cve/CVE-2021-44790
|   CRITICAL   9.8   9.8           https://vulners.com/cve/CVE-2023-25690
|_  262 more not shown; -v shows all, -vv adds where each was found
With a key, the same scan of the same host answers differently - KEV means
CISA has recorded the vulnerability as exploited in the wild, and EPSS is the
published probability that it will be:
| vulners: cpe:/a:apache:http_server:2.4.7  272 findings, 78 exploitable
|   SEVERITY  CVSS  EPSS  FLAGS    LINK
|   ========  ====  ====  =======  ==============================================================
|   CRITICAL   9.1  >99%  KEV EXP  https://vulners.com/cve/CVE-2024-38475
|   CRITICAL   9.0  >99%  KEV EXP  https://vulners.com/cve/CVE-2021-40438
|   CRITICAL   9.1  >99%  KEV      https://vulners.com/cnvd/CNVD-2024-36387
|   CRITICAL  10.0   71%  EXP      https://vulners.com/gitee/3E6BA608-776F-5B1F-9BA5-589CD2A5A351
|   CRITICAL   9.8   97%  EXP      https://vulners.com/cve/CVE-2021-44790
|_  262 more not shown; -v shows all, -vv adds where each was found
Same 272 findings, a different order, a different top row - and 22 more of them known to be exploitable, because a key links each exploit to the CVEs it exploits. Both of these are real answers from vulners.com, captured against a local server presenting that banner.
Facts outrank predictions. Findings are ordered:
active - a coordinator's judgement that exploitation is happeningCVSS breaks ties inside a band, not across them: an exploited 7.5 is a worse problem than an unexploited 9.8, and this is the order that says so.
Columns follow the data. A signal the answer did not carry loses its column rather than showing an empty cell, because a blank EPSS reads as "quiet", and that is a claim an absent field cannot support.
| Without a key | Every CPE nmap found is looked up on the free endpoint. Findings, scores, exploit flags and Vulners' own AI score. No credits, no account |
| A key, no credits | Each finding gains what the id endpoint knows: titles, dates, the upstream advisory or exploit page, the exploit-to-CVE linkage, CISA KEV, and - depending on the licence - EPSS and SSVC |
| A key, one credit | Software the free path could not name at all is identified from its raw banner. This is the only thing here that costs anything, and only for a service with no CPE |
A port that already carries a CPE never costs a credit: measured across four products, the free lookup returns the same CVEs as the paid one for a CPE. What a credit buys is identification, not more vulnerabilities.
Free keys are at vulners.com/userinfo.
macOS, Linux, Kali, WSL - one line, no arguments:
curl -fsSL https://raw.githubusercontent.com/vulnersCom/nmap-vulners/master/install.sh | sh
Windows - PowerShell as Administrator:
irm https://raw.githubusercontent.com/vulnersCom/nmap-vulners/master/install.ps1 | iex
The installer asks nmap where it keeps its data, copies the scripts and their
data files there, rebuilds the script database, and then checks that
--script vulners really resolves to what it just installed - nmap ships a
vulners.nse of its own, and this replaces it.
# into ~/.nmap, no sudo; the installer prints the NMAPDIR line to add to your profile
curl -fsSL https://raw.githubusercontent.com/vulnersCom/nmap-vulners/master/install.sh | sh -s -- --user

# a specific directory
./install.sh --prefix /usr/local/share/nmap

# a specific release
./install.sh --ref v2.0

# remove everything it installed
./install.sh --uninstall
PowerShell takes the same options: -User, -Prefix, -Ref, -Uninstall.
git clone https://github.com/vulnersCom/nmap-vulners
cd nmap-vulners
./install.sh







