Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve-2026-32699-facturascripts-nick-bypass — Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the unvalidated nick parameter via proxy interception. Patched but unpublished CVE. | Kitploit
Tools/GitHubGitHub/turkios/cve-2026-32699-facturascripts-nick-bypass
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubturkios/cve-2026-32699-facturascripts-nick-bypass

cve-2026-32699-facturascripts-nick-bypass

Share

Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the unvalidated nick parameter via proxy interception. Patched but unpublished CVE.

View Repository
336 months agoNot yet reviewed

CVE-2026-32699 - FacturaScripts EditUser Nick Parameter Broken Access Control

CVSS Score CWE-862 OWASP A01

Description

Summary

The application fails to validate the nick parameter during a POST request to the EditUser controller. Although the UI prevents editing this field, a user can bypass this restriction using a proxy to rename any account (including the Administrator). This leads to Broken Access Control and potential Audit Log Corruption.

Details

The vulnerability exists in the user update logic. When a POST request is sent to /EditUser, the backend processes the nick form-data parameter without checking:

  • If it matches the original value
  • If the user has privilege to change a unique identifier intended to be immutable

PoC

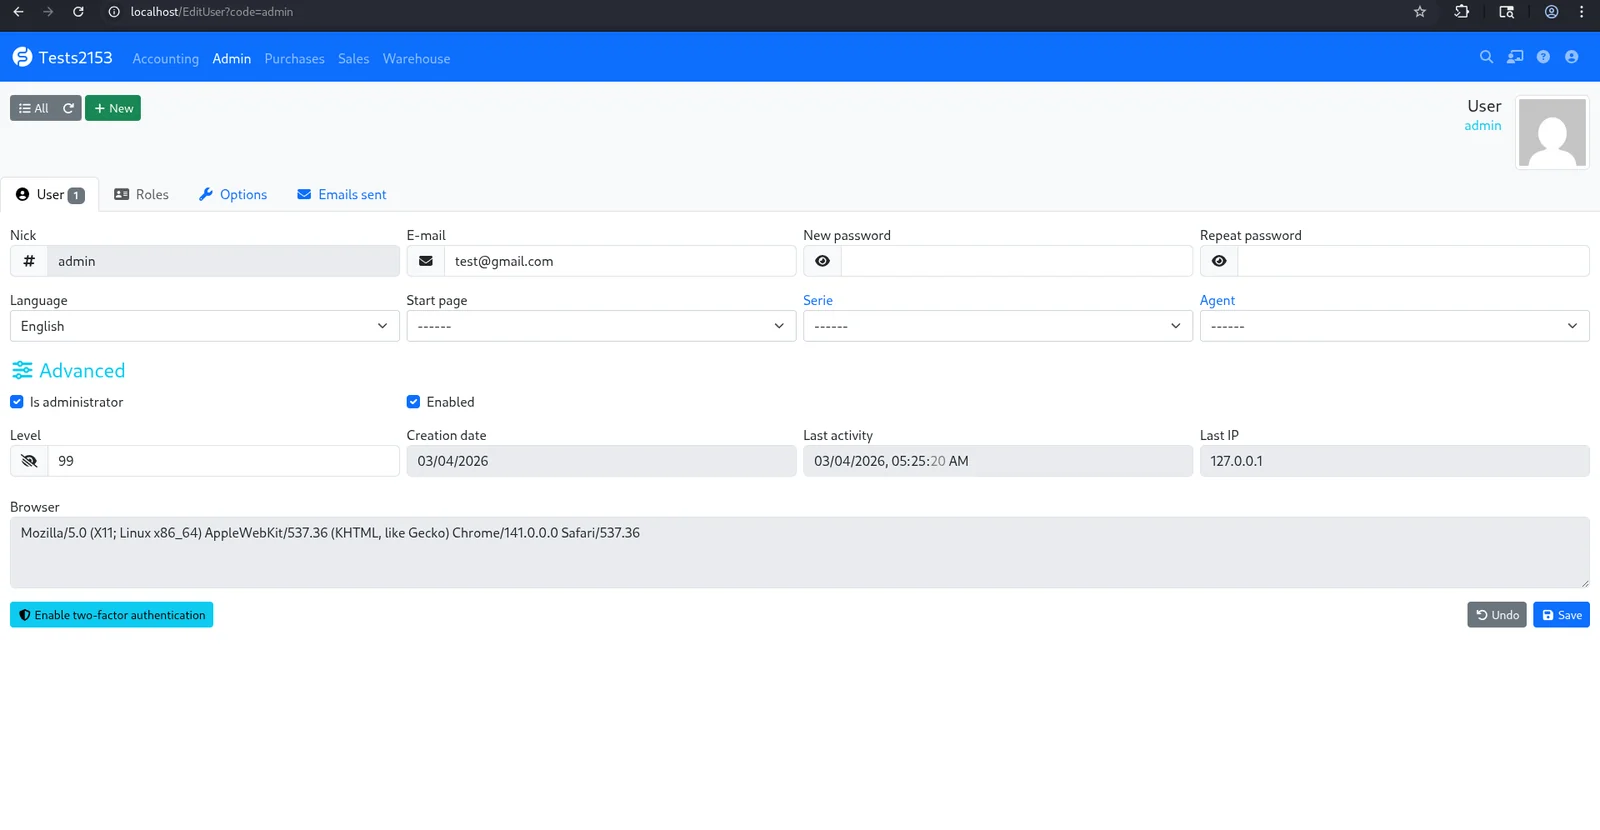
  1. Log in to the dashboard as any user (e.g. admin user)
  2. Go to your Profile by clicking your username/avatar in the top right
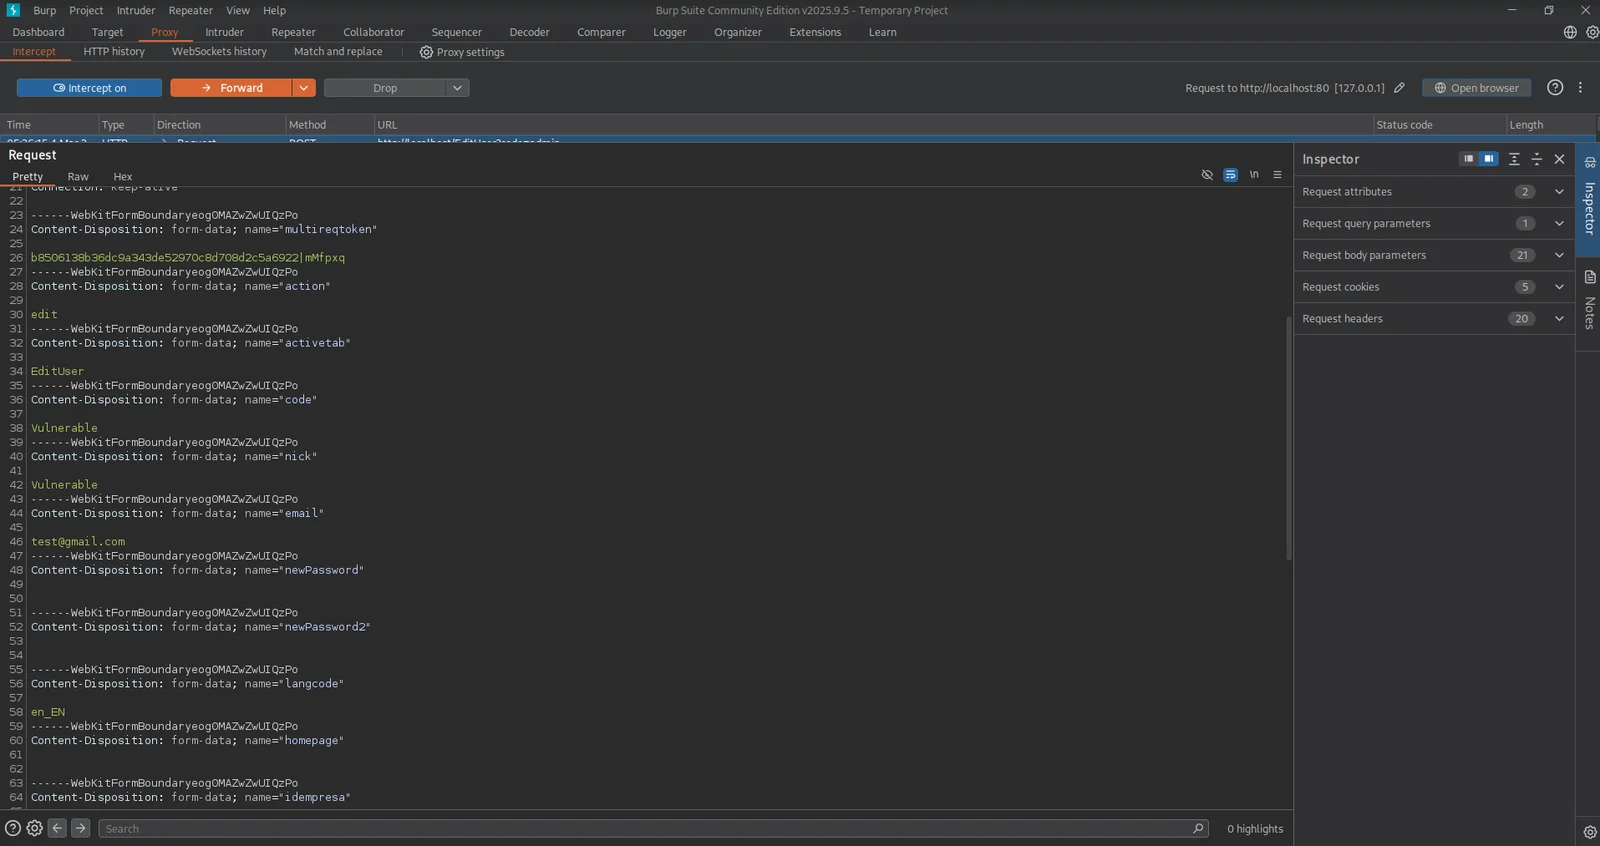
  3. Open Burp Suite and ensure Intercept is ON
  4. Click the Save button in the UI
  5. In Burp Suite, locate nick in the body:
1
  1. Change the value admin to Vulnerable (or any other string)
  2. Click Forward in Burp Suite

Result: The application logs the user out. Log back in using username Vulnerable + original password.

Impact

An attacker can effectively sabotage the system’s audit trail, performing malicious actions and then renaming their account to evade detection or frame other users. This breakdown in accountability facilitates identity impersonation and risks data corruption, as internal references to the original username become orphaned, undermining the overall integrity of the multi-user environment.
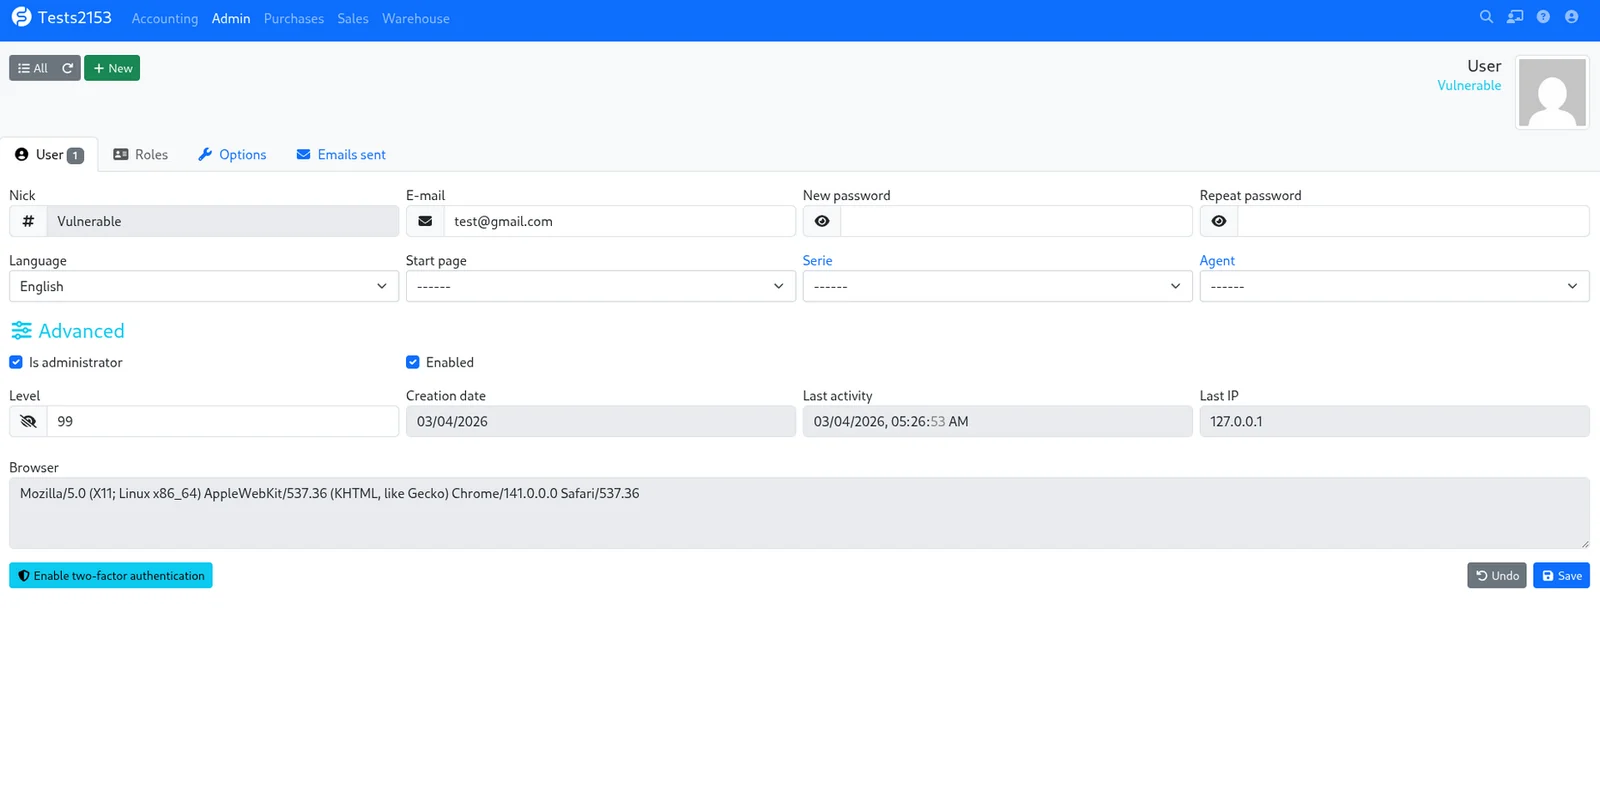
Result

Before

2

After

Screenshot_2026-04-26_02_29_09
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    930
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    354
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    349
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →