 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs for compromise.

Read-only precondition and exposure checker for the Citrix NetScaler ADC / NetScaler Gateway security bulletin CTX697096, covering CVE-2026-88771 through CVE-2026-88778, and for CTX697174, covering CVE-2026-88779 (the SAML crash attack), and for CTX697191, covering CVE-2026-107406 (SAML, remote code execution), and for CTX697263, covering PHP CVE-2026-109618 / CVE-2026-109619 ("php2shell", management GUI), and for CTX697305, covering 28 CVEs published on 12 November 2026.
License in plain words: Free for everyone - run it, change it, share it, use it in your company or for your customers' incident response. The only thing not allowed: using the code to build a competing tool. Questions or other needs: [email protected].
⚠️ CVE-2026-88771 and CVE-2026-88772 are exploited in the wild and are listed in the CISA KEV catalog. Upgrade now, and assume breach on internet-facing appliances.
🚨 NEW – CTX697305 (12 November): 28 CVEs, critical, every NetScaler affected. Install 14.1-73.58, 13.1-64.39, 14.1-73.58 FIPS or 13.1-37.293 FIPS/NDcPP. CTX697305 fixes 28 memory-safety flaws (up to CVSS 9.5). CVE-2026-120868 (packet processing, 9.3) applies to every deployment in the default configuration, and CVE-2026-107412 (9.5) to every Gateway and AAA vserver. The bulletin lists no workaround and no exploitation so far. The fixed builds also contain every earlier fix (CTX697096, CVE-2026-88779, CVE-2026-107406, php2shell), so they are the one build to install. Checker v1.19 checks your build against them, shows which of the 28 CVE preconditions your configuration meets, and returns VULNERABLE (exit code 2) on any build below the fix.
php2shell is fixed (27 October): install 14.1-73.49, 13.1-64.32, 14.1-73.49 FIPS or 13.1-37.286 FIPS/NDcPP. Citrix updated CTX697263 with the fixed builds. They also contain the CTX697096, CVE-2026-88779 and CVE-2026-107406 fixes. Checker v1.18 checks your build against them; on a build without the fix, a management GUI open to any source (or forwarded by a load-balancing vserver) is now VULNERABLE (exit code 2), and a restricted GUI is a
[CHECK].
php2shell (21 October): PHP CVE-2026-109618 and CVE-2026-109619 reach the NetScaler management GUI. Two pre-auth remote code execution flaws in PHP itself (CVSS 9.2 each), exploited since 17 October. NetScaler's management GUI runs PHP on the NSIP, on every SNIP with management access and on the cluster IP; Gateway and AAA are not affected. Citrix: all supported builds below the fixed builds above are affected; NetScaler Console and SVM are not. Until you have upgraded, restrict GUI and API access to admin hosts with ACLs (CTX228148). Checker v1.17 shows whether the PHP on the appliance has the fix, whether the management GUI is restricted, and hunting leads in the logs. Background: Remko Weijnen's firmware analysis.
CVE-2026-107406 (8 October): critical SAML flaw, remote code execution, upgrade AGAIN. CTX697191, CVSS 9.5: a SAML memory overflow leading to remote code execution or denial of service. On the builds already fixed for CTX697096 and CVE-2026-88779 (14.1-73.37 to 73.41, 13.1-64.23 to 64.28, 14.1-FIPS 73.37 to 73.41, 13.1-FIPS/NDcPP 37.279 to 37.282) you are affected when the appliance is a SAML IdP (
add authentication samlIdPProfile); on older builds when it is a SAML SP or IdP. Fixed in 14.1-73.46, 13.1-64.29, 14.1-73.46 FIPS and 13.1-37.283 FIPS/NDcPP. The bulletin lists no workaround. Secure Private Access hybrid deployments using NetScaler are affected too. Checker v1.16 checks your build and SAML config against these versions.
CVE-2026-88779 (3 October): the SAML attack now has a fix, and SAML appliances must upgrade again. The crafted SAML requests that crash patched NetScalers since 2 October are CVE-2026-88779 (CTX697174, CVSS 8.7, targeted attacks; on CISA's Known Exploited Vulnerabilities list since 4 October, US federal deadline 7 October). You are affected if your config has
add authentication samlActionoradd authentication samlIdPProfile. Fixed in 14.1-73.41, 13.1-64.28, 14.1-73.41 FIPS and 13.1-37.282 FIPS/NDcPP, so an appliance already upgraded for CTX697096 must be upgraded again. Until then, Citrix offers Global Deny List signatures through NetScaler Console, or a responder policy from Citrix Support. Checker v1.15 checks your build against these versions, shows whether a SAML mitigation policy covers every Gateway/AAA vserver, and reports injection attempts from 2 October until the CVE-2026-88779 fix as "may have run".
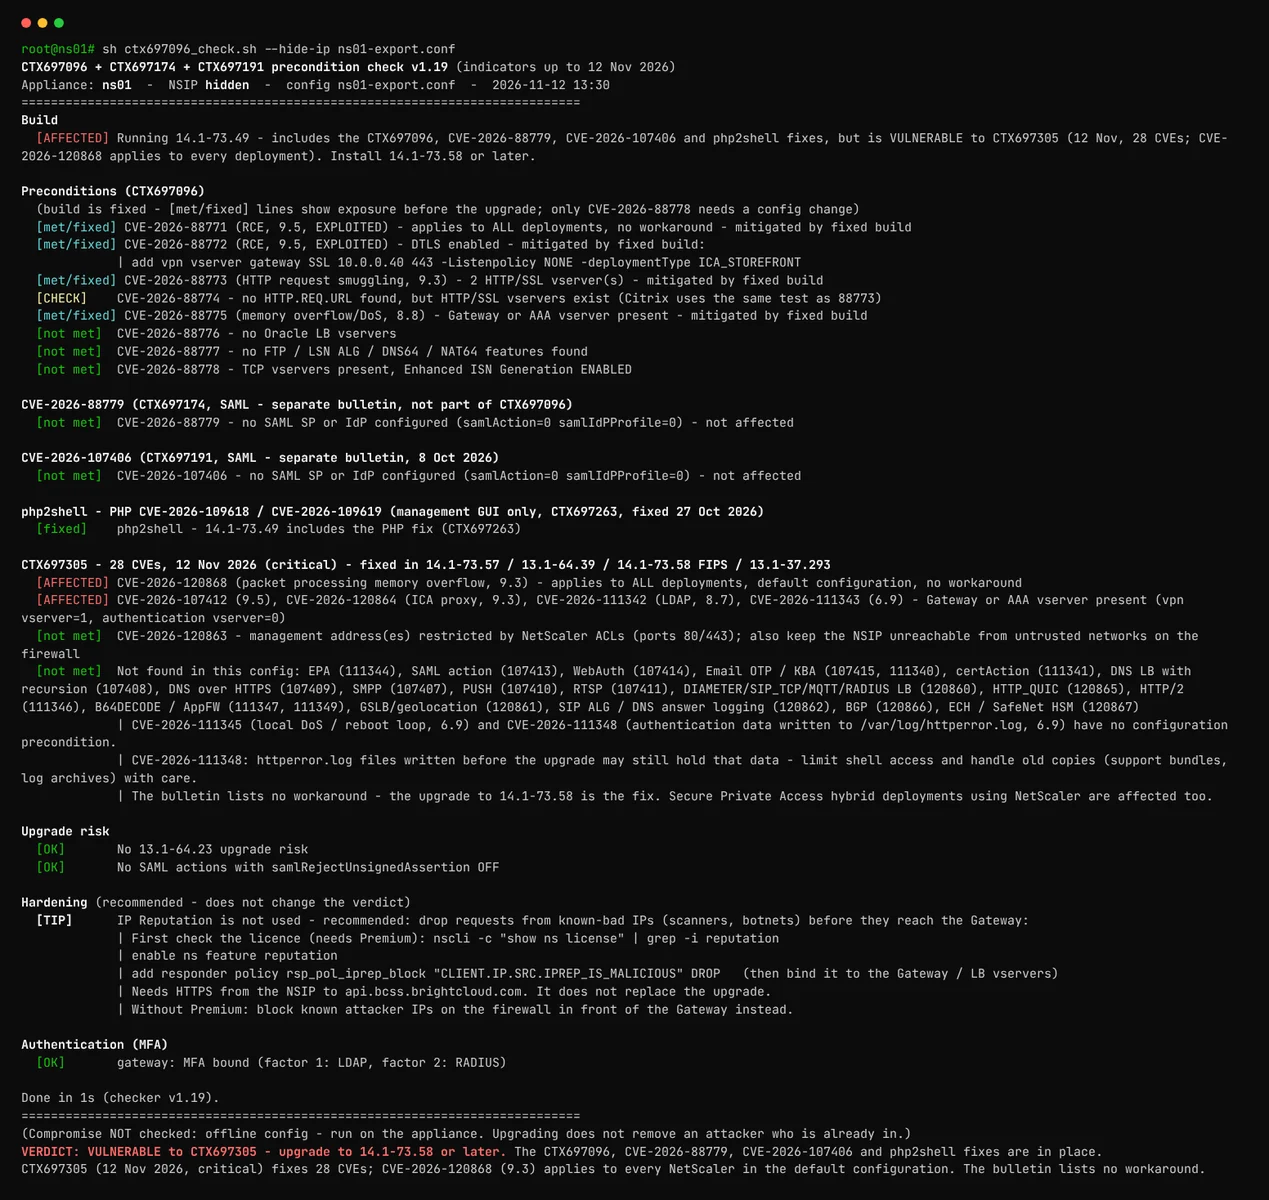
A clean run on a fixed lab appliance, shortened ("..."). The commands are under Usage; example output for other results is under Example output.
❤️ New: you can now support this project. The checker is free and stays free – if it saved you time, a voluntary contribution is appreciated.
It answers four questions for each NetScaler:
For background, a timeline and step-by-step remediation, see the accompanying blog post: CVE-2026-88771 through CVE-2026-88778 – what you should know and how to fix your NetScaler.
It is a single POSIX shell script with no dependencies. It runs on the appliance itself or against an exported ns.conf on any Linux, macOS or WSL machine.







