
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/teycir/honeypotscan
Static AnalysisVulnerability ScannersWeb SecurityPrivacyLearning & EducationAPI Security
GitHubteycir/honeypotscan

honeypotscan

Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13 specialized patterns. No API keys, no limits, 100% free. Built with Next.js 16 & Cloudflare Workers.

View Repository
10468 months agoNot yet reviewed
Share
Website

Support Development

If this project helps your work, support ongoing maintenance and new features.

ETH Donation Wallet
0x11282eE5726B3370c8B480e321b3B2aA13686582

Ethereum donation QR code

Scan the QR code or copy the wallet address above.
HoneypotScan Logo

🛡️ HoneypotScan

Check if a token is a scam before you buy

Free, fast, and accurate honeypot detection for Ethereum, Polygon, and Arbitrum smart contracts.

Version License Next.js React


🍯 What Are Honeypot Tokens?

We hunt honeypots. A honeypot token is a malicious smart contract designed to steal your money. It lets you buy tokens freely, but when you try to sell—your transaction fails. Your funds are trapped forever.

How Honeypots Work

Scammers embed hidden logic in the token's smart contract code:

  • Sell blockers - Only whitelisted addresses (the scammer) can sell
  • Hidden taxes - 95-100% sell tax drains your tokens
  • tx.origin tricks - Contract checks if you're the original buyer and blocks resale
  • Dynamic blacklists - Your address gets blacklisted after buying

The Risks

  • 💸 Total loss of funds - Once trapped, there's no way out
  • 🎭 Fake legitimacy - Honeypots often mimic real projects with copied websites and social media
  • ⚡ Speed - Scammers launch, pump, and abandon tokens within hours
  • 📈 Rising threat - Thousands of new honeypot tokens are deployed daily

⚠️ Important: This Is NOT a Full Security Audit

HoneypotScan is specialized for honeypot detection only. We do not scan for:

  • Reentrancy vulnerabilities
  • Flash loan exploits
  • Ownership/admin risks
  • Liquidity rug pulls
  • Other smart contract vulnerabilities

For comprehensive security audits, consult professional auditors. HoneypotScan answers one question: "Can I sell this token after I buy it?"

✨ Features

  • 🚀 Instant Results - Scan in 2 seconds
  • 🌐 Multi-chain - Ethereum, Polygon, Arbitrum
  • 💾 Smart Caching - 95%+ cache hit rate
  • 🔒 Privacy First - No tracking, no data collection
  • 💰 100% Free - No limits, no API keys needed
  • 🎯 High Accuracy - Pattern-based detection with confidence scoring
  • 📱 Mobile Friendly - Responsive design works on any device
  • 🛡️ Enterprise Security - CSP headers, CORS whitelist, input validation
  • 📚 Educational Tooltips - Learn about each detected pattern with severity levels and protection tips
  • 📋 Scan History - Track your last 10 scans locally for quick reference
  • 🔗 Share Results - Generate shareable URLs to send scan results to others
  • 💾 Export Data - Download scan results as JSON files for record-keeping

📚 Educational Features

Pattern Explanations

Every detected honeypot pattern comes with detailed educational content:

  • Severity Level - Critical, High, or Medium risk classification
  • How It Works - Plain-English explanation of the malicious technique
  • Protection Tips - Actionable advice to avoid similar scams

Example pattern explanation:

🚨 tx.origin in Require Statement (CRITICAL)

How it works: Transactions are blocked unless tx.origin matches 
a specific address. DEX sells always fail because the router 
becomes the msg.sender.

Protection: tx.origin checks in access control are a major red flag.

Scan History

Your last 10 scans are automatically saved locally:

  • Quick access to previously scanned contracts
  • No server storage - complete privacy
  • Includes token name, symbol, and scan timestamp
  • One-click re-scan or share functionality

Share & Export

Share Results via URL:

https://honeypotscan.com#result=eyJhIjoiMHguLi4ifQ==
  • Results encoded in URL hash (no server needed)
  • Share with friends, communities, or social media
  • Recipient sees full scan details instantly

Export as JSON:

{
  "scanner": "HoneypotScan",
  "version": "1.0",
  "scannedAt": "2026-02-01T12:00:00Z",
  "result": {
    "address": "0x...",
    "isHoneypot": true,
    "confidence": 95,
    "patterns": [...]
  }
}

Copy as Text:

🔍 HoneypotScan Result
════════════════════════════════════════
Token: Scam Token (SCAM)
Address: 0x...
Chain: Ethereum

Status: 🚨 HONEYPOT DETECTED
Confidence: 95%

⚠️ Patterns Found (3):
  • tx_origin_require (line 123)
  • hidden_sell_tax (line 456)
  • transfer_whitelist_only (line 789)

🎯 Use Cases

  • Traders - Verify tokens before buying on DEXs like Uniswap or SushiSwap
  • Investors - Due diligence on new token launches and presales
  • Developers - Audit smart contracts for common honeypot patterns
  • Communities - Protect group members from scam tokens
  • Researchers - Analyze honeypot trends across different chains

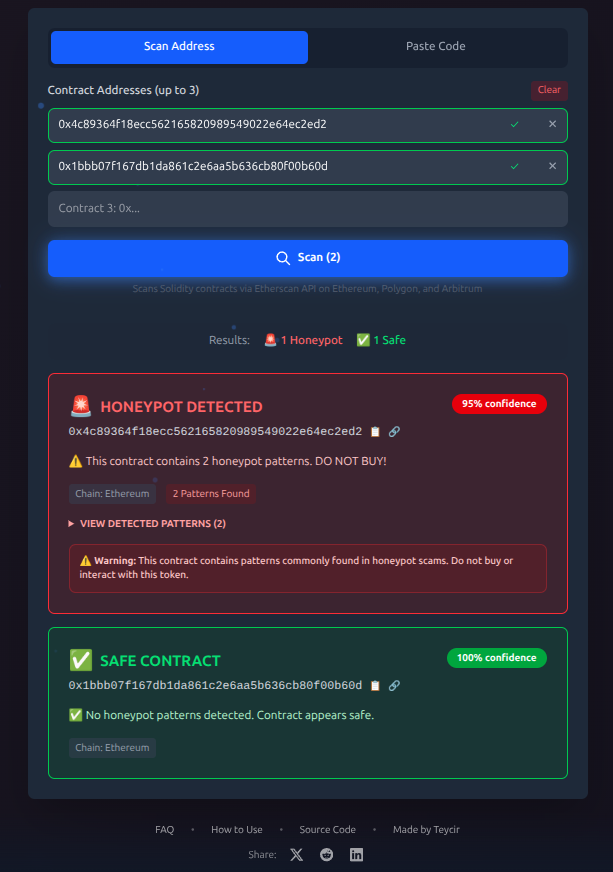
📸 How to Use

HoneypotScan offers two scanning modes for maximum flexibility:

🔍 Scan by Address

Paste any contract address to check if it's a honeypot. Works with Ethereum, Polygon, and Arbitrum addresses.

Scan by Contract Address

📝 Scan by Source Code

Already have the contract source code? Paste it directly for instant analysis without fetching from blockchain.

Scan by Source Code

🏗️ Architecture

Next.js 16 (App Router)
    ↓
Cloudflare Workers API
    ↓
Cloudflare KV (Cache)
    ↓
TypeScript Pattern Detector
    ↓
Etherscan API (6 keys with rotation)
    ↓
Ethereum, Polygon, and Arbitrum

🧬 Detection Algorithm

HoneypotScan uses advanced static analysis to detect malicious patterns in smart contract source code. Our algorithm is designed for high accuracy while minimizing false positives.

How It Works

1. Input Validation
   └─> EIP-55 checksum validation (keccak256)
   └─> Format verification (0x + 40 hex chars)
   └─> Chain detection (Ethereum/Polygon/Arbitrum)

2. Contract Source Retrieval
   └─> Fetch from Etherscan API
   └─> 6 API keys with intelligent rotation
   └─> 10-second timeout protection
   └─> Zod schema validation

3. Code Sanitization
   └─> Remove comments and whitespace
   └─> Normalize line endings
   └─> Verify Solidity structure
   └─> Size validation (50 chars - 2MB)

4. Pattern Matching
   └─> Run 13 specialized regex patterns
   └─> Each pattern detects specific honeypot techniques
   └─> Record all matches

5. Confidence Scoring
   └─> ≥2 patterns = HONEYPOT (95% confidence)
   └─> 1 pattern = SUSPICIOUS (needs review)
   └─> 0 patterns = SAFE (100% confidence)

The 13 Detection Patterns

Our scanner detects 13 specialized honeypot patterns across 4 categories:

1️⃣ Core ERC20 Abuse (3 patterns)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →





