 tcbutler320/cve-2021-3441-check
CVE-2021-3441 CVE Check is a python script to search targets for indicators of compromise to CVE-2021-3441

A python threat intelligence tool for automating IoC discovery for CVE-2021-3441. Easily search targets for indicators of compromnise
                                            ________________
                                        _/_______________/|
                                        /___________/___//||    CVE-2021-3441 Check
                                        |===        |----| ||
                                        |           |   �| ||    Author: Tyler Butler
                                        |___________|   �| ||            @tbutler0x90
                                        | ||/.�---.||    | ||
                                        |-||/_____\||-.  | |�
                                        |_||==HP===||_|__|/
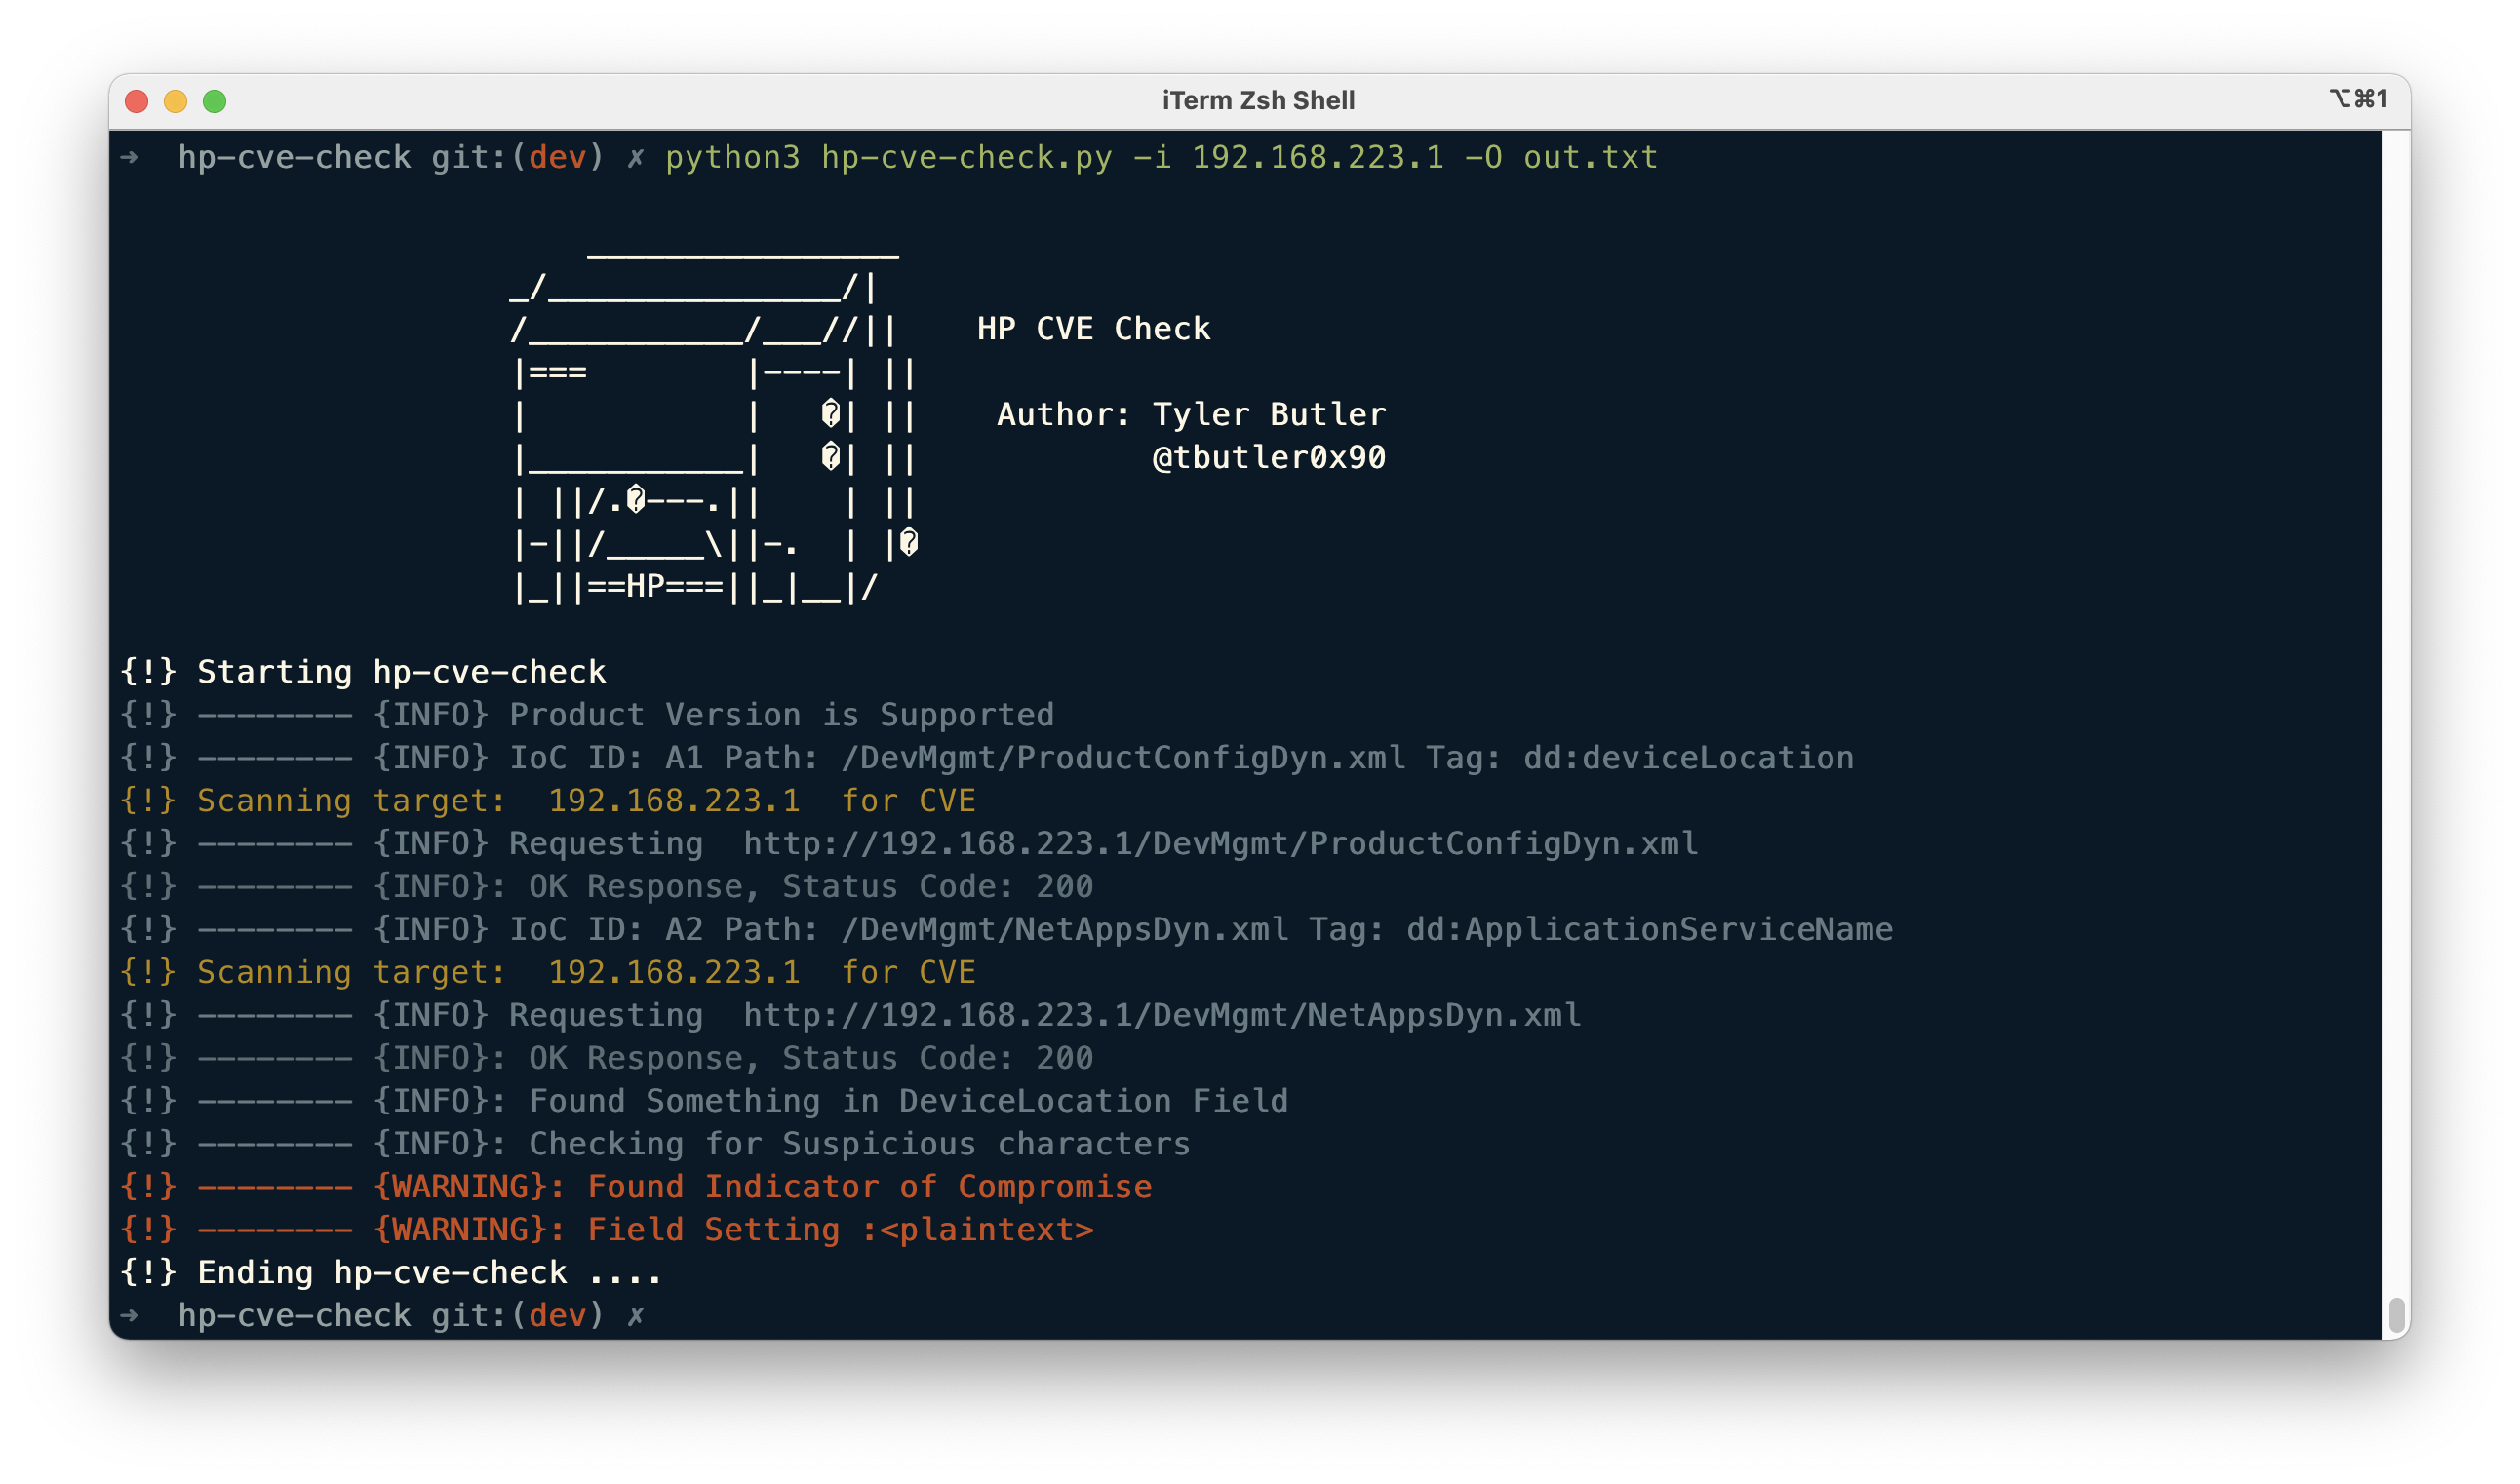
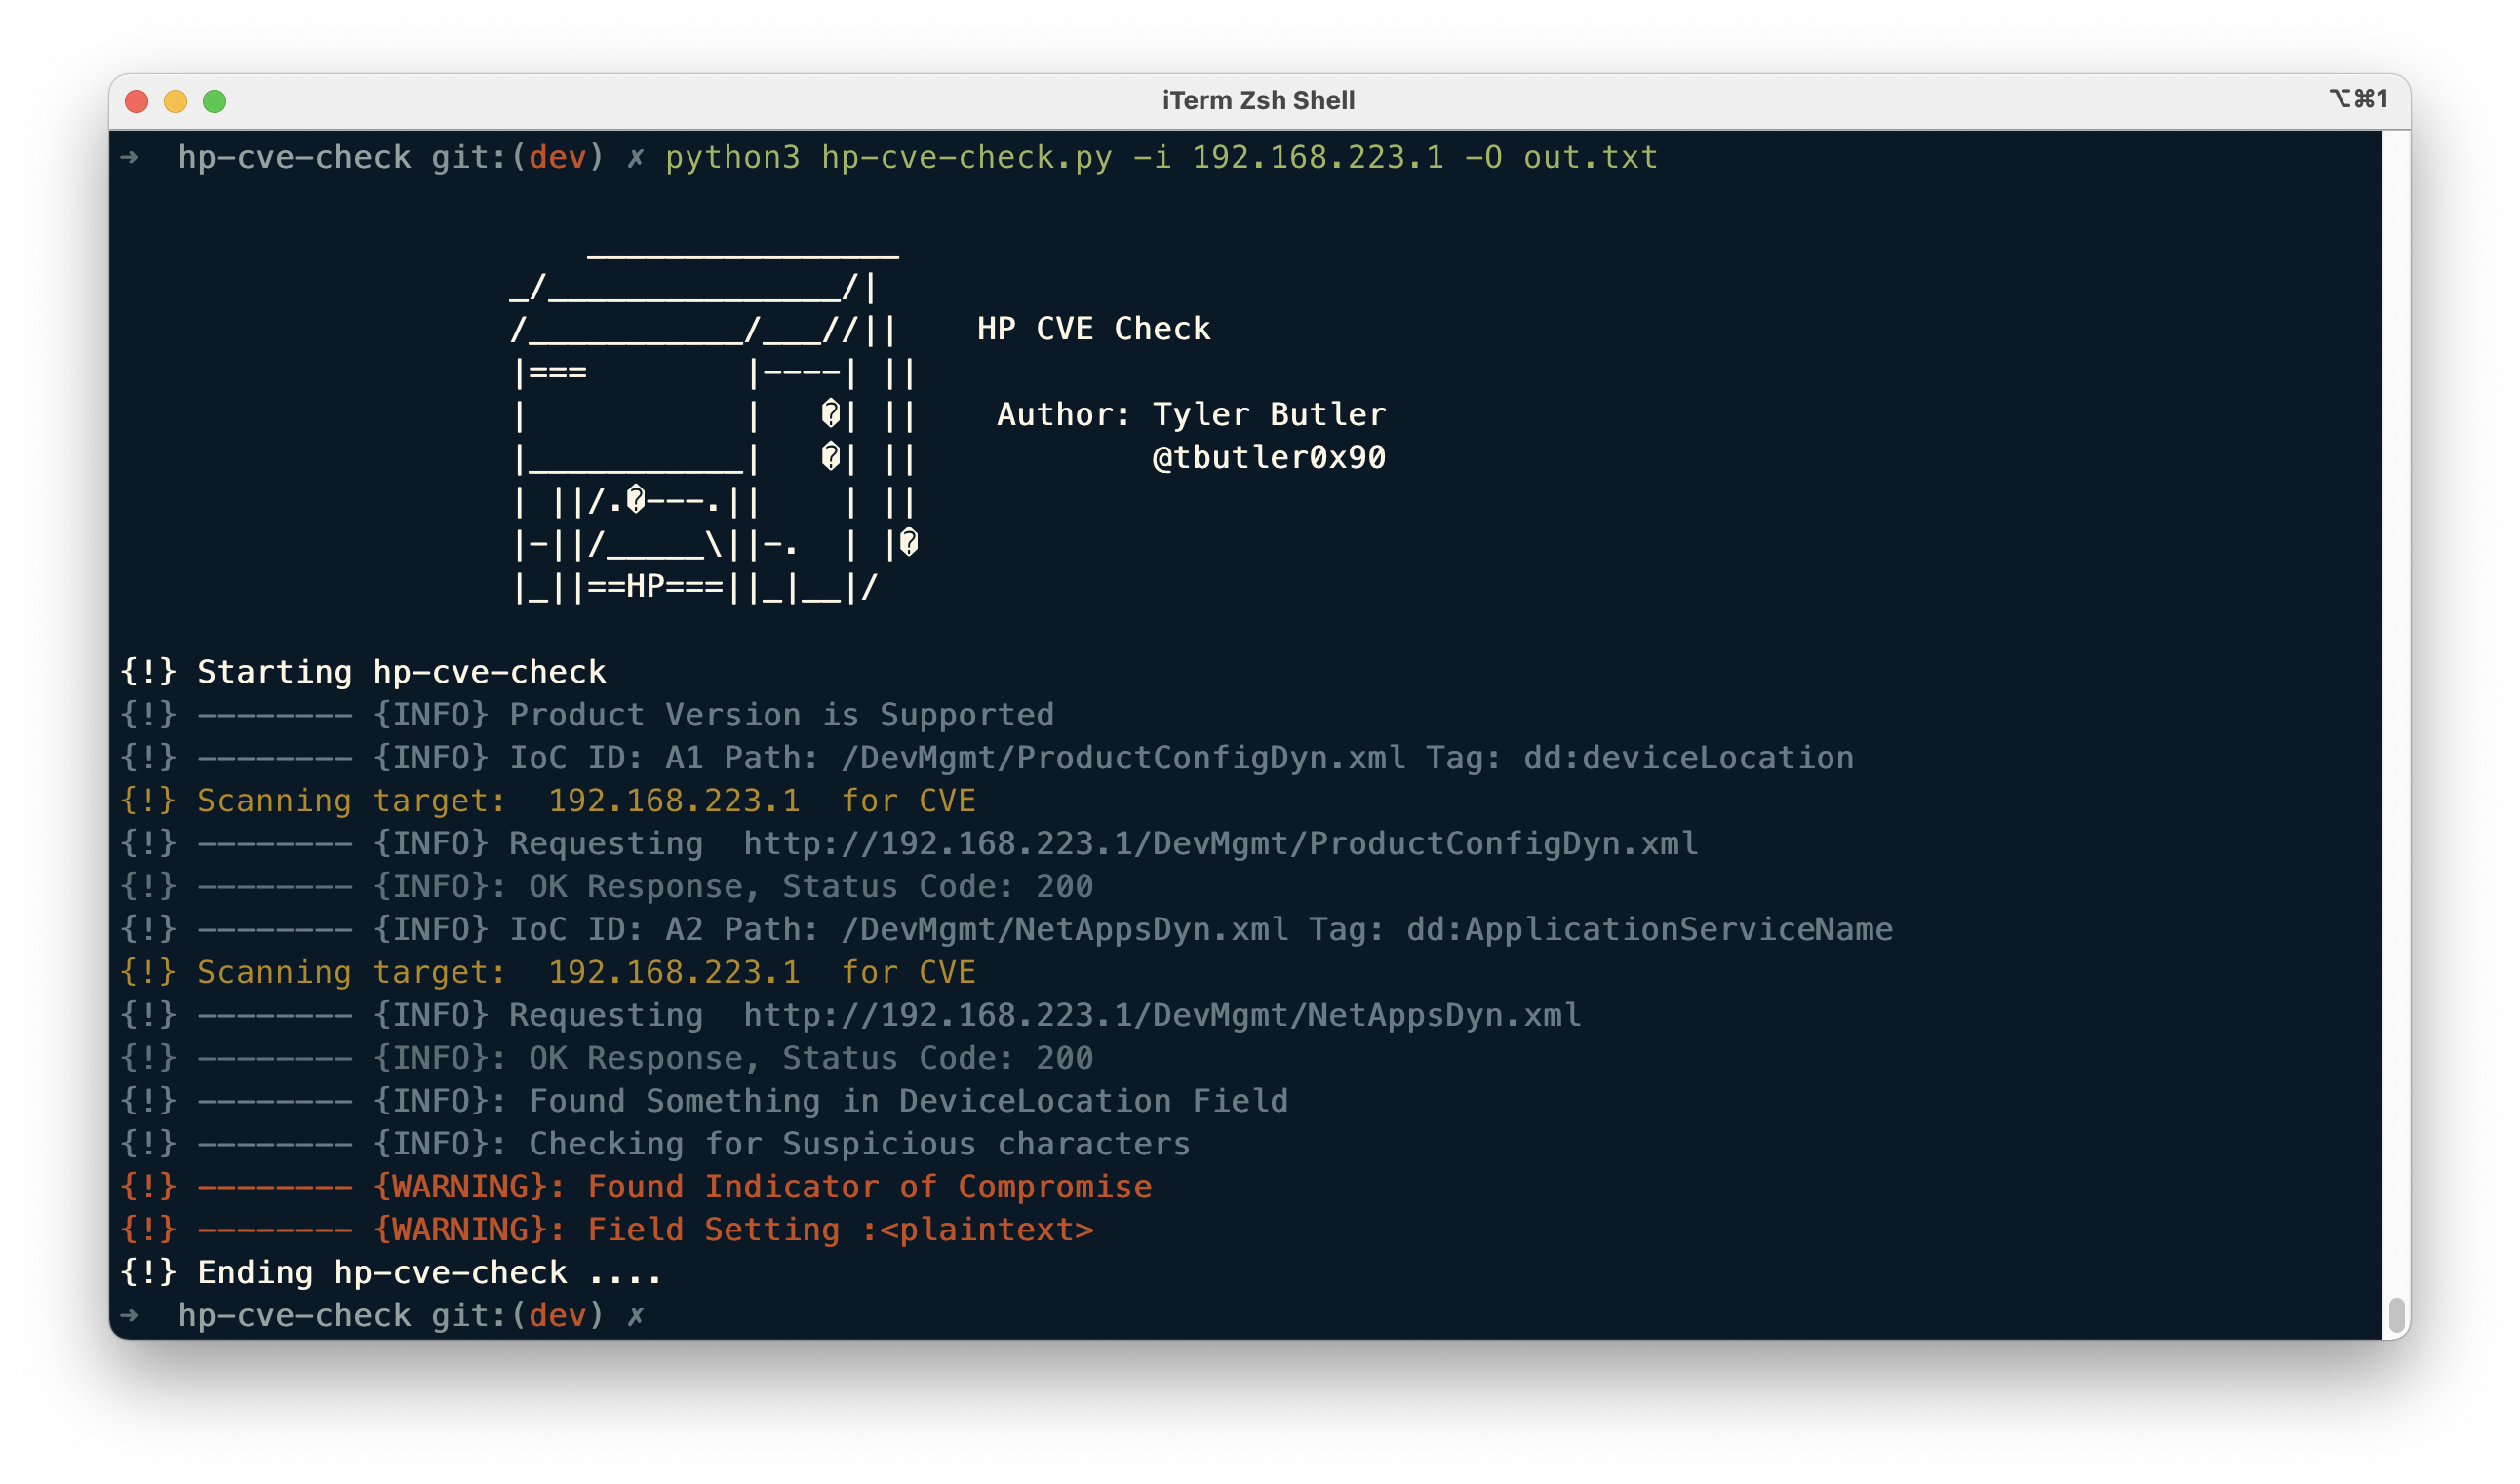
CVE-2021-3441 CVE Check is a python tool to search targets for indicators of compromise to CVE. The script gets product versions from the target's http response header. If the product version is vulnerable, and a module for the version has been created, the script requests the resource that could contain an exploit payload. Once the html entity that could contain an exploit is loaded, common XSS characters are searched for. The program alerts the user through the console if exploit payloads are found and can log findings to an output file.
python3 hp-cve-check.py -i [target ip] -O ./test/output.txt
➜  hp-cve-check git:(master) ✗ python3 hp-cve-check.py -i 192.168.223.1 -O output.txt

                        ________________
                    _/_______________/|
                    /___________/___//||    HP CVE Check
                    |===        |----| ||
                    |           |   �| ||    Author: Tyler Butler
                    |___________|   �| ||            @tbutler0x90
                    | ||/.�---.||    | ||
                    |-||/_____\||-.  | |�
                    |_||==HP===||_|__|/

{!} Starting hp-cve-check
{!} -------- {INFO} Product Version is Supported
{!} -------- {INFO} IoC ID: A1 Path: /DevMgmt/ProductConfigDyn.xml Tag: dd:deviceLocation
{!} Scanning target:  192.168.223.1  for CVE
{!} -------- {INFO} Requesting  http://192.168.223.1/DevMgmt/ProductConfigDyn.xml
{!} -------- {INFO}: OK Response, Status Code: 200
{!} -------- {INFO}: Found Something in DeviceLocation Field
{!} -------- {INFO}: Checking for Suspicious characters
{!} -------- {WARNING}: Found Indicator of Compromise
{!} -------- {WARNING}: Field Setting :<script>alert('XSS 2');</script>
{!} -------- {INFO} IoC ID: A2 Path: /DevMgmt/NetAppsDyn.xml Tag: dd:ApplicationServiceName
{!} Scanning target:  192.168.223.1  for CVE
{!} -------- {INFO} Requesting  http://192.168.223.1/DevMgmt/NetAppsDyn.xml
{!} -------- {INFO}: OK Response, Status Code: 200
{!} -------- {INFO}: Found Something in DeviceLocation Field
{!} -------- {INFO}: Checking for Suspicious characters
{!} -------- {OK}: No IoCs Detected
{!} -------- {OK}: Payload: test
{!} Ending hp-cve-check ....
python3 hp-cve-check.py -i [target list] -o [output file]
| Option | Description | Use |
|---|---|---|
| -i | target ip | -i 192.168.223.1 |
| -I | target file | -i targets.txt |
| -O | output file | -O output.txt |
IF IoC's are found they are logged to the output file in a greppable format, [target ip]:[payload]. When no payload objects are found, None is used.
➜  hp-cve-check git:(master) ✗ cat ./test/output.txt
192.168.223.1:<script>alert('XSS 2');</script>
192.168.223.1:None
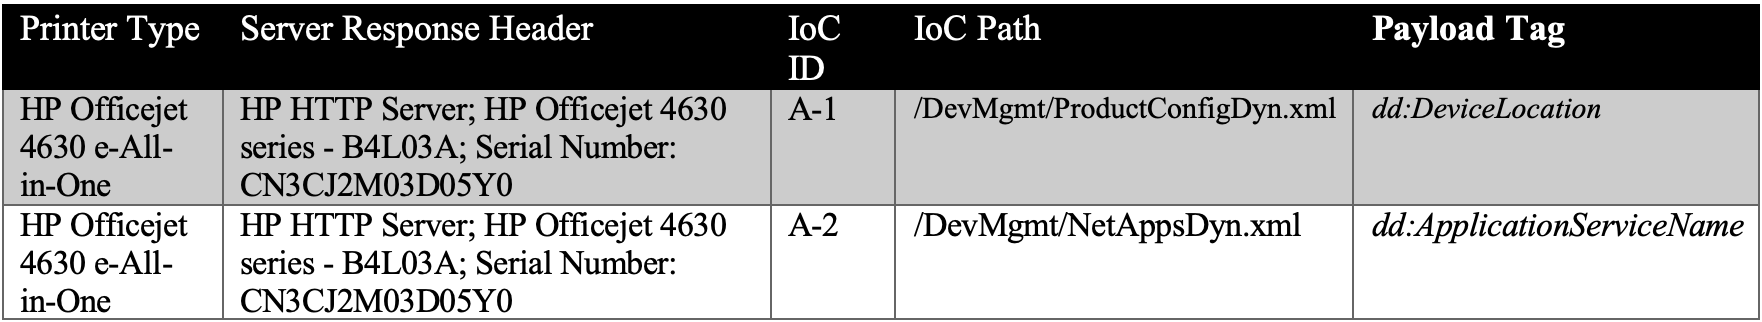
Because indicators of compromise are found in different resources depending on the product version, modules are used to store version specific configuration options. Modules are stored in the modules folder in yaml format. One module yml file is created for each supported version and contains the following options,
hp-officejet-4630.yml module
---
product: 'HP Officejet 4630'
path: '/DevMgmt/ProductConfigDyn.xml'
tag: 'dd:deviceLocation'
paths:
 - A1: '/DevMgmt/ProductConfigDyn.xml'
   A2: '/DevMgmt/NetAppsDyn.xml'
tags:
 - A1: 'dd:deviceLocation'
   A2: 'dd:ApplicationServiceName'
Paths and tags are broken down based on the IoC Discovery Table described in the vulnerability report, see below.
HP CVE Check is broken down into the core and util packages.
HP CVE Check Packages
➜  hp-cve-check git:(master) ✗ tree
├── lib
│   ├── core
│   │   ├── constants.py
│   │   ├── iocCheck.py
│   │   ├── module_parser.py
│   │   └── requests.py
│   └── utils
│       ├── printer.py
│       └── help.py
├── modules
│   └── hp-officejet-4630.yml






