Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/shivshantp/cve-2025-5777-trendmicro-apexcentral-rce
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlAuthenticationRed Teaming
GitHub
shivshantp/cve-2025-5777-trendmicro-apexcentral-rce

CVE-2025-5777-TrendMicro-ApexCentral-RCE

PoC for CVE-2025-5777 – Auth Bypass and RCE in Trend Micro Apex Central

View Repository
4311 year agoNot yet reviewed
Share

CVE Exploit-Status

🚨 CVE-2025-5777 – Trend Micro Apex Central Auth Bypass + RCE

🔎 Overview

CVE-2025-5777 is a critical authentication bypass and remote code execution (RCE) vulnerability discovered in Trend Micro Apex Central. It allows unauthenticated attackers to execute arbitrary commands on the system by abusing a flaw in the web-based management interface.

  • Severity: Critical
  • CVSS Score: 10.0
  • Attack Vector: Remote
  • Authentication Required: No
  • Affected Product: Trend Micro Apex Central
  • Affected Versions: Prior to Patch 2379
  • Status: Actively exploited in the wild

🧠 Technical Details

The vulnerability exists in the web interface of Trend Micro Apex Central. By sending a specially crafted HTTP request, an attacker can bypass authentication and trigger command execution with SYSTEM/root privileges.

📝 Note: This flaw impacts externally accessible deployments that have not applied the patch released in June 2025.


🧪 Proof of Concept (PoC)

🔸 HTTP Exploit Vector:

The PoC abuses a misconfigured authentication check in an internal endpoint, followed by injection of system commands.

📄 PoC Script:

cve-2025-5777-poc.py

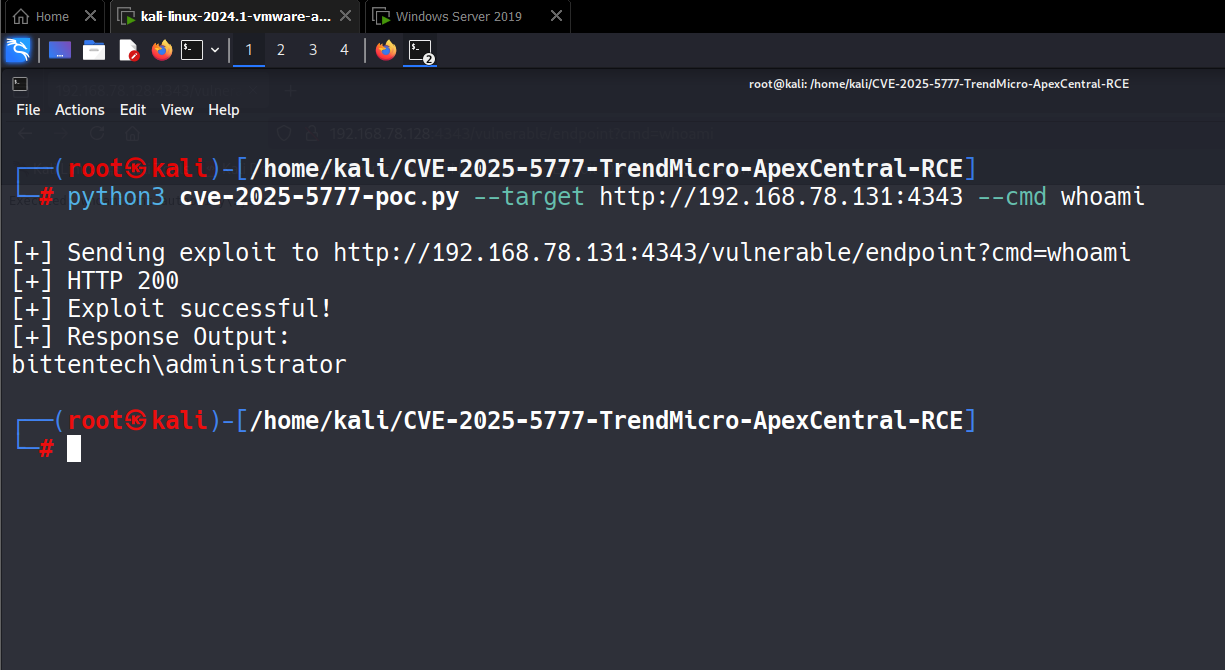
python3 cve-2025-5777-poc.py --target http://<target-ip> --cmd "whoami"

Replace <target-ip> with the vulnerable Apex Central instance address.

If successful, the command output (e.g., nt authority\system) will be returned in the HTTP response.


🛠️ Tools & Technologies Used

  • Python – scripting the exploit
  • Burp Suite – intercepting & modifying requests
  • Wireshark – packet analysis
  • Nmap – service enumeration
  • Trend Micro Apex Central – target application
  • GitHub – for publishing PoC & documentation

📝 Steps to Reproduce

  1. Deploy a vulnerable version of Trend Micro Apex Central (prior to Patch 2379).
  2. Run the exploit script with the target IP and desired command.
  3. Observe the output returned from the server (indicating code execution).
  4. Confirm system-level privileges via additional commands (whoami, id, etc.).

✅ Mitigation

  • Update Trend Micro Apex Central to Patch 2379 or later.

  • Restrict public access to the Apex Central web interface.

  • Monitor logs for unusual system command execution patterns.

  • Use network-layer controls to prevent unauthenticated access.


⚠️ Disclaimer:
This PoC is created strictly for educational and demonstration purposes.
Unauthorized use against systems you do not own or have permission to test is illegal.


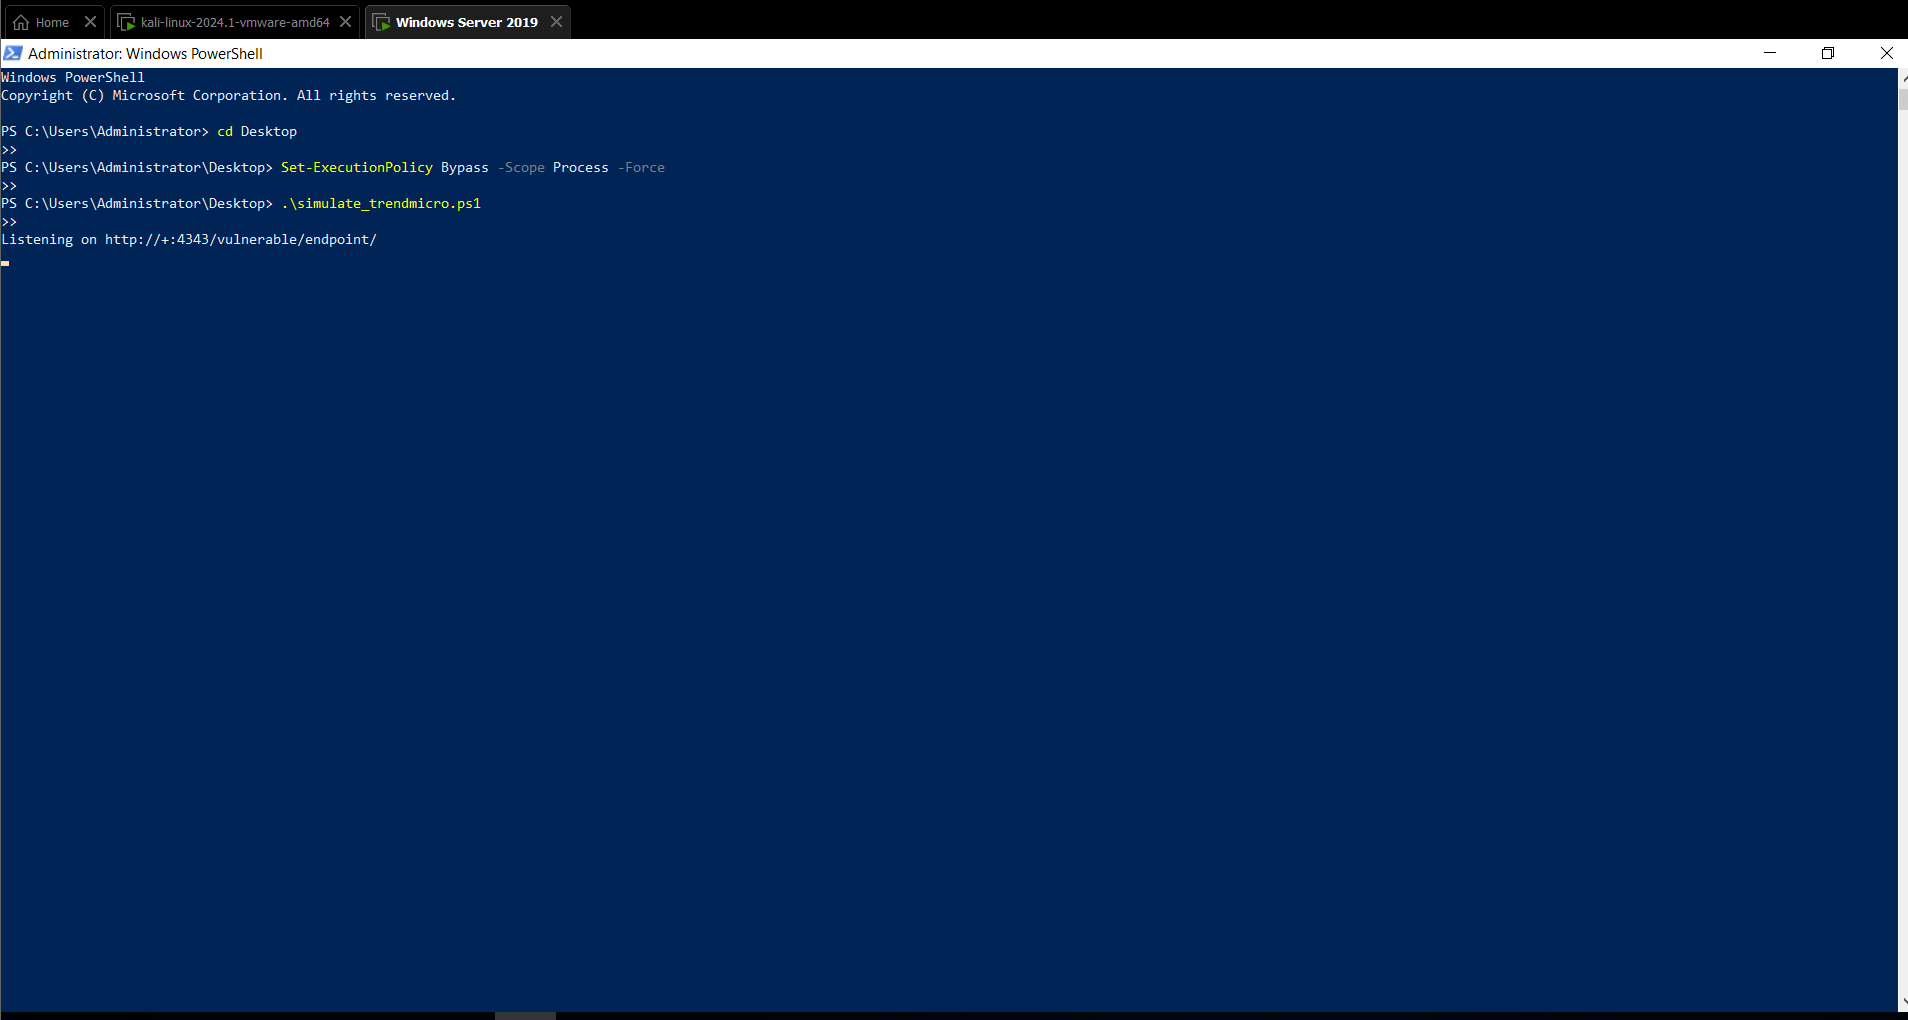
🎬 Live Demo (Simulated)

Simulated PowerShell Listener Output: Listener

Exploit Executed from Kali: PoC Output

👨‍💻 Author

Shivshant Patil
Certified Ethical Hacker (CEH v13)
B.Tech Computer Engineering Graduate
🔗 LinkedIn Profile
🔗 GitHub Profile

📚 References

  • 🔗 Trend Micro Security Advisory
  • 🔗 NVD Entry - CVE-2025-5777
  • 🔗 ThreatPost Coverage
  • 🔗 PacketStorm Security

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    968
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    347
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    319
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    297

Explore all tools

Browse our collection of tools

View all tools →
Download Tool