
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CorsMe — Cross Origin Resource Sharing MisConfiguration Scanner | Kitploit

Tools/GitHubGitHub/shivangx01b/corsme
Vulnerability ScannersWeb SecurityPenetration TestingMisconfiguration
GitHubshivangx01b/corsme

CorsMe

Cross Origin Resource Sharing MisConfiguration Scanner

View Repository
17026496 years agoReviewed by Kitploit
Share


What is CorsMe ?

A cors misconfiguration scanner tool based on golang with speed and precision in mind !

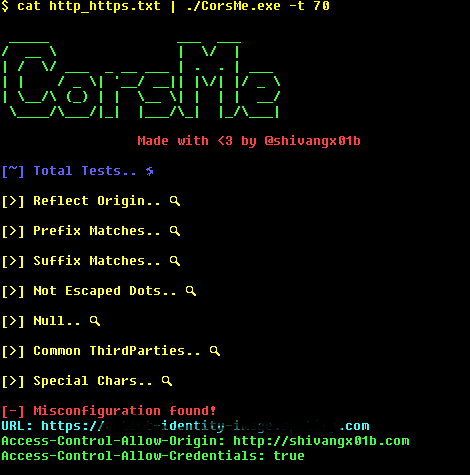
Misconfiguration type this scanner can check for

  • Reflect Origin checks
  • Prefix Match
  • Suffix Match
  • Not Esacped Dots
  • Null
  • ThirdParties (Like => github.io, repl.it etc.)
    • Taken from Chenjj's github repo
  • SpecialChars (Like => "}","(", etc.)
    • See more in Advanced CORS Exploitation Techniques

How to Install

$ go get -u -v github.com/shivangx01b/CorsMe

Usage

Single Url

echo "https://example.com" | ./CorsMe 

Multiple Url

cat http_https.txt | ./CorsMe -t 70

Allow wildcard .. Now if Access-Control-Allow-Origin is * it will be printed

cat http_https.txt | ./CorsMe -t 70 -wildcard

Add header if required

cat http_https.txt | ./CorsMe -t 70 -wildcard -header "Cookie: Session=12cbcx...."

Save output in a file

cat http_https.txt | ./CorsMe -t 70 -output audit.logs

Add another method if required

cat http_https.txt | ./CorsMe -t 70 -wildcard -header "Cookie: Session=12cbcx...." -method "POST"

Tip

subfinder -d hackerone.com -nW -silent | ./httprobe -c 70 -p 80,443,8080,8081,8089 | tee http_https.txt
cat http_https.txt | ./CorsMe -t 70


Screenshot

1414

Note:

  • Scanner stores the error results as "error_requests.txt"... which contains hosts which cannot be requested

Ideas for making this tool are taken from :

CORScanner

Corsy

cors-blimey

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





