Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
EntraGoat — A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges. | Kitploit
Tools/GitHubGitHub/semperis/entragoat
Privilege EscalationCTFPenetration TestingCloud SecurityIdentity & Access Management (IAM)AuthenticationMisconfigurationLearning & EducationRed TeamingLabs & Practice
GitHub
97494406 months agoReviewed by Kitploit
Share
semperis/entragoat

EntraGoat

A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges.

View Repository

EntraGoat - A Deliberately Vulnerable Entra ID Environment

EntraGoat is a deliberately vulnerable Microsoft Entra ID infrastructure for security professionals. Deploy real-world identity misconfigurations and privilege escalation paths in your own tenant, then practice exploiting them in a safe, black-box CTF format.

📖 Documentation  |  📝 Blog Posts


Quick Start

Prerequisites

  • Microsoft Entra ID test/trial tenant with Global Administrator
  • Microsoft Graph PowerShell SDK

Option A: PowerShell GUI (recommended, no Node.js)

git clone https://github.com/Semperis/EntraGoat && cd EntraGoat
Install-Module Microsoft.Graph -Scope CurrentUser -Force
.\Start-EntraGoat.ps1

Requires Windows (WPF). Works on PowerShell 5.1+ and 7+.
Zoom: Ctrl+Plus / Ctrl+Minus / Ctrl+0

Option B: Web UI

git clone https://github.com/Semperis/EntraGoat && cd EntraGoat
Install-Module Microsoft.Graph -Scope CurrentUser -Force
cd frontend && npm install && npm start

Open http://localhost:3000

Option C: Manual scripts

cd scenarios
.\EntraGoat-Scenario1-Setup.ps1

See docs/getting-started.md for detailed setup instructions.


Challenges

#NameDifficulty
1Misowned and Dangerous — Owner's Manual to Global AdminBeginner
2Graph Me the Crown (and Role)Beginner
3Group MemberShipwreck — Sailed into Admin WatersBeginner
4I (Eligibly) Own ThatIntermediate
5Department of Escalations - AU Ready for This?Advanced
6CBA (Certificate Bypass Authority) - Root Access GrantedAdvanced

Each scenario includes a setup script, cleanup script, solution walkthrough, and a hidden flag.


Screenshots

PowerShell GUI (recommended)

Home
PS GUI Home
Challenge
PS GUI Challenge

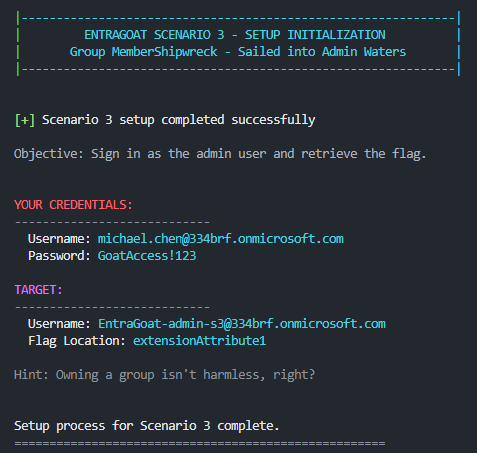
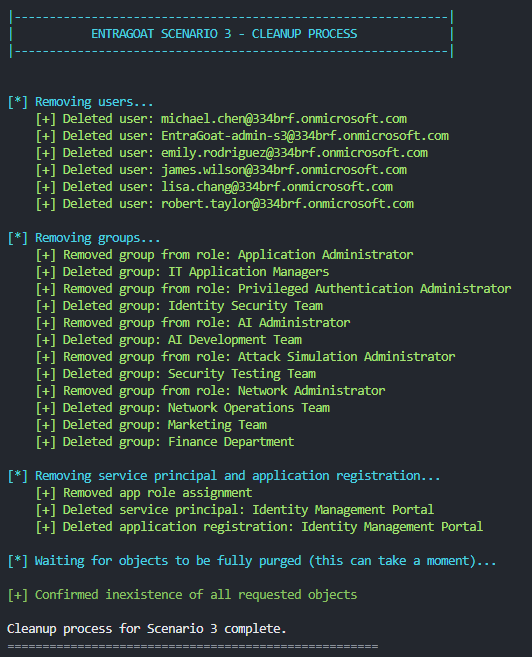
Terminal Output

SetupCleanup
Setup OutputCleanup Output

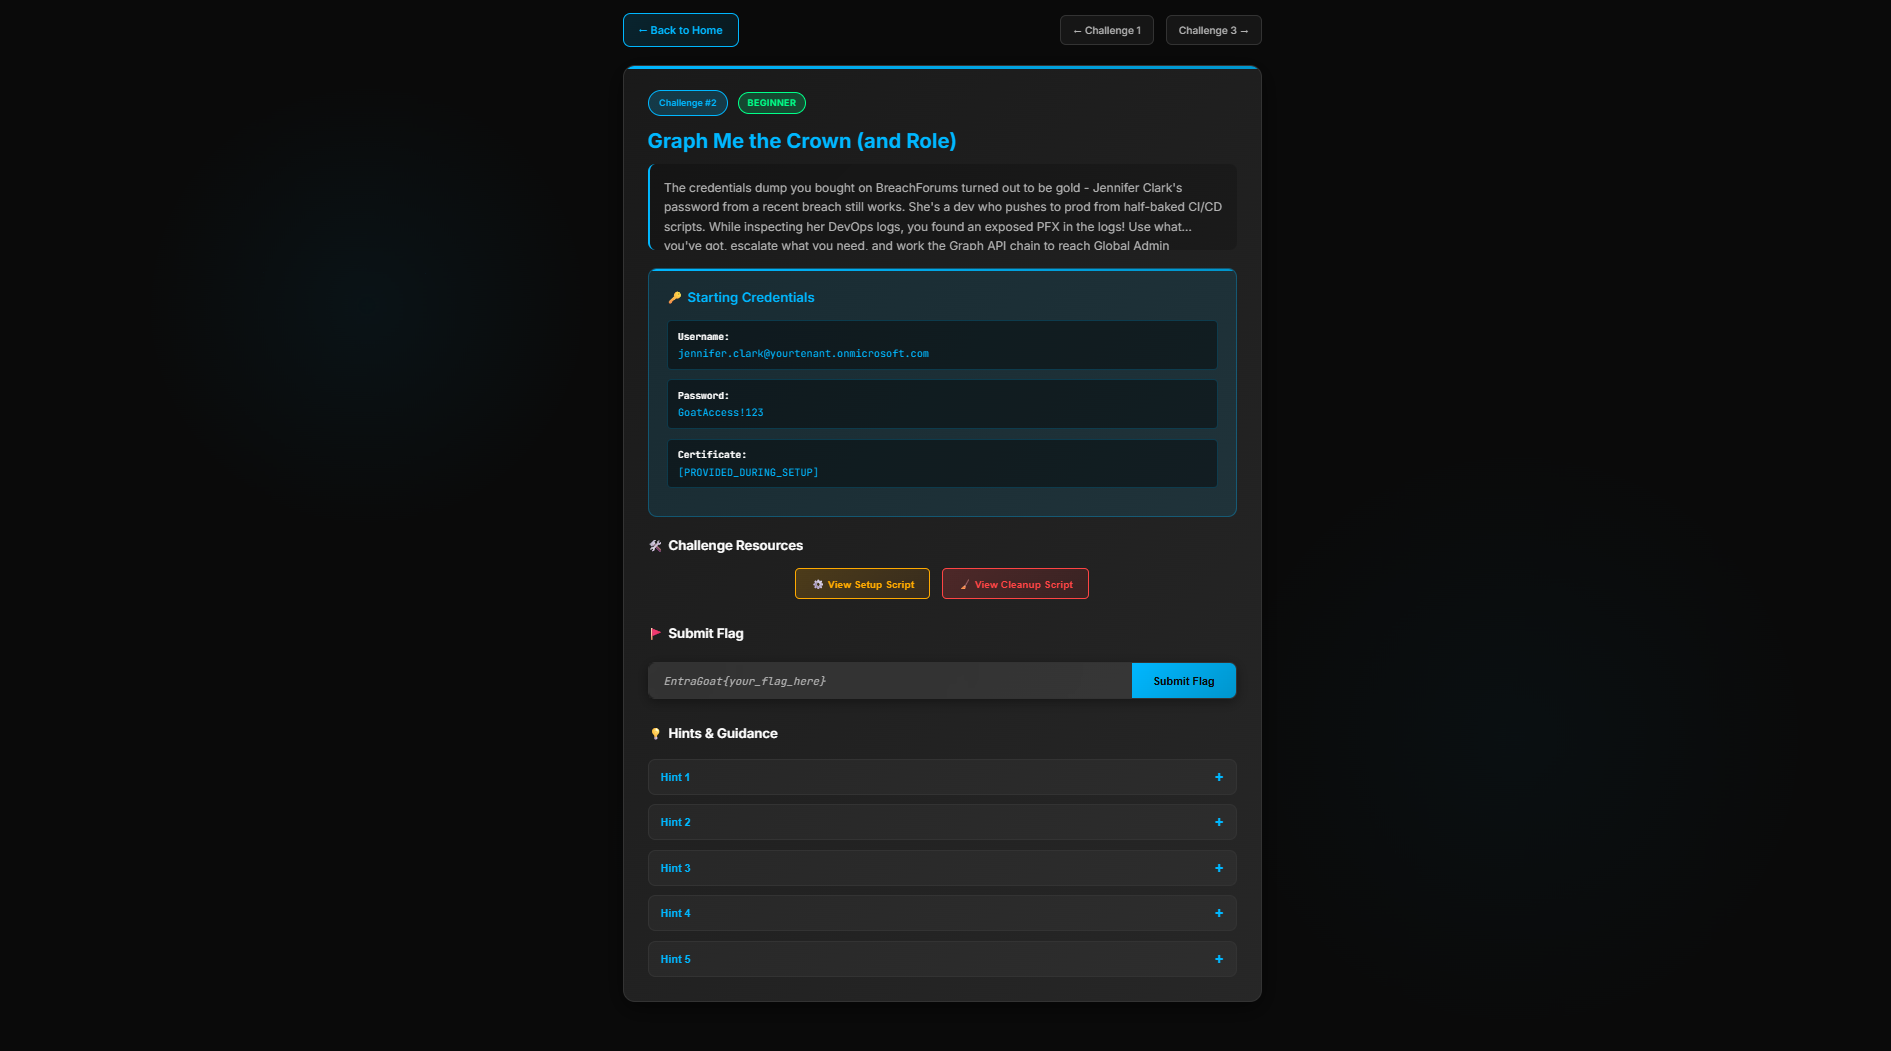
Web UI (alternative)

DashboardChallenge
Web DashboardWeb Challenge

Presented at

  • Black Hat USA 2025 — Arsenal
  • DEF CON 33 — Demo Labs
  • BSides Frankfurt 2025
  • SEC-T 0x11
  • Black Hat SecTor 2025 — Arsenal
  • Black Hat Europe 2025 — Arsenal
  • Black Hat Asia 2026 — Arsenal

Resources

  • What Is EntraGoat?
  • Getting Started with EntraGoat
  • Scenario 1: Service Principal Ownership Abuse
  • Scenario 2: Exploiting App-Only Graph Permissions
  • Scenario 6: Certificate-Based Authentication Abuse

⚠️ Disclaimer

For educational and authorized testing only. Use a dedicated test tenant. See LICENSE for full terms. The authors assume no liability for misuse.


Happy Hunting! — The EntraGoat Team

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →