
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-22457 — CVE-2025-22457: Python Exploit POC Scanner to Detect Ivanti Connect Secure RCE | Kitploit

Tools/GitHubGitHub/securekomodo/cve-2025-22457
ReconnaissanceVulnerability ScannersExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubsecurekomodo/cve-2025-22457

CVE-2025-22457

CVE-2025-22457: Python Exploit POC Scanner to Detect Ivanti Connect Secure RCE

View Repository
185471 year agoNot yet reviewed
Share

CVE-2025-22457

CVE-2025-22457: Python Exploit POC Scanner to Detect Ivanti Connect Secure RCE

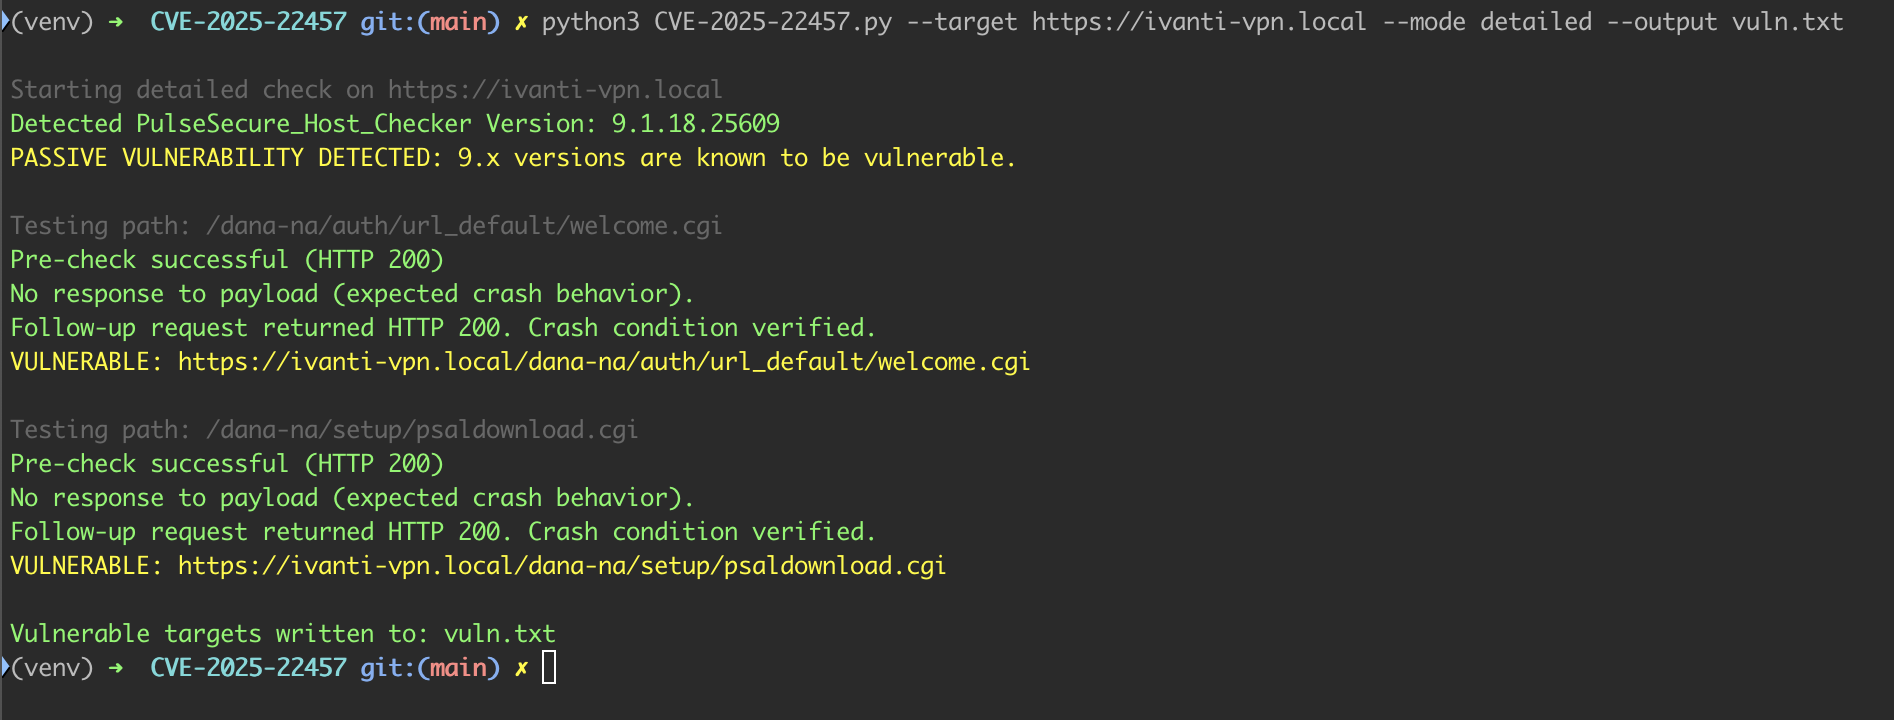
image

This script helps identify Ivanti Connect Secure, Policy Secure, or ZTA Gateways that may be vulnerable to CVE-2025-22457, a critical unauthenticated stack-based buffer overflow in the web process triggered via a crafted X-Forwarded-For header. It can also identify the remote targets version based on scraping the version information from the HTTP response.

Inspired by early work to build a Nuclei template, this script was created after discovering that Nuclei could not handle cases where no response is received from the target, which is essential to reliably detect this issue.

📖 Background

Original research and disclosure:

  • watchTowr Labs Blog

  • Redline Blog)

Shodan Query: http.favicon.hash:-485487831

4,260 Results as of April 9, 2025

When the payload is successful, the target system logs: ERROR31093: Program web recently failed.

This can be used to build log-based detections in addition to the scan.

🔍 How It Works

The script sends a long X-Forwarded-For header to vulnerable .cgi endpoints. It supports two modes:

Quick Mode (default)

  • Fingerprints the target and grabs the version
  • Determines if vulnerable based on version only, no attempt at triggering buffer overflow.

Detailed Mode

  • Sends a pre-check request and expects HTTP 200.
  • Sends the crash payload and expects no response.
  • Sends a follow-up request to ensure the crash wasn’t incidental.
  • Only if all three steps behave as expected is the system marked as vulnerable.

🛠 Usage

Install requirements:

pip install requests

Scan a single target

python cve_2025_22457_check.py --target https://example.com

Use detailed mode

python cve_2025_22457_check.py --target https://example.com --mode detailed

Scan a list of targets from file

python cve_2025_22457_check.py --input targets.txt --mode detailed

Output results to a file

python cve_2025_22457_check.py --input targets.txt --mode detailed --output vulnerable.txt

📌 How It Works

The default path /dana-na/auth/url_default/welcome.cgi can be changed by Ivanti administrators and may result in false negatives.

A secondary hardcoded path /dana-na/setup/psaldownload.cgi is included, which cannot be modified and still triggers the vulnerability. Any .cgi endpoint appears potentially affected.

✅ Example Output

Pre-check successful (HTTP 200)
No response to payload (expected crash behavior).
Follow-up request returned HTTP 200. Crash condition verified.
VULNERABLE: https://example.com/dana-na/setup/psaldownload.cgi

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    938
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    556
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    352
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    336
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    291

Explore all tools

Browse our collection of tools

View all tools →





