
 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic

This repository is a documentation of my adventures with Stratus Red Team - a tool for adversary emulation for the cloud.
Stratus Red Team is "Atomic Red Team for the cloud, allowing to emulate offensive attack techniques in a granular and self-contained manner.
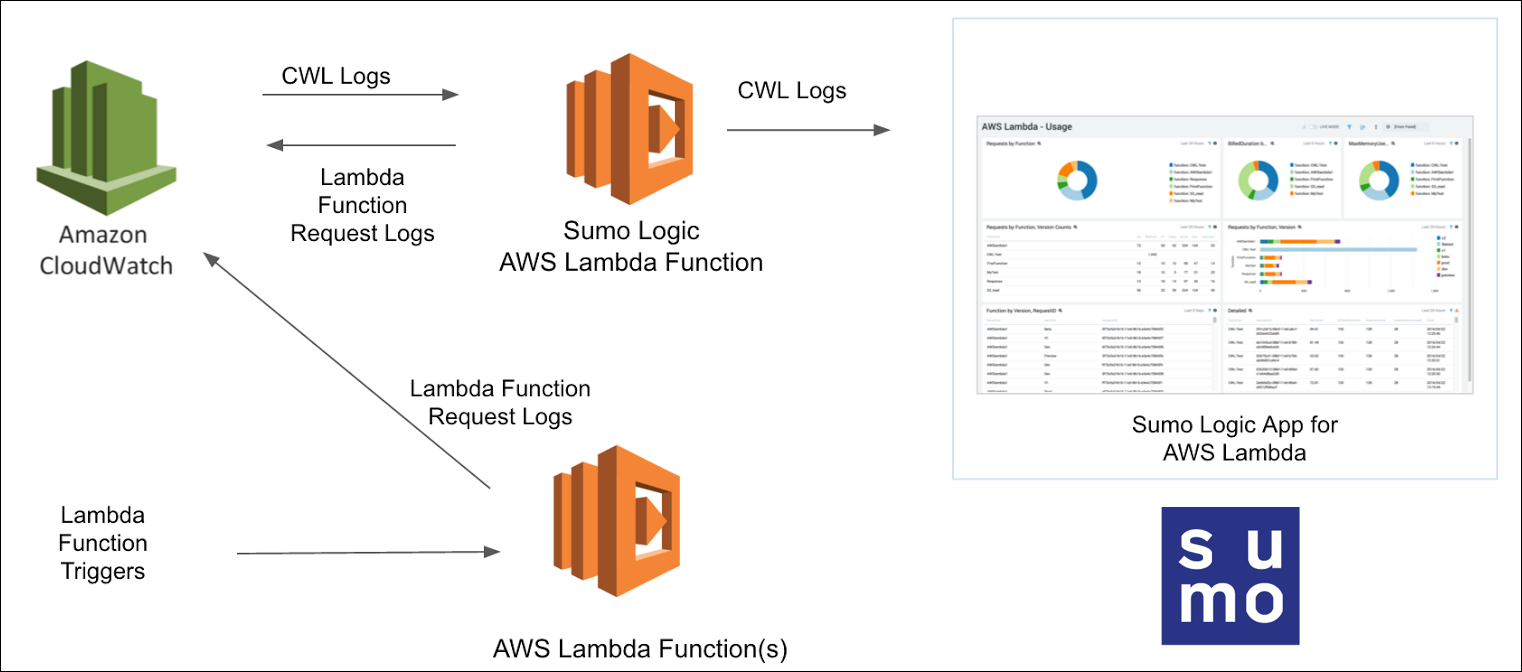
We run the attacks covered in the Stratus Red Team repository one by one on our AWS account. In order to monitor them, we will use CloudTrail and CloudWatch for logging and ingest these logs into SumoLogic for further analysis.
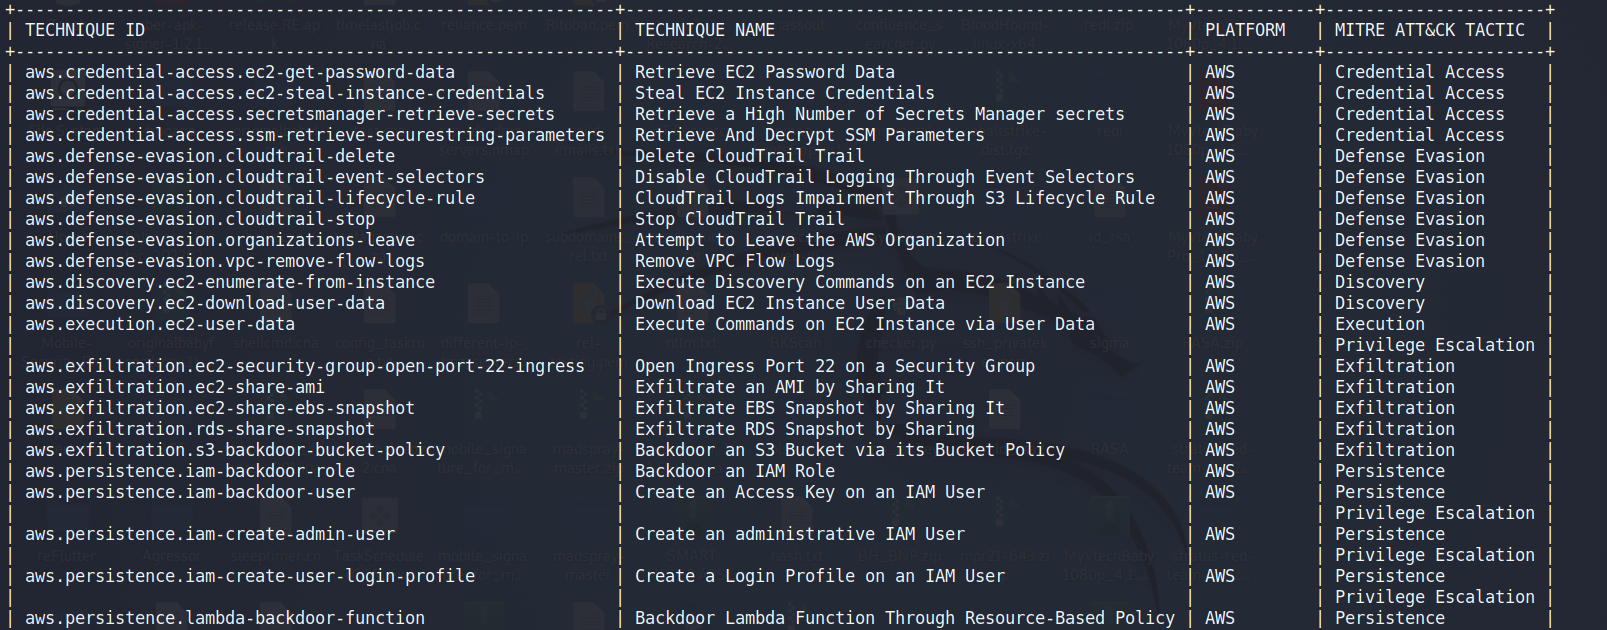
| Attack | Description | Link |
|---|---|---|
| aws.credential-access.ec2-get-password-data | Retrieve EC2 Password Data | Link |
| aws.credential-access.ec2-steal-instance-credentials | Steal EC2 Instance Credentials | Link |
| aws.credential-access.secretsmanager-retrieve-secrets | Retrieve a High Number of Secrets Manager secrets | Link |
| aws.credential-access.ssm-retrieve-securestring-parameters | Retrieve And Decrypt SSM Parameters | Link |
| aws.defense-evasion.cloudtrail-delete | Delete CloudTrail Trail | Link |
| aws.defense-evasion.cloudtrail-event-selectors | Disable CloudTrail Logging Through Event Selectors | Link |
| aws.defense-evasion.cloudtrail-lifecycle-rule | CloudTrail Logs Impairment Through S3 Lifecycle Rule | Link |
| aws.defense-evasion.cloudtrail-stop | Stop CloudTrail Trail | Link |
| aws.defense-evasion.organizations-leave | Attempt to Leave the AWS Organization | Link |
| aws.defense-evasion.vpc-remove-flow-logs | Remove VPC Flow Logs | Link |
| aws.discovery.ec2-enumerate-from-instance | Execute Discovery Commands on an EC2 Instance | Link |
| aws.exfiltration.ec2-security-group-open-port-22-ingress | Open Ingress Port 22 on a Security Group | Link |
| aws.exfiltration.ec2-share-ami | Exfiltrate an AMI by Sharing It | Link |
| aws.exfiltration.ec2-share-ebs-snapshot | Exfiltrate EBS Snapshot by Sharing It | Link |
| aws.exfiltration.rds-share-snapshot | Exfiltrate RDS Snapshot by Sharing | Link |
| aws.exfiltration.s3-backdoor-bucket-policy | Backdoor an S3 Bucket via its Bucket Policy | Link |
| aws.persistence.iam-backdoor-role | Backdoor an IAM Role | Link |
| aws.persistence.iam-backdoor-user | Create an Access Key on an IAM User | TBD |
| aws.persistence.iam-create-admin-user | Create an administrative IAM User | TBD |
| aws.persistence.iam-create-user-login-profile | Create a Login Profile on an IAM User | TBD |
| aws.persistence.lambda-backdoor-function | Backdoor Lambda Function Through Resource-Based Policy | TBD |






