
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/savio-code/fern-wifi-cracker
Password CrackingWi-Fi AuditingInformation GatheringWireless SecurityPenetration Testing
GitHubsavio-code/fern-wifi-cracker

fern-wifi-cracker

Automatically exported from code.google.com/p/fern-wifi-cracker

View Repository
1.6k454517 months agoReviewed by Kitploit
Share

Fern Wifi Cracker

Fern Wifi Cracker is a Wireless security auditing and attack software program written using the Python Programming Language and the Python Qt GUI library. The program is able to crack and recover WEP/WPA/WPS keys and also run other network based attacks on wireless or ethernet based networks

DISCLAIMER

Fern-Wifi-Cracker is designed to be used in testing and discovering flaws in one's own network with the aim of fixing the flaws detected, DO NOT use the program on networks for which you don't have permission, I am not responsible for whatever damage you cause by using this software.


Visit http://www.fern-pro.com for professional version
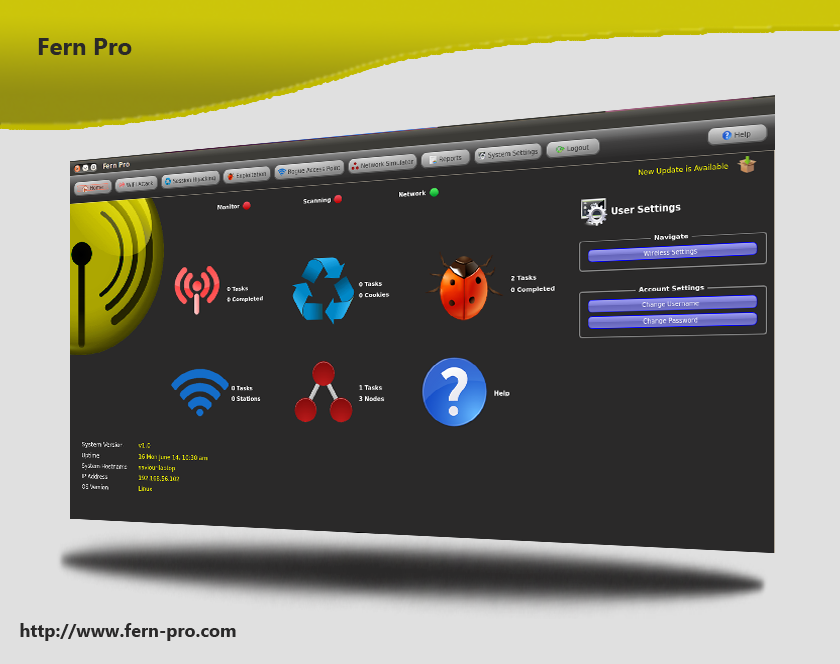
https://raw.githubusercontent.com/savio-code/savio-project-images/master/Fern/shadow_case.png

Supported operating systems

The Software runs on any Linux machine with the programs prerequisites. The program has been tested to work on the following Linux based operating systems:

  1. KDE/GNOME
  2. BackTrack Linux
  3. BackBox Linux

Prerequisites

The following dependencies can be installed using the Debian package installer command on Debian based systems using apt-get install <program> or otherwise downloaded and installed manually

  1. Aircrack-NG
  2. Python 3.x
  3. Python-Scapy
  4. Python Qt5
  5. Subversion
  6. Xterm
  7. Reaver (for WPS Attacks)
  8. Macchanger

Features

Fern Wifi Cracker currently supports the following features:

  1. WEP Cracking with Fragmentation,Chop-Chop, Caffe-Latte, Hirte, ARP Request Replay or WPS attack
  2. WPA/WPA2 Cracking with Dictionary or WPS based attacks
  3. Automatic saving of key in database on successful crack
  4. Automatic Access Point Attack System
  5. Session Hijacking (Passive and Ethernet Modes)
  6. Access Point MAC Address Geo Location Tracking
  7. Internal MITM Engine
  8. Bruteforce Attacks (HTTP,HTTPS,TELNET,FTP)
  9. Update Support

Running Program

root@host:~# python3 execute.py

The source code for the program can be fetched using the following command on terminal:

root@host:~# git clone https://github.com/savio-code/fern-wifi-cracker.git

Upgrading and Updating

Check for update button The Program automatically checks for updates each time the program is ran, if the program finds an update, it notifies user with the message New Update is Available, in other to update all you simply have to do is click on the update button When the button is clicked, allow to download update files until it displays the message Please Restart Application
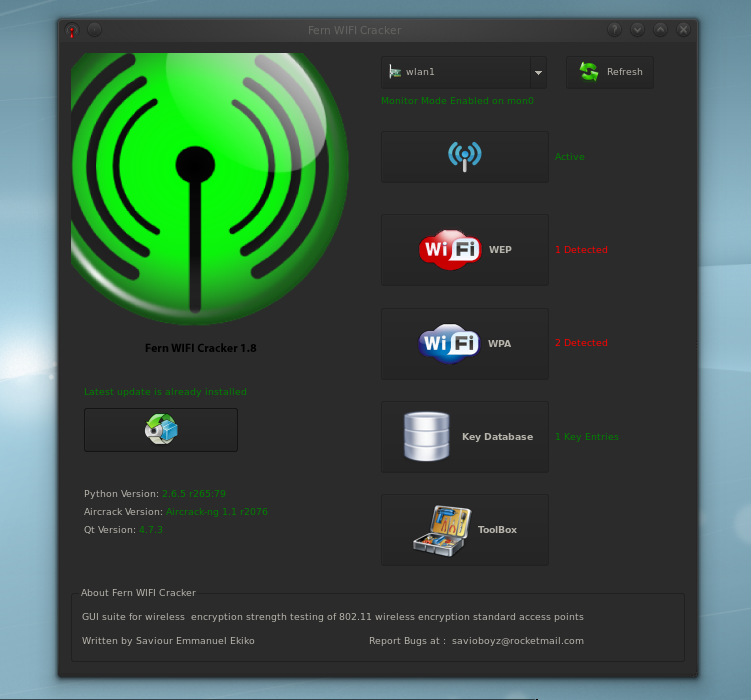
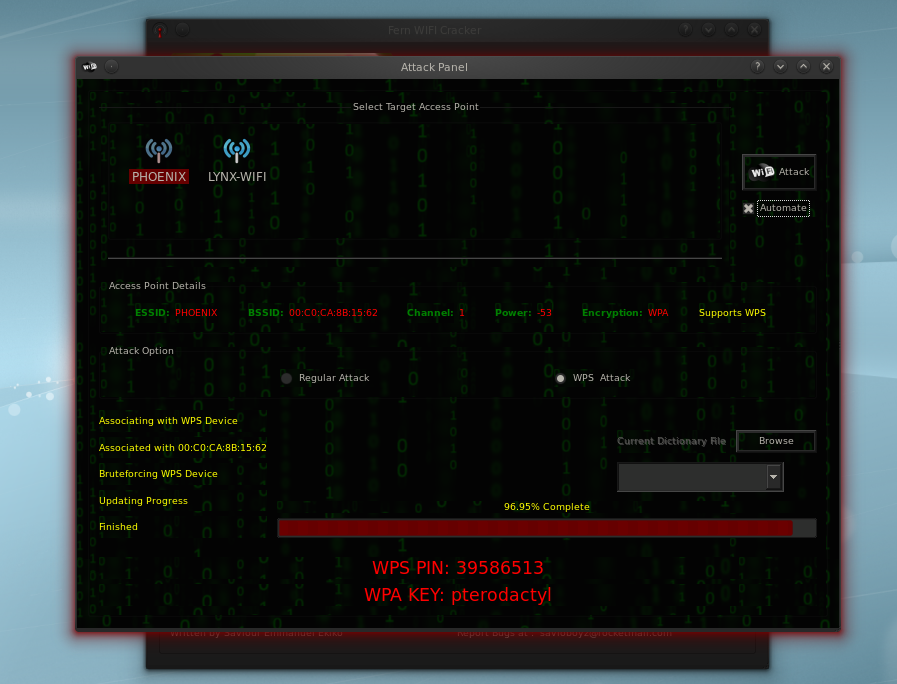
Screenshots

Main Window

Main window

WPA Cracking with WPS Attack

WPA attack

Cookie highjacking

Cookie hifhjacking

Other Projects

https://github.com/savio-code/ghost-phisher

https://github.com/savio-code/hexorbase

Supporting

If you like Fern Wifi Cracker and would like to support the development, please do so using bitcoin: 1AoBfNLfwDrw4ofZXZVm9YfeaFCXtG9k9B


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →




