Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CyberSec2026 — Educational lab environment for exploiting CVE-2022-22947 in Spring Cloud Gateway, with automated victim VM setup and attacker configuration scripts. | Kitploit
Tools/GitHubGitHub/sanderschepers1993/cybersec2026
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubsanderschepers1993/cybersec2026

CyberSec2026

Educational lab environment for exploiting CVE-2022-22947 in Spring Cloud Gateway, with automated victim VM setup and attacker configuration scripts.

View Repository
276 months agoNot yet reviewed
Share

Victim installation

Start your VM in VirtualBox

  1. Log in with:
  • username: osboxes
  • password: osboxes.org
  1. Open a terminal

  2. Test if you have a working internet connection.

ping 8.8.8.8
  • If your ping is not successful, check if your NAT interface is enabled.
  1. Update your OS
sudo apt-get update
  1. Install Git
sudo apt install -y git
  1. Clone your configuration files for Kali
git clone https://github.com/SanderSchepers1993/CyberSec2026.git
  1. Go to the newly cloned Victim directory
cd CyberSec2026/Victim
  1. Run the script 01_setup_server.sh with sudo privileges
sudo bash 01_setup_server.sh
  • If you encounter problems with openjdk-11-jdk, see TROUBLESHOOTING at the bottom of this README.
  1. Continue with the post-installation of the Attacker VM

[TROUBLESHOOTING]

Unable to locate package openjdk-11-jdk
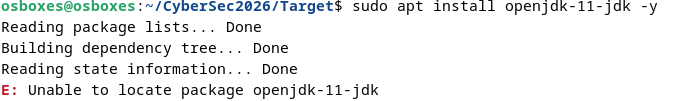
Unable to find openjdk11

  1. Run the script 02_setup_server_java17.sh with sudo privileges
sudo bash 02_setup_server_java17.sh
  1. Open your spring-gateway service with a text editor:
sudo nano /etc/systemd/system/spring-gateway.service
  1. Replace ExecStart with the following
ExecStart=/usr/bin/java --add-opens java.base/java.lang=ALL-UNNAMED -jar /opt/spring-gateway/target/vulnerable-gateway-1.0.0.jar
  • We are now setting up the environment with Java 17 instead of Java 11.
  • Java 17 blocks the execution of external Java libraries by default.
  • With the above command, you allow Java libraries outside the Java module to use reflection to look into java.lang.
  1. Restart the service
sudo systemctl daemon-reload
sudo systemctl restart spring-gateway.service
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →








