
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
TakeOver-v1 — Takeover script extracts CNAME record of all subdomains at once. TakeOver saves researcher time and increase the chance of finding subdomain takeover vulnerability. | Kitploit
Tools/GitHubGitHub/samhaxr/takeover-v1
Vulnerability AnalysisWeb SecuritySubdomain EnumerationDNS Analysis
GitHubsamhaxr/takeover-v1

TakeOver-v1

Takeover script extracts CNAME record of all subdomains at once. TakeOver saves researcher time and increase the chance of finding subdomain takeover vulnerability.

View Repository
10026553 years agoReviewed by Kitploit
Share

TakeOver-v1

What is Subdomain Takeover?

Subdomain Takeover is a type of vulnerability that arises when a subdomain points to an external service that has been deleted or is no longer in use. Common examples of these external services include Github, Heroku, Gitlab, and Tumblr. In this scenario, an attacker can exploit this vulnerability if the original owner fails to remove the DNS entry that points to the deleted service, allowing the attacker to takeover the subdomain by adding a CNAME file containing the subdomain name. This type of vulnerability can have significant security implications and requires careful attention to prevent exploitation.

Here is the command that checks CNAME record of a subdomain.

$dig CNAME apt.shopify.com --> apt.shopify.com.s3-website-us-east-1.amazonaws.com.

How Can Takeover script help bug bounty hunters?

Managing and securing large numbers of subdomains can be a challenging task for organizations. In order to effectively monitor subdomains for potential security risks, it is important to have a tool that can automate the process of checking CNAME records for each domain. The script in question takes a file name as input, and performs a series of actions to produce output that displays the CNAME record for each domain in the input file. This approach enables security professionals to easily manage and monitor a large number of subdomains, and can help to identify potential vulnerabilities more efficiently.

How can I recognise if the subdomain is vulnerable to subdomain takeover?

When a service is deleted, it is important to analyze the fingerprints that may be left behind when the DNS entry remains in place. In some cases, a vulnerable subdomain may display an error message when visited by an attacker, such as "There isn't a Github Pages site here." By carefully examining these error messages, security professionals can gain valuable insight into potential vulnerabilities that may exist within a domain or subdomain, and take steps to mitigate these risks. This type of analysis is essential for identifying and addressing security issues that may arise from improperly configured or abandoned services.

Alt text

Security researcher @edoverflow has listed all services and their fingerprints. For more detail visit https://github.com/EdOverflow/can-i-take-over-xyz
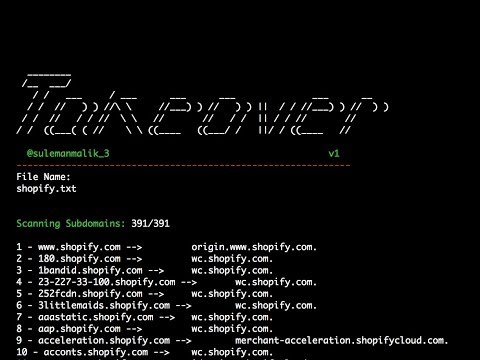

Youtube

Takeover-v1

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →





