

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
WinDefenderKiller — Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++) | Kitploit

Tools/GitHubGitHub/s12cybersecurity/windefenderkiller
Privilege EscalationExploitationIDS/IPS EvasionPost-ExploitationRed TeamingAdversarial Attack
GitHubs12cybersecurity/windefenderkiller

WinDefenderKiller

Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)

Share
View Repository
54975387 months agoReviewed by Kitploit

WinDefenderKiller

PermanentDisablefromRegistry

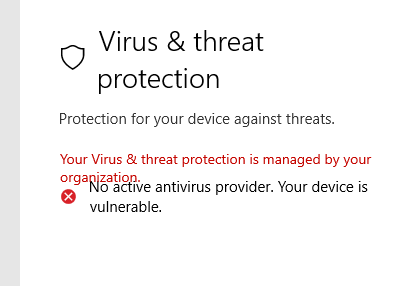
C++ Code for Permanently Disabling Windows Defender via Registry Keys

Just compile and execute it!

And when i restart it:
image

BYOVDWindowsDefenderKiller

This module implements a BYOVD (Bring Your Own Vulnerable Driver) technique to disable Windows Defender by continuously terminating its processes.

A vulnerable signed driver is loaded to gain kernel-level access, allowing the program to repeatedly kill MsMpEng.exe services in a loop.

Driver

https://github.com/DeathShotXD/0xKern3lCrush-Foreverday-BYOVD-CVE-2026-0828/blob/main/drivers/0xhashes.md

Registry + BYOVD (CombinedWindowsDefKiller)

This repository brings together two separate techniques to illustrate a combined approach for disabling Windows Defender more effectively.

The registry-based method applies permanent configuration changes, but it is heavily detected and blocked by most antivirus solutions, including Defender itself. Because of this, running it directly is often unreliable.

To address this, the BYOVD technique can be used beforehand. By loading a vulnerable driver and gaining kernel-level access, Defender-related processes are continuously terminated, reducing its ability to detect or block further actions.

With Defender in this weakened state, the registry-based code can then be executed and disable in a permanent way the defender

Workflow

  • Use BYOVD to disrupt Defender at runtime (process termination loop)
  • Execute the registry-based method without interference

⚠️ Disclaimer For educational and security research purposes only. Use in controlled environments.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →




