
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides and professional reporting.




Ethical network security auditor — 50+ checks across SMB, RDP, LDAP, SSH, Kerberos and more, with AI-powered CVE analysis and OWASP/CIS/NIST compliance mapping.
Quick Start · Documentation · Docker · AI Features · Star on GitHub
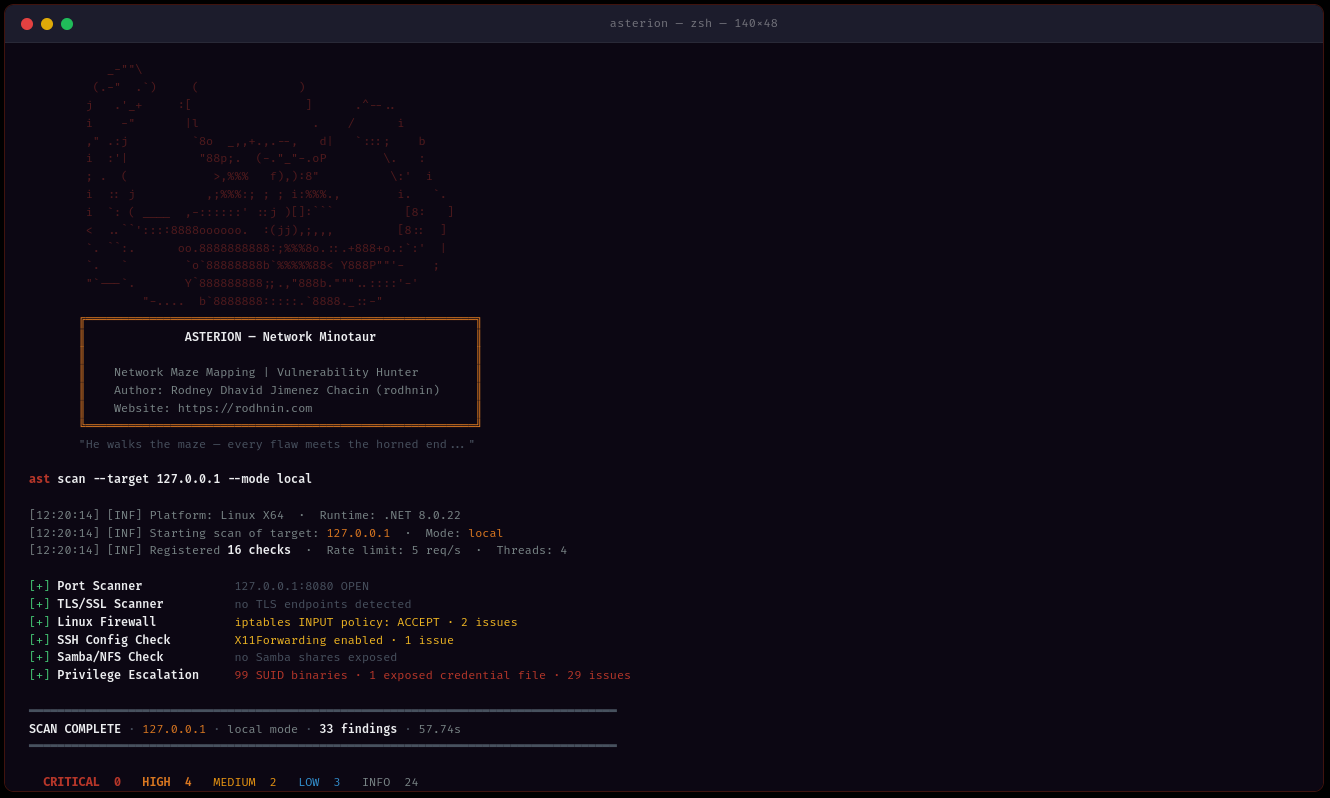
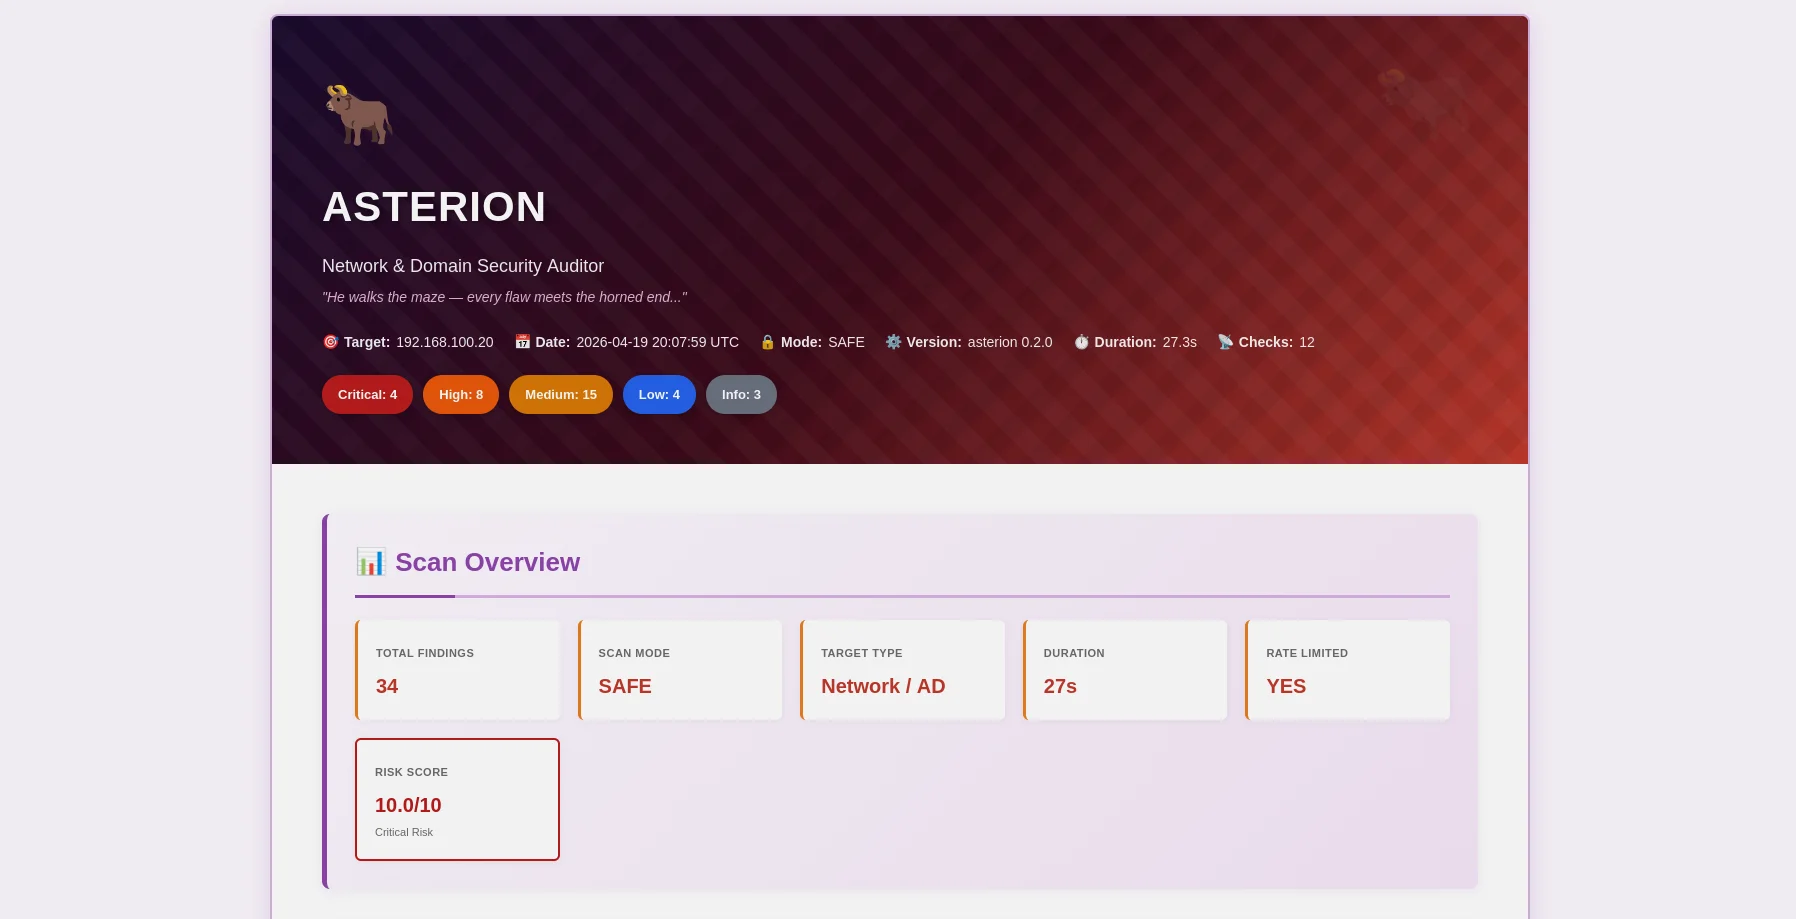
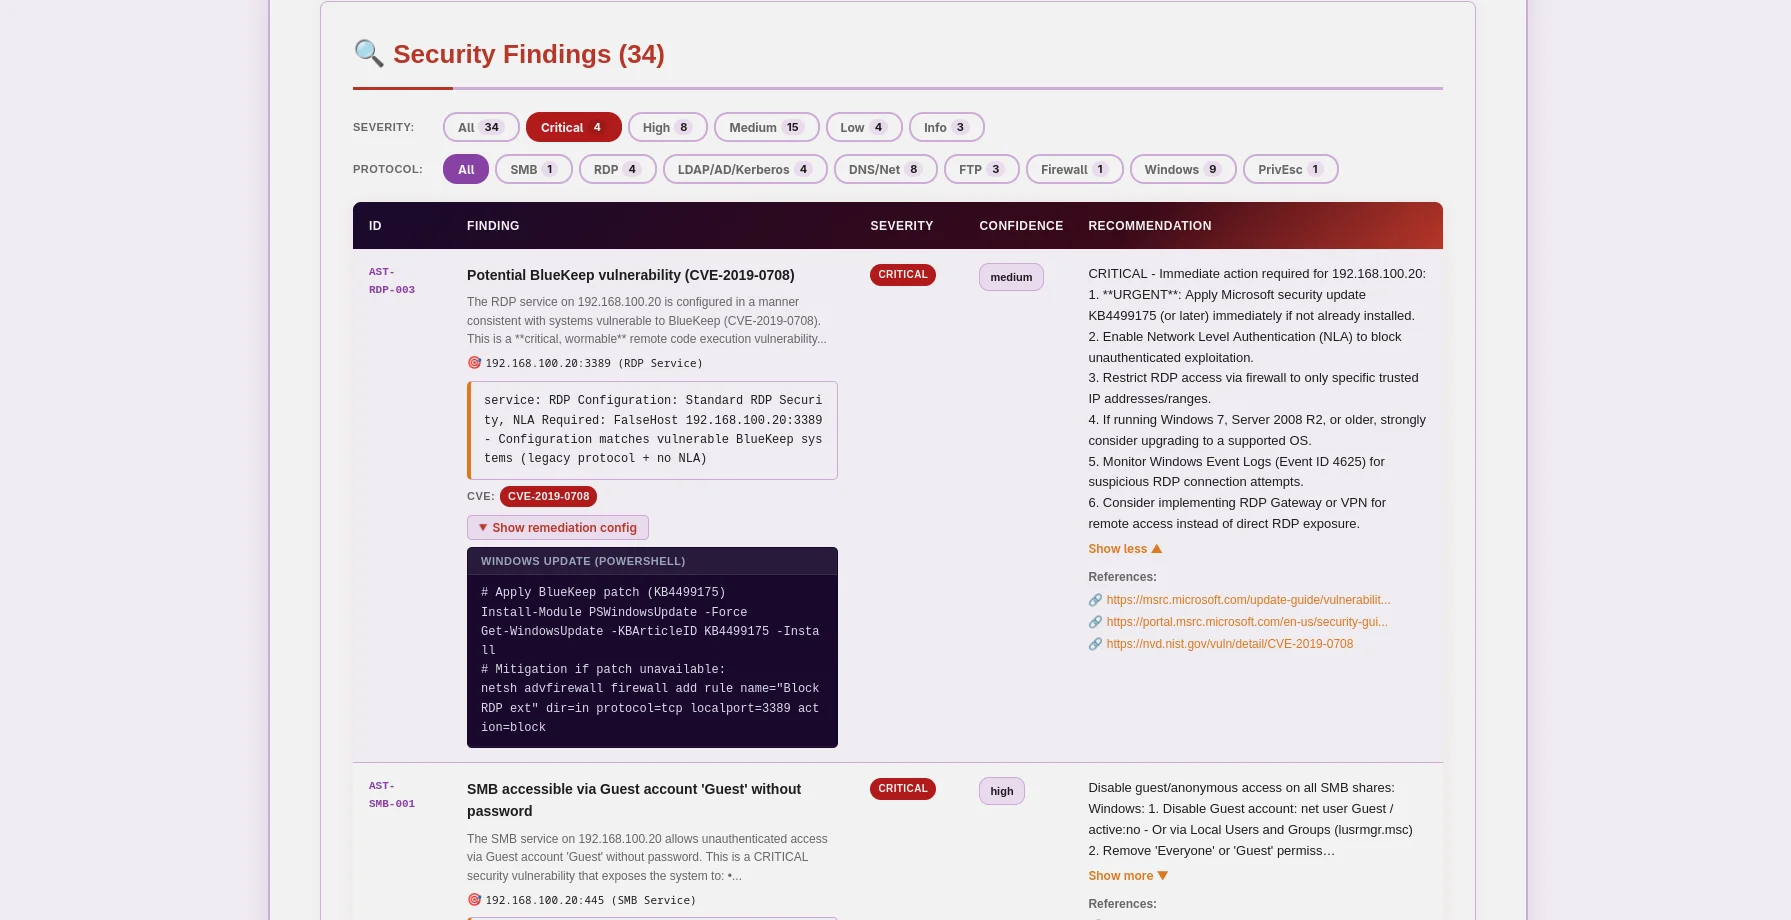
Minotaur-themed HTML report — severity badges, expandable evidence, AI remediation |
JSON report — OWASP/CIS/NIST/PCI mapping, CVE data, machine-readable |
Asterion is a production-ready network and domain security auditor that puts ethics first. Built for penetration testers, security researchers, and enterprise security teams, it combines traditional vulnerability scanning with cutting-edge AI analysis to deliver actionable insights for Windows Active Directory, Linux systems, and network infrastructure.
| Check Category | Details |
|---|---|
| SMB/CIFS Security | Anonymous shares, SMB signing, SMBv1 (EternalBlue), NTLMv1, writable shares |
| RDP Security | Network Level Authentication (NLA), encryption levels, exposed RDP |
| LDAP/Active Directory | Anonymous bind, LDAP signing, password policies, Kerberos pre-auth |
| Kerberos Security | AS-REP roasting, Kerberoasting, excessive ticket lifetime |
| SNMP | Default community strings, SNMPv1/v2c, write access |
| DNS/NetBIOS | Zone transfers (AXFR), LLMNR/NetBIOS poisoning, mDNS |
| Windows Systems | Firewall, Registry (UAC, LSA), services, privilege escalation |
| Linux Systems | iptables/nftables, SSH, Samba/NFS, SUID binaries, sudo misconfig |
# One command, comprehensive network analysis
ast scan --target 10.0.0.0/24 --output html
Choose your AI provider based on your needs:
| Provider | Best For | Speed | Cost | Privacy |
|---|---|---|---|---|
| OpenAI GPT-4 | Production quality | ⚡ Fast (40s) | 💰 $0.30/scan | 🔒 Standard |
| Anthropic Claude | Privacy-focused | ⚡ Fast (50s) | 💰 $0.35/scan | 🔒 Enhanced |
| Ollama (Local) | Complete privacy | 🐢 Slow (30min) | 💰 Free | 🔐 100% Offline |
Two Analysis Modes:
JSON Reports (Machine-Readable)
{
  "tool": "asterion",
  "version": "0.2.0",
  "target": "192.168.1.10",
  "riskScore": 10.0,
  "summary": {
    "critical": 3,
    "high": 8,
    "medium": 16,
    "low": 5,
    "info": 2
  },
  "findings": [
    {
      "id": "AST-SMB-003",
      "title": "SMBv1 protocol enabled (EternalBlue vector)",
      "severity": "high",
      "owasp": { "id": "A06", "name": "Vulnerable and Outdated Components" },
      "vulnerabilities": [
        {
          "cve_id": "CVE-2017-0143",
          "cvss_score": 9.8,
          "cwe_id": "CWE-119"
        }
      ],
      "cvss": 9.8
    }
  ],
  "attackChains": [...],
  "diff": { "refScanId": 41, "new": [...], "fixed": [...], "persisting": [...] }
}
HTML Reports (Human-Friendly)
Asterion enforces ethical hacking through technology. Aggressive scanning and AI analysis require proof of ownership:
# 1. Generate token
ast consent generate --domain corp.local

# 2. Place token (choose one method)
# HTTP: Upload to https://corp.local/.well-known/verify-abc123.txt
# DNS: Add TXT record: corp.local = "asterion-verify=verify-abc123"
# SSH: Create file /tmp/consent_verify-abc123 with token content

# 3. Verify ownership
ast consent verify --method http --domain corp.local --token verify-abc123

# 4. Now you can use aggressive mode
ast scan --target corp.local --mode aggressive --use-ai
Shared SQLite database with Argos Suite tracks everything: