
 revoltsecurities/shodanx
ShodanX is a tool to gather information of targets using shodan dorks⚡.


Features | Installation | Usage | Post Installation Setup


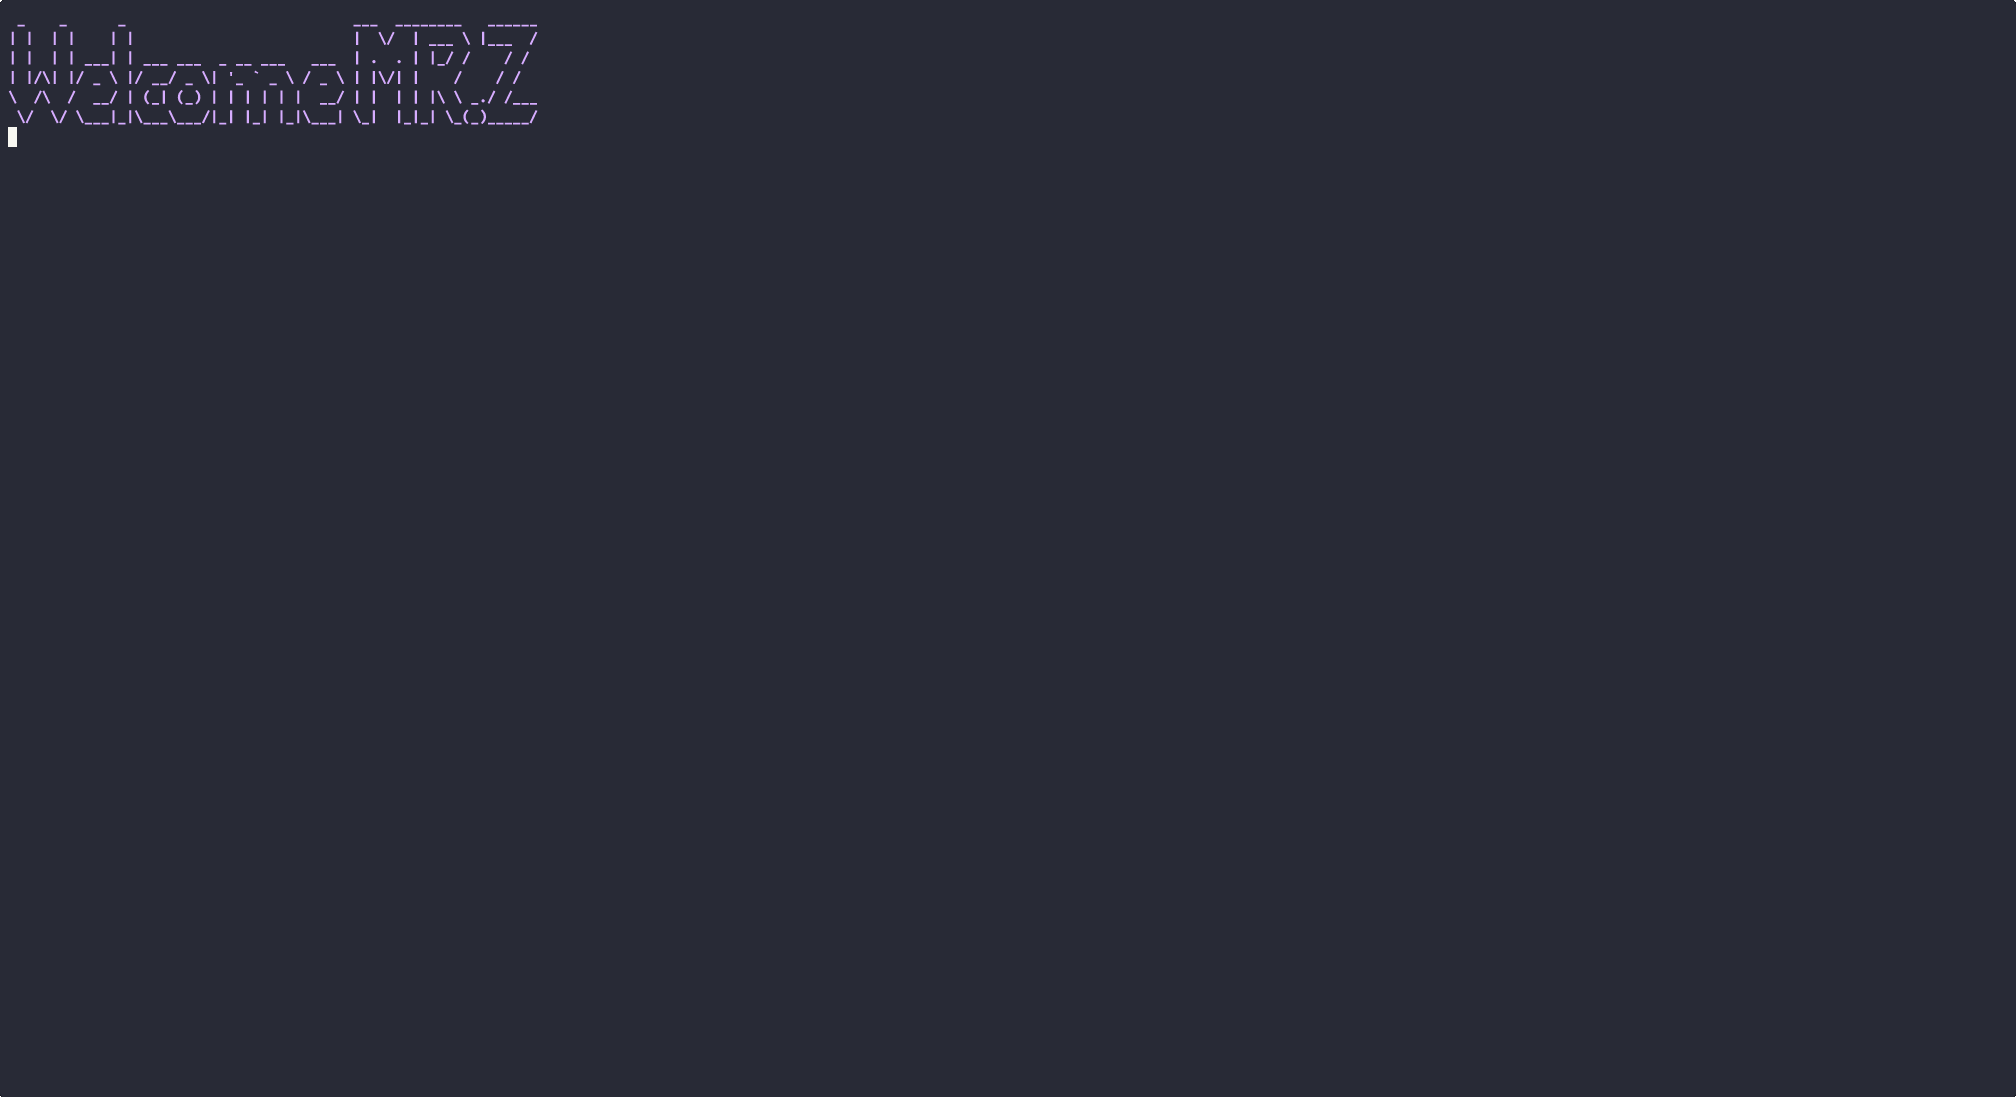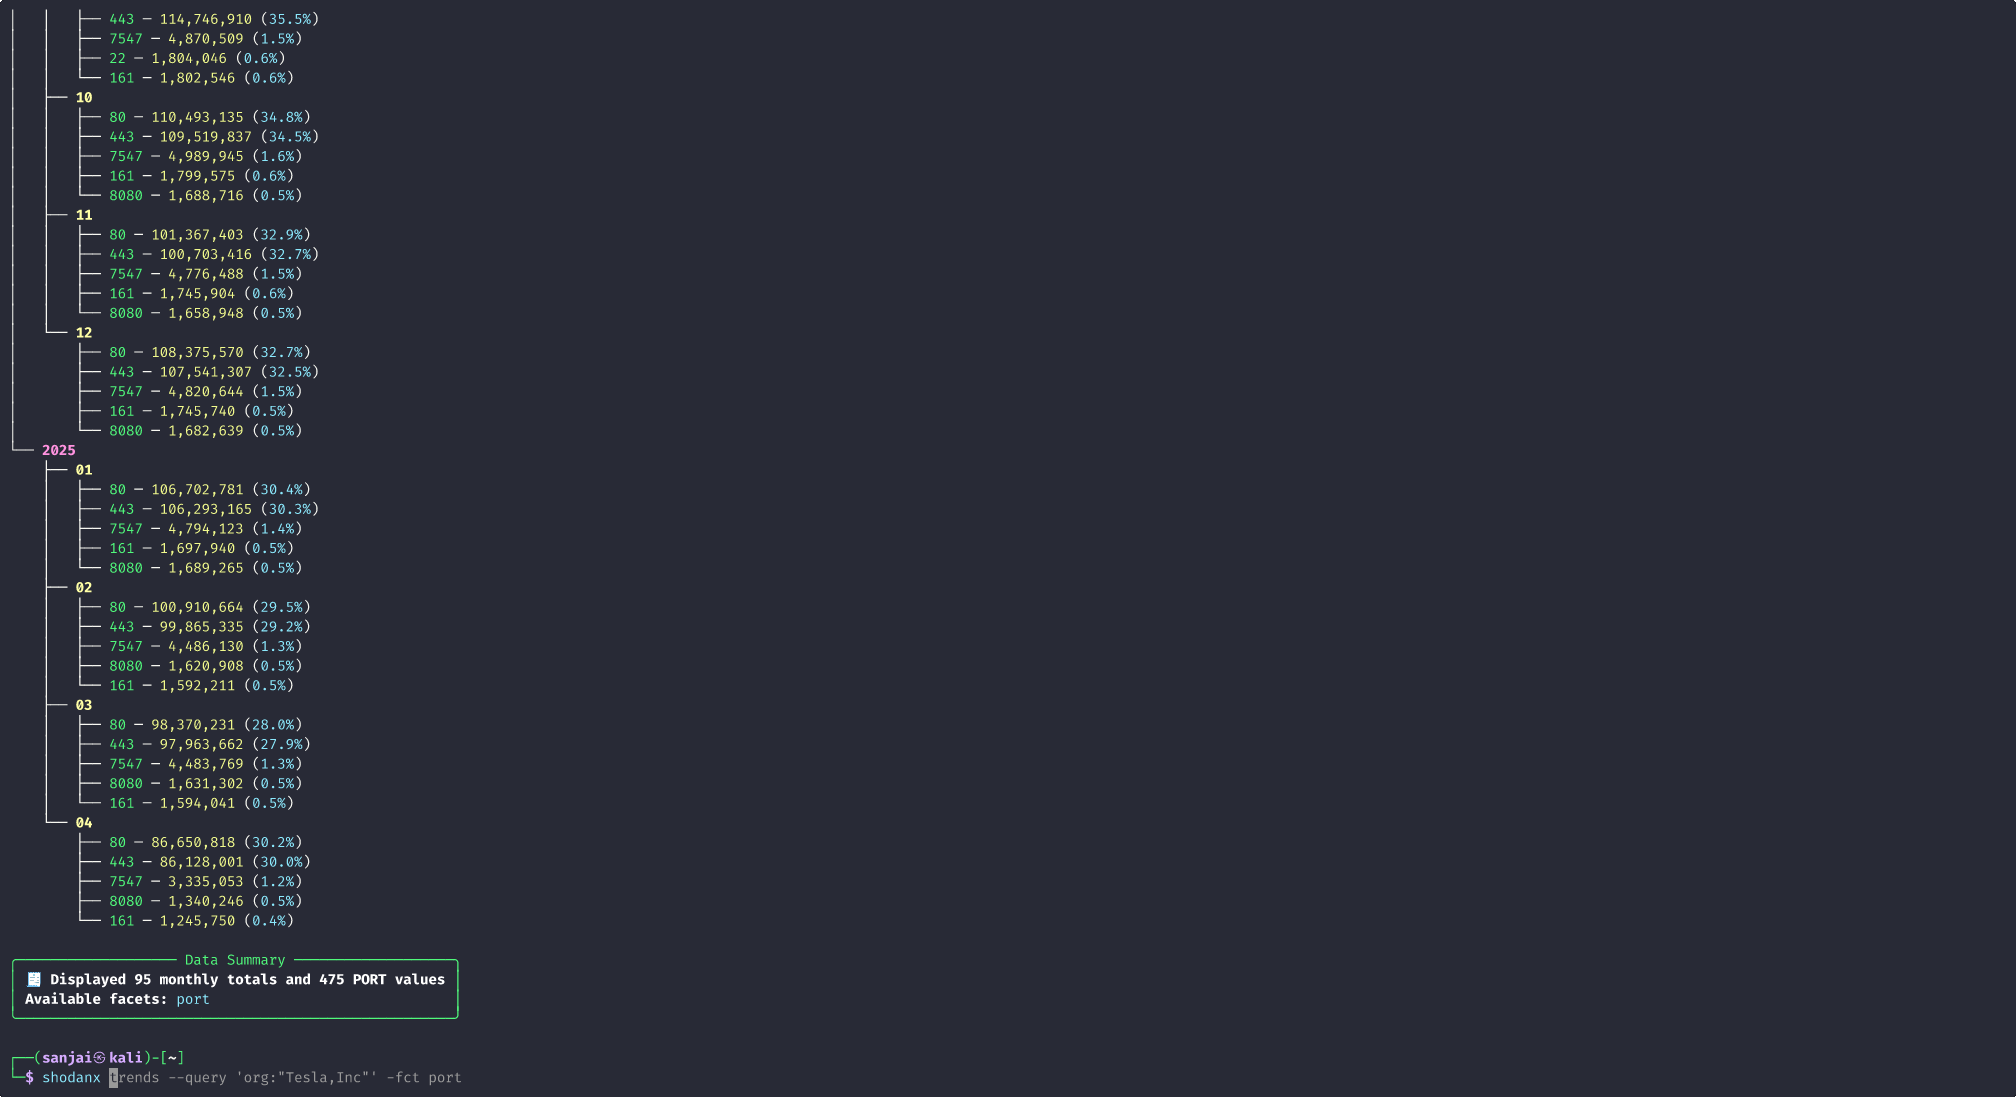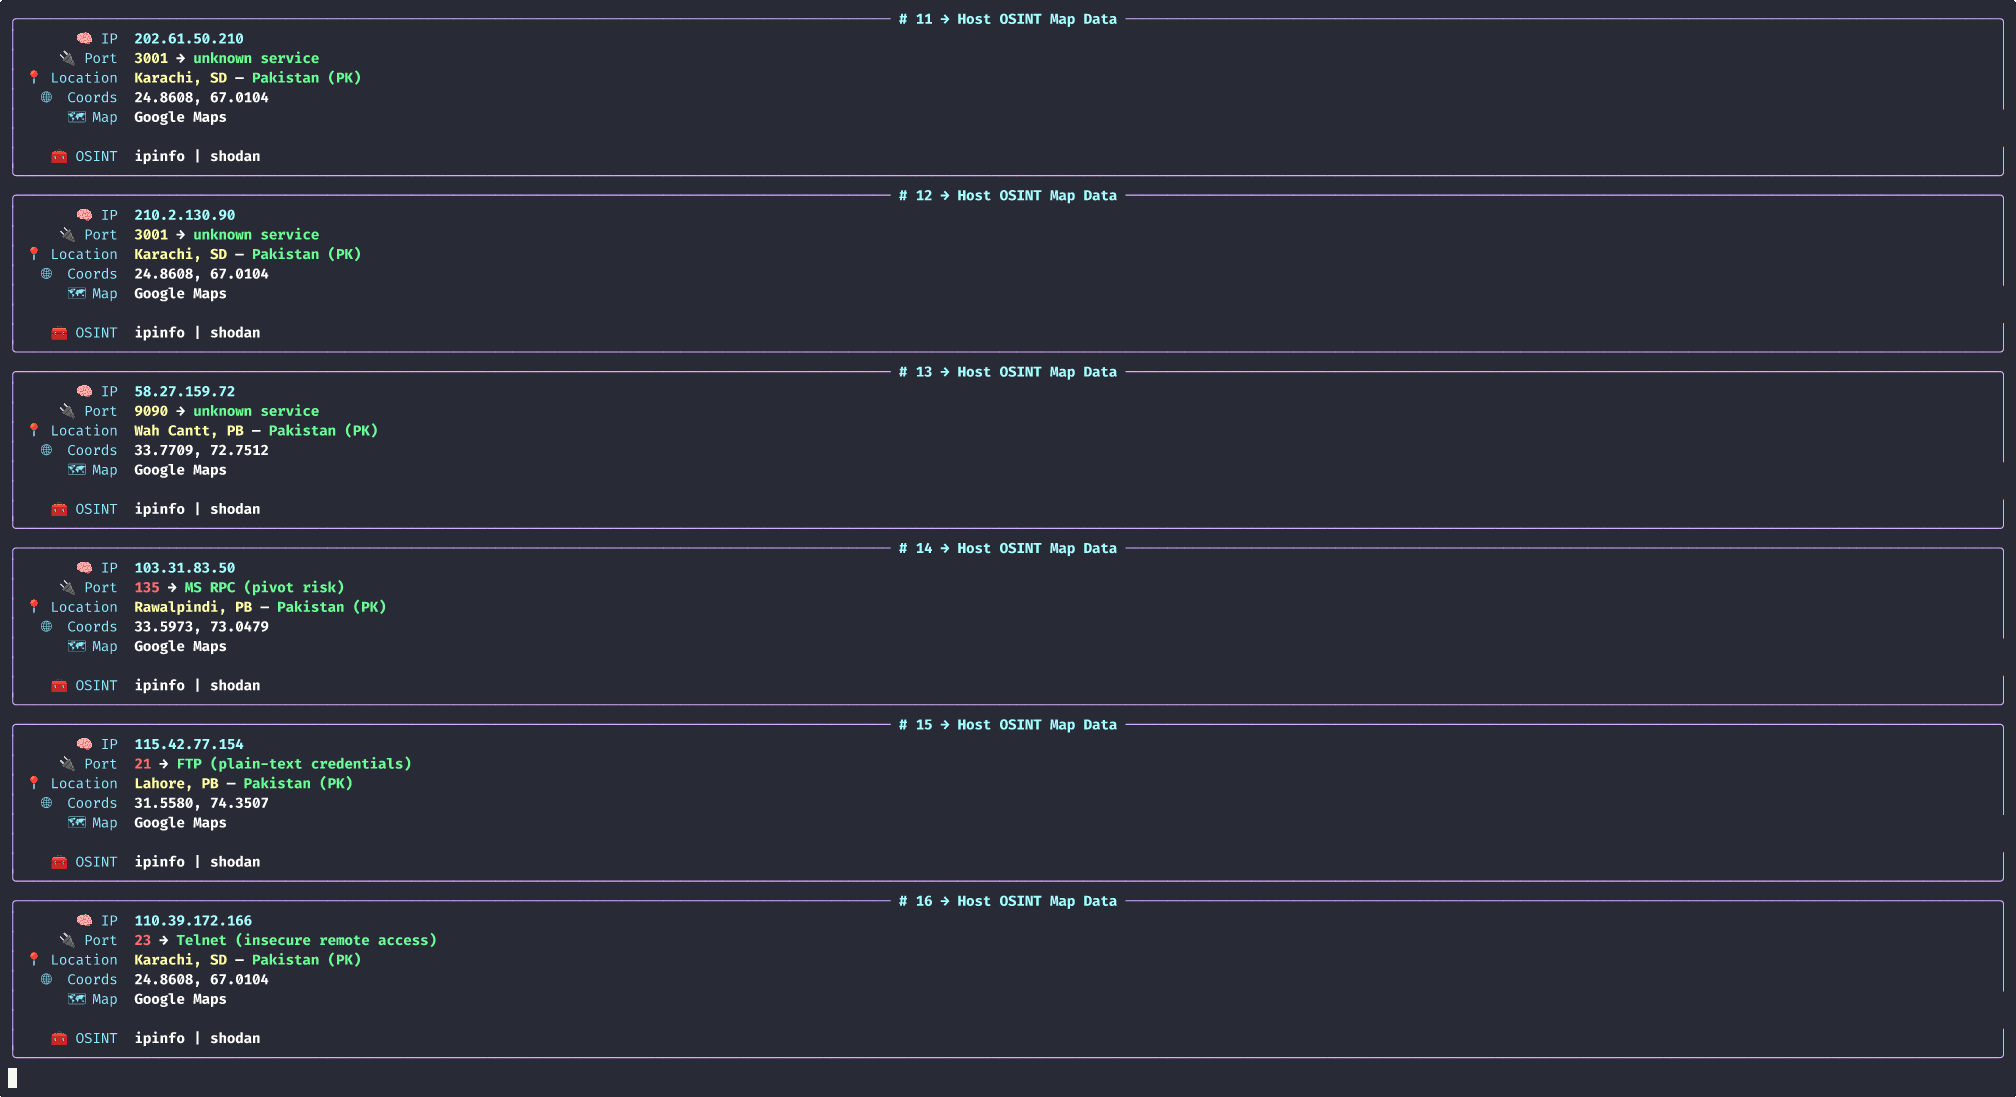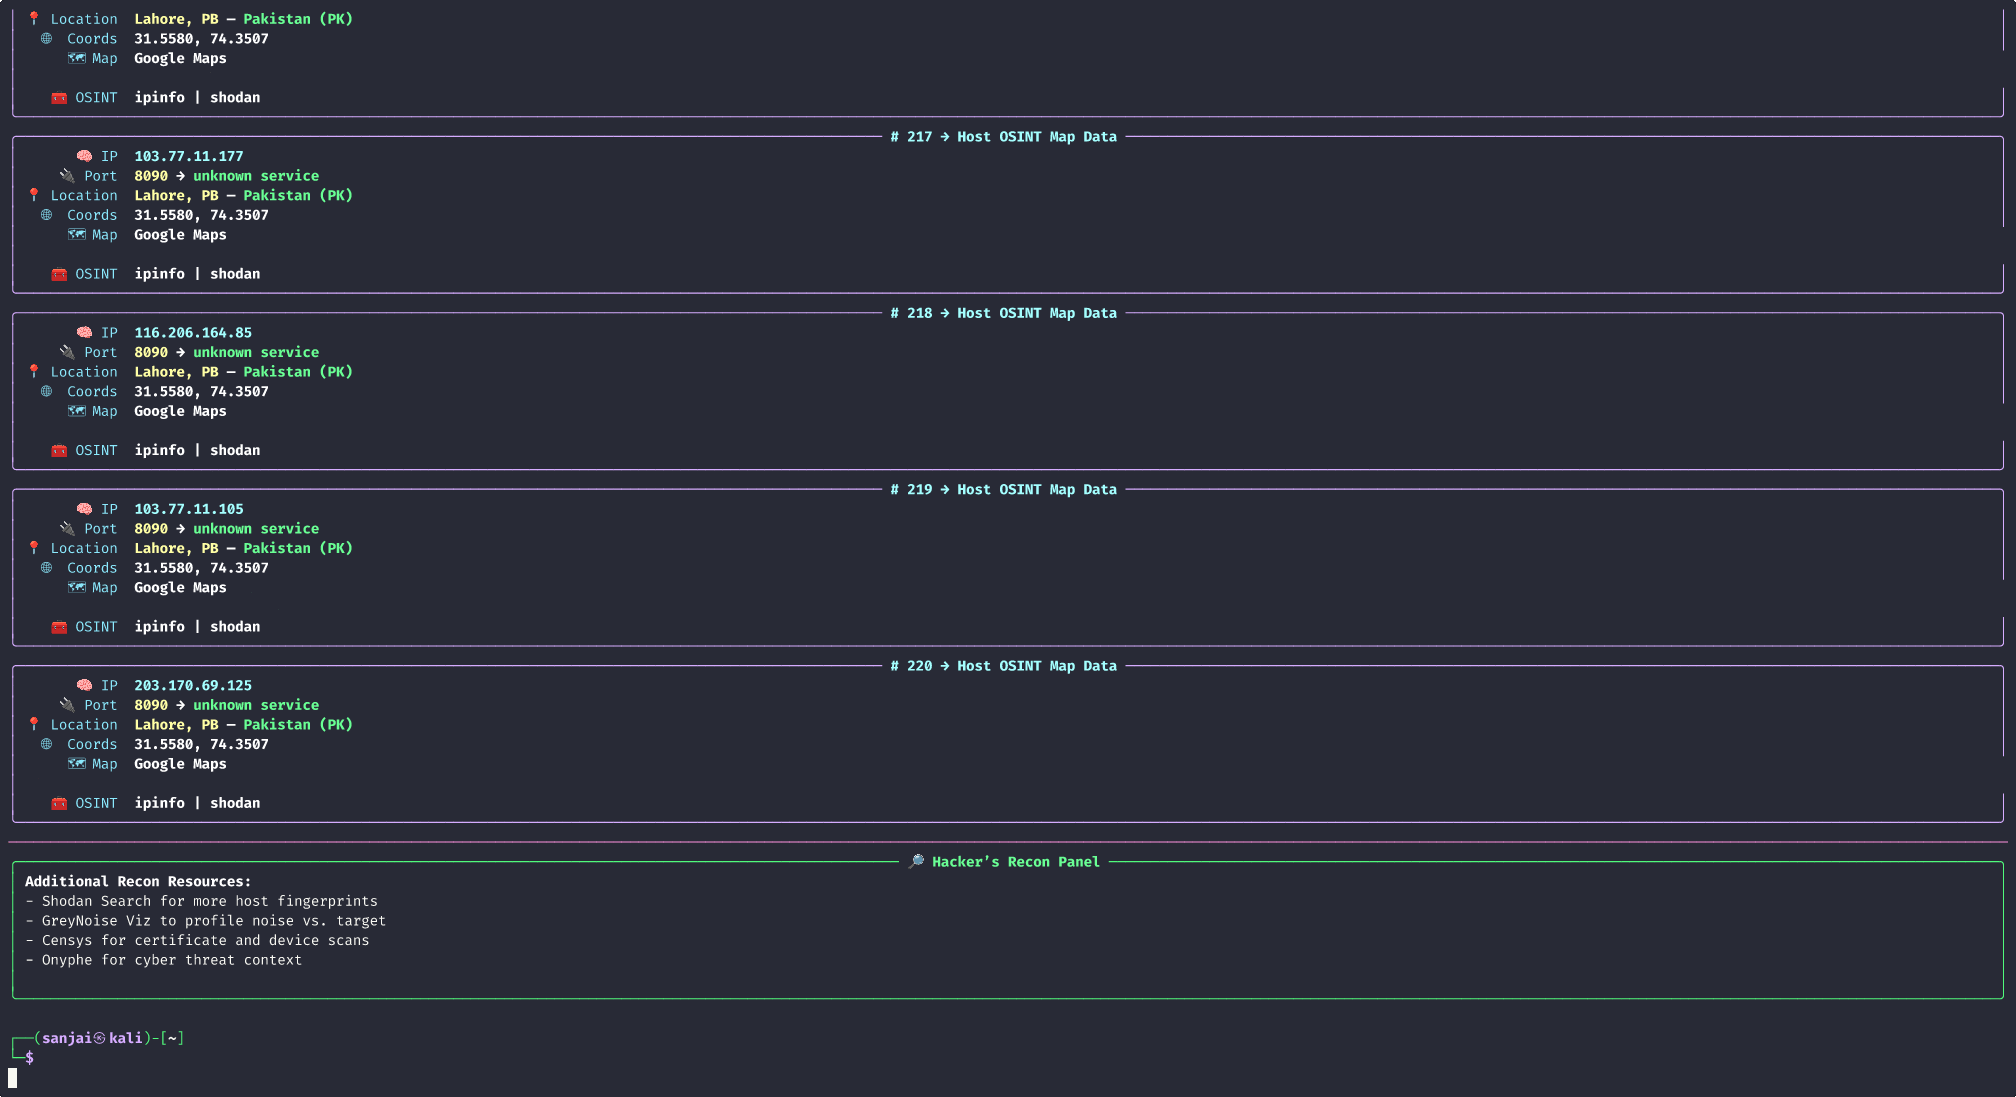
🔐 shodanx auth – Configure and store your Shodan API key securely.🔓 shodanx login – Validate your access level and API key status.🏢 shodanx org – Perform organization-wide scans using Shodan’s powerful facets.🌐 shodanx domain – Enumerate domain-related metadata, open ports, and host exposures.📡 shodanx subdomain – Discover passive subdomains via Shodan’s DNS intel.🔒 shodanx ssl – Track reused or expired SSL certificates via fingerprint searches.🎯 shodanx custom – Run advanced Shodan dorks and custom filter queries.📦 shodanx internetdb – Use Shodan’s lightweight InternetDB for quick IP/domain analysis.🗺️ shodanx map – Visualize geographic distribution of exposed services and ports.🧬 shodanx cvedb – Map hosts to known vulnerabilities using the CVE database.🏭 shodanx entitydb – Explore technologies, software, and vendors across exposed systems.🌍 shodanx exposuredb – Identify publicly exposed assets and data leaks by country.🖼️ shodanx faviconmap – Track systems by unique favicons for lateral discovery.📈 shodanx trends – Analyze exposure trends over time (Enterprise access required).shodanx can be easily installed using pip
pip install git+https://github.com/RevoltSecurities/ShodanX --break-system-packages
✅ Make sure you have Python 3.13 or newer installed.
shodanx -h
   _____    __                __                   _  __
  / ___/   / /_   ____   ____/ /  ____ _   ____   | |/ /
  \__ \   / __ \ / __ \ / __  /  / __ `/  / __ \  |   /
 ___/ /  / / / // /_/ // /_/ /  / /_/ /  / / / / /   |
/____/  /_/ /_/ \____/ \__,_/   \__,_/  /_/ /_/ /_/|_|


                     - RevoltSecurities

╭───────────────────────╮
│                       │
│    SHODANX ⚡ HELP    │
│                       │
╰───────────────────────╯
DESCRIPTION

ShodanX is a terminal-powered recon and OSINT tool built on top of the Shodan Services.
It empowers ethical hackers and red teamers to identify exposed infrastructure,
search CVEs, map attack surfaces, and run internet-wide queries in real time.

MODES (shodanx <mode>)

┏━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┓
┃ Mode       ┃ Description                                                      ┃
┡━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┩
│ auth       │ Configure and save your Shodan API key for authenticated access. │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ login      │ Verify your ShodanX access level and API key validity.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ org        │ Perform organization-wide scans using Shodan facets.             │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ domain     │ Enumerate metadata, ports, and host exposure for a domain.       │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ subdomain  │ Discover passive subdomains using Shodan’s DNS data.             │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ ssl        │ Search by SSL fingerprint to track reused/expired certs.         │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ custom     │ Execute advanced queries using Shodan filters and dorks.         │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ internetdb │ Lightweight analysis of IPs/domains via Shodan InternetDB API.   │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ map        │ Visualize geo-distribution of exposed services and ports.        │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ cvedb      │ Identify vulnerable systems via Shodan’s CVE database.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ entitydb   │ Explore technologies/vendors via Shodan’s EntityDB.              │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ exposuredb │ Discover globally exposed assets and leaks by country.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ faviconmap │ Find systems using specific favicons via Shodan FaviconMap.      │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ trends     │ View historical exposure trends (Shodan Enterprise required).    │
└────────────┴──────────────────────────────────────────────────────────────────┘
FLAGS
┏━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┓
┃ Flag       ┃ Description                      ┃
┡━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┩
│ -h, --help │ Show this help message and exit. │
└────────────┴──────────────────────────────────┘
USAGE
shodanx <mode>

DETAILS
 shodanx auth        → Configure and save your Shodan API key for authenticated access.
 shodanx login       → Verify your ShodanX access level and API key validity.
 shodanx org         → Perform organization-wide scans using Shodan facets.
 shodanx domain      → Enumerate metadata, ports, and host exposure for a domain.
 shodanx subdomain   → Discover passive subdomains using Shodan’s DNS data.
 shodanx ssl         → Search by SSL fingerprint to track reused/expired certs.
 shodanx custom      → Execute advanced queries using Shodan filters and dorks.
 shodanx internetdb  → Lightweight analysis of IPs/domains via Shodan InternetDB API.
 shodanx map         → Visualize geo-distribution of exposed services and ports.
 shodanx cvedb       → Identify vulnerable systems via Shodan’s CVE database.
 shodanx entitydb    → Explore technologies/vendors via Shodan’s EntityDB.
 shodanx exposuredb  → Discover globally exposed assets and leaks by country.
 shodanx faviconmap  → Find systems using specific favicons via Shodan FaviconMap.
 shodanx trends      → View historical exposure trends (Shodan Enterprise required).
Once you've successfully installed shodanx, follow these quick steps to get fully authenticated and ready to scan:
Start by running the auth command to securely store your credentials:
shodanx auth
You'll be prompted to enter:







