
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
BurpSuite-Asset_Discover — Burp Suite extension to discover assets from HTTP response. | Kitploit

Tools/GitHubGitHub/redhuntlabs/burpsuite-asset_discover
OSINT (Open Source Intelligence)Information GatheringWeb Security
GitHubredhuntlabs/burpsuite-asset_discover

BurpSuite-Asset_Discover

Burp Suite extension to discover assets from HTTP response.

View Repository
Share
23552341 year agoReviewed by Kitploit

BurpSuite Extension - Asset Discover

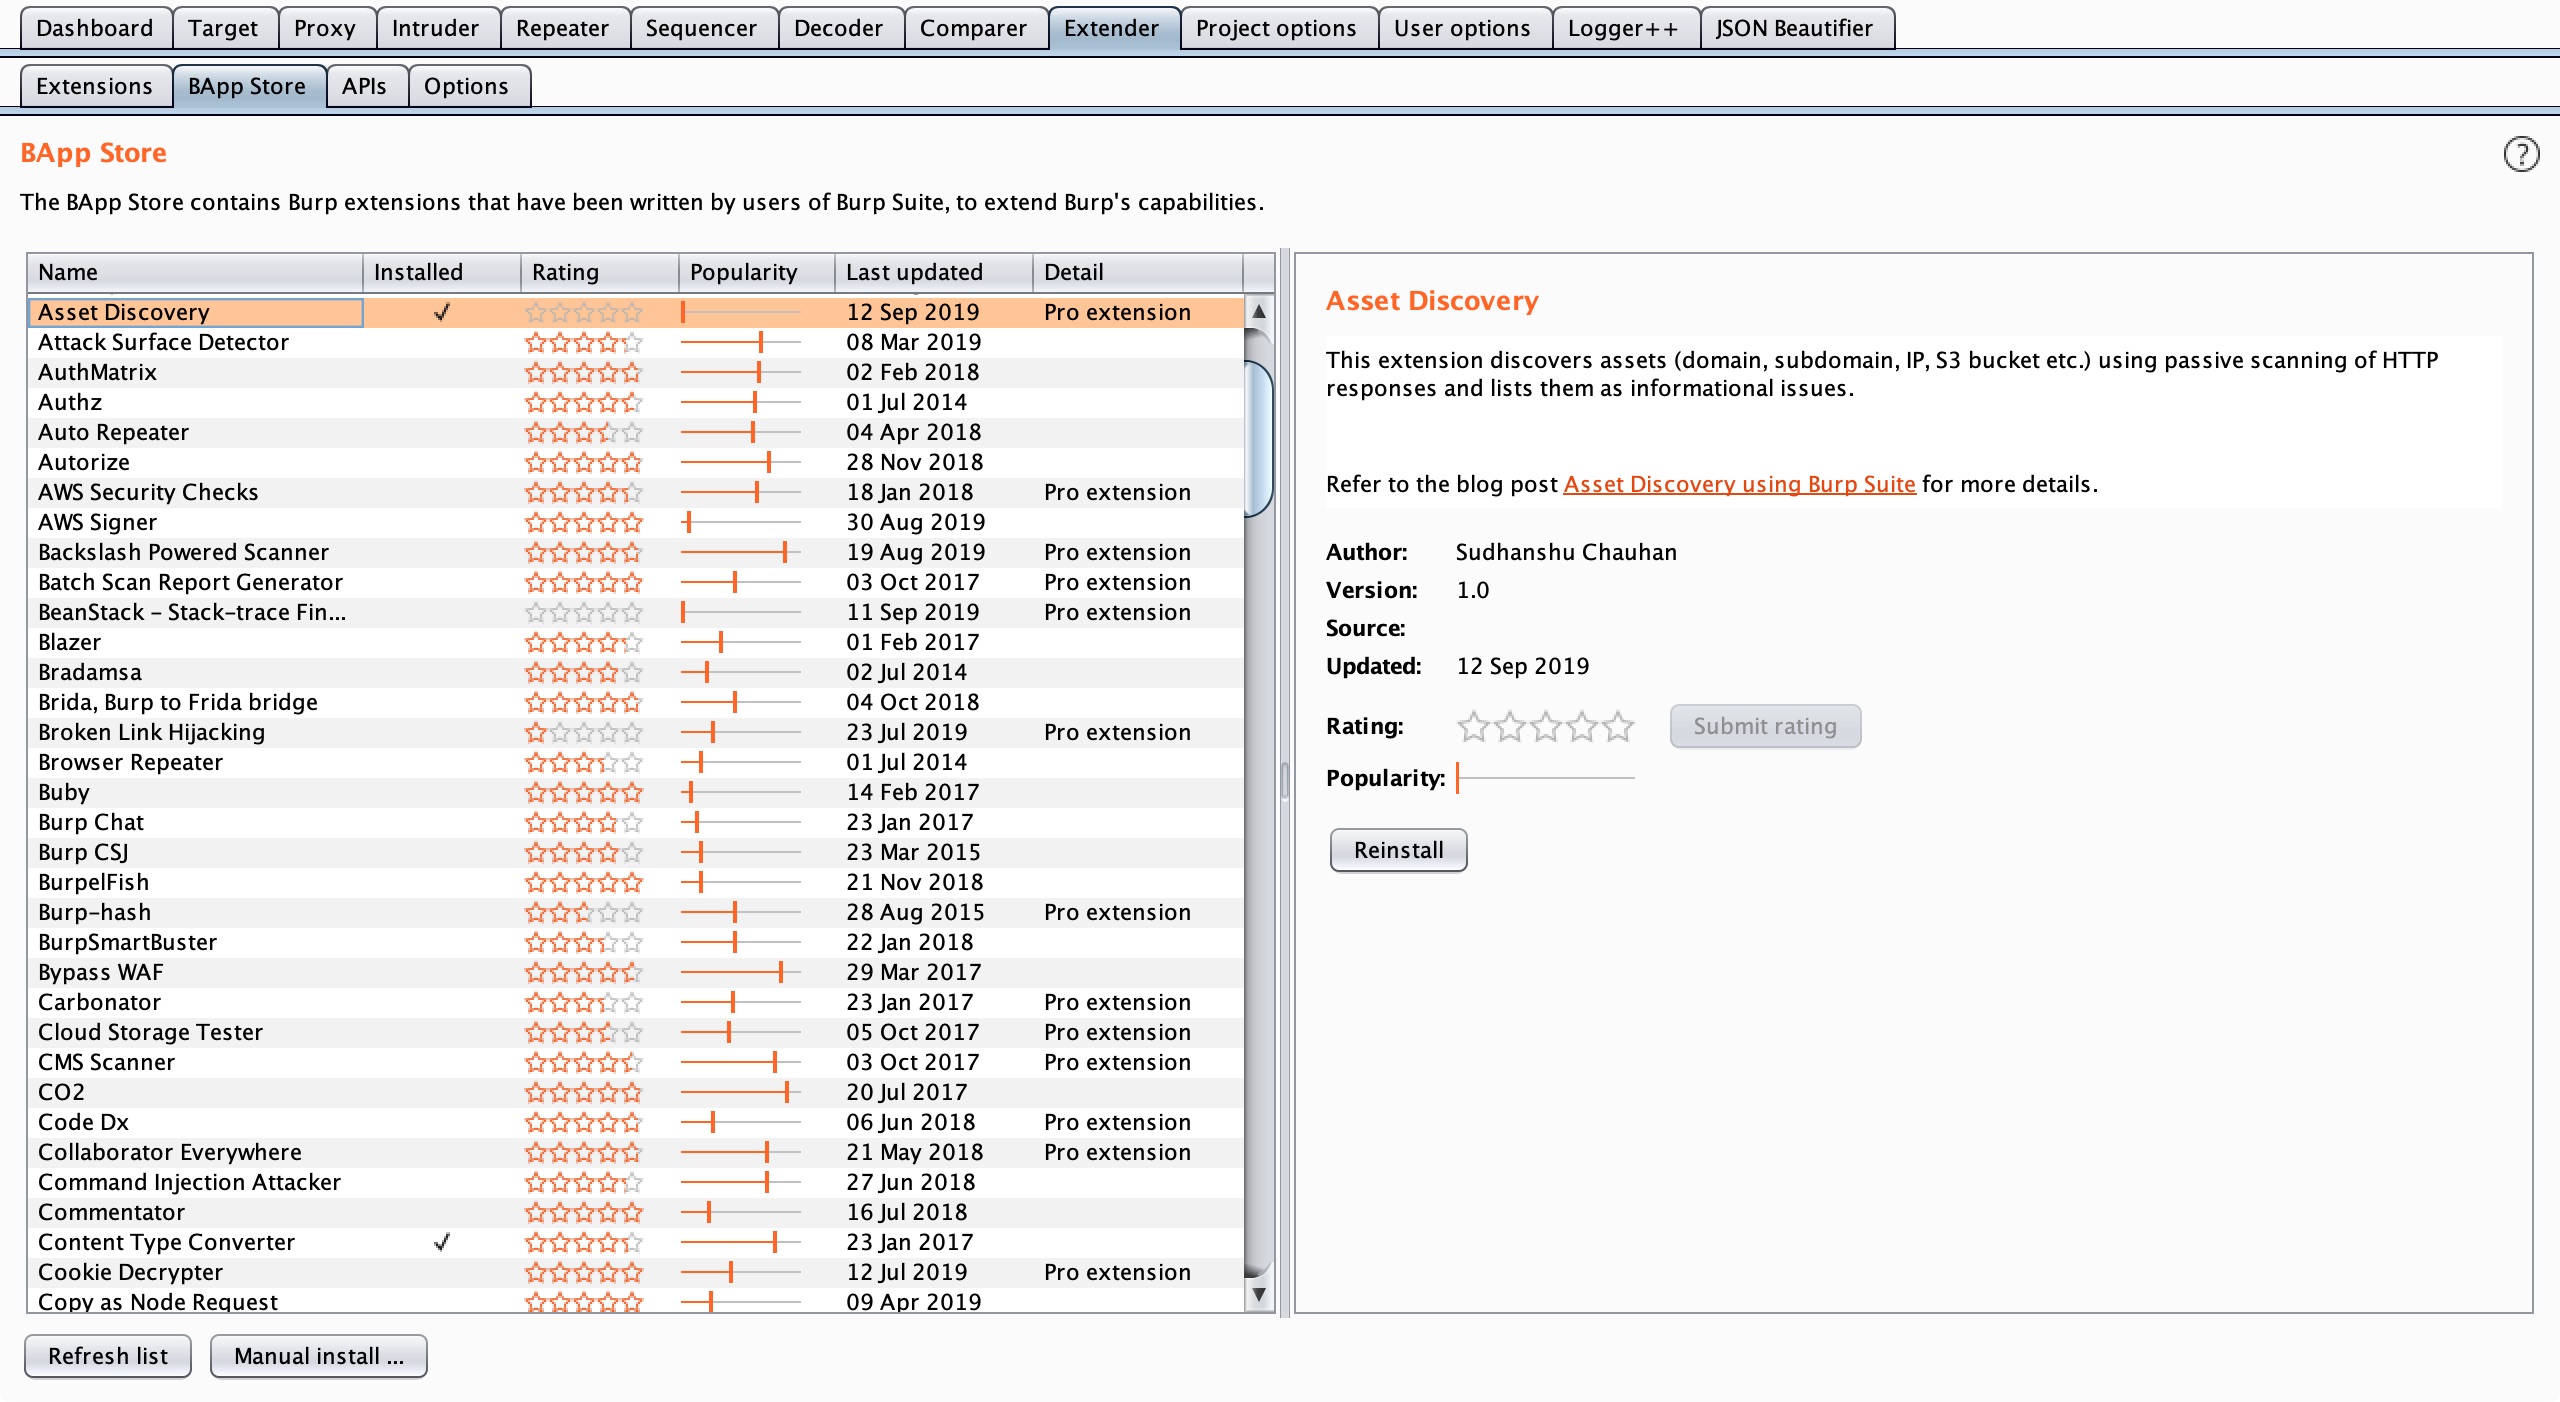
Burp Suite extension to discover assets from HTTP response using passive scanning. Refer our blog Asset Discovery using Burp Suite for more details.

The extension is now part of the BApp store and can be installed directly from the Burp Suite. https://portswigger.net/bappstore/d927f0065171485981d6eb49a860fc3e

To know more about our Attack Surface Management platform, check out NVADR.

Description

Passively parses HTTP response of the URLs in scope and identifies different type assets such as domain, subdomain, IP, S3 bucket etc. and lists them as informational issues.

Setup

  • Setup the python environment by providing the jython.jar file in the 'Options' tab under 'Extender' in Burp Suite.
  • Download the extension.
  • In the 'Extensions' tab under 'Extender', select 'Add'.
  • Change the extension type to 'Python'.
  • Provide the path of the file ‘Asset_Discover.py’ and click on 'Next'.

Usage

  • Add a URL to the 'Scope' under the 'Target' tab. The extension will start identifying assets through passive scan.

Requirements

  • Jython 2.7.0
  • Burp Suite Pro v2.1

Code Credits

A large portion of the base code has been taken from the following sources:

  • OpenSecurityResearch CustomPassiveScanner
  • PortSwigger example-scanner-checks

License

The project is available under MIT license, see LICENSE file.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





