 qm4rs/cve-2026-0023-update-ownership-poc
Proof-of-concept demonstrating CVE-2026-0023, an Android Update Ownership trust bypass that suppresses the ownership warning during app updates. Includes three Android apps for reproducing and studying the vulnerability.

A complete Android laboratory environment for reproducing and studying CVE-2026-0023.
This repository demonstrates how CVE-2026-0023 allows a regular installer to influence an internal Android installation flag that should only be controlled by the system, resulting in Android's Update Ownership warning being suppressed during application updates.
The project contains three Android applications that model a realistic update ownership workflow and provide a reproducible environment for observing the vulnerable behavior.
Android introduced Update Ownership to help applications, app stores, and enterprise environments maintain a trusted update chain.
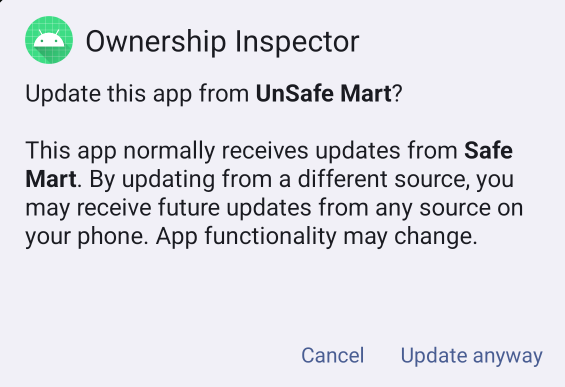
When an application has a registered update owner, Android warns the user if another installer attempts to update that application.
Under normal conditions, this warning tells the user that the application usually receives updates from a different source.
CVE-2026-0023 affects Android's package installation flow inside PackageInstallerService#createSessionInternal.
The issue is related to the handling of the internal INSTALL_FROM_MANAGED_USER_OR_PROFILE installation flag.
In vulnerable builds, this flag was not explicitly cleared before Android checked whether the installation was actually associated with a managed user or managed profile.
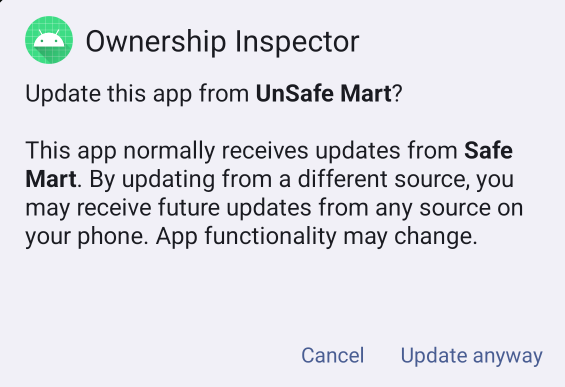
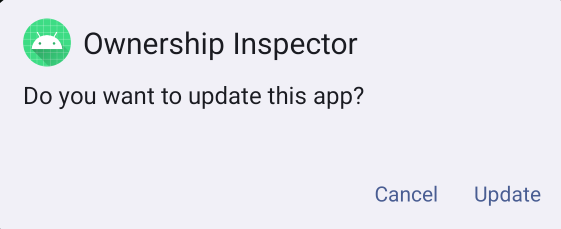
As a result, a regular installer could influence update ownership behavior and cause Android to suppress the expected Update Ownership warning.
This repository demonstrates the difference between the expected behavior and the vulnerable behavior using a controlled proof-of-concept environment.
| Expected behavior | Vulnerable behavior |
|---|---|
| Android displays the Update Ownership warning. | Android displays only a generic update dialog. |
 |  |
| Field | Value |
|---|---|
| CVE | CVE-2026-0023 |
| Component | Framework / PackageInstaller |
| Affected file | PackageInstallerService.java |
| Affected method | createSessionInternal |
| Vulnerability type | Elevation of Privilege |
| Severity | High |
| CVSS v3.1 | 7.8 |
| CVSS vector | CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H |
| Attack Vector | Local |
| Attack Complexity | Low |
| Privileges Required | Low |
| User Interaction | None |
| Scope | Unchanged |
| Impact | Elevation of Privilege through unauthorized update ownership behavior |
| Android Security Bulletin | March 2026 |
| Android bug reference | A-459461121 |
| Affected AOSP versions listed by Google | Android 14, 15, 16, 16-qpr2 |
| Event | Value |
|---|---|
| Android Security Bulletin | March 2026 |
| Bulletin publication date | March 2, 2026 |
| Security patch level section | 2026-03-01 |
| Bulletin-wide fully addressed patch level | 2026-03-05 or later |
| Android bug reference | A-459461121 |
| AOSP patch | 09055276288a68cf35b0f84ba32e28822f74ecf9 |
| Patch title | Explicitly unset INSTALL_FROM_MANAGED_USER_OR_PROFILE flag |
CVE-2026-0023 is listed in the March 2026 Android Security Bulletin under the 2026-03-01 security patch level vulnerability details.
Android security patch levels of 2026-03-01 or later address all issues associated with the 2026-03-01 security patch level.
Android security patch levels of 2026-03-05 or later address all issues associated with the 2026-03-05 security patch level and all previous patch levels.
The vulnerable behavior is related to the handling of the internal INSTALL_FROM_MANAGED_USER_OR_PROFILE flag.
This flag is intended to represent installation behavior associated with a managed user or managed profile.
The official AOSP patch explicitly clears this flag before Android checks whether the install actually belongs to an organization-managed user.
The fixed logic ensures that only the system can set this flag based on the result of DevicePolicyManagerInternal#isUserOrganizationManaged(userId).
Simplified patch logic:
final var dpmi = LocalServices.getService(DevicePolicyManagerInternal.class);

+ // Only the system should be able to set this flag - so ensure it is unset when not needed.
+ params.installFlags &= ~PackageManager.INSTALL_FROM_MANAGED_USER_OR_PROFILE;

if (dpmi != null && dpmi.isUserOrganizationManaged(userId)) {
    params.installFlags |= PackageManager.INSTALL_FROM_MANAGED_USER_OR_PROFILE;
}
Before the patch, the flag was not explicitly cleared before this managed-profile check.
After the patch, Android first removes the flag and only sets it again if the system determines that the user is actually organization-managed.
This prevents a regular installer from influencing this internal install-session state.
This repository contains three Android applications:
CVE-2026-0023-Update-Ownership-PoC
├── Safe Mart
├── Unsafe Mart
└── Ownership Inspector
Safe Mart is a reference installer application.
It installs the target application and requests update ownership during the initial installation.
Its purpose is to simulate a legitimate application store that becomes the registered update owner of the target app.
